AI, identity, resilience, and quantum computing. What do they have in common? They’re all changing what CISOs need to prepare for.
In the conversations from KuppingerCole’s The CISO Perspective, four security leaders look at different parts of that challenge: from securing AI today to preparing for threats that may take years to materialize.
AI is changing the game
AI is already influencing both attackers and defenders.
In Full Steam Ahead: AI, Attackers, and Why CISOs Must Keep Pace, Michael Schrank and Berthold Kerl look at what AI means in practice for security teams.
AI can automate repetitive work, support investigations, and make security processes more efficient. But when organizations adopt AI faster than security teams can establish the right controls, new risks emerge.
For security leaders, that means being part of the conversation about how the business adopts AI, not just managing the risks afterwards.
Then there’s the question of identity
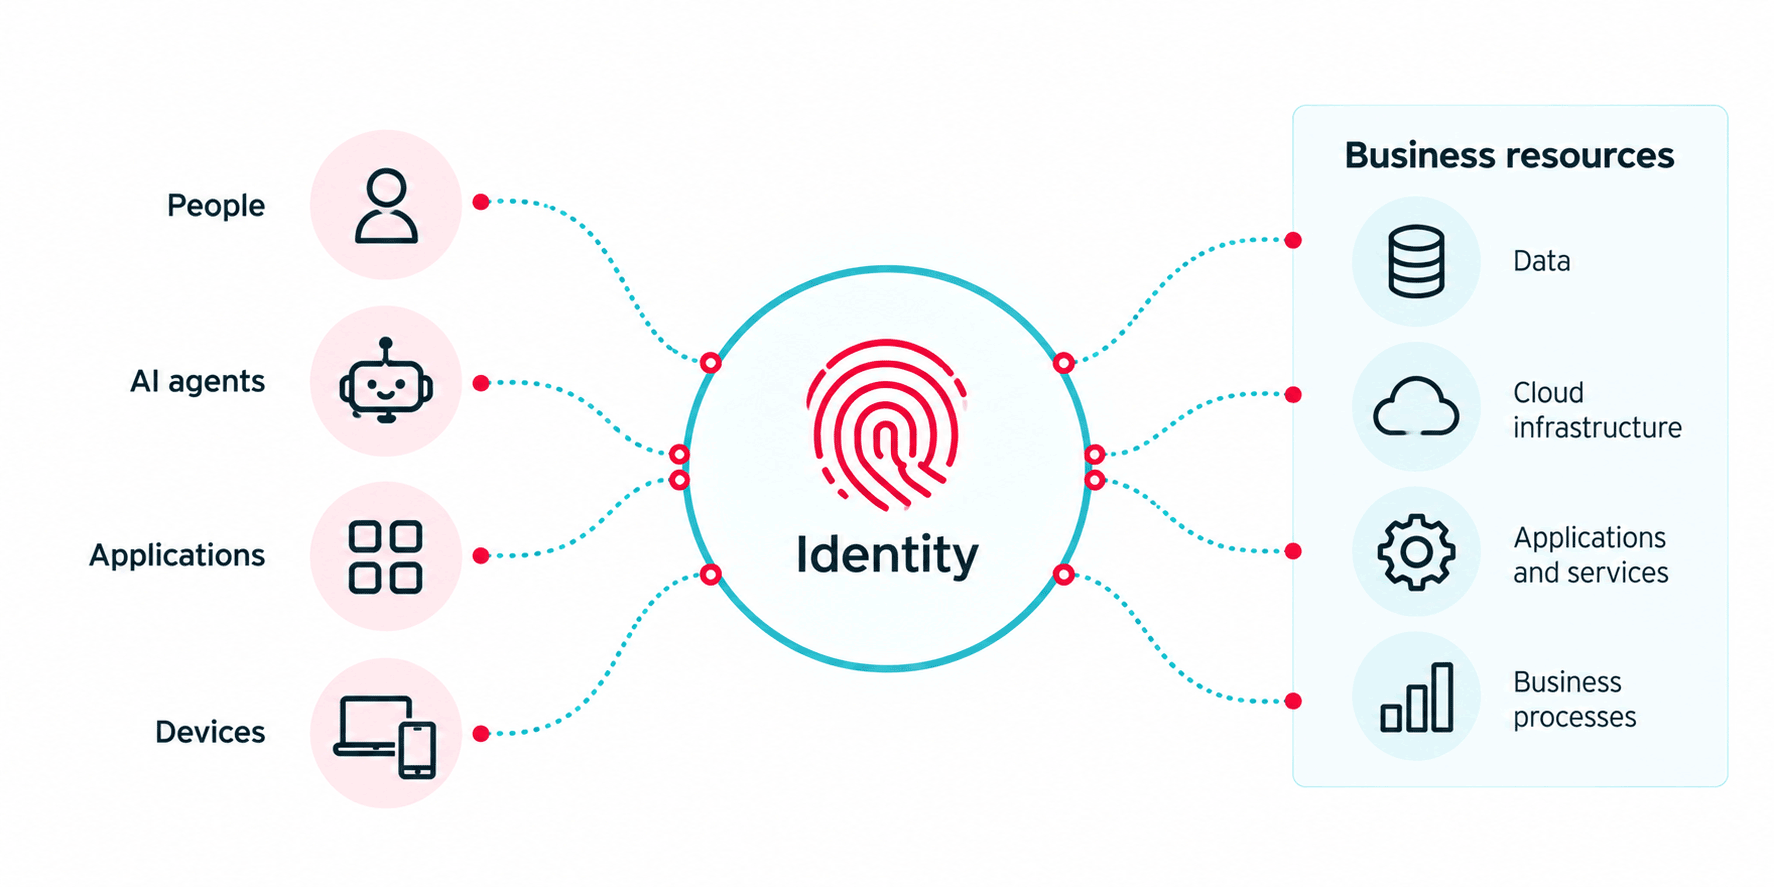
As organizations use more AI, applications, machines and AI agents are increasingly acting alongside people.
That raises a basic security question: who or what is allowed to access which resources?
That is the focus of Identity at the Epicenter: Why AI Makes It the Most Critical Control in Security.
The fundamentals haven’t changed. But there are more identities to manage, and more things that can act on behalf of an organization.
Security also has to look beyond technology
In Bigger Than Technology – A 360-Degree View of the Modern Threat Landscape, Thomas Tschersich of Deutsche Telekom takes a broader view of cybersecurity: looking at business impact, resilience and the environment in which organizations operate.
As he puts it: “So you need to get a much broader view in my perspective.”
The point is simple: security decisions affect more than systems. They affect people, operations and the organization’s ability to keep going when something goes wrong.
And some threats need to be addressed before they arrive
Quantum computing is a different kind of challenge.
In The Harvest Is Done: A CISO's Take on the Quantum Cryptography Threat, Connie McIntosh looks at what quantum computing could mean for today’s cryptographic foundations and why organizations need to start preparing now.
Her advice is practical: “You must start with the inventory and mapping your dependencies.”
Across all four conversations, the message is consistent: the CISO’s agenda is increasingly about looking ahead: understanding what is changing, where dependencies are emerging, and what the organization needs to prepare for next.
Explore The CISO Perspective for these conversations and more, including M&A, critical infrastructure, cyber sovereignty and the broader business role of the CISO.