Passwordless authentication is essential for digital identity security, differing in enterprise and consumer markets. Solutions must balance security, usability, and cost, focusing on user experience for adoption. Vendors excel at either integration depth or niche innovation, presenting buyers with a choice between consolidation and specialization, aligning with identity governance and security strategies.
Why don't you like this?


Description
Short Summary
Interesting Facts
Notable Quotes
Recommendations
Takeaways
Executive Summary
Passwordless authentication is no longer a novelty; it is a necessary evolution of digital identity security. Many enterprises and service providers still cling to passwords, often for legacy or perceived user convenience reasons, even though the security and usability arguments against passwords are now overwhelming. However, enterprise and consumer passwordless solutions diverge in design and expectations. In this context, “consumer” refers specifically to end users outside the enterprise workforce, typically individuals who access public-facing digital services such as banking applications, online retail services, government portals, healthcare portals, and telecom applications.
Enterprises can tolerate more controlled workflows aligned with Identity and Access Management (IAM) policies, while consumers demand seamless omnichannel journeys, intuitive self-service, strong privacy controls, and consistent experiences across any device. Consumer-focused offerings must also operate securely in unmanaged environments and meet strict regulatory requirements such as the European Union’s General Data Protection Regulation (GDPR). Although both domains pursue secure authentication, they differ in how they balance security, usability, and scalability. Organizations evaluating passwordless options should weigh these factors alongside implementation effort, interoperability, and cost, with user experience remaining central to successful adoption.
From our perspective, the market is moving toward a clear separation between vendors offering passwordless as a module within a broad IAM ecosystem and those delivering highly specialized, agile solutions. The former offers depth and integration; the latter provides speed of innovation and niche expertise. The challenge for buyers will be choosing between consolidation and specialization and ensuring that passwordless implementation aligns with broader identity governance and security strategies.
In this Leadership Compass, we assess solutions that lay the groundwork for customers in adopting passwordless authentication. To better understand the fundamental principles this report is based on, please refer to KuppingerCole’s Research Methodology.
Key Findings
What are the top considerations buyers should know about?
- Passwordless adoption is accelerating in both enterprise and consumer markets, with heightened interest in phishing-resistant methods aligned to Fast Identity Online 2 (FIDO2) and Web Authentication (WebAuthn).
- Consumer IAM (CIAM)-focused and-supporting vendors commonly deliver capabilities such as frictionless user experiences, including cross-device passkey portability, biometric enrolment, and social identity integration.
- Passkeys are gaining significant momentum, particularly for consumer use, but adoption remains limited by ecosystem readiness and user device diversity.
- Multifactor passwordless approaches that combine biometrics, device trust, and contextual risk are becoming standard for high-assurance environments, including certain CIAM use cases.
- Solutions aligned with the Federal Risk and Authorization Management Program (FedRAMP), electronic Identification, Authentication and Trust Services (eIDAS), and the National Institute of Standards and Technology (NIST) are differentiating in regulated industries, especially government and financial services.
- Specialist vendors tend to innovate faster than large IAM suites in device-independent authentication, offline workflows, and shared endpoint scenarios.
- Behavioral biometrics and Artificial Intelligence (AI)-driven continuous authentication are emerging as differentiators for detecting anomalous activity post-login.
- Deployment flexibility (on-premises, cloud hybrid) remains critical, especially in highly regulated or data sovereignty-sensitive sectors.
- Buyers increasingly expect passwordless platforms to offer orchestration, analytics, and integration with Identity Threat Detection and Response (ITDR).
Market Analysis
The market for passwordless authentication in consumer and customer-facing use cases has moved from experimentation to mainstream adoption. Most of the larger digital businesses now have active initiatives to reduce or remove passwords in their CIAM environments, driven by Account Takeover (ATO) Fraud, compliance pressure, and usability issues around traditional credentials. At the same time, many organizations still operate hybrid models where passwords exist in the background, or as fallbacks, even when the primary user experience is passwordless.
A major accelerator has been the broad ecosystem support for FIDO2, WebAuthn, and passkeys by Apple, Google, and Microsoft. Native platform support has turned what used to be specialist capabilities into something that can be consumed via browsers, mobile operating systems, and built-in authenticators. For CIAM especially, this has made phishing-resistant authentication practical at scale, including for high-risk segments such as financial services, e-commerce, and digital-native brands.
Vendors in this market can broadly be grouped into two categories. On one side are CIAM and broader IAM platforms that embed passwordless as part of a larger identity fabric, offering strong integration into directories, Single Sign-On (SSO), consent management, and customer data platforms. On the other side are specialists with narrowly focused, highly optimized passwordless and fraud prevention technologies, often delivering advanced behavioral biometrics, device intelligence, or orchestration capabilities. Buyers must decide whether to consolidate on a platform or combine several focused components.
From a capability perspective, passwordless for Business-to-Consumer (B2C) is no longer only about authentication at login. Leading solutions combine passkeys or other phishing-resistant methods with adaptive risk engines, fraud detection, and behavioral biometrics to maintain trust throughout the customer session and during high-risk transactions. In many deployments, passwordless authentication is tightly coupled with identity verification at onboarding to bind a verified real-world identity to a trusted device or credential.
Despite this progress, the market is not yet fully mature. Ecosystem readiness is uneven: older browsers and devices, legacy backend applications, and third-party services that still require usernames and passwords, continue to constrain full passwordless roll-out. Many organizations also face user acceptance and education challenges, especially in segments where customers are accustomed to passwords and Short Message Service (SMS) One-Time Passwords (OTPs). As a result, passwordless is often introduced gradually, starting with low-friction options (with passkeys as the “recommended” logon, for example) and only later deprecating passwords.
Finally, passwords are unlikely to disappear completely in the near term. Even advanced deployments typically retain some form of password or alternative fallback path for account recovery, shared devices, or edge cases. In practice, passwordless becomes the default and visible mode of strong authentication, while passwords are pushed into the background or tightly constrained. Selecting the right solution therefore means not only enabling modern authenticators but also managing coexistence with legacy methods, recovery processes, and regulatory requirements in a way that fits each organization’s customer base and risk profile.
Key Market Trends and Innovations
- Ecosystem support for FIDO2/WebAuthn and passkeys from Apple, Google, and Microsoft have significantly increased public awareness and adoption readiness.
- Most leading solutions now align with these standards, ensuring interoperability and phishing resistance.
- Combining device-bound authentication with biometrics and contextual signals is becoming best practice, particularly for regulated industries.
- Vendors are developing solutions that break dependency on a single personal device and extend support to shared-device scenarios, including for consumers.
- AI-driven monitoring of typing patterns, mouse movement, and other behaviors is being used to maintain session integrity beyond login.
- Some vendors are exploring decentralized identity storage to further reduce credential theft risk. This is expected to gain further momentum with the introduction of the European Digital Identity Wallet (EUDIW) from 2026, offering strong identity verification and support for decentralized identity standards.
- Innovation is visible in recovery workflows that avoid reintroducing passwords, using trusted devices, passkey re-binding, step-up proofing, and help-desk–assisted flows with strong verification, recognizing recovery as a primary attack vector.
- Especially in CIAM, vendors are integrating identity verification at onboarding, linking strong initial proofing to passwordless authentication.
- Within five years, passkeys and phishing-resistant passwordless methods will be the default for most new CIAM deployments. This will also drive migration away from username/password authentication in these environments.
Delivery Models
Passwordless authentication for consumers in the Business to Consumers (B2C) context is predominantly delivered as cloud-based Software as a Service (SaaS), either as a standalone CIAM service or as part of a broader identity platform. Multitenant cloud environments allow vendors to manage global peak loads, provide frequent capability updates (for example, new authenticator support or risk signals), and offer standardized Service Level Agreements (SLAs) for availability and response times. For many organizations, especially digital-native businesses and online retailers, SaaS is the default choice due to the speed of integration and reduced operational overhead.
At the same time, deployment flexibility remains important. Regulated sectors and organizations with strict data residency and sovereignty requirements often demand regional hosting options, private cloud deployments, or managed services that run in their own Infrastructure as a Service (IaaS) environment. Some vendors also offer on-premises or hybrid models based on containerized microservices, which can be useful where integration with legacy systems, internal data stores, or local Hardware Security Modules (HSMs) is required.
For B2C use cases, licensing models typically follow per-Monthly Active User (MAU) or per-transaction pricing, sometimes with dedicated add-ons for identity verification, fraud analytics, or premium support. Buyers should understand how authentication volumes, seasonal peaks, and growth projections affect total cost, and how pricing scales when passwordless methods are adopted more broadly across brands and channels.
Required Capabilities
Selecting a passwordless solution for consumers requires attention to both technical capabilities and broader operational and commercial aspects. The goal is to balance high assurance, strong fraud resistance, and regulatory compliance with a low-friction user experience and manageable cost.
Technical and Functional Criteria
- Breadth and depth of authentication methods. Look for comprehensive support for FIDO2/WebAuthn, passkeys, platform authenticators (Face ID, Windows Hello, Android biometrics), and hardware tokens where required. This is essential for high-risk use cases such as banking and large e-commerce platforms, and for gradually replacing SMS OTPs and passwords with phishing-resistant factors.
- Adaptive risk and fraud prevention. Solutions should ingest contextual and behavioral signals (Internet Protocol (IP) reputation, device fingerprinting, geo-velocity, device health, behavioral biometrics) and expose them via risk scores or policies. This is critical for detecting account takeover, Bot traffic, and social engineering in real time, especially during payments, profile changes, and high-value actions.
- Risk policy management and orchestration. A flexible policy engine, ideally with graphical flows as well as Application Programming Interface (API) and JavaScript Object Notation (JSON) -based configuration, is needed to define when to allow, challenge, or block. Buyers should ensure that policies can combine multiple signals, perform step-up authentication, and integrate with external fraud or authorization engines, which is important when orchestrating complex customer journeys.
- Device lifecycle and trust management. The solution should provide clear workflows for device enrollment, binding, and revocation across mobiles, desktops, and potentially Internet of Things (IoT) devices or wearables. For example, banks and telcos must manage lost/stolen devices and support customers who use multiple or shared endpoints, while maintaining strong assurance of which devices are trusted.
- User provisioning, onboarding, and self-service. For CIAM, strong support is required for self-registration, consent capture, and integration with identity proofing (where needed), as well as for linking identities across channels. Bulk import and synchronization with existing directories or customer databases remain important for phased migrations from legacy CIAM systems.
- Developer experience, APIs, and SDKs. Passwordless must be easy to embed into mobile apps and web frontends. Comprehensive APIs, SDKs for major platforms (iOS, Android, web), and good documentation are key selection factors, especially for digital-native businesses that build their own customer experiences and require deep customization.
- User experience and UI flexibility. Buyers should assess how enrollment, login, step-up prompts, and recovery are presented to end users, and how easily these flows can be customized to match brand and accessibility requirements. Good User Experience (UX) is a primary success factor in B2C scenarios where abandoned registrations or logins directly reduce revenue.
- Account recovery and fallback mechanisms. Evaluate how users regain access when devices or authenticators are lost, and to what extent recovery can avoid reverting to weak passwords. For example, recovery via another trusted device, identity verification, or orchestrated help-desk flows are particularly relevant in regulated industries and high-risk segments.
- Standards and integration capabilities. Support for Security Assertion Markup Language (SAML), Open Authorization 2.0 (OAuth 2.0), OpenID Connect (OIDC), System for Cross-domain Identity Management (SCIM), and relevant regional standards are essential to integrate passwordless into existing CIAM, CRM, and marketing stacks. Organizations with diverse application landscapes should prioritize vendors with proven connectors and integration patterns.
Operational, Compliance, and Commercial Criteria
- Architecture, scalability, and performance. Modern, microservices-based architectures with elastic scaling, global data centers, and clear SLAs for uptime and latency are important for consumer-scale environments. Buyers should ask for reference values (peak login per second, largest deployment sizes) and assess how these fit with their expected growth and peak usage patterns.
- Compliance, data protection, and residency. Vendors must support relevant regulations such as the Revised Payment Services Directive (PSD2), Strong Customer Authentication (SCA) requirements, Electronic Identification, Authentication and Trust Services (eIDAS), Network and Information Security Directive 2 (NIS2), and the GDPR, and must provide options for data localization and clear data processing boundaries. This is especially important for financial services, the public sector, and globally operating brands subject to multiple regulatory regimes. Also check for FIDO certification of the related components.
- Security assurances and cryptographic robustness. Hardware-backed key protection, secure key storage, use of HSMs, and well-documented cryptographic implementations are important evaluation points. Independent certifications or audits, where available, provide additional assurance for high-risk use cases. Consider the vendor’s plans related to quantum safe encryption.
- Vendor maturity and product roadmap. Buyers should consider reference customers, financial stability, and the clarity of the roadmap around passkeys, identity wallets, behavioral analytics, and fraud integration. For long-lived CIAM deployments, the ability of a vendor to align future development with emerging regulations and standards is crucial.
- Total cost of ownership and licensing flexibility. Understanding pricing models (per MAU, per transaction, or tiered bundles for fraud and proofing) is essential. Organizations should model costs under realistic adoption scenarios, including growth in registered users, increased login frequency after simplifying UX, and seasonal peaks in e-commerce.
- Support, operations, and ecosystem partnerships. Finally, evaluate the quality of support, availability of professional services and integration partners, and the breadth of the vendor’s ecosystem. Complex CIAM and passwordless projects often involve multiple stakeholders, and strong vendor and partner support can significantly reduce implementation risk and time to value.
Leadership
As always, this year's report serves as a useful guide, but it is not a prescription. The Leadership Compass should be the start of the conversation, not the end. Organizations must look beyond the charts and think critically about their unique B2C requirements, whether that is mobile-first experiences, accessibility compliance, integration complexity, or specific industry regulations. Vendors may occupy impressive positions on the chart, but the true test lies in their ability to solve real-world consumer authentication challenges while maintaining the seamless experiences that modern consumers demand.
Selecting a vendor of a product or service must not be based only on the information provided in this KuppingerCole Leadership Compass. The Leadership Compass provides a comparison based on standardized criteria and can help identify vendors that should be considered for further evaluation. However, a thorough selection process should include a detailed analysis and a Proof of Concept of pilot phase, based on the specific criteria of the customer.
Our rating methodology determines each vendor’s position in four leadership categories:
- Overall Leadership
- Product Leadership
- Innovation Leadership
- Market Leadership
Overall Leadership
The Overall Leadership chart reflects how vendors balance product strength, innovation, and market presence. The chart evaluates vendors in this market across two dimensions. The horizontal axis measures Product Leadership, and the vertical axis measures Innovation Leadership. Overall Leaders are those in the upper right-hand quadrant, with the bubbles colored red. Vendors in this quadrant score highly in both dimensions, earning Overall Leadership status. These organizations ship mature products while maintaining strong innovation.
The bubble size reflects each vendor's relative strength in terms of Market Leadership. Further details on Market Leadership can be found in the Market Leadership section.
Product Leaders are found to the right of the vertical dividing line. The vendors in the lower right quadrant, colored black, are established vendors with full-featured products but fewer innovative differentiators. These providers demonstrate solid execution using conventional methods. Further details on Product Leadership can be found in the Product Leadership section.
Innovation Leaders are found above the horizontal dividing line. Vendors in the upper left-hand quadrant, colored black, have advanced technology approaches but less mature product offerings. These companies often introduce new technical approaches that are not yet widely adopted. Further details on Innovation Leadership can be found in the Innovation Leadership section.
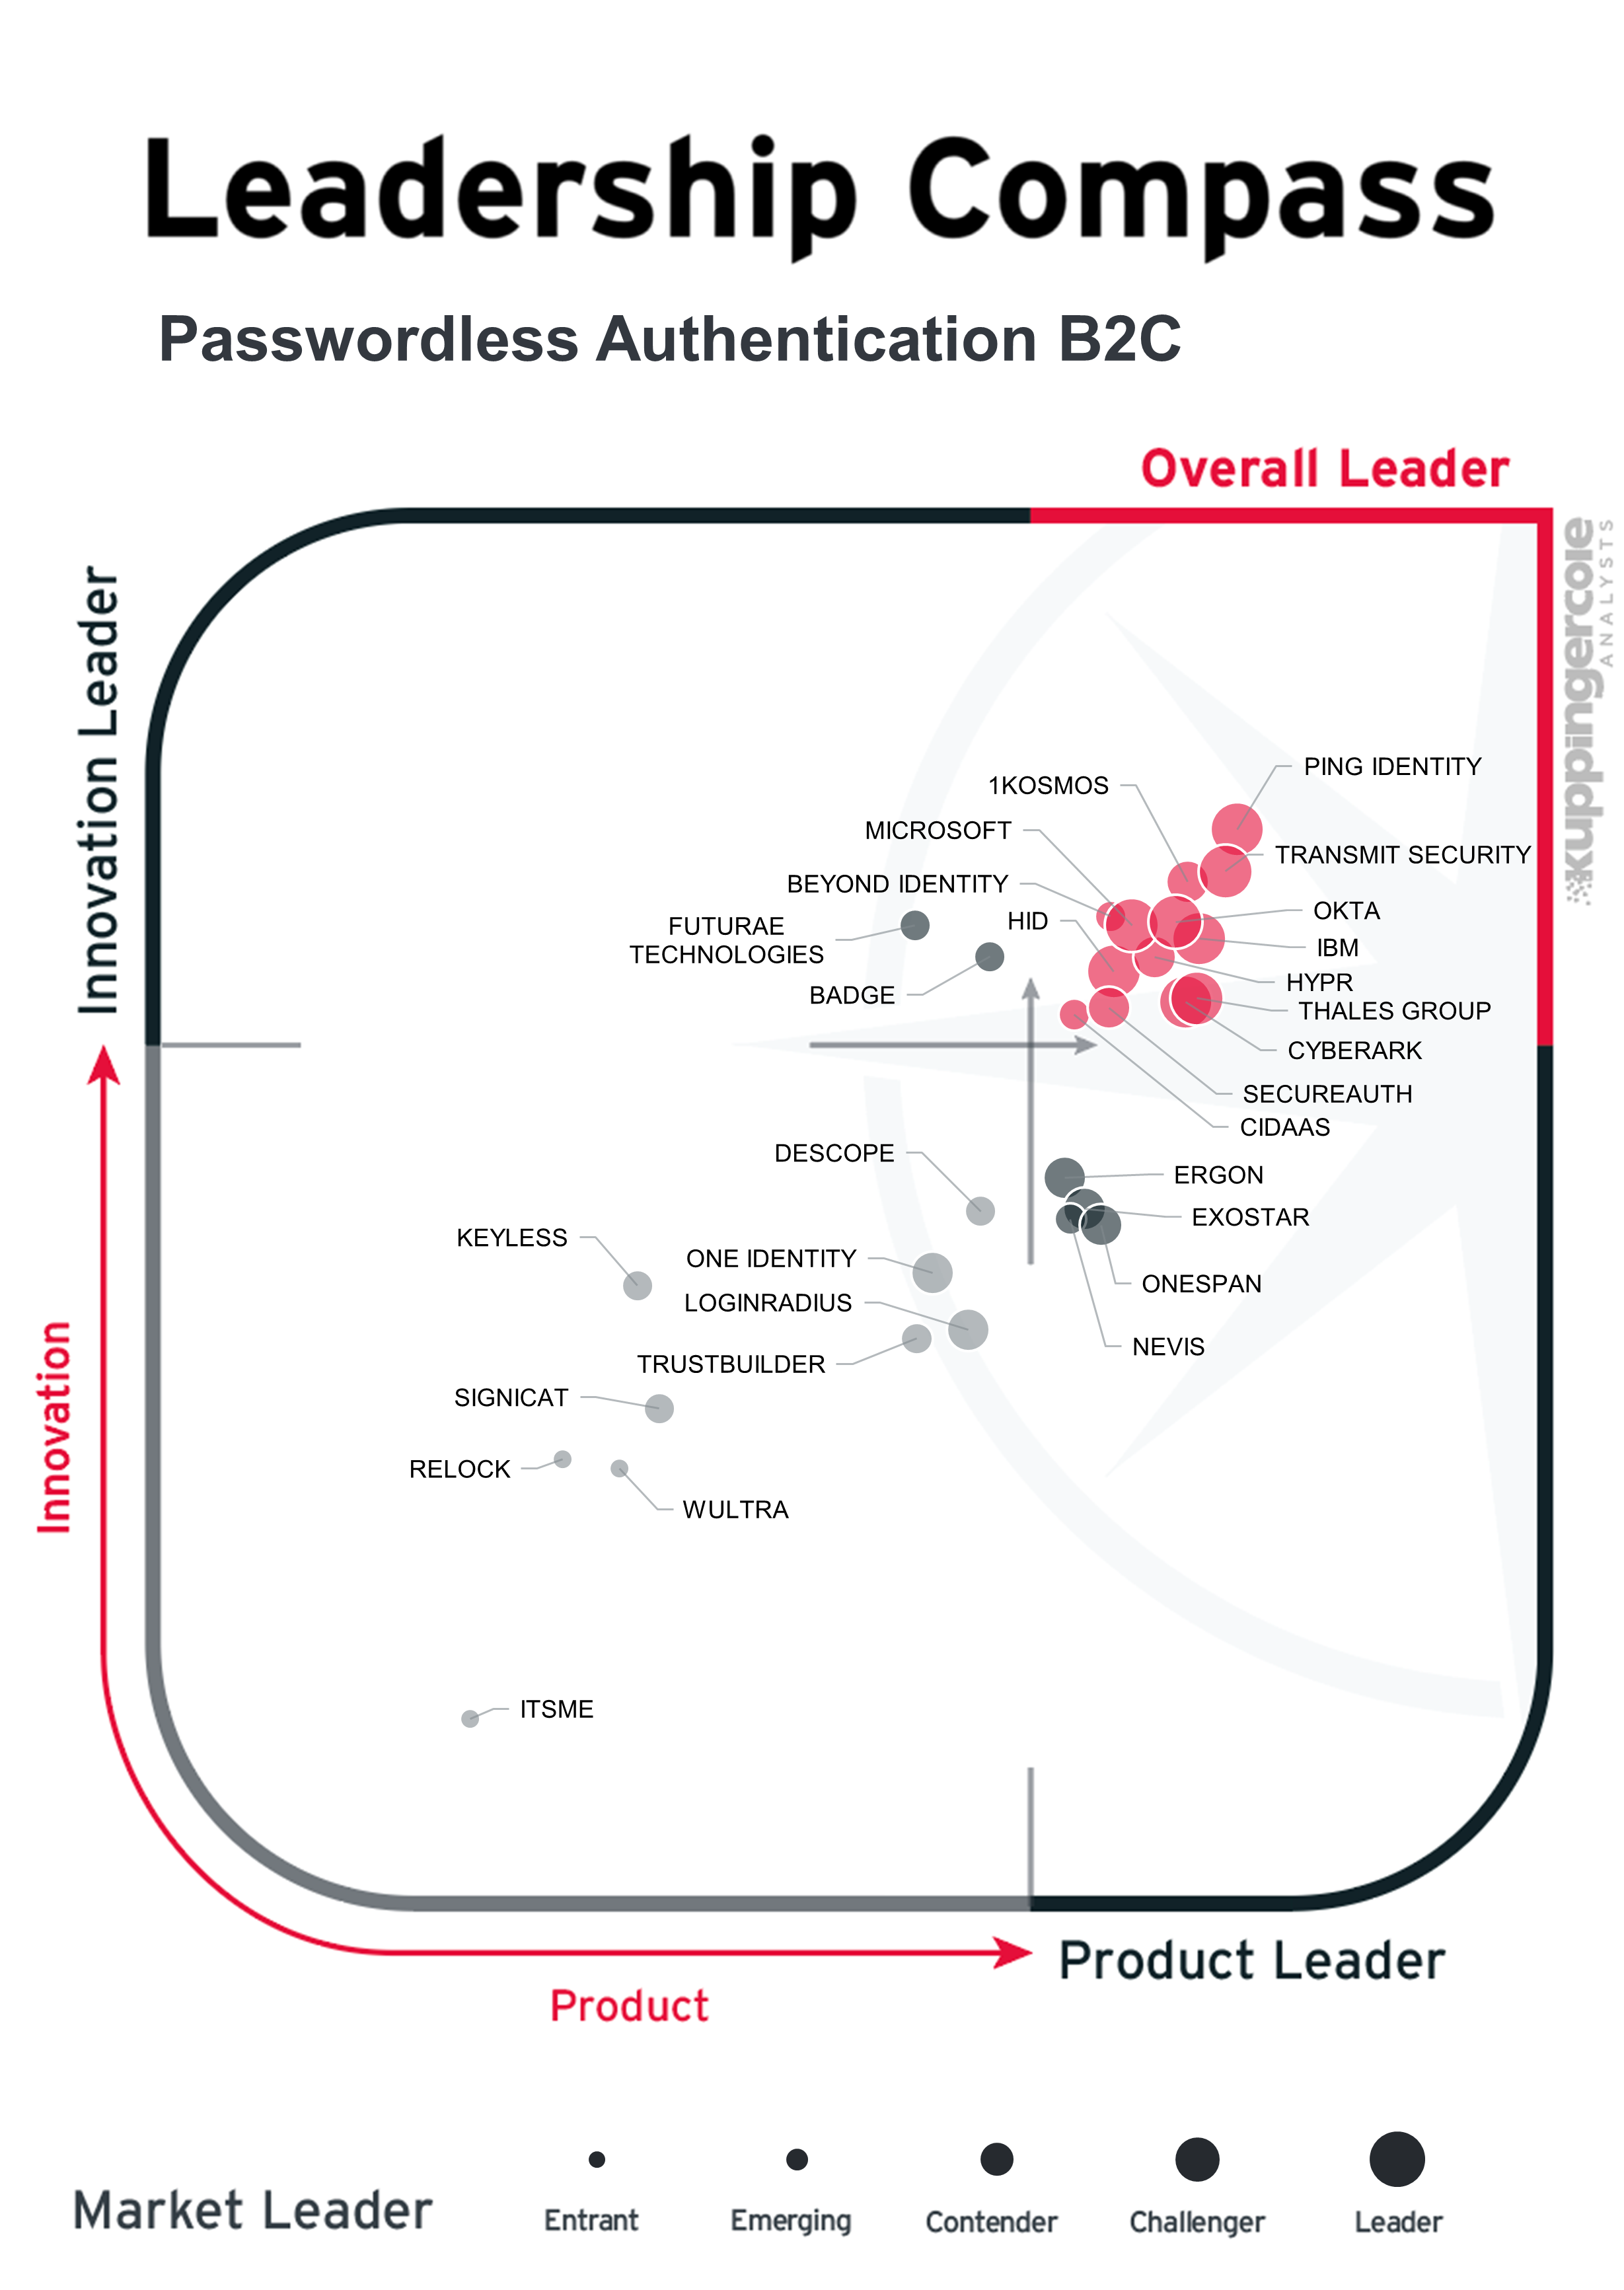
Figure 1: Overall Leadership in the B2C Passwordless Authentication market.
Vendors in the lower left-hand quadrant, colored grey. are challengers for both product and innovation leadership. Those toward the bottom left-hand corner are mainly niche vendors with products focused on specific market segments and geographical areas.
The top Overall Leaders are Ping Identity, 1Kosmos, and Transmit Security.
Ping Identity stands out with its combination of FIDO2-certified passkey authentication, advanced adaptive risk detection, and a highly flexible no-code orchestration platform, DaVinci. This enables organizations to design seamless consumer identity journeys.
1Kosmos Customer is recognized for its privacy-preserving architecture that uses blockchain to secure identity data, effectively unifying high-assurance identity proofing with FIDO2/WebAuthn-based authentication on a single platform.
Transmit Mosaic integrates CIAM, fraud detection, and identity verification in a unified platform, providing passwordless authentication based on FIDO standards which strengthens every authentication and recovery process with device intelligence, behavioral analytics, and real-time fraud risk scoring.
Other vendors with Overall Leadership include Beyond Identity, CyberArk, HID, HYPR, IBM, Microsoft, Okta with Auth0, SecureAuth and Thales Group. Beyond Identity provides phishing-resistant Multifactor Authentication (MFA) combined with continuous device trust and risk-based policy enforcement. cidaas with integrated fraud detection and identity verification positioned around eIDAS, CyberArk extends its privileged account management to incorporate passwordless authentication, SSO, MFA, and CIAM-focused user management. HID offers a broad range of FIDO-certified hardware as well as software to provision, reset and manage passkeys at scale, while HYPR delivers complete end-to-end solutions with FIDO-certified passwordless MFA and integrated identity verification. IBM Verify brings passwordless authentication with adaptive access analytics powered by Trusteer, while Microsoft Entra provides extensive support for FIDO2 passkeys underpinned by Azure's global infrastructure. Okta, leveraging Auth0, provides globally distributed authentication services, enriched with adaptive risk intelligence. SecureAuth with its adaptive, identity-threat detection and anomaly modelling to provide early detection of identity-based attacks. Thales Group provides phishing-resistant authenticators (including device-bound passkeys) to address a broad range of passwordless authentication needs.
Futurae Technologies is an Innovation Leader for its “Multi-Factor-in-the-Background” and Trust Signals (formerly referred to by Futurae as “User Risk Radar”) but not an Overall Leader based on its product capabilities.
Badge, with its ability to unify authentication processes across devices without relying on permanent storage of user credentials or biometrics, is an innovation leader.
Niche vendors and vendors with a strong local presence that is limited to some geographies or market segments are Descope, Futurae Technologies, itsme, Keyless, LoginRadius, One Identity, Relock, Signicat, TrustBuilder and Wultra.
For global enterprises, the vendors in the Leaders quadrant offer proven capabilities, a global presence and scalability. However, vendors may differ significantly from each other in terms of product details, features, innovation, and market leadership. Therefore, buyers should also consider how the other capabilities described in the sections covering each vendor and their products would best support their use cases.
Product Leadership
Product leadership is the first specific category examined below. This view is based on the presence and completeness of required features as defined in the required capabilities section above. The chart is horizontal and divided into two areas, the vendors to the right of the chart and colored red are Product Leaders and those to the left and colored black are Product Leadership Challengers.
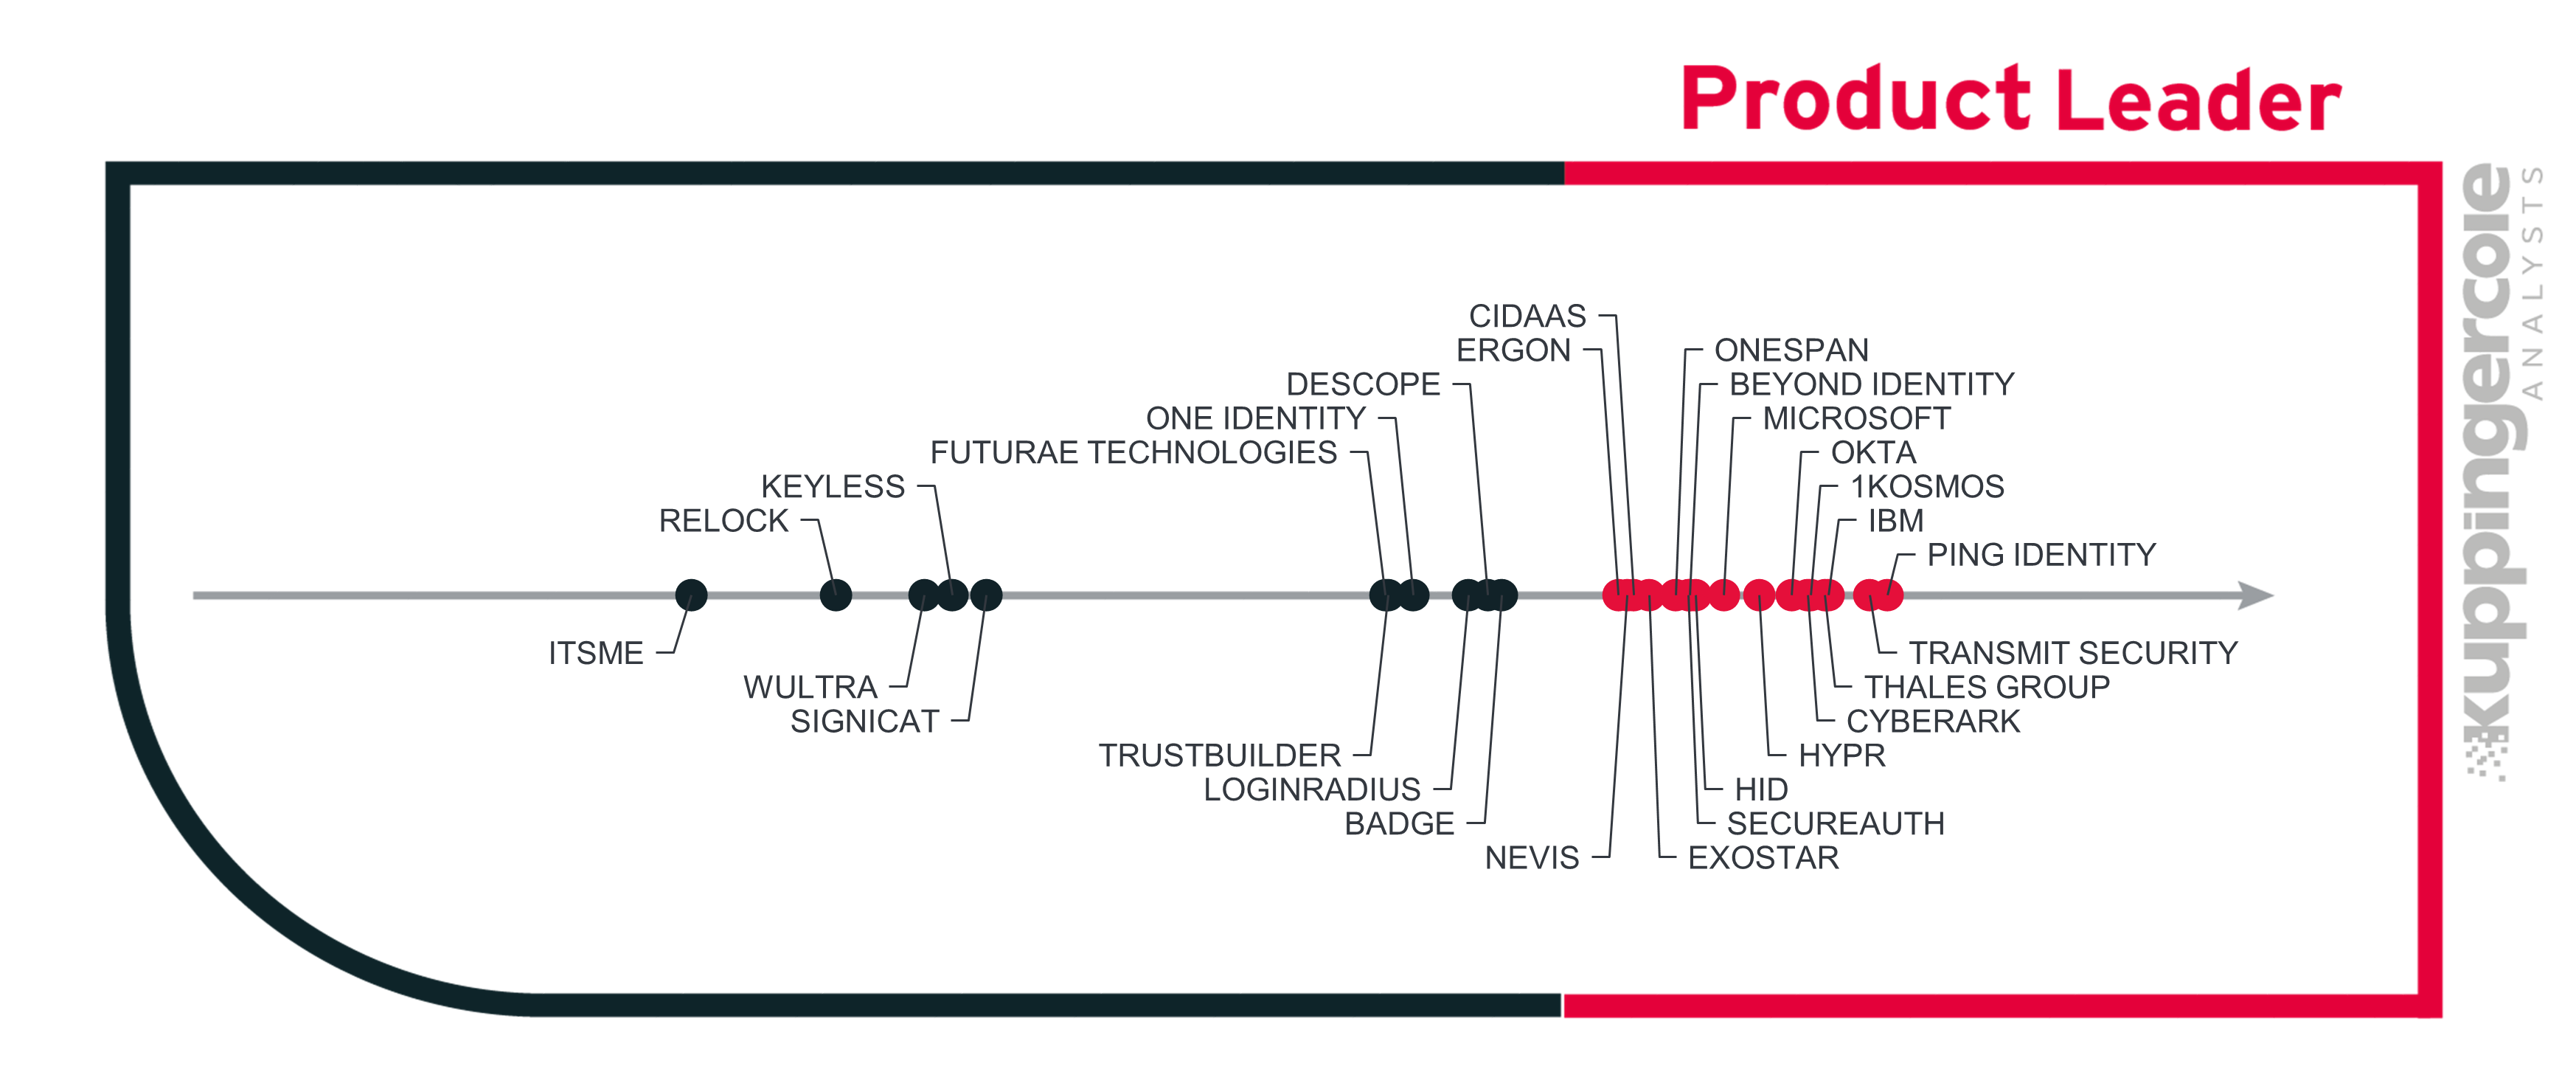
Figure 2: Product Leadership in the B2C Passwordless Authentication market.
Ping Identity is the top product leader in this report, offering a combination of FIDO2-certified passkey authentication, advanced adaptive risk detection, and a highly flexible no-code orchestration platform (DaVinci) that enables organizations to design frictionless consumer identity journeys.
The following group of vendors with strong Product Leadership are IBM, Transmit Security, 1Kosmos, CyberArk, and Okta. IBM integrates FIDO2 passkeys with IBM Trusteer’s advanced fraud detection, creating risk-adaptive passwordless authentication. Transmit Security provides a no-code orchestration platform that unifies passkeys, device intelligence, and fraud signals for adaptive, passwordless B2C journeys. 1Kosmos combines passwordless passkeys with a blockchain-secured, verifiable digital identity, enabling strong authentication tied to a cryptographically validated user identity. CyberArk extends enterprise-grade privileged access security controls to consumers, bringing privileged-class authentication protections to B2C use cases. Okta / Auth0 delivers developer extensibility through Actions/Rules, enabling custom logic and integrations inside passkey and passwordless flows.
Following these is a tightly packed group of vendors that all offer excellent products. These are Microsoft, HID, Beyond Identity, SecureAuth, OneSpan, Thales Group HYPR, Exostar, Nevis, cidaas, and Ergon (Airlock).
Microsoft (Entra External ID) offers the most powerful policy orchestration for passkeys via custom policies, enabling highly bespoke B2C passwordless journeys at global scale. HID unifies FIDO passkeys with a powerful system that offers continuous risk assessment prior to authentication, enabling real-time threat detection improving HID's broad range of authenticators that support passwordless authentication in one solution. Beyond Identity eliminates shared secrets entirely by binding identity to cryptographic keys stored securely on the user’s device, creating a passwordless model with no passwords, OTPs, or passcodes. SecureAuth uses adaptive, identity-threat detection and anomaly modelling to shape passwordless authentication, offering early detection of identity-based attacks. OneSpan (DIGIPASS S3) Combines FIDO passkeys with deep device-health, transaction signing, and Secure Payment Confirmation for high-risk, transaction-oriented consumer sectors.
Thales Group (OneWelcome) combines highly regulated CIAM with strong passwordless identity that integrates with national eIDs and verified credentials, ideal for compliance-driven industries. HYPR provides “Identity Assurance” that merges passkeys with identity verification, ensuring each passwordless login is tied to a previously verified person. Exostar enables cross-enterprise passwordless access across complex multi-supplier ecosystems, allowing a single secure identity across aerospace, defence, and high-assurance partner networks.
Nevis Security brings banking-grade transaction signing and passwordless login through a FIDO-based Authentication Cloud, proven in national e-banking environments. cidaas provides omnichannel passwordless login across web, mobile, IoT, smart kiosks and physical touchpoints, supporting consistent journeys across all consumer-facing channels. Ergon (Airlock) combines CIAM, Web Application Firewall, and API Security with passwordless authentication in a unified perimeter, integrating identity with application security.
Challengers include niche vendors and those with a strong local presence that is limited to some geographies or market segments are Badge, Descope, Futurae Technologies, itsme, Keyless, LoginRadius, One Identity, Relock, Signicat, TrustBuilder and Wultra.
Innovation Leadership
Next, we examine innovation in the marketplace. Innovation is, from our perspective, a key capability in all IT market segments. Customers require innovation to meet evolving and even emerging business requirements. Innovation is not about delivering a constant flow of new releases. Rather, innovative companies take a customer-oriented upgrade approach, delivering customer-requested and other cutting-edge features, while maintaining compatibility with previous versions.
This view is based on the evaluation of innovative features recently added together with the vendor’s history in innovation. The chart is horizontal and divided into two areas, the vendors to the right of the chart and colored red are Innovation Leaders and those to the left and colored black are Innovation Leadership Challengers.
Innovation Leaders are those vendors that deliver cutting-edge products, not only in response to customers’ requests but also because they are driving technical changes in the market by anticipating what will be needed in the months and years ahead.
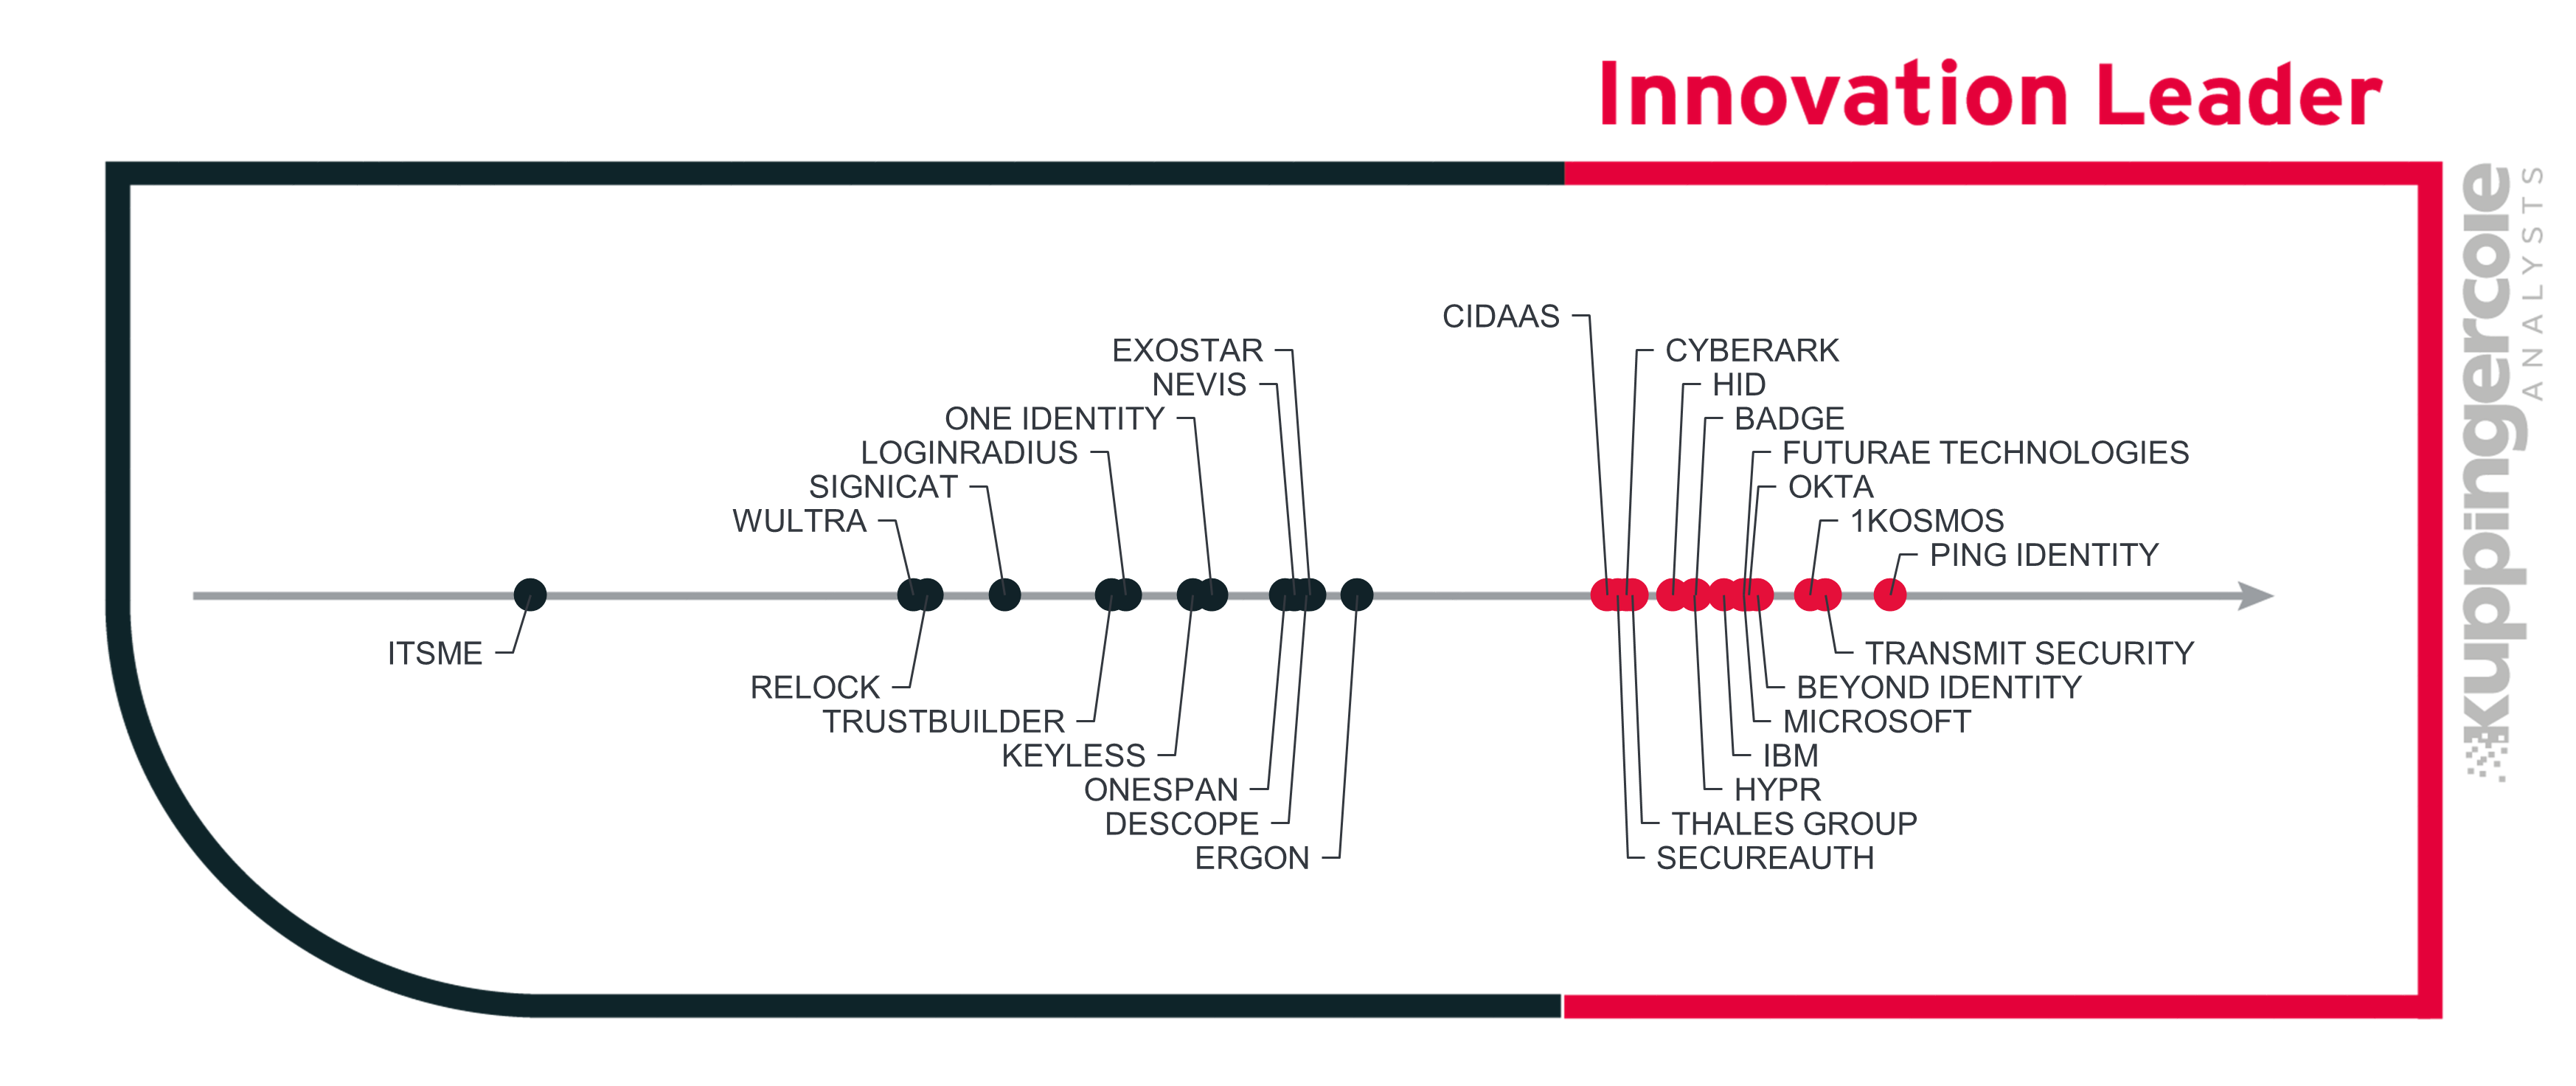
Figure 3: Innovation Leadership in the B2C Passwordless Authentication market.
Ping Identity is the top leader in innovation with orchestration (PingOne DaVinci) and broad standards support, helping organizations to integrate passkeys, risk engines, and fraud services into tailored B2C flows.
The next leading vendors are 1Kosmos and Transmit Security. 1Kosmos blends FIDO2 passwordless with a unique blockchain protected digital identity that has been verified to meet the US National Institute of Standards and Technology (NIST) requirements for Identity Assurance Level 2 (IAL2), making identity proofing and authentication part of the same platform. Transmit Security offers a no-code / low-code identity orchestration platform that unifies passkeys, device intelligence, and fraud signals into adaptive B2C journeys.
The other leading vendors in innovation are Badge, Beyond Identity, Okta, Futurae Technologies, Microsoft, IBM, HID, HYPR and CyberArk. Badge uses unique cryptographic techniques to unify authentication processes across devices without relying on permanent storage of user credentials or biometrics. Beyond Identity uses device-bound, certificate-based credentials with no shared secrets (no passwords, no OTPs) to create a phishing-resistant customer login. Okta (incl. Auth0) provides developer tooling and extensibility through Actions / Rules for building bespoke passkey and passwordless flows across large consumer apps. Futurae Technologies pioneers “Multi-Factor-in-the-Background” and Trust Signals, running continuous MFA and risk checks silently. Microsoft (Entra External ID) delivers enterprise-scale passkeys backed and custom policy orchestration for complex B2C journeys. IBM, HID and HYPR all combine FIDO passkeys with integrated risk and fraud analytics bringing bank-grade risk intelligence directly into B2C passkey flows. CyberArk extends its strong enterprise security heritage to B2C by combining risk-aware passwordless authentication with privileged-grade controls for consumer access to sensitive services. SecureAuth which builds a model of each user’s behaviour over time that can be used to assess the risk of each transaction. Thales Group with developments in areas like Brain Computer Interface and Post-Quantum Cryptography, which have the potential to change the future of passwordless authentication. cidaas is an innovation leader with recent developments that include low code / no code orchestration platform with GenAI powered integration options.
Challengers with innovation that is typically focused on narrow areas and that lacks the breadth and depth of the Leaders are: Descope, Ergon (Airlock), Exostar, itsme, Keyless, LoginRadius, Nevis, One Identity, OneSpan, Relock, SecureAuth, Signicat, TrustBuilder, and Wultra.
Market Leadership
Finally, we analyze Market Leadership. This is an amalgamation of the number of customers and their geographic distribution, the size of deployments and services, the size and geographic distribution of the partner ecosystem, and the financial health of the participating companies. Market Leadership, from our point of view, requires global reach.
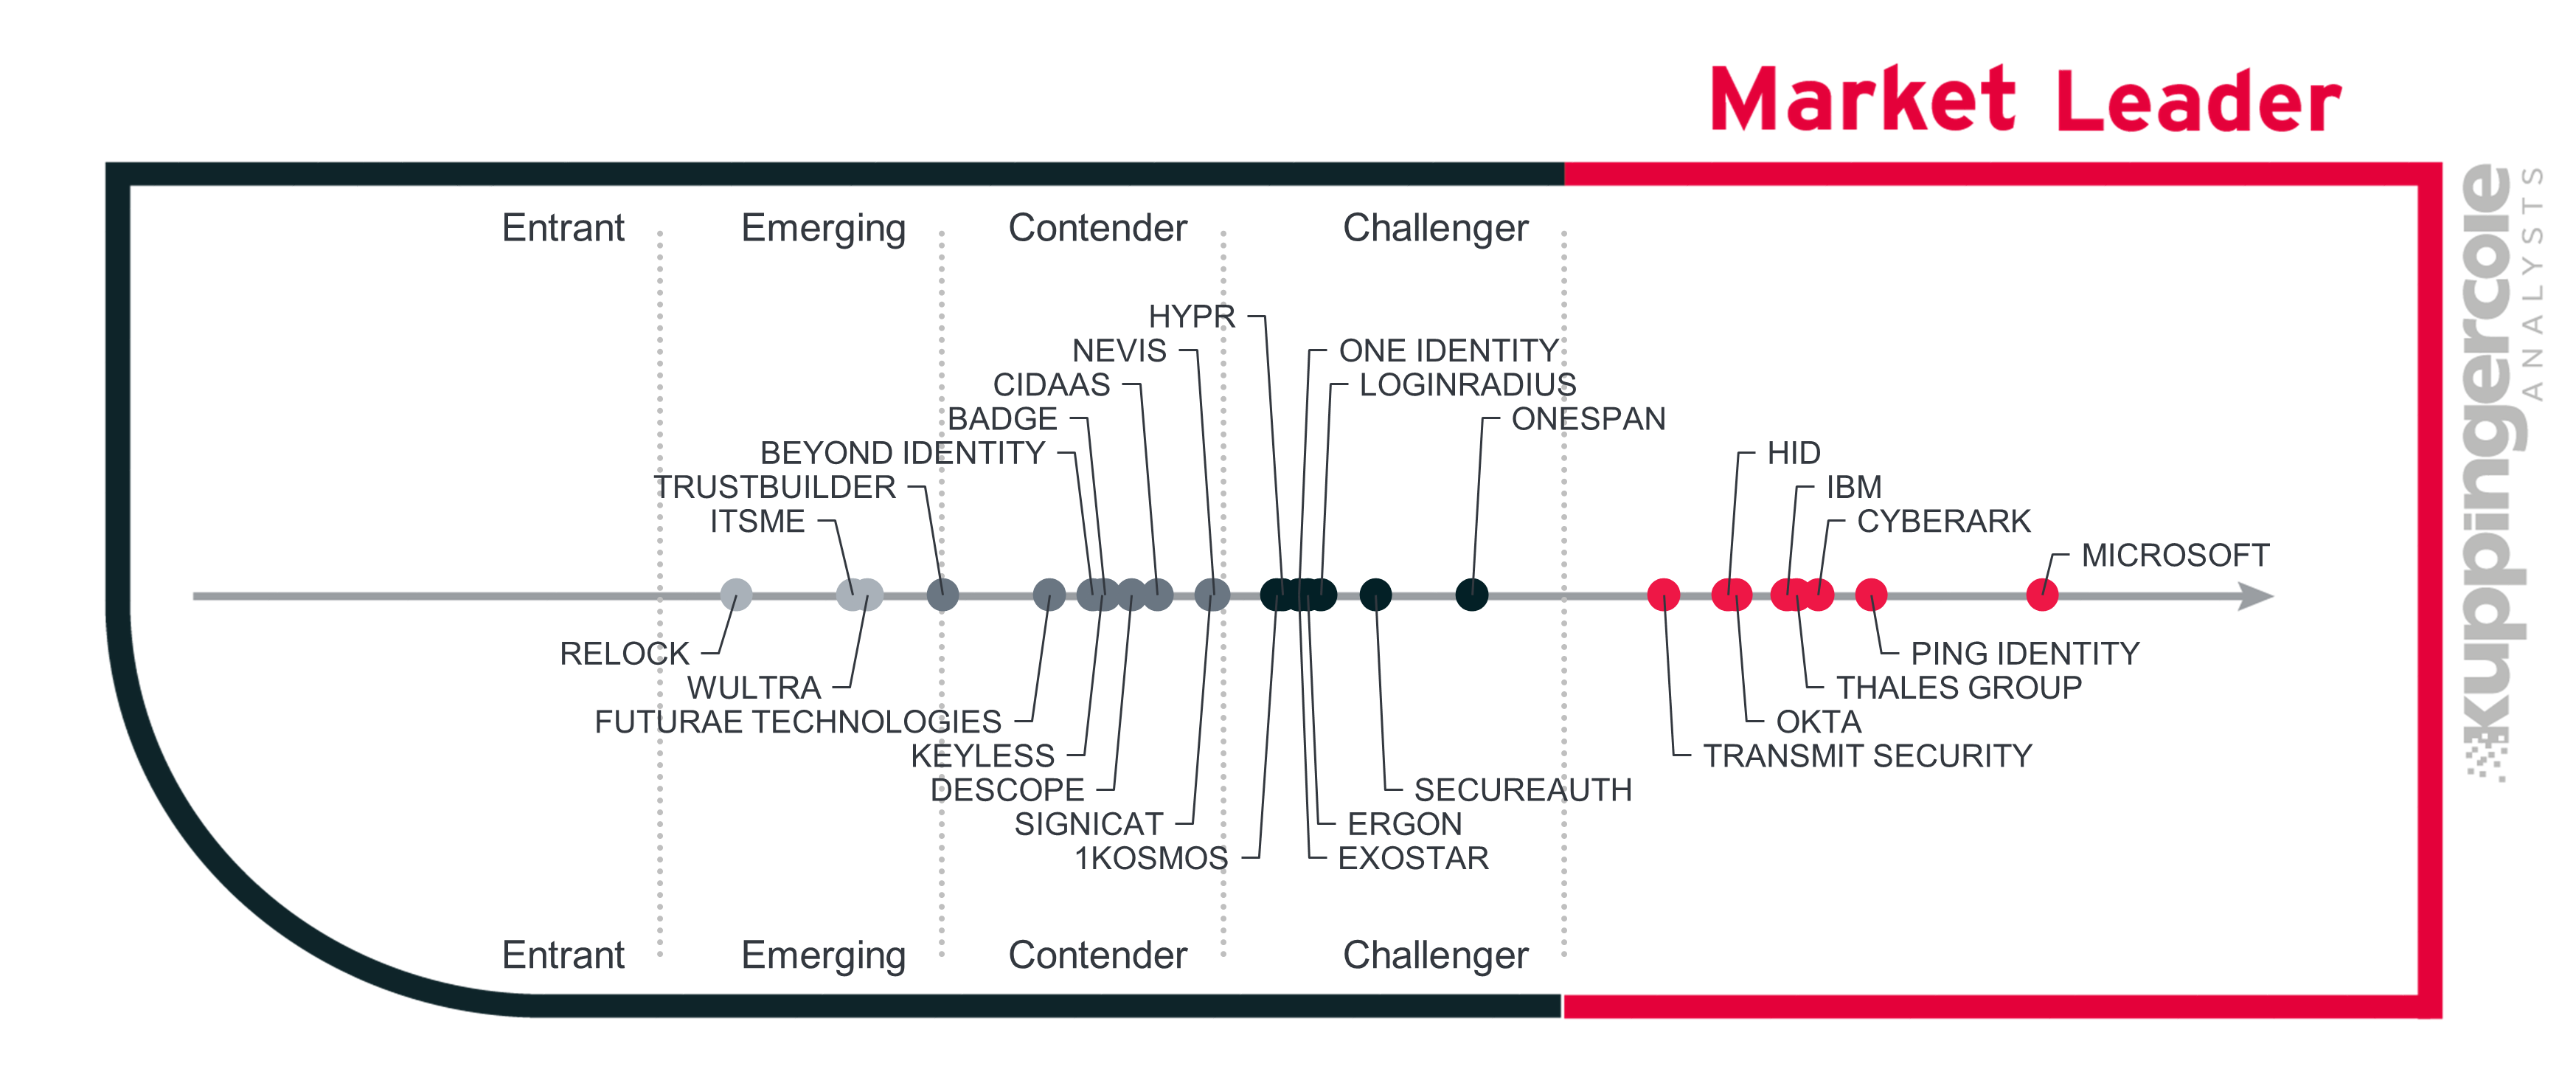
Figure 4: Market Leaders in the B2C Passwordless Authentication Market.
This chart shows the market strength of vendors plotted on the horizontal axis. The chart divides vendors into five categories Leaders, Challengers, Contenders, Emerging, and Entrants. The Market Leaders, shown to the right of the chart and colored red, are those with market dominance and high influence. Market Challengers, shown to the left of leaders and colored black, are strong competitors with significant market presence and growth potential. Contenders, shown in in grey, are solid players with a stable position and reliable offerings. Emerging vendors with a growing presence and the potential for further market impact are colored light grey. Entrants, shown to the left of the chart, are newcomers or smaller players just beginning to establish market presence.
The Market Leaders that dominate the market for B2C passwordless authentication are those with multi-billion-dollar market presence, global customer bases, and partner ecosystems. Microsoft is the Market leader for passwordless authentication due to its unmatched scale, FIDO2-certified infrastructure, and multi-hundred-million user ecosystem around the Microsoft Entra platform.
The next leading vendors are Ping Identity, CyberArk, Thales Group, IBM, Okta, HID, and Transmit Security. These vendors are all market leaders for several reasons. Ping Identity leads because of its strong financial backing, and dominance in large, regulated B2C deployments across finance, telecom, and public sector. CyberArk, with global leadership in privileged access security, has now moved into the broader authentication market for high-assurance B2C use cases. Thales Group leads through its multi-billion-euro security business, leadership in national eID programs, and OneWelcome CIAM platform. IBM, because of its worldwide enterprise penetration, and a mature identity product suite commands a major presence in high-security B2C authentication markets. Okta, because of its massive SaaS CIAM footprint, and Auth0 developer ecosystem. HID, through its hardware-backed and identity-bound authentication and large enterprise and government footprint. Transmit Security – because of its rapid global growth, and a strong foothold in financial services.
The market challengers with a large customer base and strong ecosystem are: OneSpan, SecureAuth, LoginRadius, Ergon, One Identity, Exostar, 1Kosmos and HYPR.
Contenders, solid players with a stable market position and reliable offerings are Badge, Beyond Identity, cidaas, Descope, Futurae technologies, Keyless, Nevis, One Identity, and Signicat.
Emerging vendors with a growing presence and the potential for further market impact are: itsme, Relock, TrustBuilder, and Wultra.
Product/Vendor evaluation
This section contains a quick rating for every product/service we have included in this KuppingerCole Leadership Compass document. For many of the products there are additional KuppingerCole Product Reports and Executive Views available, providing more detailed information.
Spider graphs
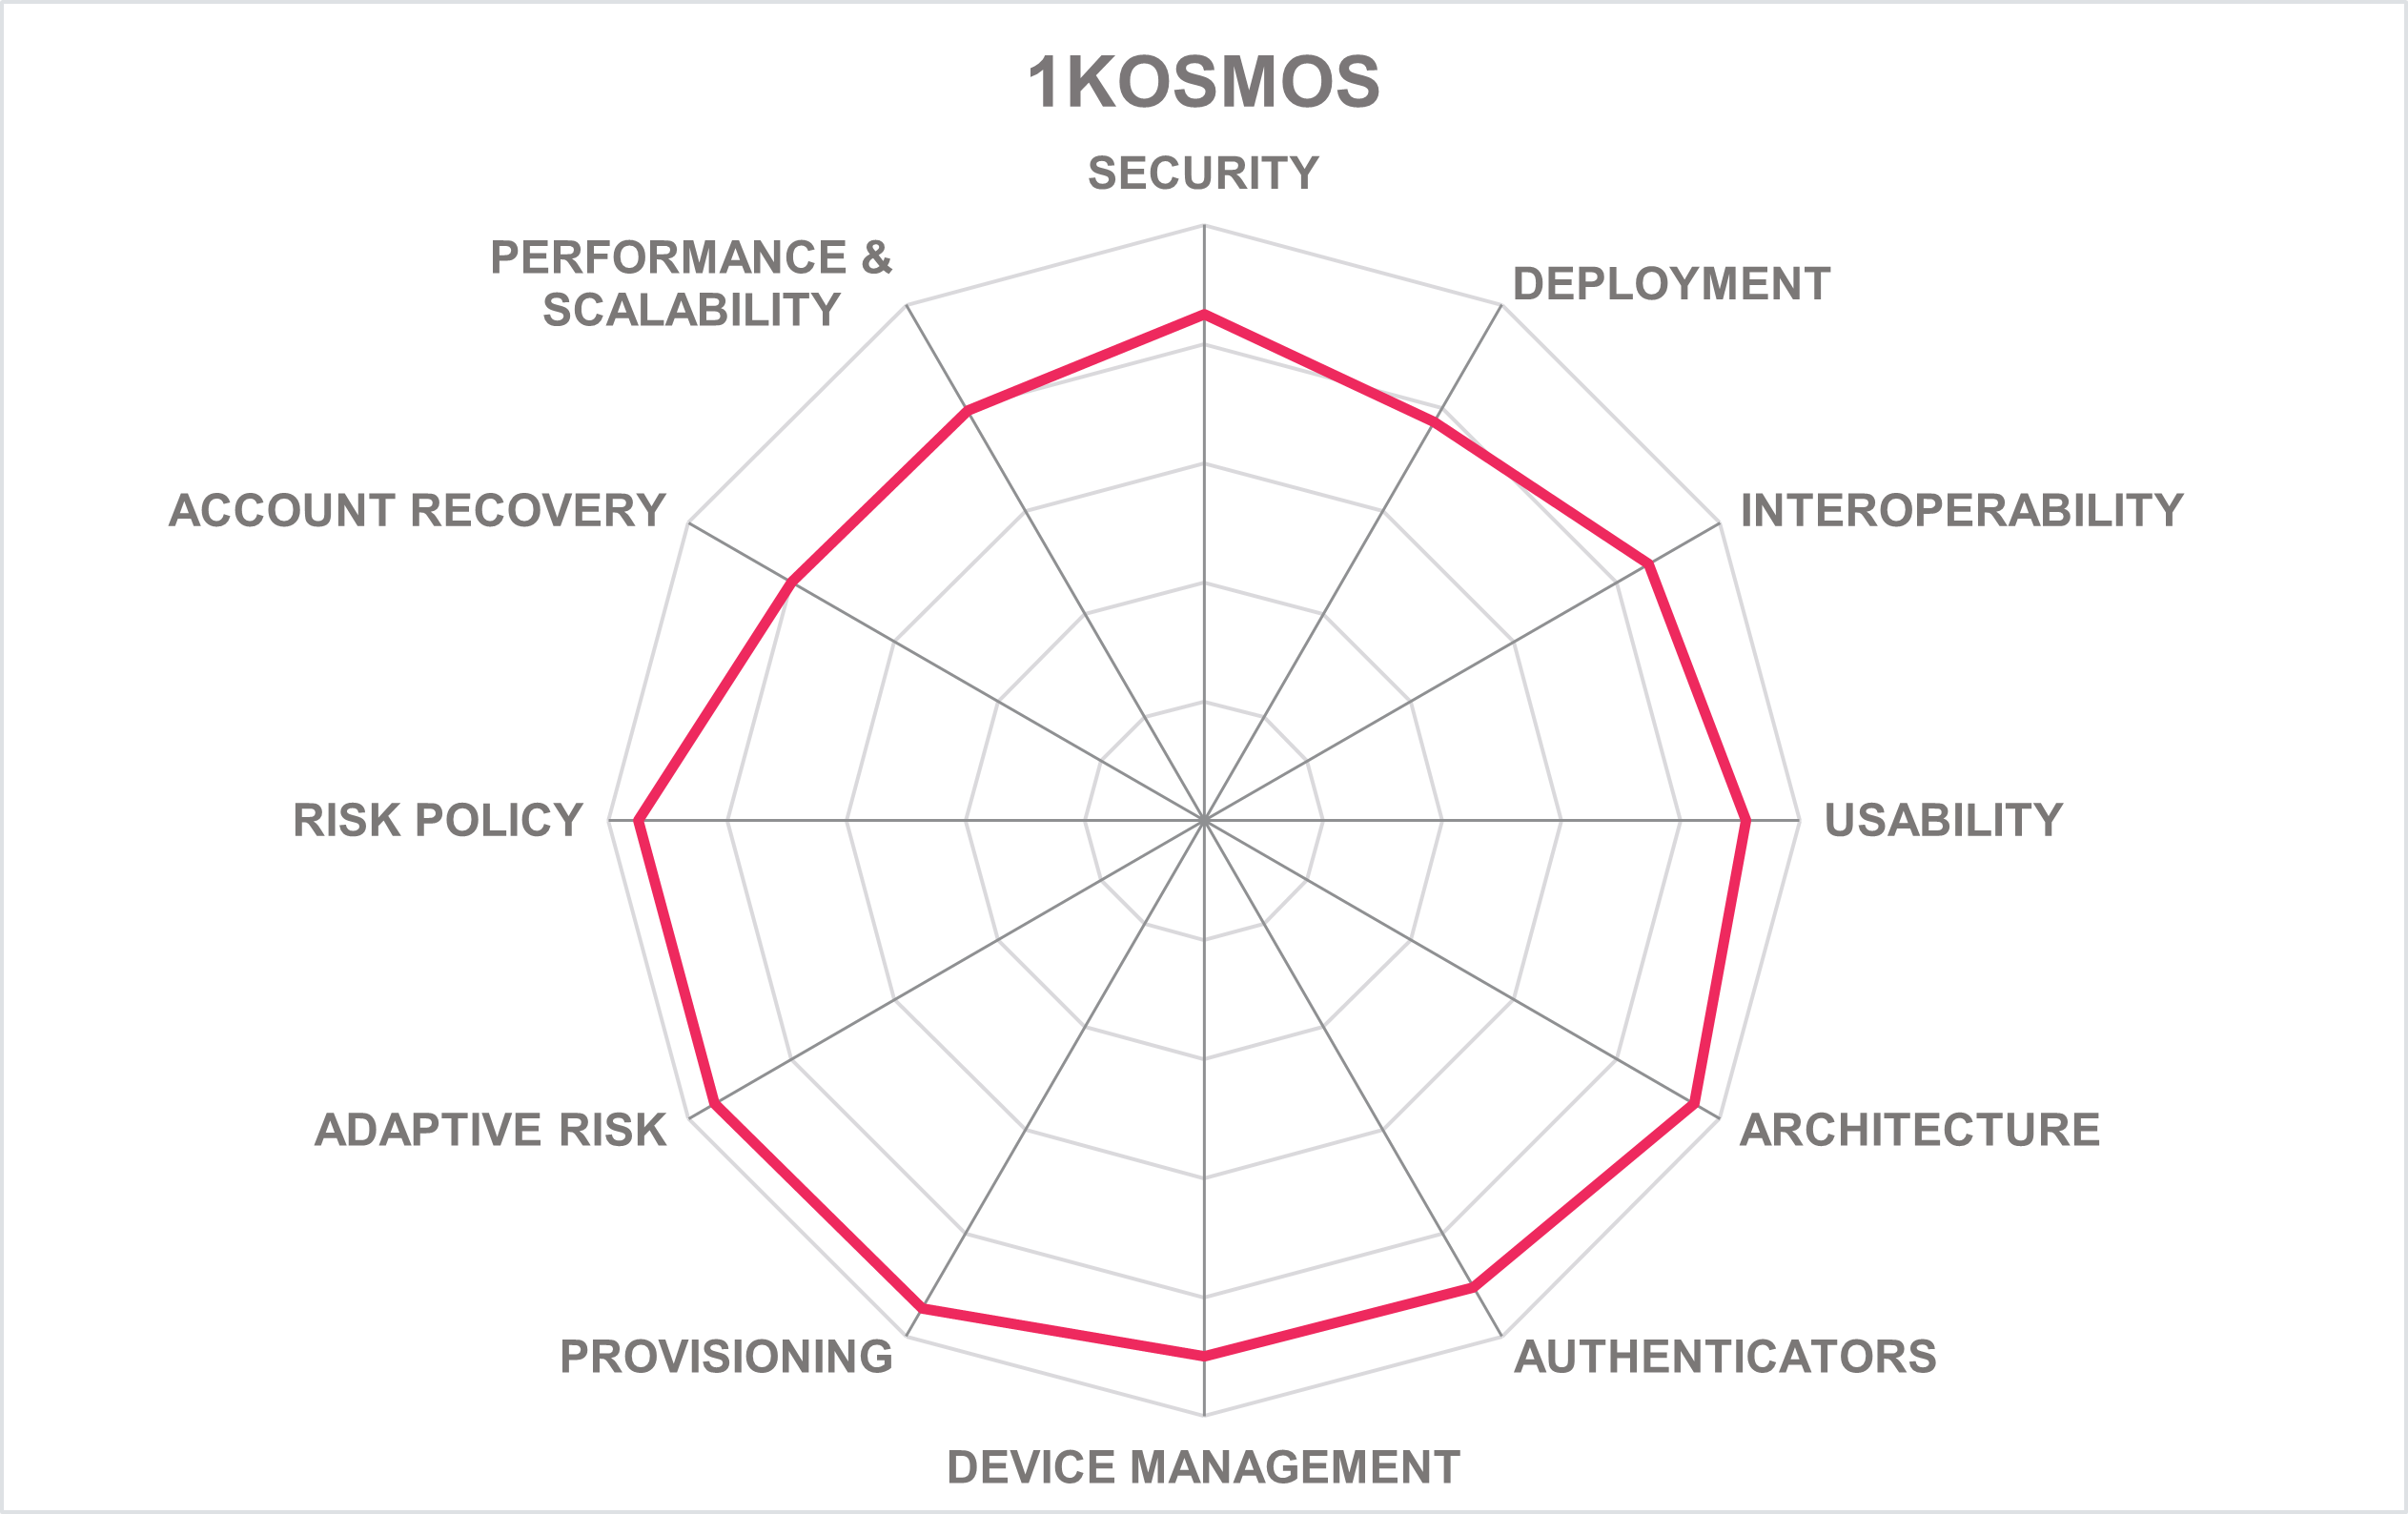
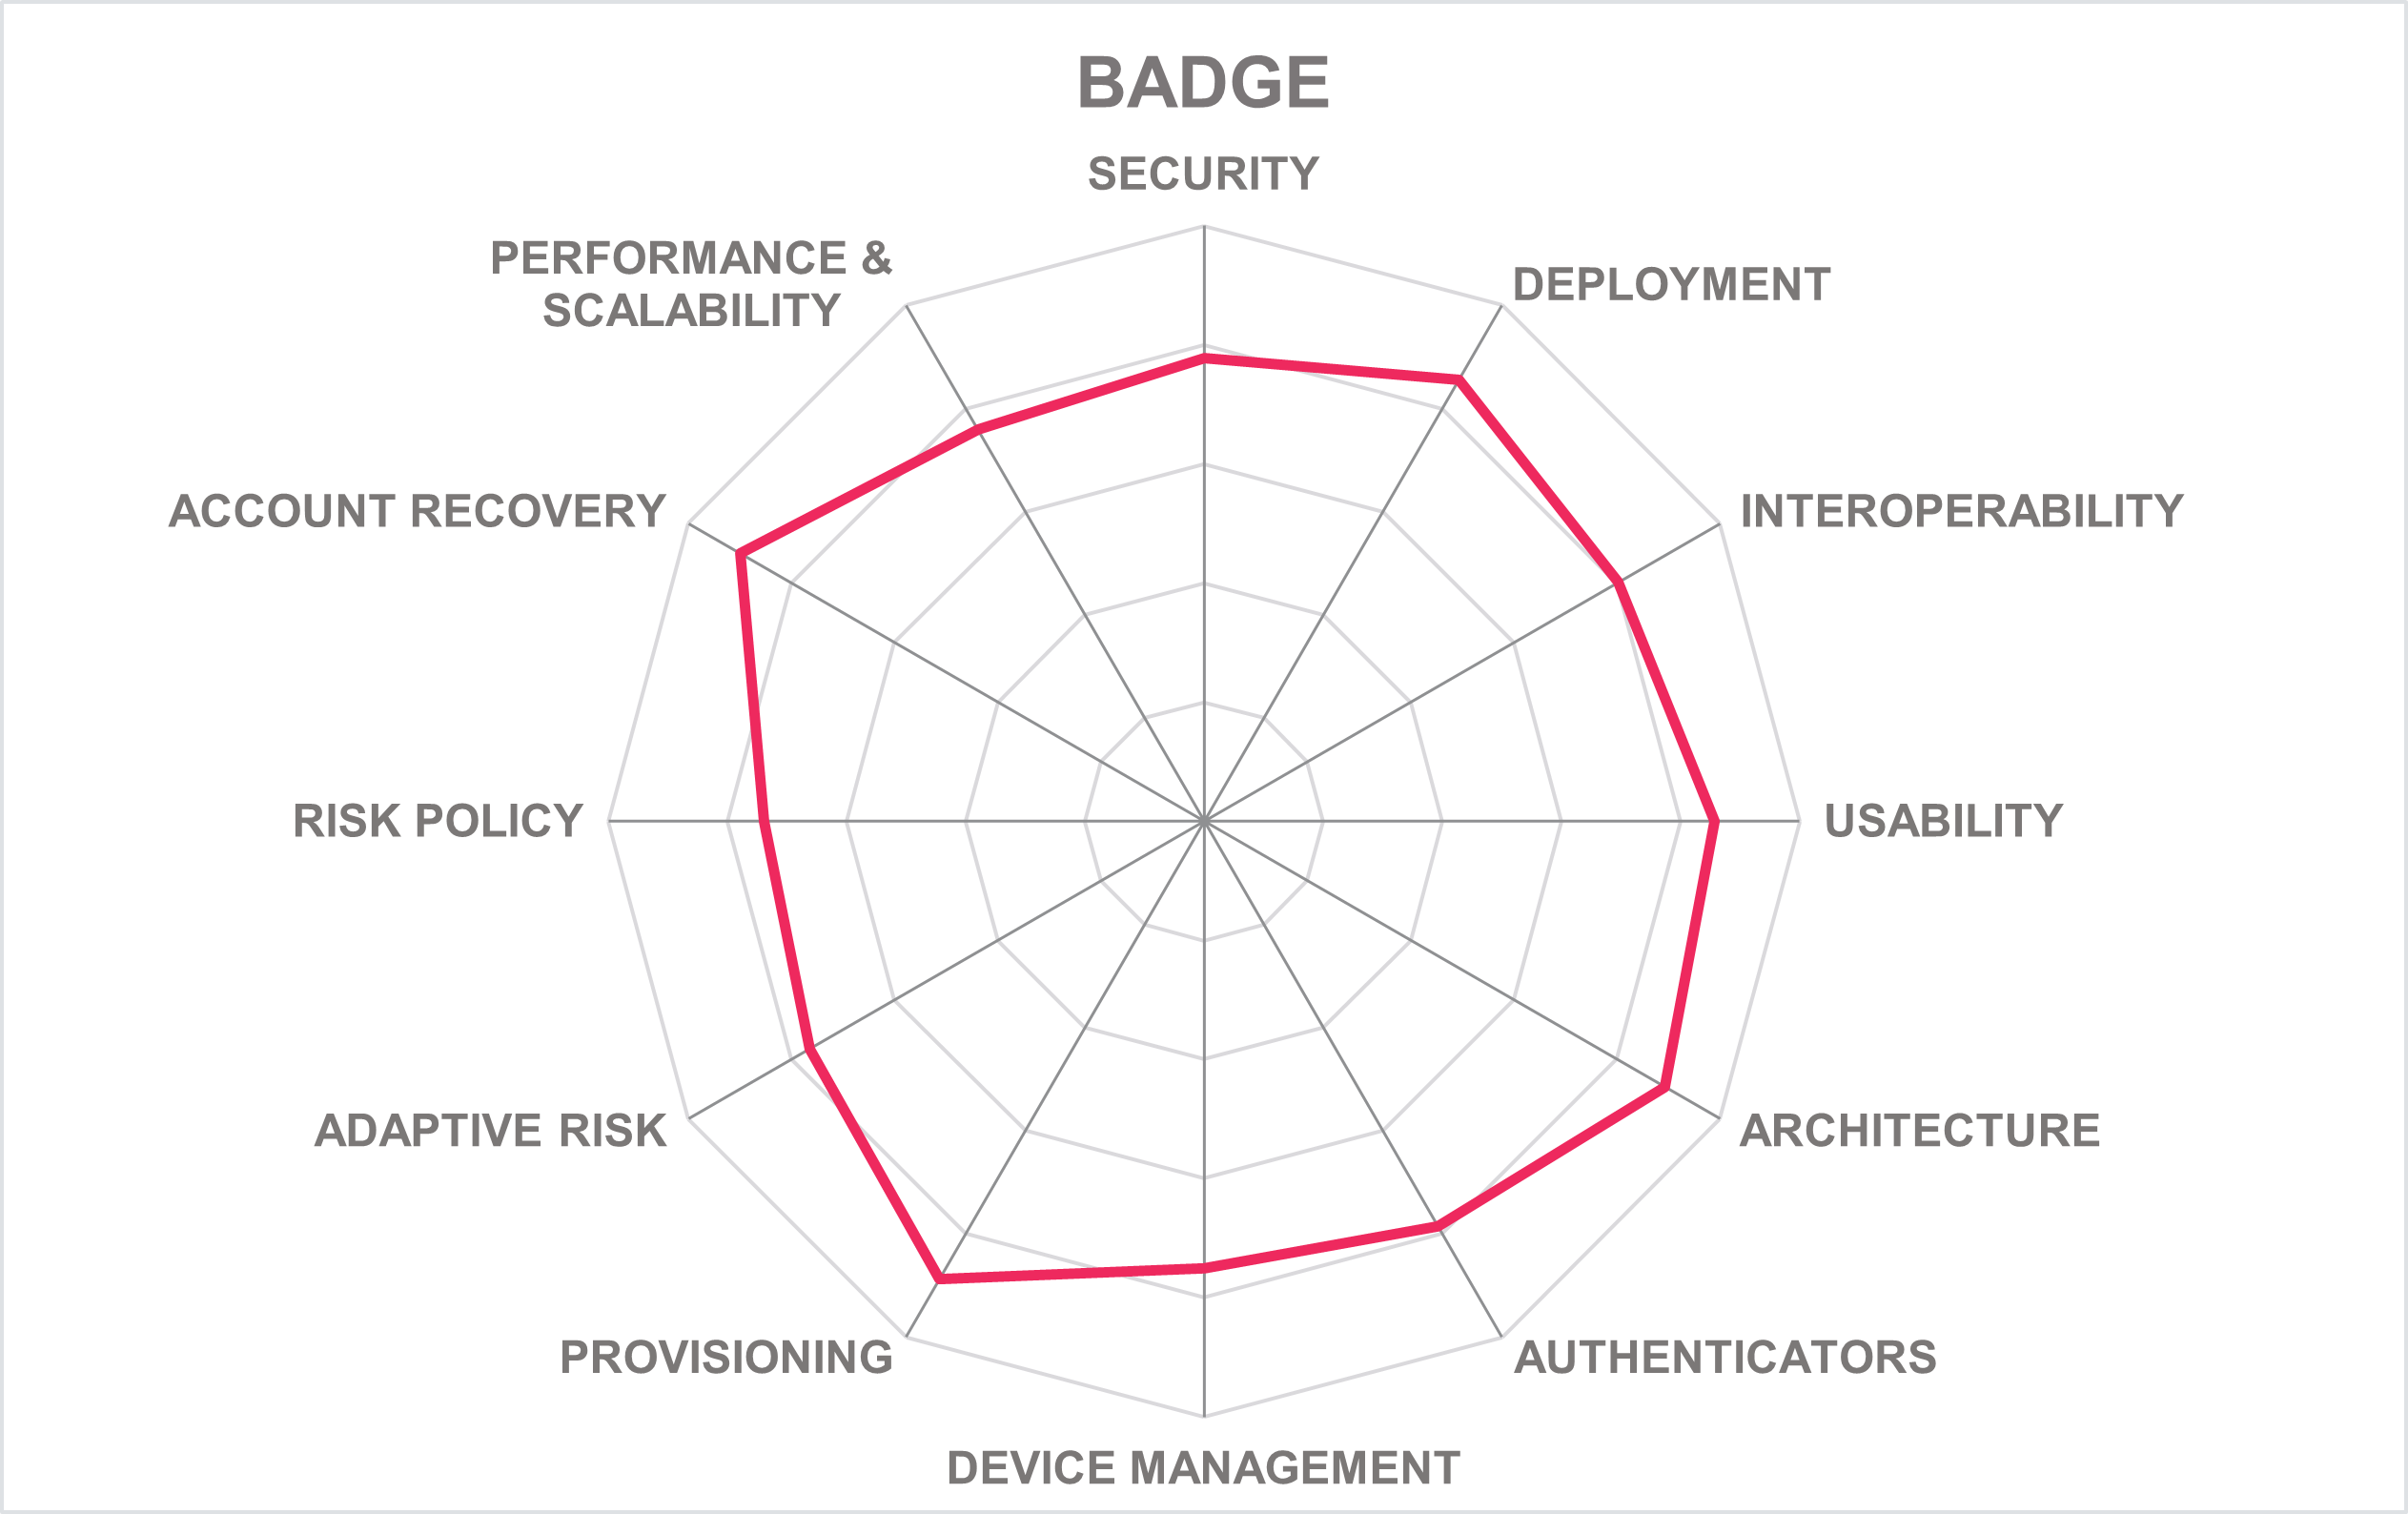
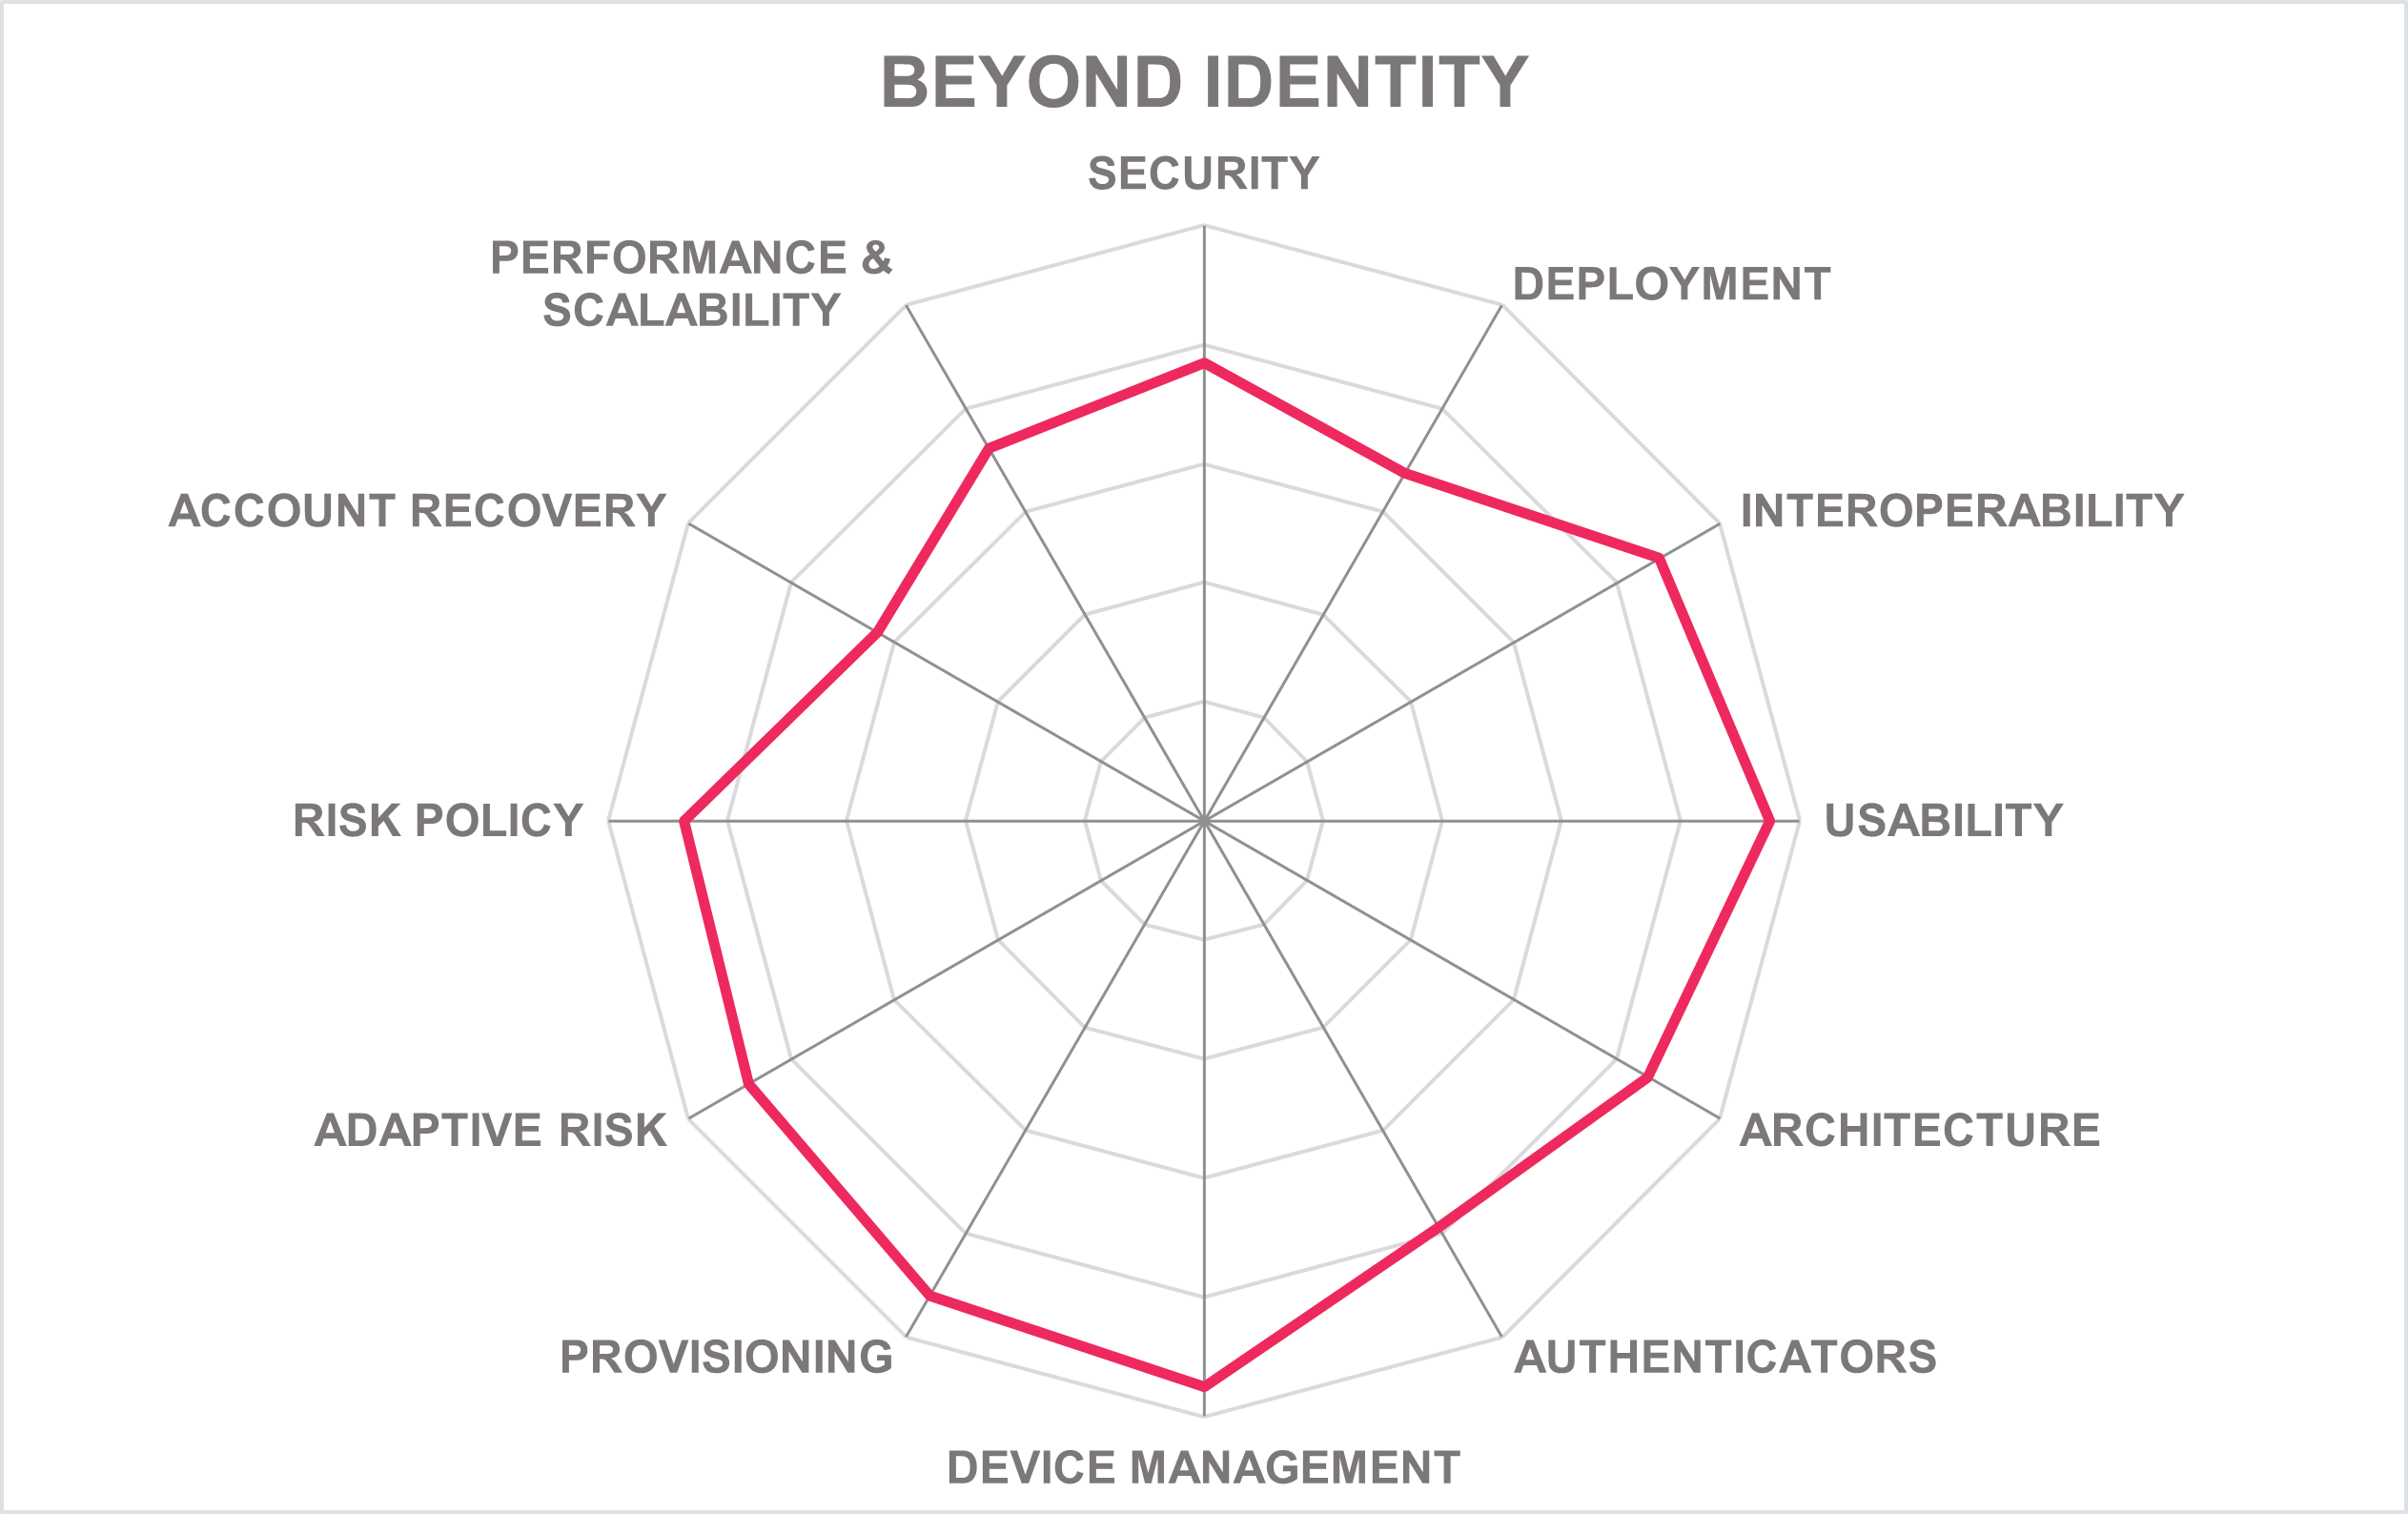
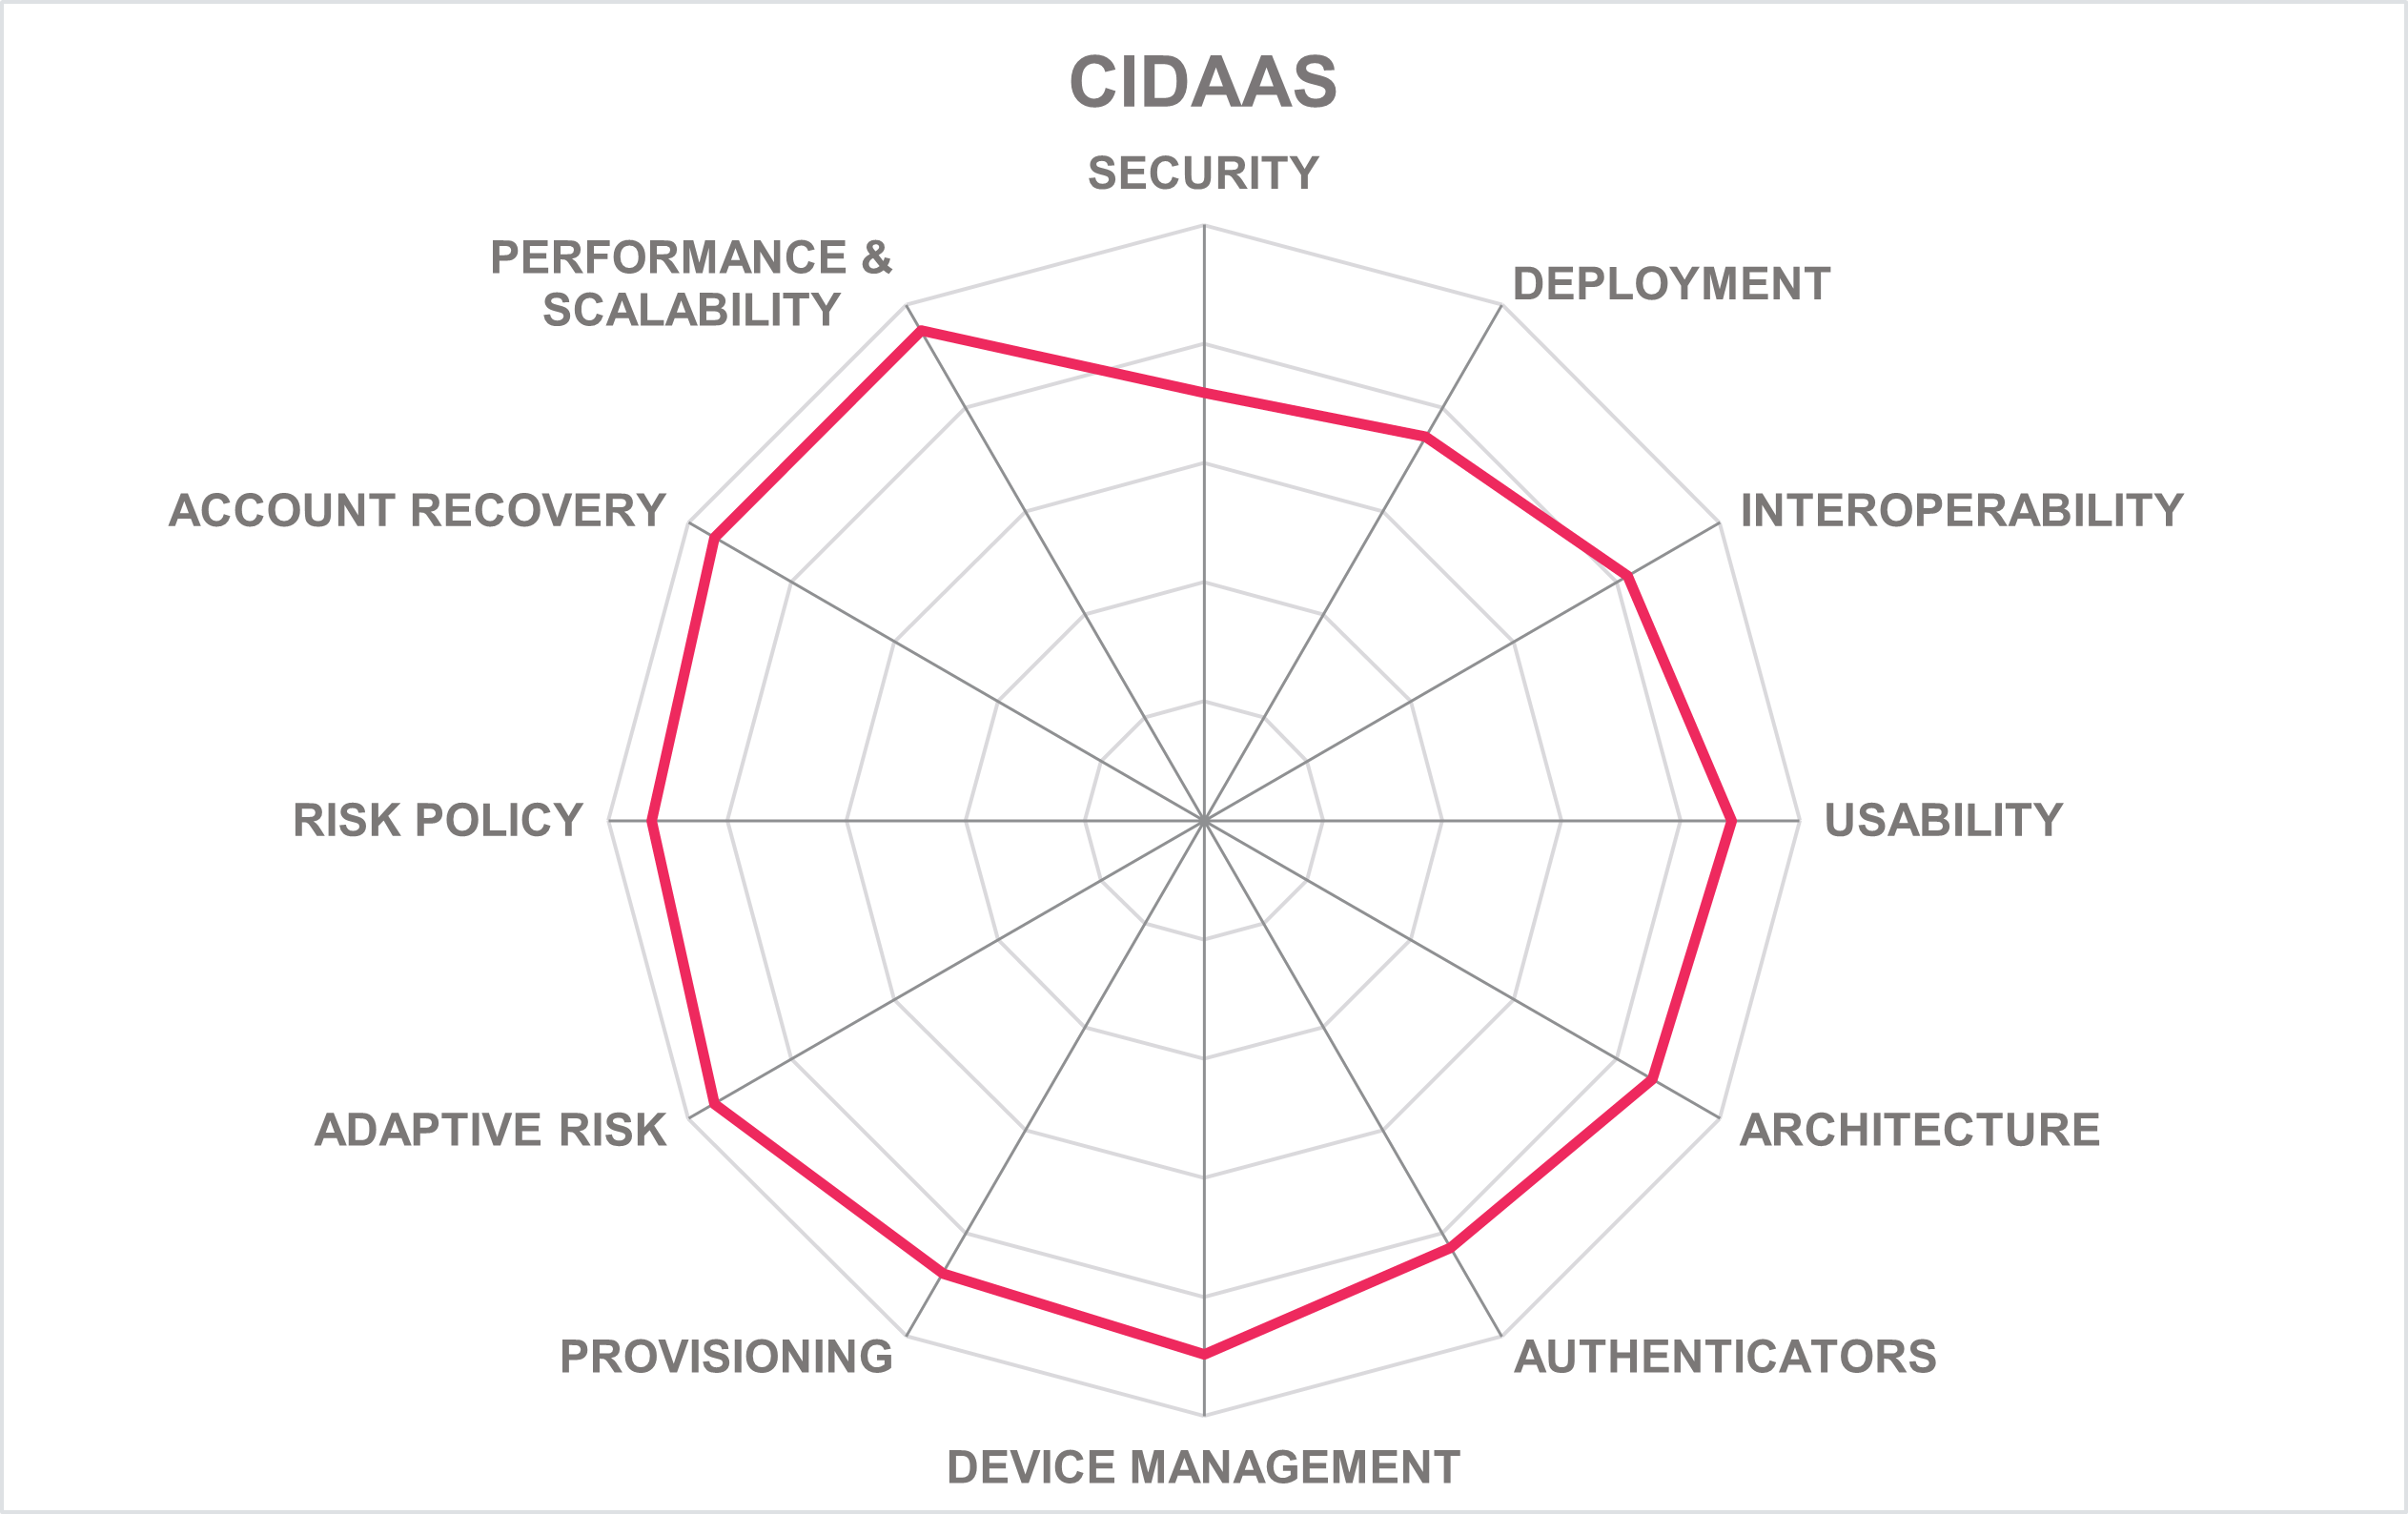
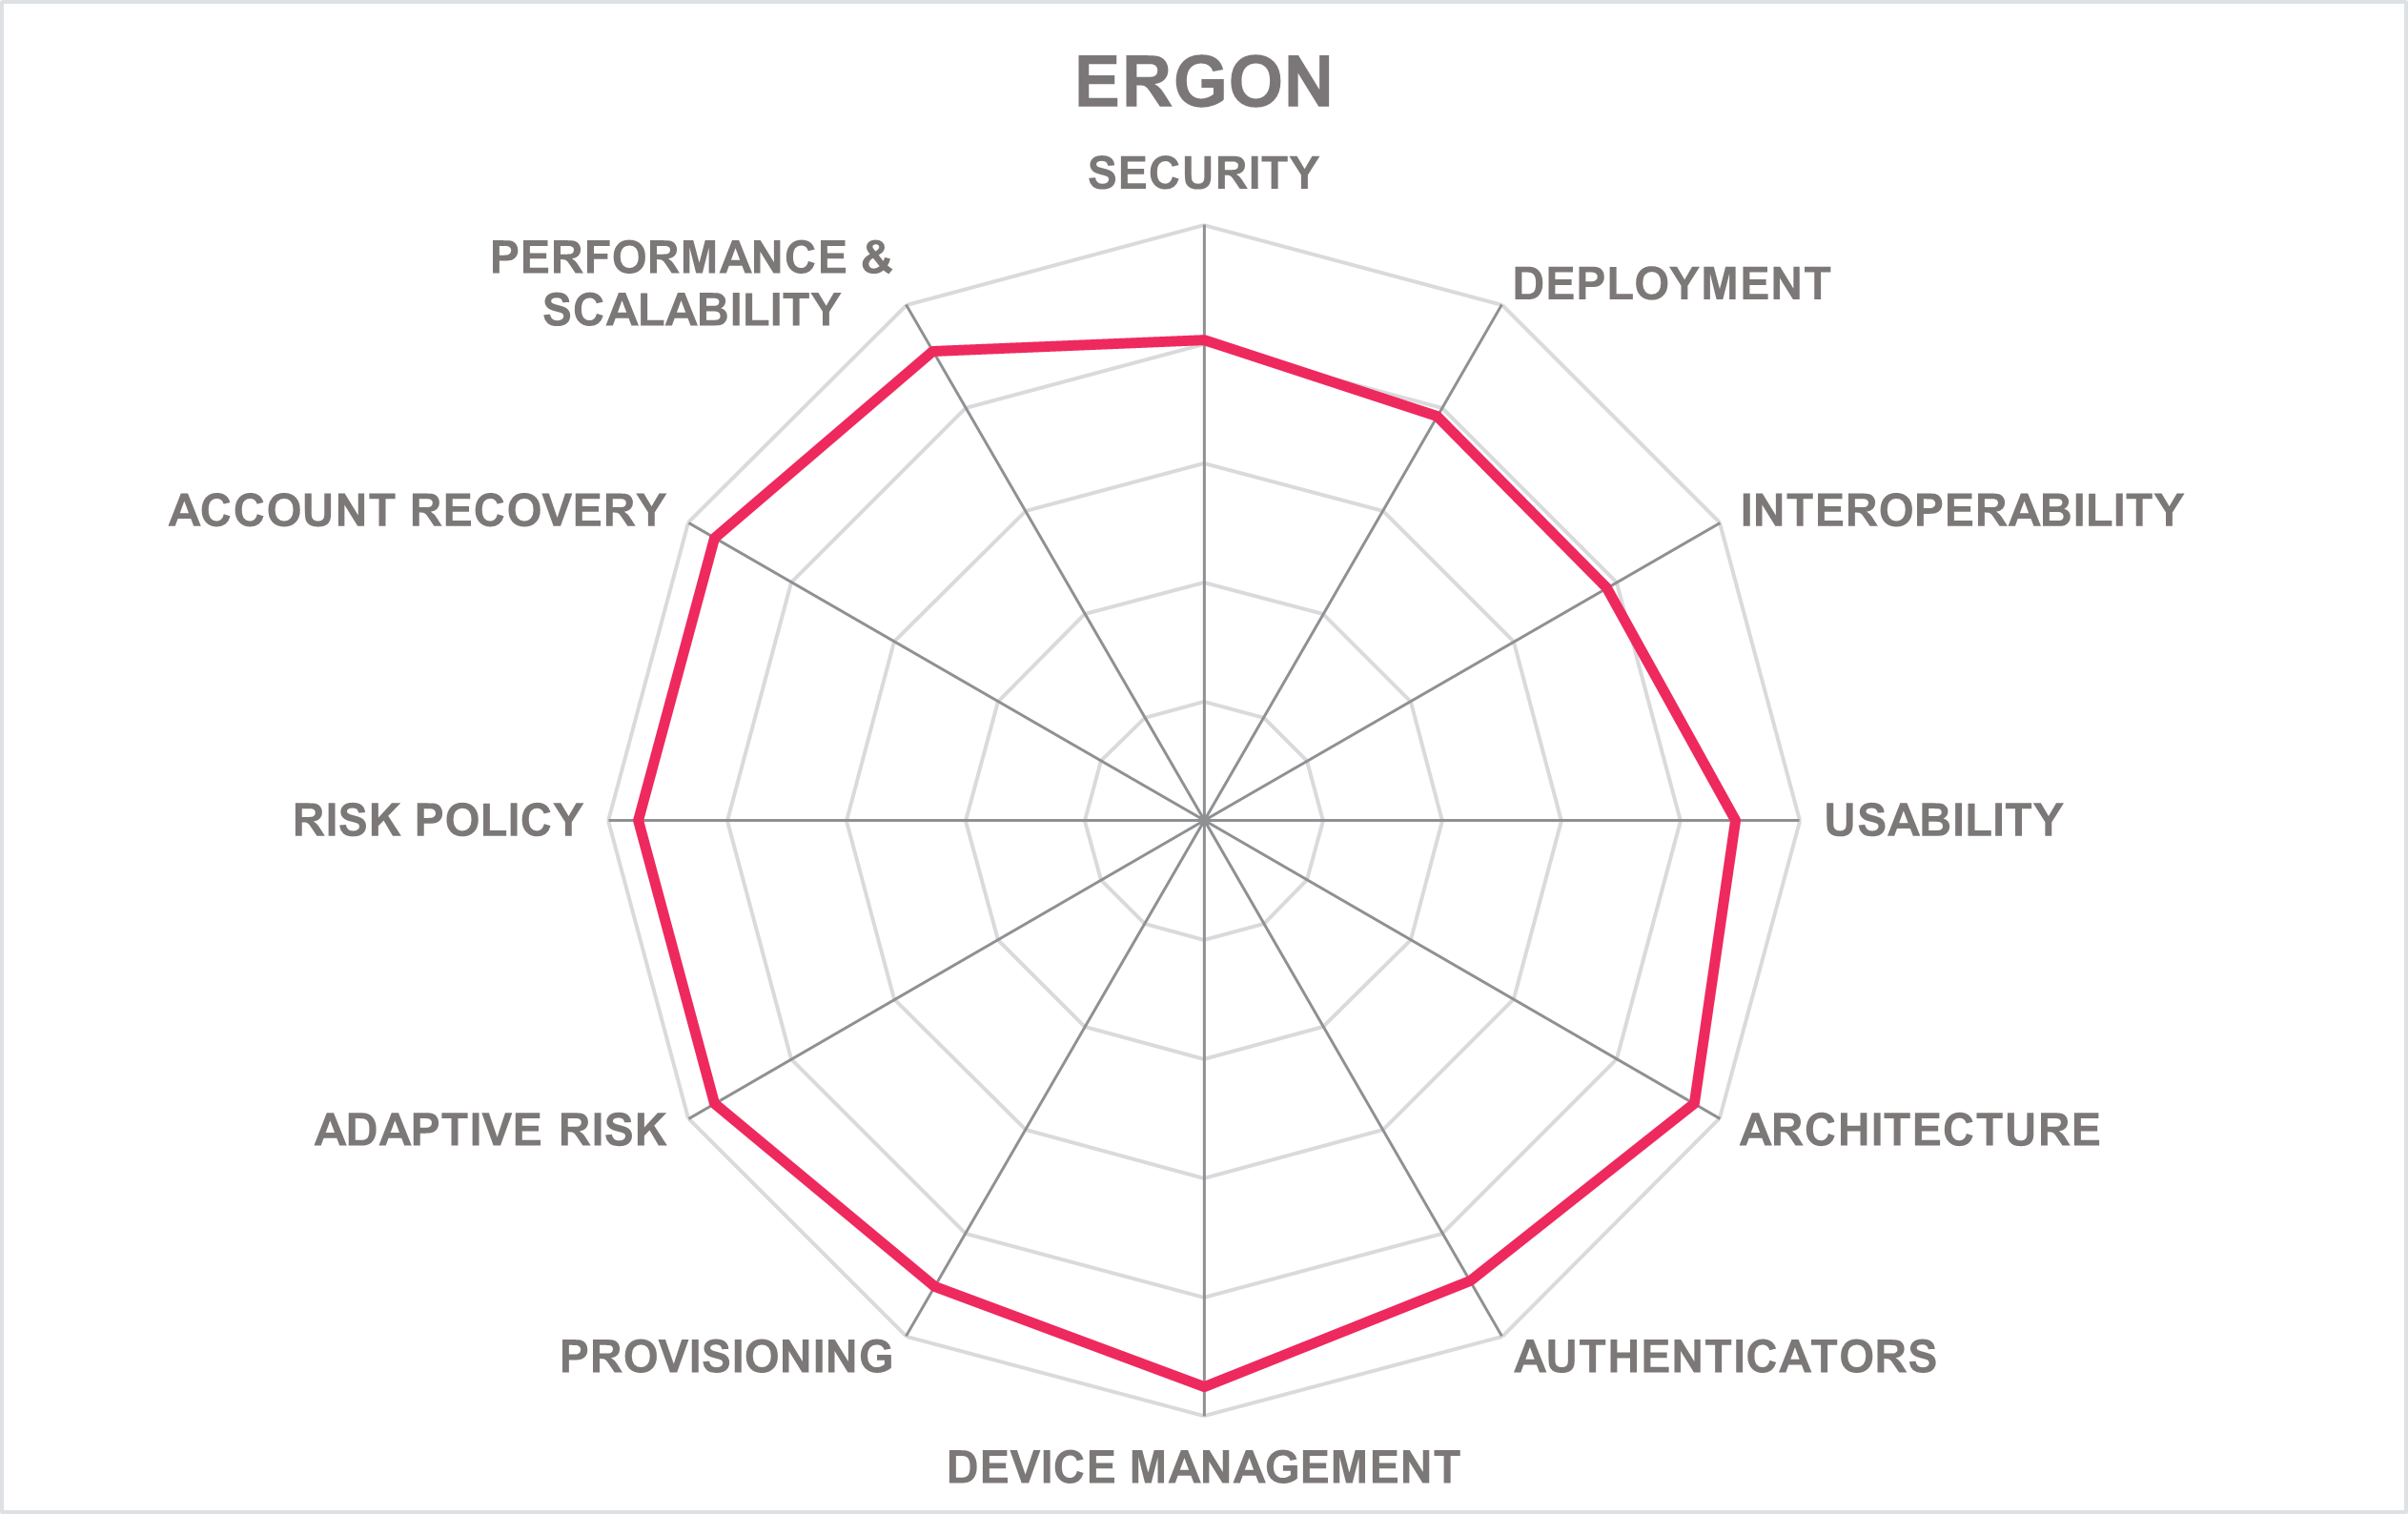
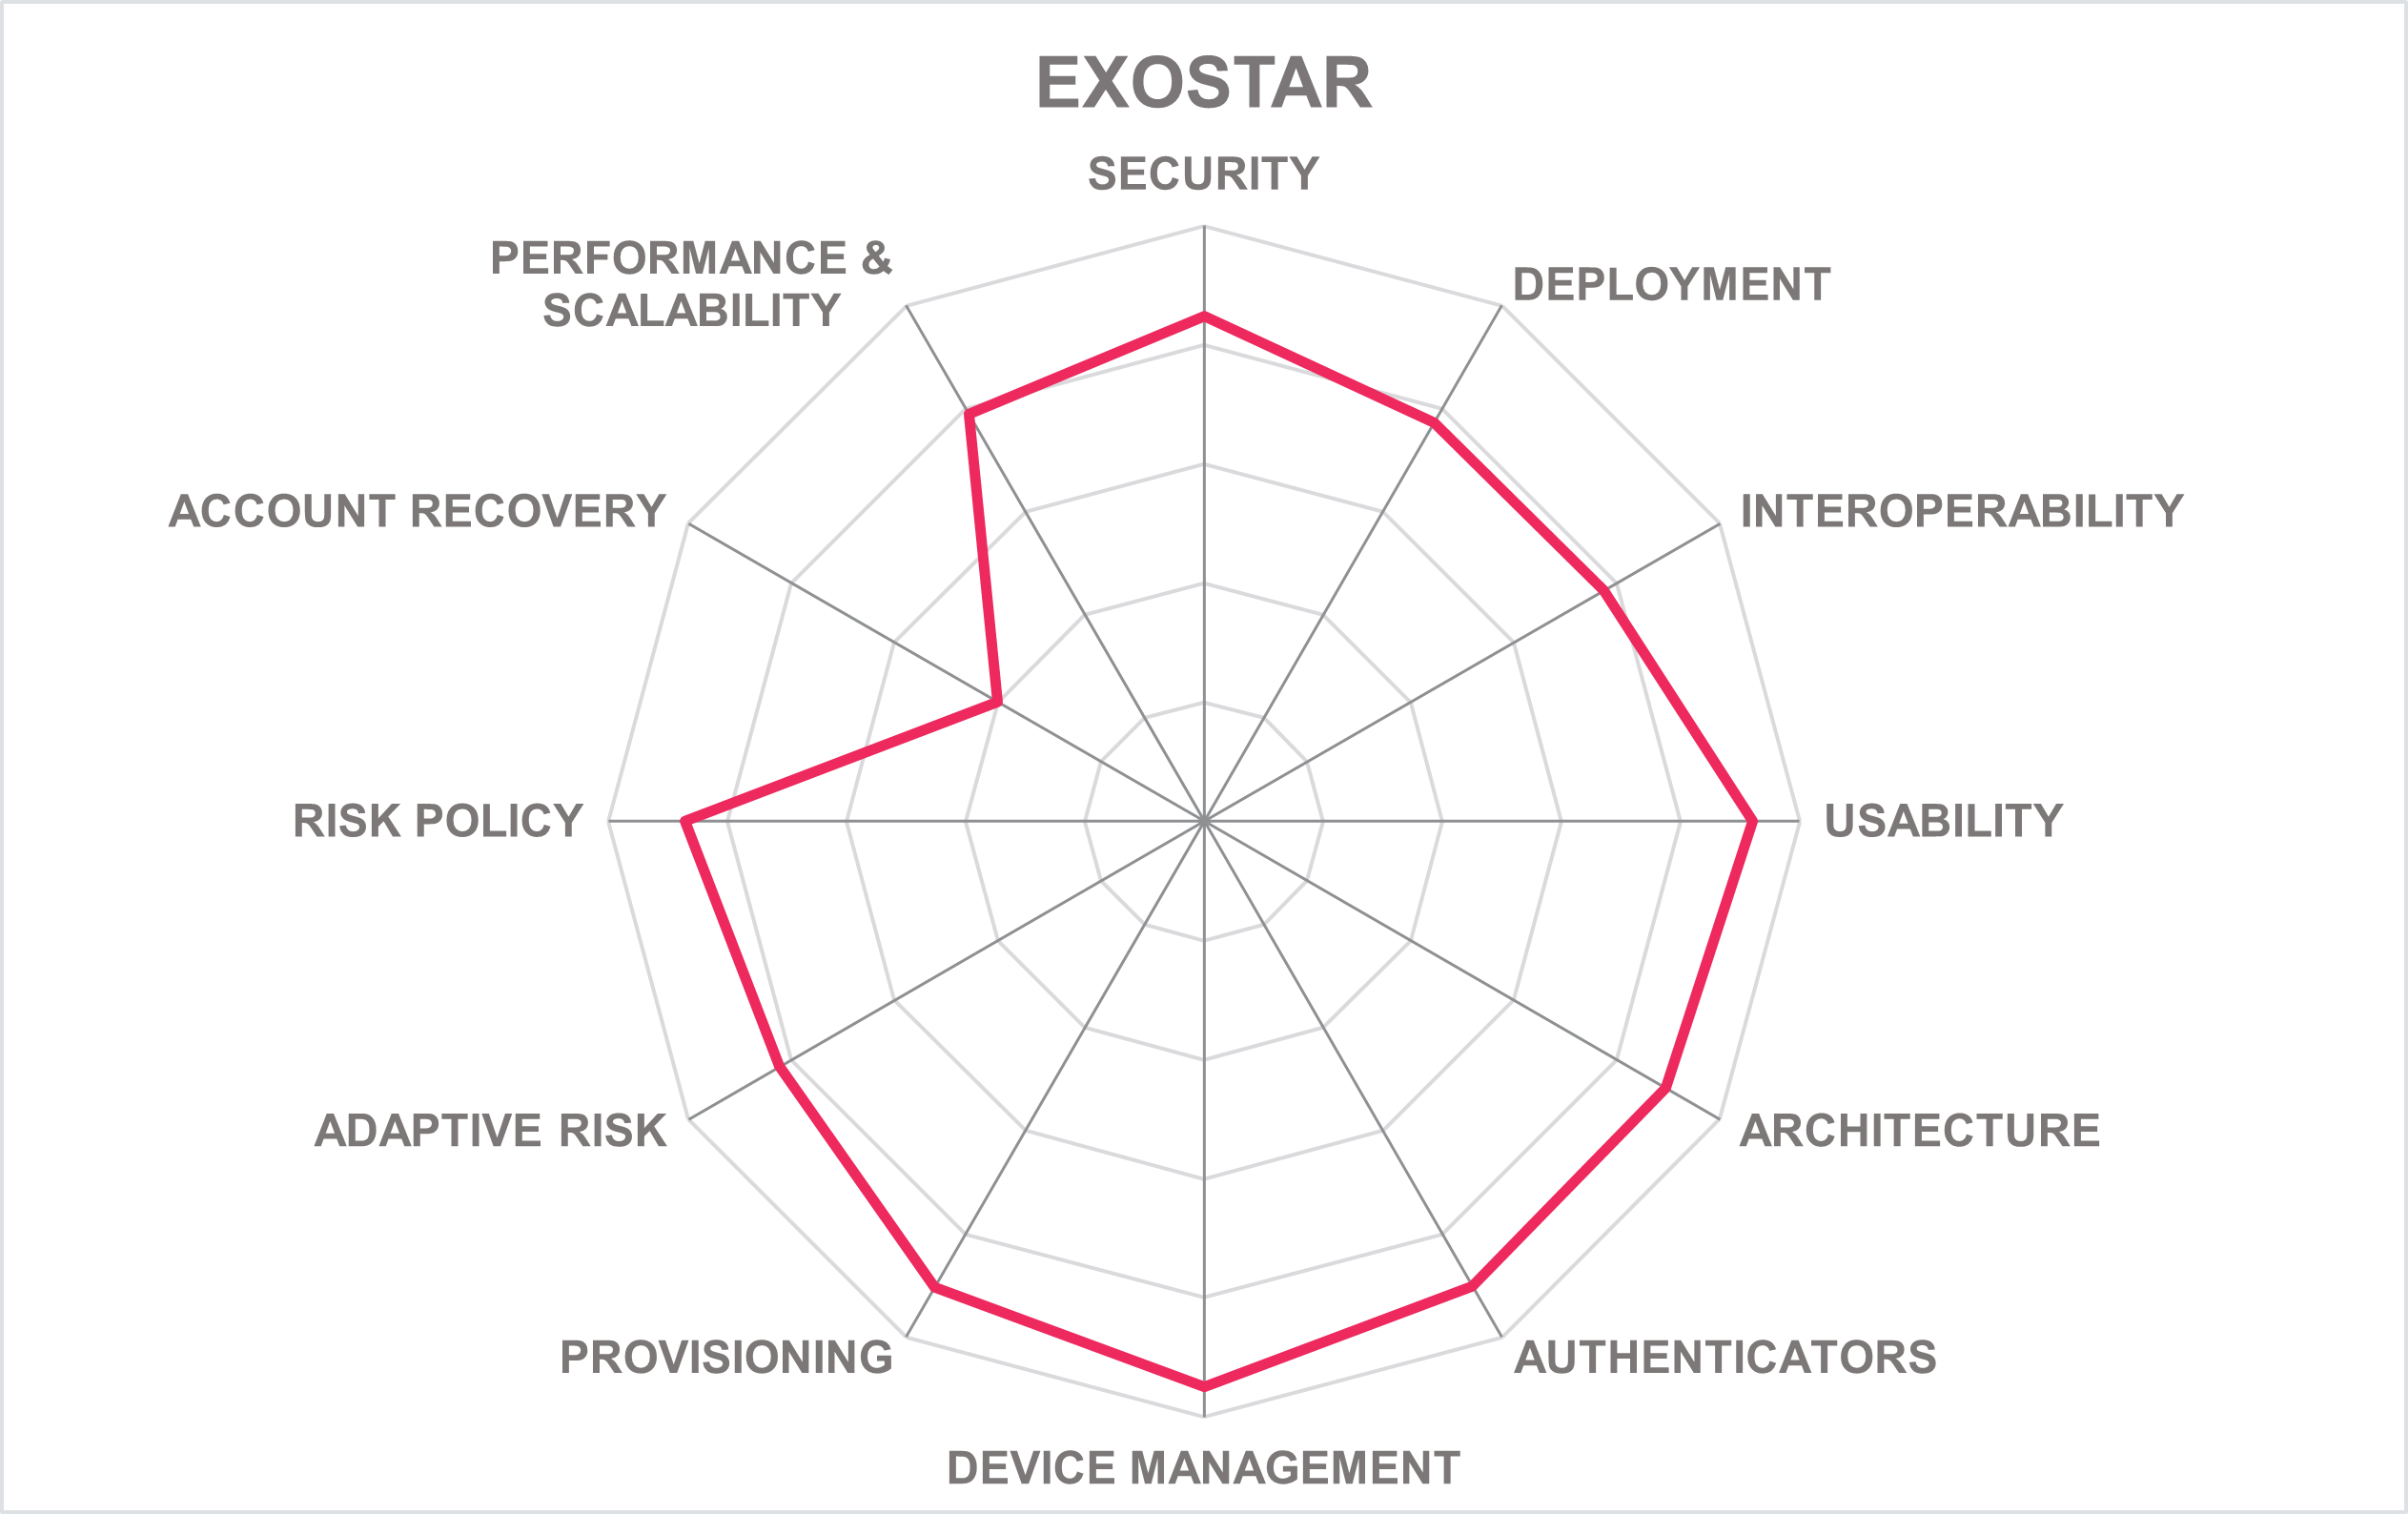
In addition to the ratings for our standard categories such as Product Leadership and Innovation Leadership, we add a spider chart for every vendor we rate, looking at specific capabilities for the market segment researched in the respective Leadership Compass. For this market segment, we look at the following categories:
Authenticators This covers the breadth, flexibility, and interoperability of authentication options supported by the passwordless authentication solution. It examines whether traditional credentials (such as usernames and passwords) are still supported alongside modern passwordless methods, including passkeys, mobile-based verification (SMS, push notifications, and vendor-specific apps), and biometric authentication (native Android and iOS capabilities). Additionally, we assess whether the solution provides secure mobile Software Development Kits (SDKs) for administrative functions, enables transaction signing for high-trust operations (such as financial services), and supports remote access scenarios.
Device Management This covers the solution’s device management capabilities, a critical aspect of maintaining secure passwordless authentication. It examines capabilities provided for a device registration workflow and how this process can be customized to meet organizational or regulatory requirements. The assessment includes the range of supported devices, such as mobile phones, desktops, IoT devices, and wearables. Key considerations include the presence of device health checks to ensure compliance with security posture requirements such as OS version and jailbreak detection.
Provisioning of Users This covers the user provisioning and lifecycle management capabilities of the passwordless authentication solution, assessing how it can onboard and manage users at scale. It examines whether the platform supports bulk provisioning from common identity sources, such as directories accessed via the Lightweight Directory Access Protocol (LDAP) and systems using the SCIM protocol, enabling integration with existing enterprise directories and identity management systems. It considers the API capabilities provided to provision to or synchronize with other cloud services. Additionally, support for user self-registration is reviewed to determine the solution’s suitability for consumer-facing deployments, where end users may create and manage their own accounts without administrator intervention.
Adaptive Risk Factors This covers the adaptive risk and contextual intelligence capabilities provided by the solution that enable dynamic, risk-based authentication decisions. It assesses whether the platform can analyze a wide range of risk factors, including IP reputation, geo-location, geo-velocity (impossible travel detection), device identifiers, and temporal patterns (date/time anomalies). The evaluation extends to advanced capabilities such as device fingerprinting, software signatures, and device health assessments, which help determine whether a device is trustworthy based on Operating System (OS) version, patch level, or the presence of security software. It also covers the capabilities to track device and user history, correlating behavioral and environmental signals to detect anomalies, such as a known user appearing on a new or potentially compromised device. Additional capabilities include support for jailbreak/root detection, fraud intelligence feeds, and compromised credential monitoring, which strengthens protection against account takeover and synthetic identity attacks. Finally, the capabilities to integrate these signals into risk-based access controls, allowing organizations to automatically adjust authentication requirements or enforce step-up verification based on real-time contextual risk.
Risk Policy This covers the risk policy management and orchestration capabilities of the passwordless authentication solution, focusing on how administrators define, manage, and enforce adaptive access rules. It examines the methods available for authoring policies, such as importing configurations via JSON or Extensible Access Control Markup Language (XACML), or using intuitive graphical interfaces, from drop-down menus and guided natural language inputs to flowchart-based models. The section also covers the support for weighted risk factors, and whether the risk evaluation produces quantifiable scores or levels (for example, numeric ranges or tiered risk categories). Another consideration is whether the risk analysis engine is API-addressable, allowing external systems to consume risk insights or trigger workflows. The capabilities for policy-based actions and branching logic, such as enforcing step-up authentication or conditional access responses based on risk thresholds. Finally, it covers whether the risk engine integrates with third-party services, such as authorization or fraud detection platforms.
Account Recovery This covers the account recovery mechanisms provided by the passwordless authentication solution, emphasizing how users can securely regain access when credentials or devices are lost. It examines the availability of multiple recovery channels, such as traditional username/password fallback, Knowledge-Based Authentication (KBA) (security questions), and more secure methods like email or phone OTPs, SMS verification, or mobile push notifications. The inclusion of account linking allows recovery through pre-associated trusted accounts (such as social or enterprise identities), while help-desk–assisted recovery provides administrative oversight for high-assurance scenarios.
Performance and Scalability This covers the performance, scalability, and reliability characteristics of the passwordless authentication solution. It assesses metrics such as the maximum transaction volume managed by the largest customer, average daily login throughput across the platform, and peak authentication rates (logins per second) to gauge capacity under both steady-state and high-demand conditions. It includes factors such as average response times that users experience, the platform’s uptime commitments through defined SLAs or Operational Level Agreements (OLAs). High availability and fault tolerance are key indicators of system maturity, particularly in global, cloud-hosted environments. Additionally, the section investigates scaling mechanisms (such as elastic cloud infrastructure, load balancing, and distributed microservices) that enable rapid adaptation to a spike in demand or user growth.
1Kosmos – 1Kosmos Customer
| Leader in |  |  |  |  |
1Kosmos, founded in 2018, operates out of Iselin, New Jersey in the US as a private entity supported by venture capital. It has a strong market presence in North America, and is expanding its reach into Europe, Middle East, and Africa (EMEA) and Asia-Pacific (APAC) regions. The company's primary offering, 1Kosmos Customer, is SaaS hosted across multiple IaaS platforms in data centers on four continents. It supports both multitenant and single-tenant configurations. Subscriptions are priced on a per-user basis, and they have per-transaction fees for Identity Verification (IDV) events and wallets.
The 1Kosmos Customer passwordless authentication solution is part of their CIAM and supports a wide range of passwordless authentication methods including FIDO2/WebAuthn passkeys with native biometric authentication on both iOS and Android devices. 1Kosmos has achieved FIDO2 certification for core component (specifically its FIDO server) and that the platform aligns with NIST SP 800-63-3 at IAL2/AAL2 levels.
The solution’s underlying digital identity and authentication platform provides the cryptographic, blockchain, and identity-proofing foundation. This is FIDO2 certified to the FIDO Alliance standards for phishing-resistant authentication. This confirms interoperability with hardware security keys such as YubiKey, Google Titan, and Feitian’s FIDO2 keys, while maintaining compliance with identity protocols, including SAML, OAuth 2.0, and OIDC. The solution’s SDK-based mobile authentication and cryptographically bound transaction signing meet the requirements for high-trust operations in financial and regulated sectors.
For device management, provisioning, and recovery, the solution enables secure device registration, monitoring, and re-enrollment through the 1Kosmos platform that maintains device trust consistency across user sessions and devices. During registration, the consumer’s verified identity is bound to one or more devices through the establishment of secure key material tied to that device. The platform uses secure hardware and local biometrics to maintain device trust and prevent compromise.
It supports device posture checks by integrating with endpoint and Unified Endpoint Management (UEM) solutions to assess device trust. It can evaluate factors like OS version, device registration status, biometric availability, and jailbreak/root detection, enabling adaptive access controls based on device health and compliance. 1Kosmos supports integration with enterprise and cloud identity sources via SCIM and LDAP, as well as consumer self-registration workflows. Account recovery supports multiple secure recovery channels and verifiable identity re-binding.
For adaptive risk-based authentication, the 1Kosmos risk engine continuously evaluates contextual indicators such as device posture, IP reputation, geo-velocity, and behavioral anomalies. Using these inputs, it dynamically enforces step-up authentication or conditional access rules in line with policy-based risk thresholds. These policies can include weighted risk factors and produce quantifiable risk scores. By combining device fingerprinting, behavioral analytics, and its decentralized identity model, the solution can detect anomalies such as compromised devices or synthetic identities.
Policy authoring is flexible, with support for JSON, XACML, and Graphical User Interface (GUI)-based methods. The platform evaluates risk factors to yield detailed risk scores (0-1000) and allows for varied actions based on these scores, such as step-up authentication and access denial. Risk analysis can integrate with exterior services. Customers can import policies derived from Machine Learning (ML) algorithms or behavioral analytics platforms that evaluate factors such as user risk scores, anomalous behavior patterns, device telemetry, and threat intelligence feeds. These policies are then enforced natively within the 1Kosmos policy engine, enabling real-time, adaptive access controls based on dynamically computed risk profiles.
1Kosmos provides multiple secure recovery options when a user changes or replaces their device, ensuring continuity of access without compromising identity assurance. Users can re-establish their identity by completing a liveness-based facial recognition check that compares their live face to the originally verified identity. If users still have access to a previously registered device, they can use this to approve registration of a new one. The platform can require users to re-submit a government-issued ID and complete liveness detection to recover access securely. Organizations can also configure a help-desk-assisted recovery workflow, which can include step-up authentication and policy-based approvals.
The platform's security infrastructure is designed with privacy at its core which prevents access to personal information even by administrators. Furthermore, 1Kosmos provides over 150 connectors, offering integration capabilities with operating systems, SaaS applications, and even bespoke applications.
1Kosmos is positioned as both a product and innovation leader in this report. This leadership is based on the capabilities provided including their decentralized identity platform, combining FIDO2-certified authentication, blockchain-based identity verification, and biometric passkey technology to deliver phishing-resistant, standards-compliant access without passwords.
Organizations looking for a solution that combines passwordless passkeys with a privacy protected, verifiable digital identity, enabling strong authentication tied to a cryptographically validated user identity, should consider 1Kosmos.
| Strengths |
|
| Challenges |
|
Badge – Badge
| Leader in | | | | |
Founded in 2019, Badge Inc. is headquartered in Fremont, California in the US and specializes in passwordless authentication technology designed to integrate with existing infrastructure across both consumer and enterprise sectors. The company's platform, Badge, supports a range of complex use cases by providing a single enrollment, multi-device experience without the need for recovery devices, passwords, or centralized biometric storage. It supports operational contexts from kiosks to Virtual Desktop Infrastructure (VDI) environments. Deployment options include SaaS and on-premises solutions, with compatibility for Kubernetes, OpenShift, and K3 environments.
Badge is built natively around WebAuthn and FIDO2, with full support for passkeys across web and mobile experiences. The platform leverages platform authenticators such as Face ID, Touch ID, Windows Hello, and Android biometrics, as well as external FIDO security keys. Badge does not position itself as a full-scale FIDO server vendor with publicly listed FIDO server certifications; instead, it operates as a passkey orchestration layer built on the standards themselves.
Badge provides phishing-resistant authentication across various platforms like Windows, macOS, iOS, and Android. Its architecture is built around “Identity without Secrets™,” which enables authentication utilizing zero-knowledge cryptographic techniques to derive keys on demand, eliminating the need for centralized storage. Authentication factors include biometrics, Personal Identification Numbers (PINs), and physical tokens such as Radio-Frequency Identification (RFID), with compatibility with existing authentication hardware. The platform integrates with major identity providers like Microsoft Entra and Okta Badge via standard identity protocols including SAML, OIDC, OAuth2, SCIM and others via its partner program.
Badge has features that align with requirements around contextual risk, dynamic device trust, and recovery. The platform generates private keys dynamically from biometric and other factor inputs (such as fingerprint, face, voice, PIN, and passive attributes) and discards them after use, so there are no static credentials to compromise. This capability supports adaptive authentication by reducing reliance on device-trust assumptions (for example, even if the device changes or is untrusted, the user can still authenticate) and by shifting the trust anchor onto the user’s current context rather than a token or device footprint. The system can tailor the authentication challenge based on the assessed risk. For example, in a familiar environment it might simply use biometrics, while in an unusual context (shared device, kiosk, new device) it can require additional factors.
Badge provides an “enroll once, authenticate on any device” workflow: users complete a one-time enrollment that can be done at home or on-premises, after which they can authenticate across computers, phones, kiosks or shared devices without re-registration or device-specific tokens. During that enrollment, Badge issues a private/public key pair which is derived from the user’s biometric and/or other authentication factors. The private key is not persistently stored; rather, it is derived on the fly when the user authenticates. The public key remains for verification.
Badge transforms Account Recovery by eliminating reliance on passwords, trusted devices, or cloud sync fabrics. Passkeys are supported but not mandatory, ensuring users can gain secure recovery without ceding control to ecosystem providers like Google or Apple and risking singlepointoffailure dependencies.
Badge is designed as a lightweight, fully cloud-native authentication service optimized for high-volume consumer applications. Its architecture benefits from the efficiency of WebAuthn, which offloads most cryptographic operations to the user’s device.
Badge, with its ability to unify authentication processes across devices without relying on permanent storage of user credentials or biometrics, is an innovation leader. This innovative technology is now being exploited through several strategic partnerships as well as direct to market.
Organizations looking for phishing-resistant and privacy-preserving MFA not bound to a device should consider Badge.
| Strengths |
|
| Challenges |
|
Beyond Identity – Secure Customers (CIAM)
| Leader in | | | | |
Founded in 2019 and headquartered in New York City in the US, Beyond Identity focuses on passwordless authentication solutions. These are aimed primarily at the CIAM market, offering an identity defense platform that provides while optimizing usability. This solution is applicable to a broad range of sectors, including retail, technology, and services, and has customers in North America with growing activity in Europe, especially in the UK.
Secure Customers is Beyond Identity’s CIAM-focused product, designed to deliver cross-platform passwordless MFA for consumer and B2C applications. It removes passwords from the customer experience and the authentication database, replacing them with asymmetric key pairs held in device secure hardware and unlocked using biometrics.
Beyond Identity is a FIDO2-certified provider, and its passkey authentication can be initiated from a standard OIDC /authorize request, with SDK support for enumerating and selecting available passkeys. It also offers turnkey integration with other CIAM stacks (such as e.g., Auth0 and Okta) so customer apps can adopt passkeys without the need for custom federation development.
The solution places two authentication factors on a single device: a private key stored in secure hardware and a biometric (or equivalent local factor) used to unlock it. To authenticate, it issues a cryptographic challenge that is signed by the device’s private key; the platform then verifies this signature and assesses contextual risk in real time without any secret shared over the network.
To support device management and provisioning of users, it supports unmanaged devices with continuous authentication and real-time enforcement, so access can be controlled based on device posture even after login. Enrollment and identity lifecycle are supported via API/SDK workflows to create identities and bind passkeys, including self-enrollment and extending passkeys to new devices, addressing recovery/re-enrollment when a phone or laptop is replaced. The solution supports passkeys across web and mobile, allowing customers to authenticate via native platform authenticators such as Face ID, Touch ID, Windows Hello, and Android biometrics or hardware keys.
Beyond Identity’s architecture is explicitly device centric. Credentials are device-bound and stored in secure hardware such as Trusted Platform Modules (TPMs) or secure enclaves, and every access request is tied to a specific device with a cryptographic attestation. It continuously evaluates device security posture as part of the authentication flow, using signals such as OS security configuration, disk encryption, and endpoint security status, and incorporates additional signals from Mobile Device Management (MDM), Endpoint Detection and Response (EDR), and eXtended Detection and Response (XDR) systems.
Secure Customers is designed to plug into existing CIAM or custom user stores rather than replace them entirely. Beyond Identity provides customer-specific realms (Secure Customer Realms) that function as distinct identity directories within the Secure Access Platform; these realms can be used to manage customer identities and link them to passkey credentials. For self-service registration, customers can sign up and provision their credentials in a single, passwordless workflow without ever creating a password or interacting with legacy MFA enrolment screens. Account recovery for passwordless users relies on mechanisms such as credential extension from an existing trusted device, and recovery flows initiated through verified channels (for example, email-based registration or identity provider authorization).
For Adaptive Risk, the platform supports continuous risk-based authentication that re-evaluates user and device signals on a schedule (for example, fresh endpoint checks every 10 minutes) and integrates device security posture from partners such as CrowdStrike to gate or quarantine sessions dynamically. These signals feed fine-grained, policy-driven access decisions and can be supplied back to an upstream Identity Provider (IdP) to enforce conditional access policies.
The platform’s SaaS-based architecture enables scaling and deployment across public cloud infrastructures. The system's virtual Data Center (vDC) provides scalability to manage millions of authentications daily, supporting enterprises such as major retailers with high traffic demands. For service availability the SLA includes 99.95% uptime. The platform includes developer-friendly components such as SDKs and open-source integrations, to assist with customized deployment in a range of business environments.
Beyond Identity is a product leader and an innovation leader. This is based on the capabilities described above. Their approach uses device-bound credentials to help reduce credential-based risks. Their RealityCheck feature, introduced to safeguard against deep fake threats, addresses emerging identity verification challenges in collaborative environments such as Zoom and Microsoft Teams.
Organizations looking for a passwordless solution that eliminates shared secrets entirely by binding identity to cryptographic keys stored securely on the user’s device, without creating OTPs or passcodes, should consider Beyond Identity.
| Strengths |
|
| Challenges |
|
cidaas – cidaas
| Leader in | | | | |
Widas ID GmbH, a private German company, was established in 1997. In 2018 they launched cidaas, their CIAM product and brand. cidaas is most active in the DACH region in Europe but has been expanding into Benelux and the Nordic countries, as well as gaining some customer traction in the US and India. cidaas is delivered as SaaS. Their SaaS is hosted by a public IaaS provider and their own facilities, in data centers in Europe, North America, and Asia. Multitenant and single tenant options are available.
The cidaas platform offers full support for passwordless methods including biometric device authentication (such as Touch ID/Face ID), the FIDO2 / WebAuthn standard, magic-links via email, and OTPs via SMS or authenticator apps. It provides interoperability across a broad set of channels including web, mobile, and shared devices, through support of standards such as OAuth 2.0, OIDC and SAML 2.0. However, the platform is not listed as FIDO-certified in the FIDO Alliance product directory.
Any device can be registered with cidaas, including mobile, IoT, wearables and more. cidaas offers an advanced device management. The platform does not provide device posture checks, such as detailed OS posture evaluation (including root or jailbreak detection) or EDR-grade device integrity assessment.
For user lifecycle and device management, cidaas offers multi-channel onboarding, supports self-service registration and credential binding, and provides device recognition features for consumer identities. This is achieved through its API-driven architecture, where every function (registration, verification, consent, authentication, and recovery) can be embedded in different channels without redesigning the backend. Users can onboard themselves using existing social media accounts (such as Google, Apple, and Facebook). Users can begin with minimal information and later complete additional verification (such as cidaas ID Validator, which performs document and face match checks) as trust requirements increase. Onboarding verification can occur via email magic links, SMS OTP, Quick Response (QR) code scanning, or biometric confirmation.
For adaptive risk-based authentication and policy enforcement, cidaas supports this through integration of “smart” MFA and fraud-detection mechanisms, enabling conditional flows based on suspicious behavior, risk signals (such as geo-velocity, IP reputation, and others) or device context. cidaas includes proprietary fraud-detection modules.
For account recovery, it supports passwordless reauthentication and fallback channels such as email OTP, SMS OTP, and biometric verification. This also includes social account linkage for recovery as well as help-desk–assisted options.
The platform is built on microservices, Kubernetes, and elastic cloud infrastructure, making it inherently scalable to meet the needs of large B2C deployments. It is developed and hosted in Germany. Its integration and orchestration capabilities are based on an orchestration layer known as cnips, which acts as an iPaaS service for identity workflows. This enables low-code and no-code integration of identity processes across SaaS applications, legacy systems, and custom environments.
cidaas is a overall leader in this leadership compass. The platform's strengths include its API-first microservices architecture, which allows every identity function to be deployed across web, mobile, and IoT channels. Its combination of FIDO2/WebAuthn passkey support, adaptive MFA, and integrated fraud-detection and identity-verification (ID Validator) services provides strong, standards-based, and compliant passwordless authentication at consumer scale.
The solution is likely to be attractive to European organizations in sectors like retail, telecommunications, financial services, and regulated industries that seek a secure, sovereign platform.
| Strengths |
|
| Challenges |
|
CyberArk – CyberArk Identity Security Platform
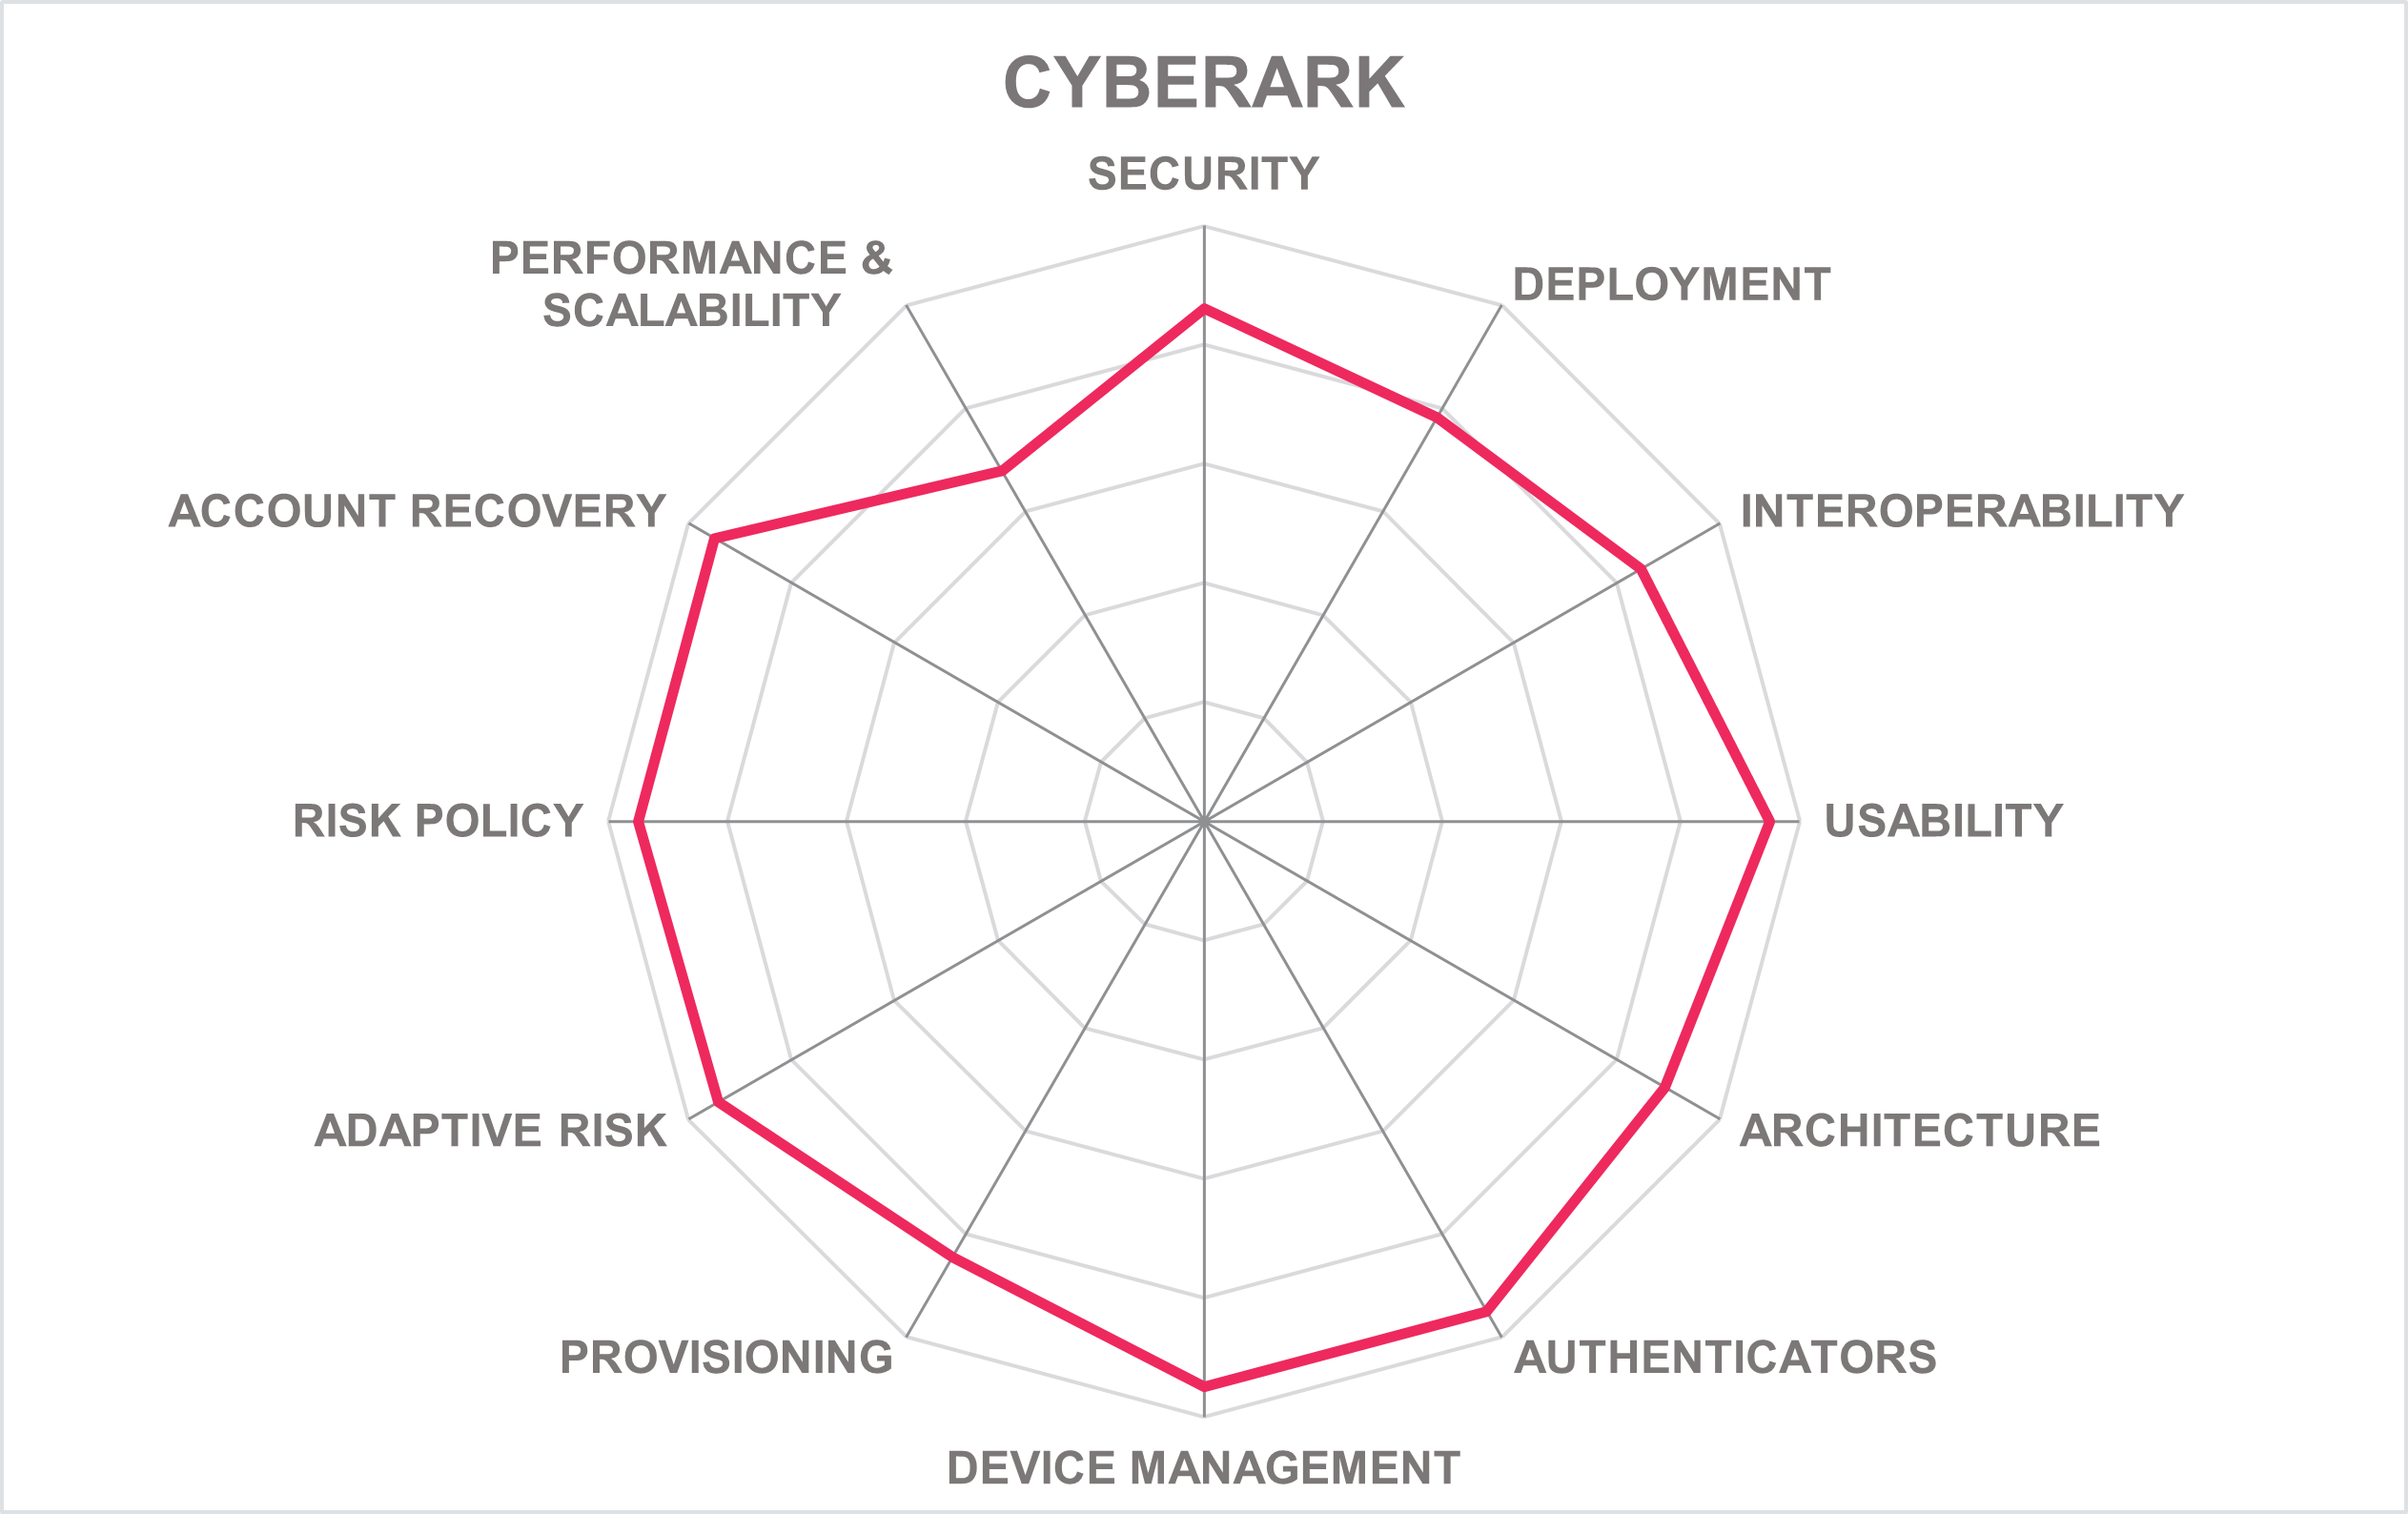
| Leader in | | | | |
CyberArk was founded in 1999 in Israel (Petah Tikva) and has global headquarters there, with a US presence in Newton, Massachusetts. In July 2025 Palo Alto Networks announced that it had agreed to acquire CyberArk, at the time of writing this acquisition has not completed. CyberArk offers the “Passwordless Experience” and its broader CyberArk Identity Security Platform supports FIDO2-based passkeys, biometrics, and device-bound authentication methods.
Within this platform, CyberArk Identity provides SaaS-based identity and access management, including SSO, MFA, passwordless, Secure Web Sessions and lifecycle management. For B2C and partner-facing scenarios, CyberArk offers CyberArk Customer Identity, which targets CIAM use cases and provides secure access to consumer websites and apps, with strong AI-powered, risk-aware, and password-free authentication, directory/user management, and developer tools.
The CyberArk Identity Platform delivers phishing-resistant passwordless login with passkeys/FIDO2/WebAuthn using both on-device authenticators including Windows Hello, Touch ID and external FIDO2 security keys such as YubiKey. CyberArk is listed as a FIDO Certified Server vendor in the FIDO Alliance directory. The platform integrates with consumer-facing applications and APIs via SAML, OAuth 2.0, and OIDC, enabling Customer Identity to act as an IdP front end for B2C services, while the underlying identity data can reside in CyberArk’s cloud directory or external systems.
CyberArk’s passwordless approach is strongly authenticator-centric rather than deeply device-posture-centric for B2C. On the access management side, the platform supports FIDO2 authenticators (on-device or external) and the CyberArk Mobile app, effectively binding customer access to trusted authenticators that hold private keys in secure hardware. There is no root/jailbreak detection or deep device attestation as part of the standard B2C CIAM capabilities.
CyberArk Customer Identity provides a cloud directory and extensive SCIM-based provisioning capabilities, enabling both inbound and outbound user lifecycle management between CyberArk and other systems such as Entra ID, Okta, SailPoint and SAML applications. For CIAM CyberArk supports fully customizable self-service registration through embeddable widgets and user APIs. Customers can enable social registration or build branded registration experiences that integrate with policy controls, identity verification, and adaptive MFA for secure onboarding.
The platform evaluates adaptive risk factors including IP address, geo-location, geo-velocity, access time, device ID, and type. Risk scores are based on user behavior patterns such as typical access time and location. Anomalies automatically trigger elevated risk scores and step-up authentication.
CyberArk Customer Identity supports policy authoring through JSON imports, graphical interfaces with flow charts, and customizable adaptive MFA. Policies can be constructed to include multiple actions depending upon risk scores, calculated on a 0-100 scale with four risk levels (None, Low, Medium, and High). The risk analysis engine supports API access for integration with third-party systems, allowing policy owners to finely tune the environment-specific ML models.
It supports account recovery workflows based on any supported authentication factor, such as FIDO2, OTPs, push notifications, or QR codes. Recovery policies can include layered verification (such as CAPTCHA or device checks) and integrate with third-party ID or MFA providers via Remote Authentication Dial-In User Service (RADIUS). Administrators can tailor recovery paths by user group and initiate or approve re-registration directly.
CyberArk is positioned as a leader in both product and innovation in the leadership compass. This is based on its breadth of functionality, maturity, and continued innovation. Its solution is differentiated by a unified approach to passwordless authentication, and its ability to monitor and control activity at the session level with step-up authentication triggered inside live applications.
The CyberArk Identity Security Platform Is likely to be attractive to large enterprises operating within highly regulated sectors such as finance, government, and healthcare. The platform's audit and compliance capabilities, along with its extensive partner ecosystem, make it attractive to organizations across a wide range of geographies, including North America, EMEA, APAC, and Latin America (LATAM)
| Strengths |
|
| Challenges |
|
Descope – Descope
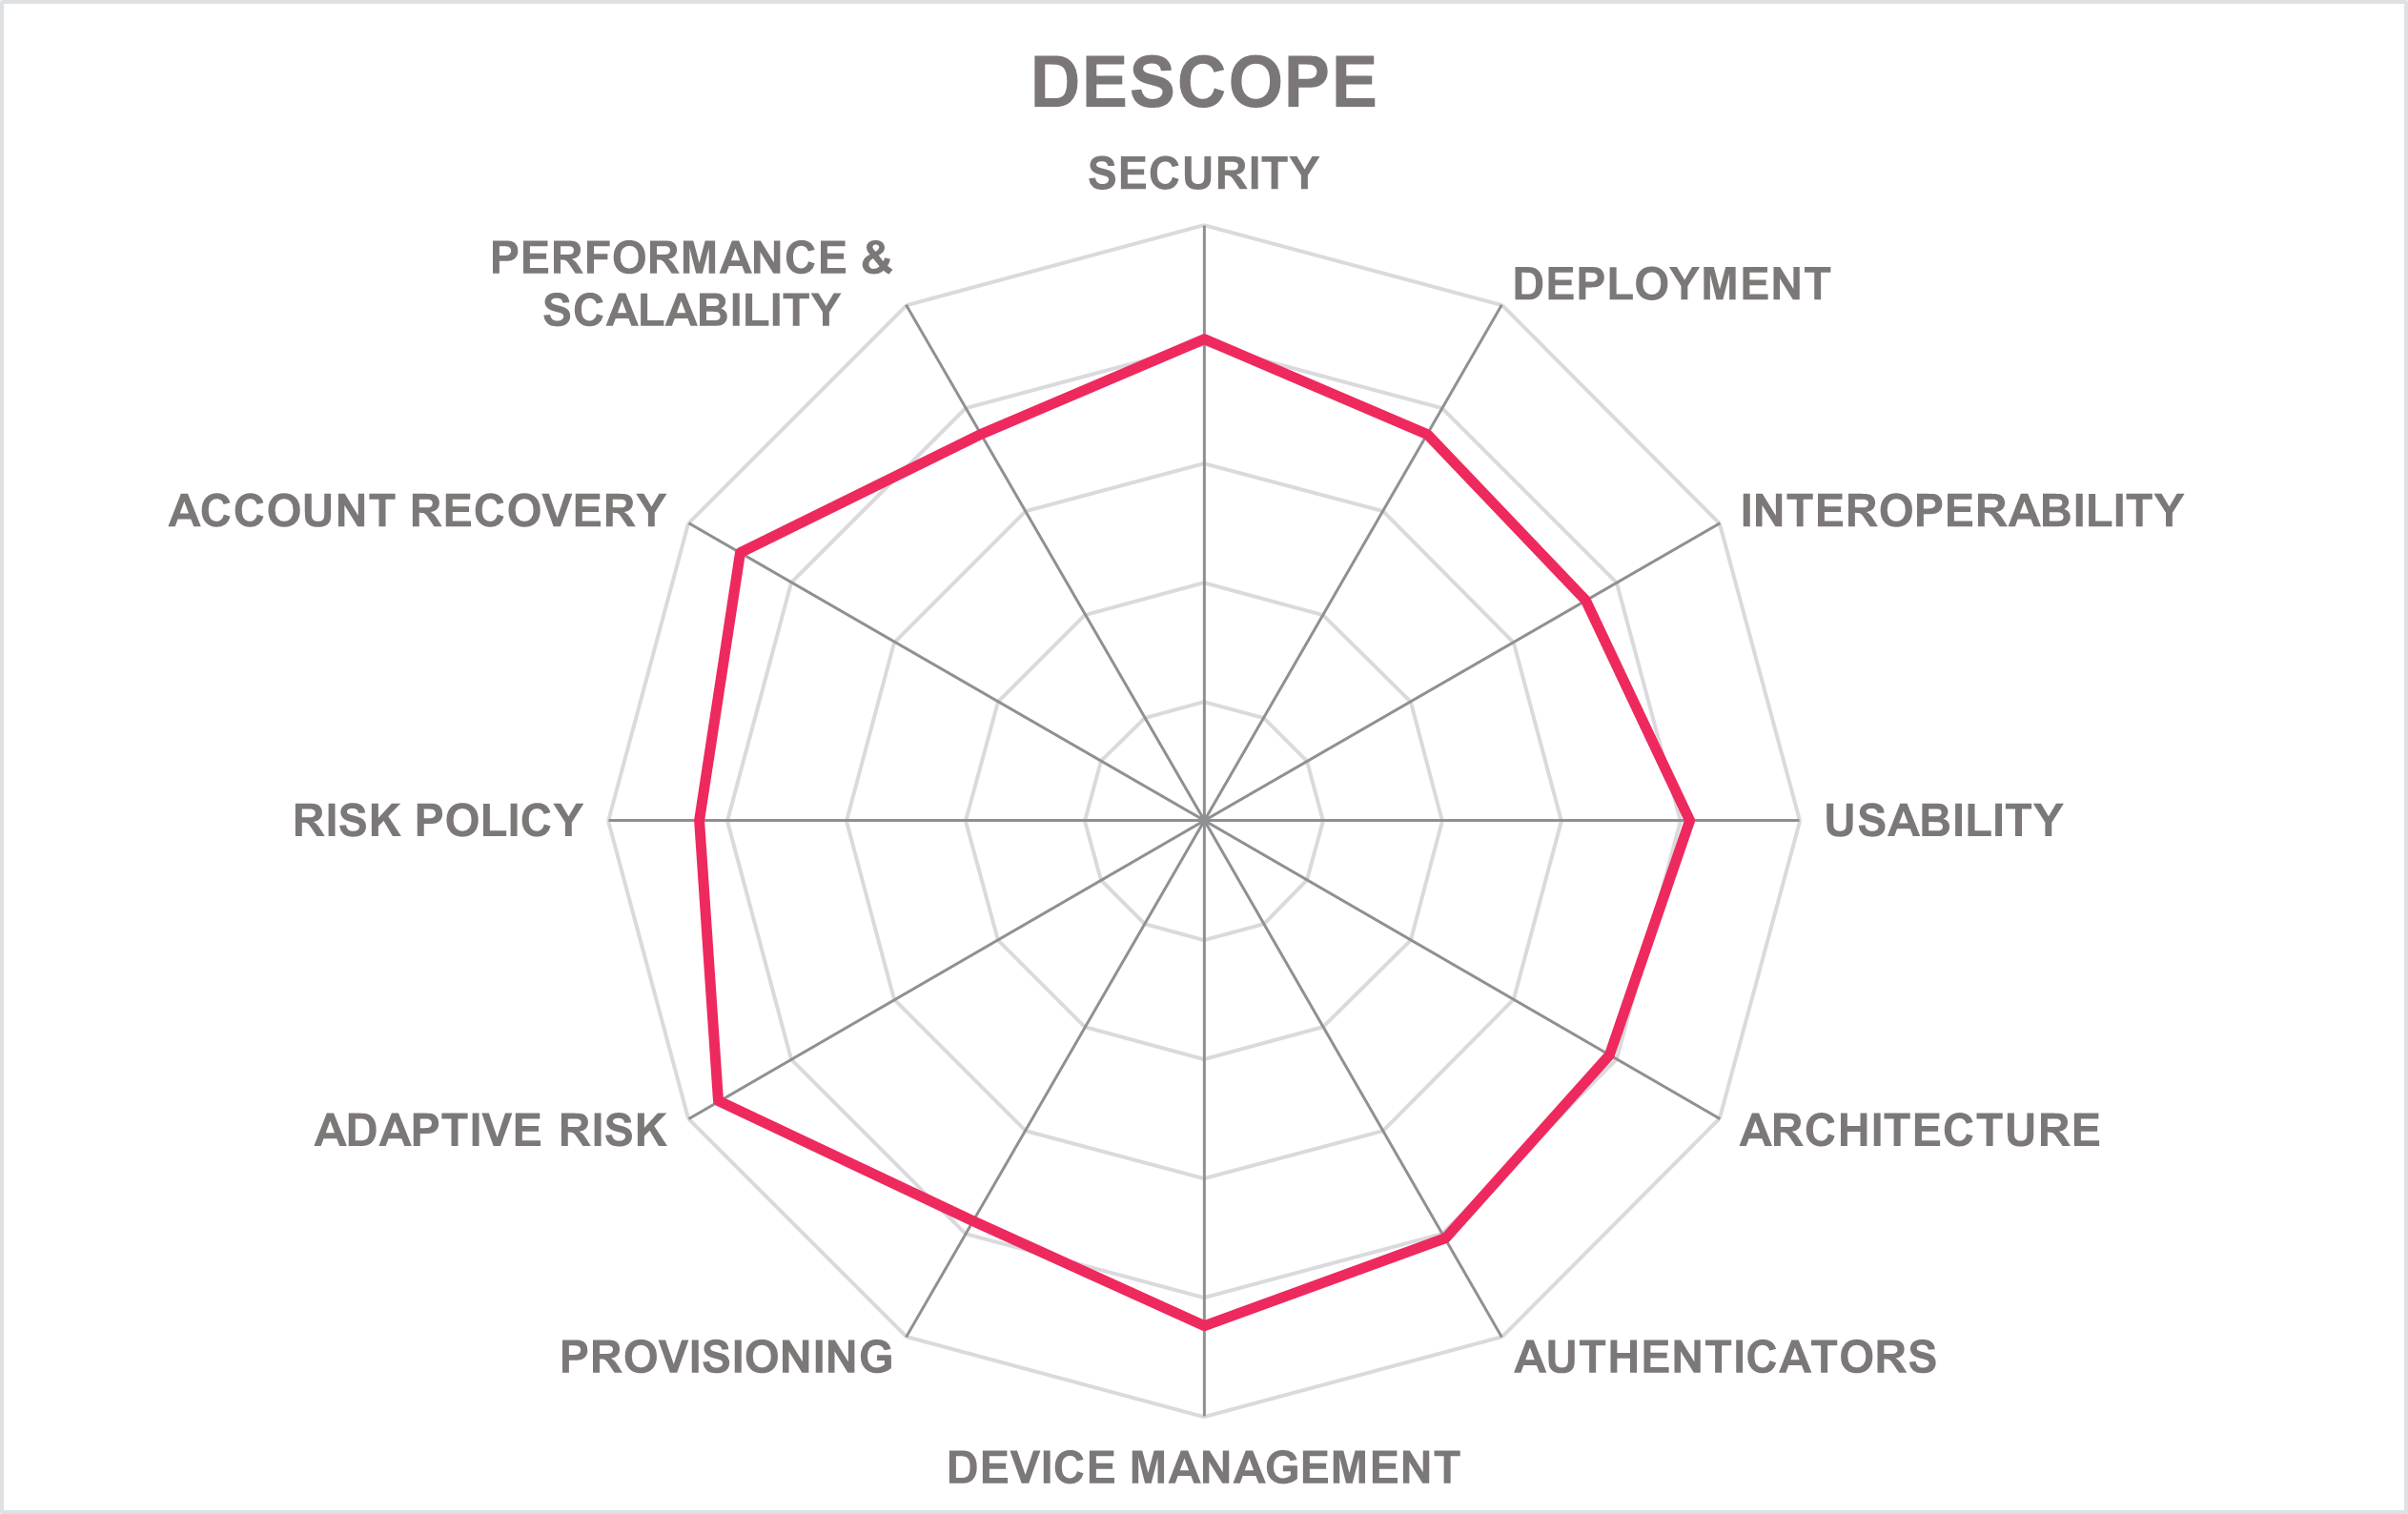
Descope, a well-funded early-stage startup headquartered in Los Altos, California, in the US, emerged from stealth mode in early 2023. Despite its recent entry into the market, Descope has established a geographically distributed customer and support footprint. Their solution is SaaS only and is hosted on a single Tier 1 IaaS provider with deployments in both the US and EU. In addition to the public SaaS, Descope offer two private cloud deployment options. One is a Descope-managed dedicated private cloud environment, and the other is a dedicated cloud managed on the customer's cloud environment. Both are currently supported on AWS. Descope offer both multitenant and single tenant . The service is offered via subscription, with pricing tiers based on MAUs, number of applications, and federation requirements.
Descope targets primarily B2C and Business-to-Business-to-Consumer (B2B2C) scenarios, letting product teams design the entire customer journey, from sign-up and sign-in to MFA, social/federated login, step-up and account recovery using visual “flows”, SDKs, and APIs.
Descope’s passwordless authentication solution supports a broad range of standards-based authentication methods. It provides FIDO2/WebAuthn passkey support with native biometric experiences on iOS and Android, allowing users to authenticate with Touch ID, Face ID, or platform security keys. Its FIDO server is FIDO2 certified by the FIDO Alliance. Descope also supports magic links and OTPs via email, SMS, voice, or WhatsApp. Developers can use Descope’s SDKs and Flow Builder to build login journeys without passwords for web or mobile. The platform supports SAML 2.0, OAuth 2.0, and OIDC, providing compatibility with external identity providers and CIAM systems.
Descope includes a device registration and fingerprinting system to recognize returning devices and detect anomalies across sessions. Its SDKs are designed to bind user sessions to trusted devices while maintaining support for re-registration when a device is lost or replaced. The platform integrates device fingerprinting and bot detection, enabling organizations to detect risky access. It does not include checks on OS patch state, jailbreak/root detection, or endpoint Anti-Virus (AV)/EDR posture checks as standard. Descope also supports multi-device access, allowing users to log in from any device while maintaining consistent trust and risk posture.
Descope offers no-code and API-driven user provisioning, enabling both user-initiated self-registration and administrative onboarding for consumer-scale applications. The platform supports SCIM and directory synchronization through its OIDC and SAML integrations. Developers can automate registration and authentication flows using Descope’s Flow Builder and APIs, enabling integration into CIAM environments. For consumer use cases, users can self-register using passkeys, OTPs, or magic links, creating verified accounts without the need for passwords.
Descope adaptive risk engine continuously evaluates risk factors such as device fingerprints, IP reputation, geo-velocity, and user behavioral patterns. The engine can automatically escalate authentication requirements when anomalies are detected, such as an unfamiliar device, suspicious IP, or “impossible travel” event. It integrates third-party device intelligence feeds for enhanced threat detection, sources such as AbuseIPDB, reCAPTCHA, Forter, Fingerprint, and other fraud services. Administrators can define step-up or block policies through conditional logic.
Descope’s risk policy framework is customizable, allowing organizations to define authentication logic visually through its Flow Builder UI or programmatically via JSON-based configurations and APIs. Policies can include conditional logic based on risk thresholds, device trust, or user context. The system supports weighted factors and step-up authentication, enforcing additional biometric or OTP verification when contextual risk scores exceed defined thresholds. Descope’s risk engine can also integrate with external fraud detection or authorization services.
Users can recover accounts through pre-issued recovery codes, email, or SMS OTPs, or by re-binding via trusted devices. Administrators can configure recovery policies that align with risk levels, for example, requiring biometric re-verification for high-assurance accounts or allowing OTP-based recovery for low-risk consumer profiles.
Descope is a cloud-native, SaaS-based identity platform built on an elastic, distributed architecture capable of supporting high-volume consumer authentication workloads. Its SLA offers 99.99% uptime.
In this leadership compass Descope is positioned as a Challenger in both product and innovation. While the solution supports a wide range of authenticator options, While the product capabilities across the range evaluated are good they are just short of being leading
Descope is suited to digital-native organizations, SaaS providers, and enterprises seeking to modernize consumer and partner identity journeys. It appeals to developers who require flexible integration options without high maintenance overhead, and to businesses prioritizing user experience alongside security.
| Strengths |
|
| Challenges |
|
Ergon – Airlock IAM
| Leader in | | | | |
Ergon Informatik AG was founded in 1984 in Switzerland and is Swiss software house specializing in digitalization, security, and bespoke enterprise solutions. Headquartered in Zurich, Switzerland, Ergon launched its ‘Airlock’ security product line in 2002. The cornerstone of its offering is the Airlock Secure Access Hub, a unified platform combining IAM, and Web Application & API Protection (WAAP).
Airlock IAM delivers authentication, SSO, federation (OAuth 2.0/OIDC/SAML), adaptive authentication, transaction approval, self-services and multifactor/passwordless authentication for external users. It is offered as a Customer IAM platform, scalable to large user populations and is widely used by Swiss and European financial services, insurance, and other customer-facing sectors.
Airlock IAM provides FIDO authentication with support for FIDO1 and FIDO2 authenticators and passkeys, including Universal Serial Bus (USB) security keys, Near Field Communication (NFC) tokens, and platform authenticators such as Windows Hello and mobile OS implementations. It supports passwordless and user nameless authentication for FIDO2-compliant authenticators, allowing passkeys to function as the primary credential without passwords. Airlock IAM acts as the FIDO relying party, using the browser’s WebAuthn API and Client to Authenticator Protocol versions 1 and 2 (CTAP1/CTAP2) to communicate with authenticators.
Airlock IAM provides SSO and federation via OAuth2, OIDC, and SAML, enabling it to function as a central IdP for consumer-facing websites, portals, and APIs. Login flows are driven via the Loginapp UI and Representational State Transfer (REST) APIs, which can be integrated into native and Single-Page Application (SPA) front ends. FIDO passwordless flows can be implemented either through the standard login UI or via REST-based flows.
The Airlock IAM solution offers customizable device registration workflows and supports a wide variety of devices including mobile, smartwatches, FIDO keys, and more. The focus is centered on authenticator and token management rather than deep endpoint posture assessment.
Airlock IAM is designed as a CIAM platform and includes self-registration and user lifecycle capabilities. The user registration self-service allows new users to create accounts via the Loginapp, with configurable data collection and the ability to grant access immediately or limit it to specific applications. It supports Bring Your Own Identity (BYOI) and social registration, linking social identities that support OAuth/OIDC to internal IAM accounts for B2C journeys. Identity attributes from remote IDPs can be used for automated account registration and account linking, enabling low-friction onboarding from existing identities like bank or telco IDs. For provisioning at scale, Airlock integrates with external directories and user stores and supports consent management and GDPR-aligned profile handling; it also offers REST APIs for user management and admin-driven lifecycle operations.
This solution offers adaptive risk evaluation covering IP reputation, geo-location, geo-velocity, date/time, device ID, device type, device fingerprint, software signature, device posture assessment, and device reputation. In-platform identity verification services and integration with Fraud Reduction Intelligence Platforms (FRIPs) enhance security. In addition, compromised credential intelligence allows for real-time risk-based access controls, to adjust the authentication strength based on evaluated risk.
Airlock IAM acts as a policy enforcement point for customer access by combining authentication flows, authorization policies, adaptive rules, and transaction approval. Risk policy authoring supports multiple import methods including YAML and GUI with flow chart models. The solution evaluates risk factors yielding risk 'tags' rather than scores, enabling a multi-dimensional risk assessment. Risk policies are addressable via an API, offering steps like step-up authentication based on risk evaluation. The integration with external services is facilitated through scripts or plugins, enhancing the solution’s flexibility and adaptability to external risk inputs.
Administrators can create granular access controls using rules and logical operators, Role-Based and Attribute-Based Access Controls (RBAC/ABAC), re-authentication/timeouts by role, and workflow-based policies built in the admin app (no-code/low-code) with flow-chart visualization. Policies can be enforced across federated apps and APIs via the Secure Access Hub, with SSO and token translation ensuring consistent application of conditional/step-up requirements.
Airlock includes user self-services including password reset, factor registration/management, and help-desk-assisted token administration) so consumers can securely regain access or re-enroll factors without reintroducing weak credentials. The combination of multifactor options (email/SMS OTP, app factors, certificates, and FIDO2) provides multiple recovery lanes according to assurance needs.
The solution is available for on-premises installation on selected Linux distributions and on IaaS or private clouds. They also have SaaS that is hosted in a single Tier 1 IaaS provider in datacenters in Europe/Switzerland. They have multiple pricing tiers, based on the number of registered users. Some features are priced separately or are available only on the higher tiers.
Ergon is a product leader in B2C passwordless authentication because of its deeply integrated security architecture and mature technical stack that merges FIDO2/WebAuthn passwordless login, adaptive risk analysis, and Web Application and API Protection (WAAP) within a single platform.
Organizations with strong security and compliance needs such as financial institutions, insurers, and government agencies should consider Ergon Airlock. Its Swiss development and data sovereignty position resonate strongly with European and Middle Eastern customers sensitive to US Cloud Act implications.
| Strengths |
|
| Challenges |
|
Exostar – Access One Platform
| Leader in | | | | |
Exostar was founded in 2000 as a joint venture by BAE Systems, Boeing, Lockheed Martin, Raytheon, and Rolls-Royce, later joined by Merck. With headquarters in Herndon, Virginia, in the US, the company operates secure, compliant collaboration and identity access platforms for highly regulated industries, notably aerospace/defense, life sciences, and healthcare. In 2023, Exostar was acquired by Arlington Capital Partners, a private equity firm that focuses on these same market verticals.
Access One (formerly styled “Access: One”) is Exostar’s cloud-native identity and access management product within The Exostar Platform. It unifies identity, strong authentication, access management, and identity governance across employees, contractors, third parties, and consumers, and is delivered as a SaaS “identity fabric.” From a B2C perspective, Access One is not a classic retail CIAM only; it is an external access platform for regulated ecosystems, covering workforce, partner, and customer-facing mobile and web experiences.
Access One provides a broad authentication portfolio designed to support passwordless, phishing-resistant access for employees, partners, and external users, including consumers. Strong authentication is a core goal, and the platform offers FIDO2 passkeys for passwordless login as a default option across devices. In addition, Exostar supports third-party authentication apps, including Google Authenticator, Microsoft, Duo Security, and Okta.
The platform supports financial transaction signing and includes the ability to manage a key pair per user, and to sign, encrypt, decrypt, and securely store data. The platform provides a packaged API that host applications use for transaction signing.
The platform support is focused on mobile devices. As it uses the OAuth device flow, this is easy to extend to include IoT, wearables, and other smart devices. It supports posture checks for mobile devices, including jailbreak/root detection. It approaches device security posture through authenticator and access-policy management rather than deep, EDR-style posture assessment. The platform secures access across devices with FIDO2 passkeys and other strong authenticators, meaning the device itself holds the private key or token (for example, Windows Hello, platform biometrics, and hardware security keys). Device registration flows are defined via workflow and can be customized.
The platform offers user self-service features. It also supports managed registration, invitation management, and delegated administration (where administrators can invite or administer users within their organization/sub-tenant). It provides an out-of-the-box self-service portal application (available via web and mobile). This can be configured for a customer's look and feel and provides a complete set of registration, recovery, and credential management services, including support for Terms and Conditions management.
The adaptive risk management capabilities include evaluating IP addresses, known bad IP/network ranges, geo-location, date/time, device ID, and device type. The authorization token support provided makes it possible to define required and forbidden session characteristics. In addition, the Access One Mobile SDK provides support for identifying jailbroken devices, while any other user detail (such as device, OS, or any other detail available by default from the browser) can be used to assist with authentication decisions. Online fraud detection is possible through integration with third party tools, such as Akamai, ThreatMetrix, and IBM X-Force.
Risk policy management is through a GUI with drop-down attributes and flow chart model options. Risk management is based on workflows and plugins. This allows authentication and authorization workflows to call upon multiple third-party risk services and data sources to build up a risk score for a user and implement that as part of the user context. This allows the platform to support a variety of scenarios and integrate with third-party risk engines.
Access One is delivered as a cloud-based, multitenant SaaS platform for identity and access management across employees, partners, and consumers.
Exostar is a product leader in B2C passwordless authentication. This is based upon the capabilities provided by the solution which include identity proofing and credential issuance aligned with Kantara's IAL2 proofing. The platform supports passwordless authentication aligned with FIDO2 standards and can help organizations meet compliance requirements under regulations such as PSD2 and the upcoming PSD3.
Exostar’s passwordless solution is likely to be attractive in regulated markets such as aerospace, defense, government contracting, financial services, healthcare, and life sciences, where regulatory compliance is important. The company has a global presence covering North America, EMEA, and APAC
| Strengths |
|
| Challenges |
|
Futurae Technologies – Futurae Authentication Platform
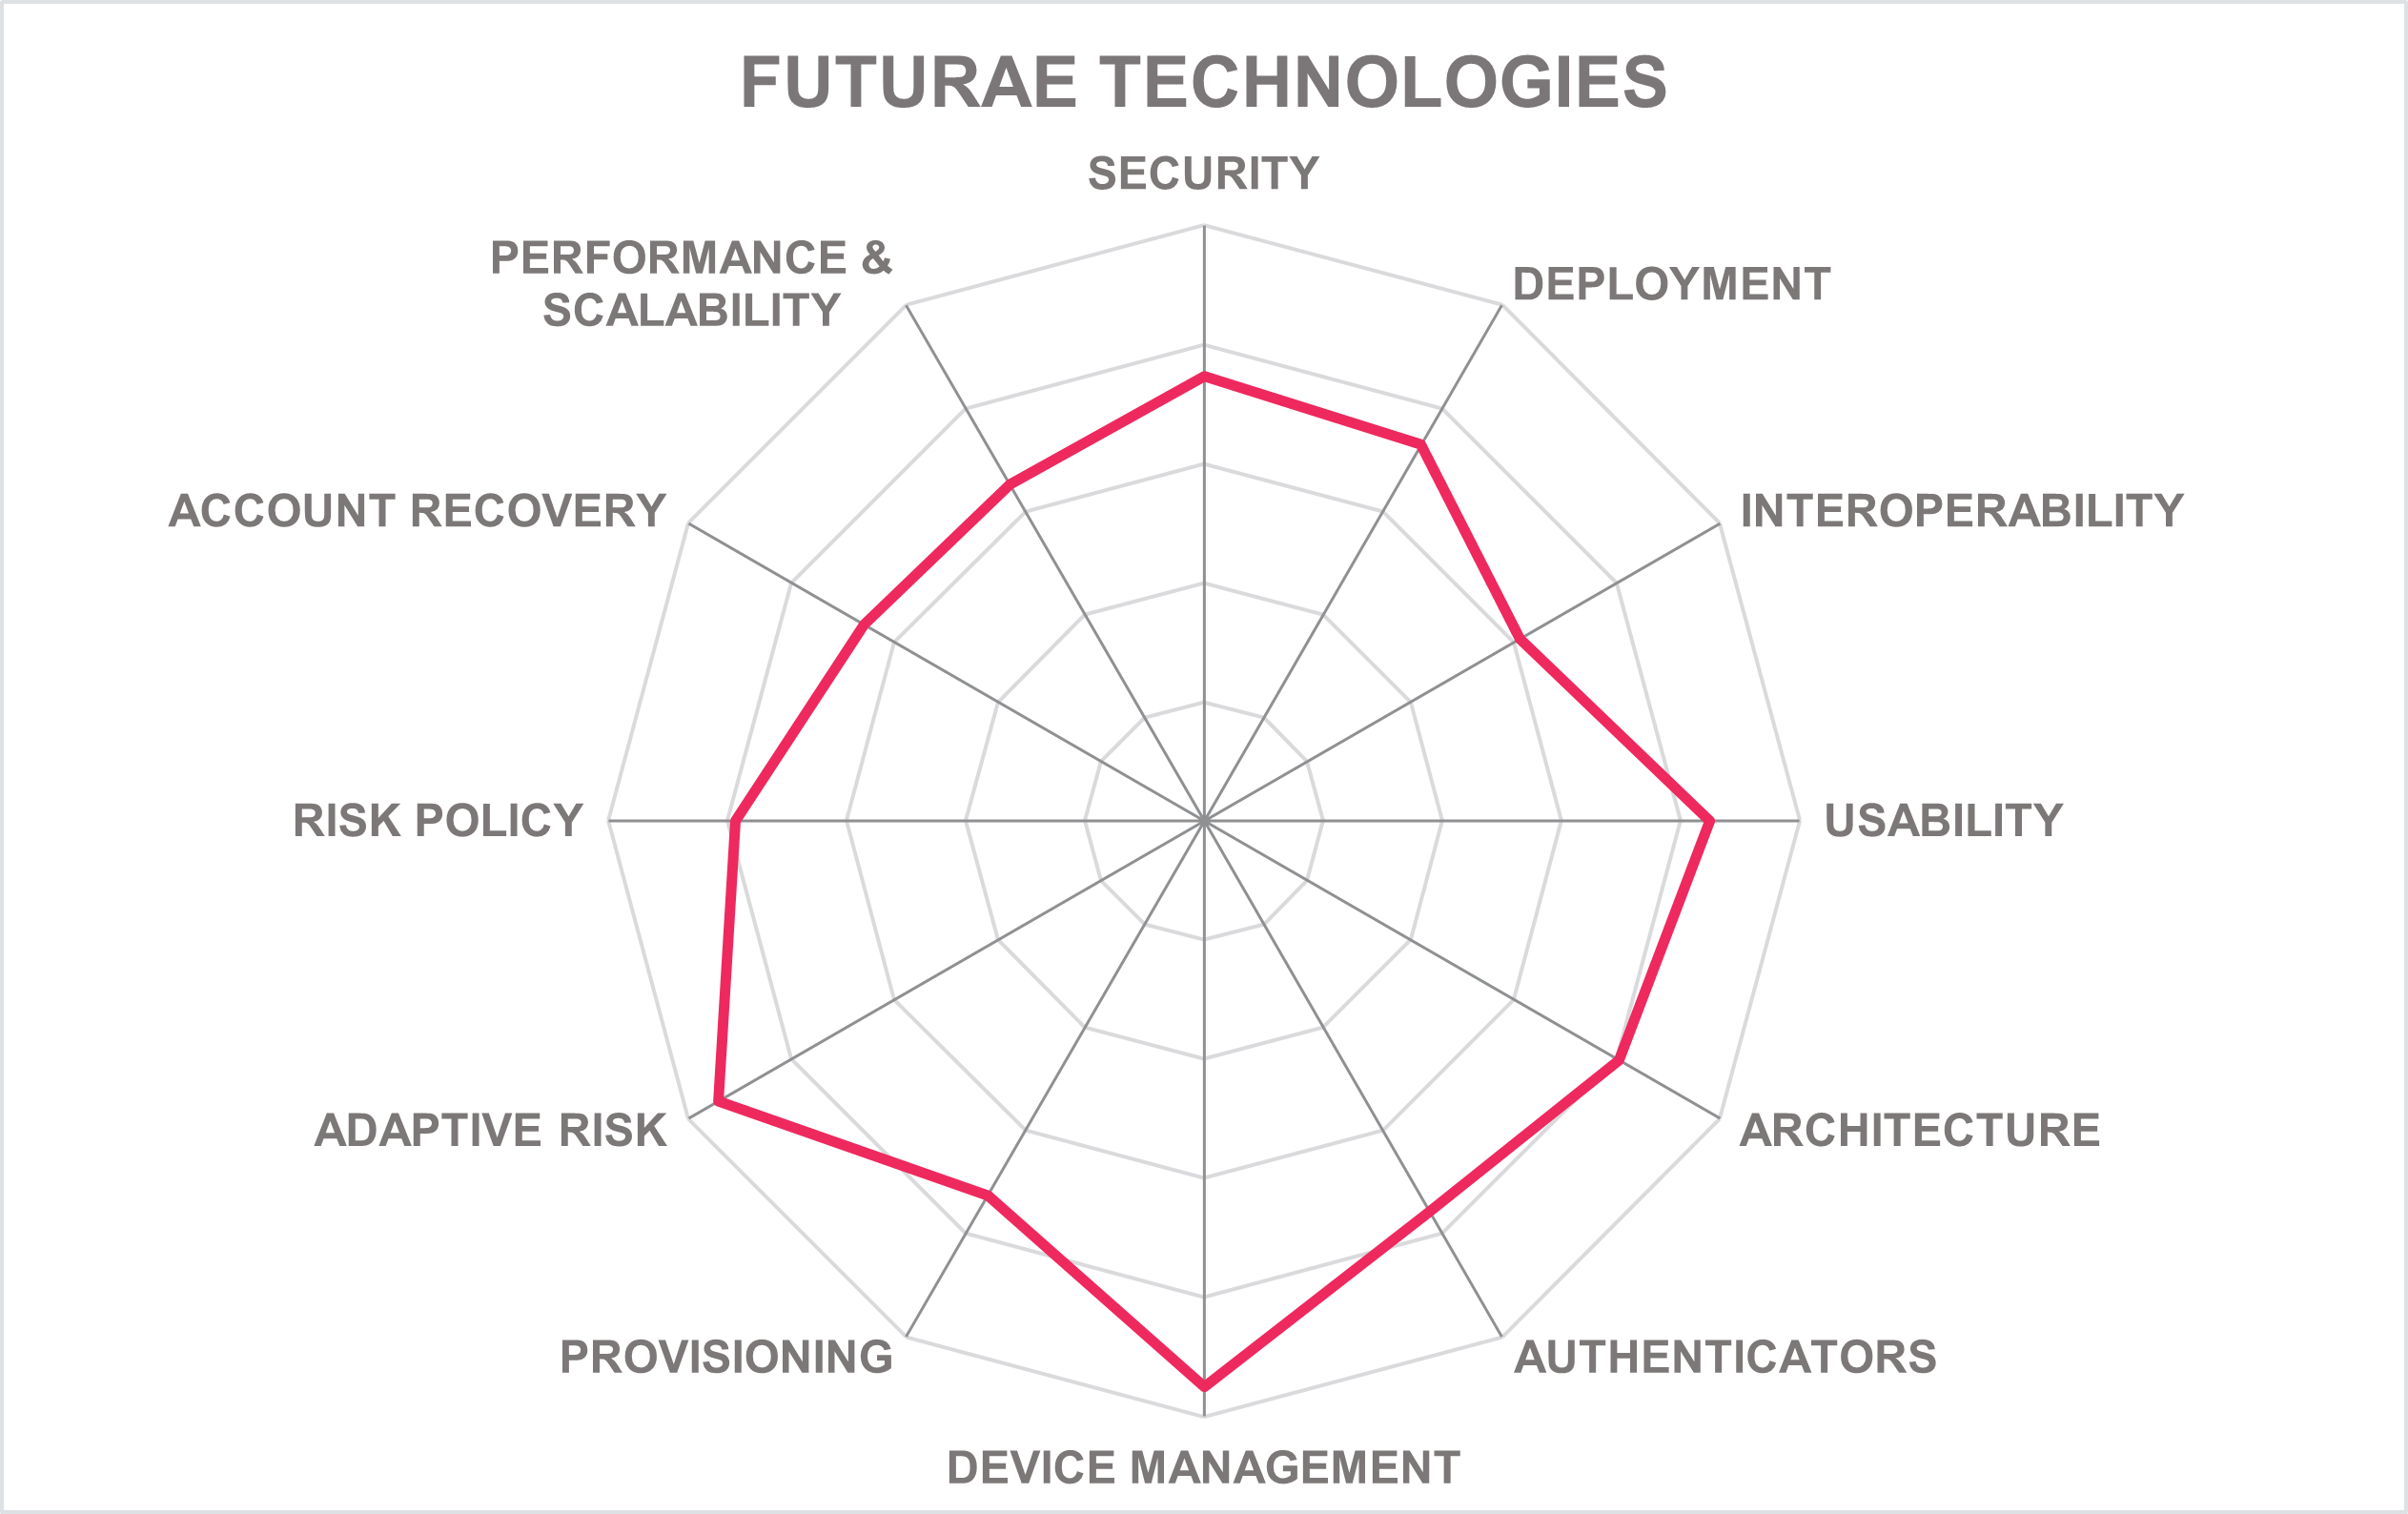
| Leader in | | | | |
Futurae Technologies AG is a Swiss cybersecurity company founded in 2016 as a spin-off from ETH Zurich. Headquartered in Zurich, Switzerland, it specializes in strong customer authentication, frictionless mobile authentication, transaction confirmation, and adaptive security for B2C environments, especially in financial services, healthcare, insurance, mobility, and digital commerce.
Futurae provides a cloud-native Authentication Platform that delivers multifactor and passwordless authentication, transaction signing, adaptive risk analysis, and secure SDK integration for web and mobile apps. Its customers include major European financial institutions and regulated industries. The platform combines FIDO2/WebAuthn passkey support, advanced push authentication, and automatic account recovery in a unified solution designed for consumer-scale. However, Futurae does not appear as a FIDO-Certified Server in the official FIDO Alliance Certified Products Directory
The Futurae platform supports passwordless methods including FIDO2/WebAuthn passkeys, platform and roaming authenticators, and a range of additional factors such as One-Touch push, QR/Offline, and Time-based OTP. The platform API enables integration of these methods into web and mobile apps through developer SDKs. Its “Zero-Touch” and “Soundproof” technologies provide authentication with minimal user interaction while maintaining cryptographic assurance. It also supports transaction signing with high assurance for PSD2.
The platform supports mobile devices and hardware tokens. End-users can register and manage authenticators through mobile SDKs that support biometrics, PINs, and account recovery. The platform supports multi-account and multi-device use, with device security posture checks like root/jailbreak detection as well as automatic account restore on new devices. Administrators manage device states and credentials through the Admin API.
The platform supports user self-registration, with device activation via QR code, magic link, or secure channel. It provides an SDK for white-labelled onboarding flows. Developers can automate enrollment, linking, and credential lifecycle events using REST APIs and webhooks. While support for SCIM is not provided, it offers two public APIs that can be used to provision to/from other cloud services.
Futurae’s platform includes a risk-analysis service named Trust Signals, which monitors user device/behavioral context to help identify and respond to suspicious login or transaction activity in B2C scenarios. Its adaptive SDK and Trust Signals collect contextual data such as IP address, device fingerprint, location, and browser details to adapt the level of authentication based on risk. It also evaluates user and device history tracking. In addition, it can integrate with fraud reduction platforms to expand the factors considered in the evaluation.
Risk policies can be created and managed using a GUI with weighted risk factors yielding risk scores. Policies allow for different actions, such as step-up authentication, based on these scores. It does not support policy import using JSON or XACML. The results of the risk engine can be integrated with any third-party service through the APIs.
Futurae implements Automatic Account Recovery and Adaptive Account Recovery features to help credential restoration when users change devices. The Automatic Account Recovery mechanism enables the user to recover the accounts based on a restore from the previous device. Account Recovery works can also use adaptive contextual data to increase security. It supports email and SMS OTP and uses cryptographically protected re-enrollment processes to maintain assurance and minimize friction. The recovery process is automated and integrated into the SDKs.
Futurae is positioned as an innovation leader and a challenger in product leadership. It recently launched an entirely new ML/Data-driven product to detect context drift and behavioral analytics.
Futurae passwordless platform is likely to be of interest to financial institutions, fintech companies, and payment service providers that demand secure authentication and transaction approval, while aligning with regulatory requirements like PSD2 and PSD3. Their presence in Europe and integration with European regulatory frameworks make them attractive to organizations that require EU data sovereignty and compliance.
| Strengths |
|
| Challenges |
|
HID – Authentication Platform, Risk Management Solution, Enterprise Passkey Management
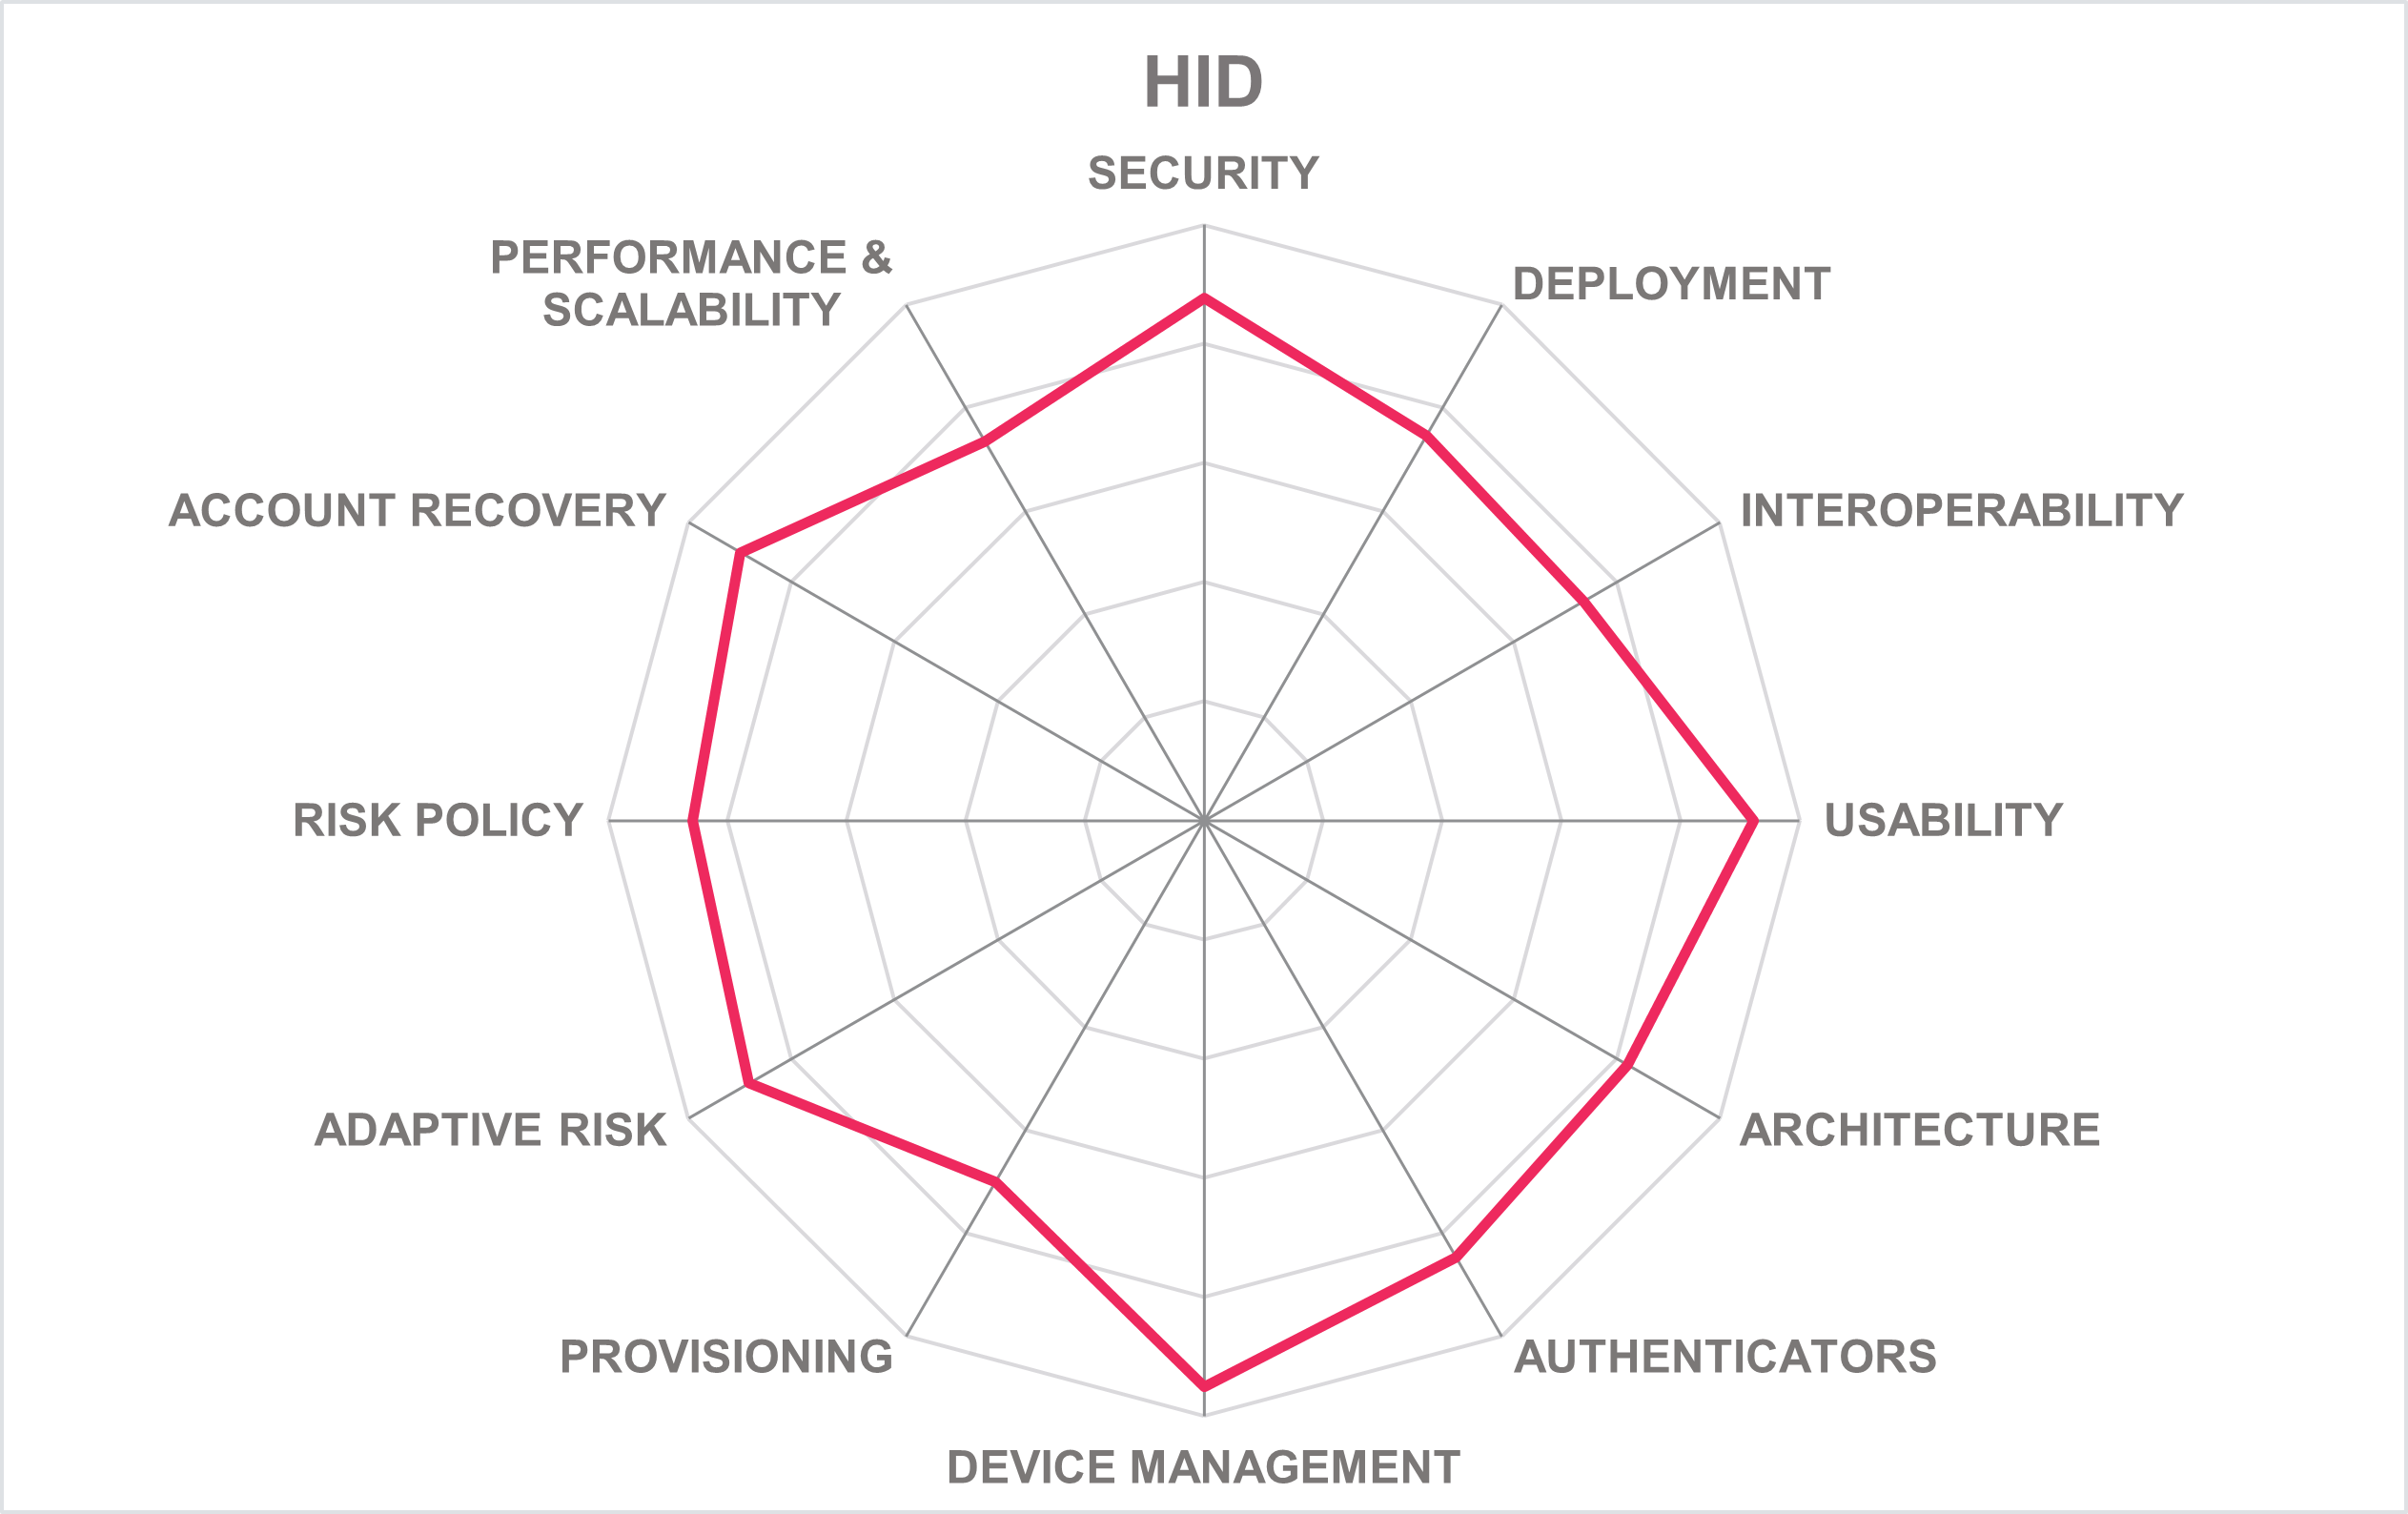
| Leader in | | | | |
HID Global, a subsidiary of ASSA ABLOY, is a US-based identity and access management company headquartered in Austin, Texas. Founded in 1991, HID develops secure identity and access management solutions including physical access control systems, FIDO credentials, Public Key Infrastructure (PKI), biometric authentication, card readers, credential issuance and management, and a cloud authentication platform. HID’s Authentication Platform is a flexible solution for both consumer and workforce, combining strong identity assurance with a seamless user experience. It can be installed on customer premises or in IaaS, and their multitenant SaaS is hosted on AWS in both EU and NA regions provides passwordless login, MFA, and adaptive risk management. HID Approve is a mobile app for push-based authentication and transaction signing used in consumer banking journeys. HID Risk Management Solution (RMS) is an AI/ML driven fraud and risk engine providing fingerprinting, behavioral biometrics, and real-time risk scoring, tightly integrated with the Authentication Platform for adaptive consumer flows.
HID is a FIDO Alliance member and an end-to-end FIDO ecosystem provider, offering a wide range of authenticators that support passkeys. This includes smart cards for physical and digital access, security keys, and device-bound mobile passkeys. HID also provides an authentication platform designed to support passkeys at scale
HID's Authentication Platform supports multiple authentication methods, including username/password, FIDO2, PKI, SMS OTP, mobile push notifications, biometrics (fingerprint and face) and vendor-provided mobile app authentication. It also supports Google Authenticator, Android and iOS biometrics, and Microsoft Authenticator. HID’s Crescendo Keys combine OTP, FIDO2, and PKI in a single device, while Crescendo Cards combine physical access to facilities and passwordless access to digital enterprise resources in a single corporate badge. HID also enables companies to use existing ID badges and smartphones as FIDO credentials, making it easy to get started with passkeys and with minimal disruption.
HID does not provide a generic turnkey “out-of-the-box CIAM portal,” it expects integration into existing B2C portals and mobile apps, where the customer designs the user experience, and HID provides the identity and authenticator backbone. Its APIs and SDKs allow developers to embed authentication and provisioning into custom CIAM workflows. HID Authentication Service supports OIDC and OAuth 2.0 protocols for standards-based authentication and integrates SCIM for user provisioning and lifecycle synchronization.
HID adaptive risk assessment evaluates factors like IP reputation, geo-location, geo-velocity, device identifiers, and more. This is supplemented with device fingerprinting, software signature verification, and posture assessment to form an adaptive, contextually aware authentication framework. By tracking user history and integrating jailbreak/root detection, the solution identifies potential anomalies, feeding data into a risk-based access control system that assists in dynamically adjusting authentication requirements.
Administrators can define authentication policies via a GUI with dropdown attributes using a flow chart model. The system supports weighted risk factors and generates risk scores, on a 0-1000 scale, to influence authentication workflows. These policies can be applied programmatically through APIs or configured in the administrative dashboard.
HID supports account recovery through a variety of channels such as username/password fallback, security questions, and OTPs via email, phone, or push notifications. The platform allows account linking for recovery through trusted accounts and offers help desk-assisted solutions for high-assurance needs.
The HID Authentication Service is delivered as a global cloud platform. By performing cryptographic operations on device through FIDO2 authenticators, latency and backend overhead are minimized. The solution supports enterprise-scale and consumer-scale deployments, leveraging HID's global infrastructure and multitenant architecture.
In this report, HID is recognized as both a product leader and an innovation leader. The platform provides strong capabilities across all the requirements for passwordless authentication for consumers. HID RMS adds behavioral biometrics, device fingerprinting, and AI-driven risk-based authentication.
HID’s suite of solutions is likely to be of interest to enterprises and highly regulated sectors, including financial services, government, and healthcare. Geographically, HID has global coverage, with infrastructure support in both Europe and North America. The flexibility in deployment models supports varied client needs.
| Strengths |
|
| Challenges |
|
HYPR – Identity Assurance Platform
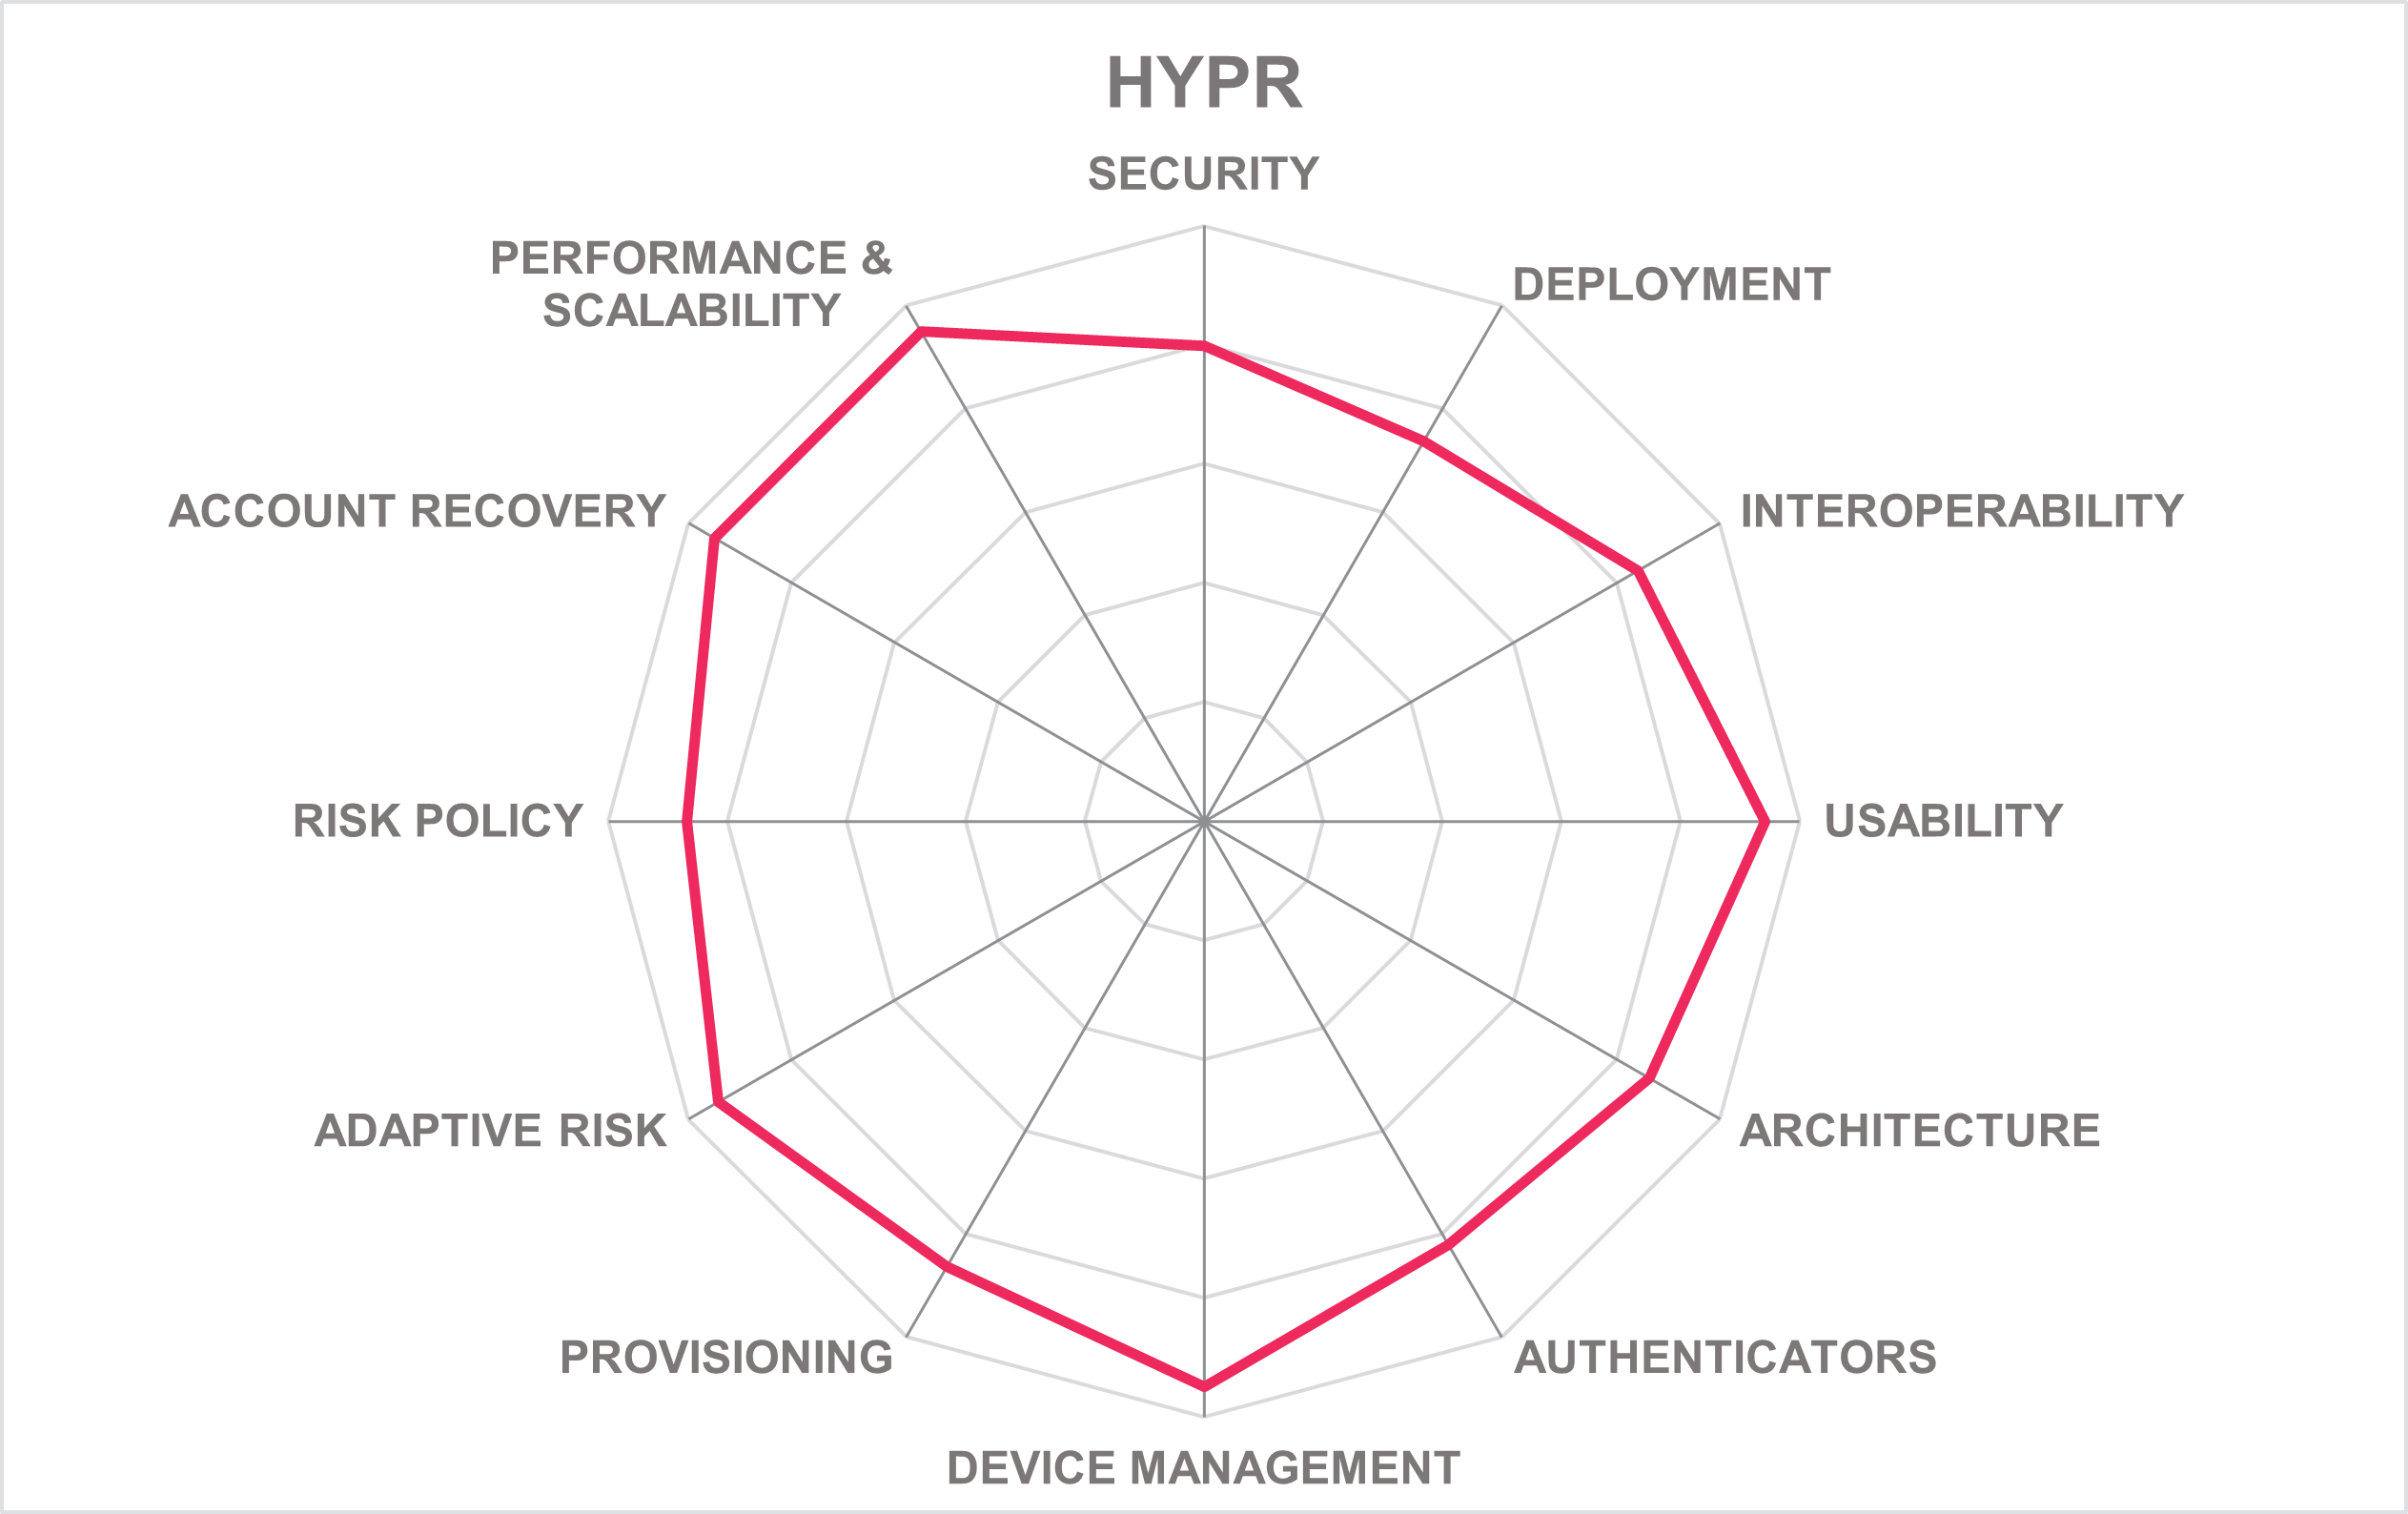
| Leader in | | | | |
HYPR Corp. was founded in 2014 and has its headquarters in New York City in the US. It focuses on phishing-resistant passwordless authentication, adaptive risk mitigation, and automated identity verification. The company’s core offering, the HYPR Identity Assurance Platform, unifies three main capabilities into a single solution. HYPR Authenticate is a FIDO2-certified, passkey-based passwordless MFA for workforce and customers. HYPR Adapt is a real-time identity risk engine for adaptive, risk-based authentication and continuous authentication. HYPR Affirm provides automated identity verification (ID proofing / KYC-style checks) integrated into the same platform.
HYPR implements phishing-resistant passwordless login using FIDO2/WebAuthn passkeys through its browser and mobile SDKs which are FIDO-certified. The platform supports both platform authenticators (such as Windows Hello and Touch ID) and roaming security keys. The HYPR mobile app and SDKs support out-of-band (OOB) push, biometric confirmation and passwordless login to web accounts. HYPR also integrates with Microsoft Entra ID, allowing B2C mobile devices to act as FIDO2 security keys.
The platform supports mobile devices (Android and iOS), hardware security keys, and smart cards (including Yubico, Feitian, IDEMIA and HID Global). It supports customizable device registration workflows and offers mobile apps in public app stores. It also includes device health checks, like jailbreak detection, to ensure a secure authentication environment. For posture, HYPR Adapt consumes telemetry and signals from mobile, endpoint, and browser to build risk profiles and detect suspicious conditions.
For user provisioning, HYPR is designed to plug into existing CIAM/IdP stacks (including Azure AD B2C/Entra, Okta, and Ping), rather than acting as a full identity store itself. Customers use their existing CIAM (such as Azure AD B2C) for identity records and registration, and HYPR for passkey/passwordless enrolment and authentication. HYPR’s CIAM Security/Customer Identity Assurance solution enables flows where users enroll HYPR passkeys or mobile factors during onboarding or at first login, via WebAuthn registration and mobile pairing.
HYPR Adapt is a dedicated identity risk engine, adding continuous and risk-based authentication on top of passkeys. This uses a variety of contextual signals, such as IP address reputation, geo-location, geo-velocity, and device identifiers to assess the risk factors dynamically. It supports integrations with third-party systems, enabling a wider evaluation of risk. This allows for step-up authentication and other responses based on dynamic assessments. HYPR Adapt provides continuous session assurance and adaptive re-verification when risk levels change.
The platform offers risk policy authoring features, allowing the creation of access rules through the Rego policy language and the Open Policy Agent (OPA) framework, as well as a GUI with drop-down menus. These policies enable granular control over risk factors and support API-driven risk analysis, including integration with external systems. Policies can define adaptive thresholds that trigger step-up verification or enforce FIDO-only flows for sensitive transactions. These policies can be integrated into existing access management frameworks via OIDC or SAML.
HYPR does not offer a single, branded customer account recovery module, but it provides building blocks for B2C passwordless recovery. It offers a secure recovery mode that leverages a server-generated Recovery PIN for passwordless re-enrollment. This PIN is renewed after each successful authentication, ensuring one-time use and limited exposure. Users can regain access or register a new authenticator without reintroducing passwords or manual administrative intervention. It does not support recovery options like security questions or email OTPs to avoid the risks from attack vectors related to these.
The HYPR Identity Assurance Platform is a cloud-native solution optimized for scale. By relying on device-resident FIDO2 cryptographic operations, it minimizes server load and latency.
HYPR is positioned as a product and innovation leader in this report. This is based on the breadth and depth of functionality offered by the solution.
HYPR is likely to be attractive to enterprise customers in high-risk sectors such as banking, healthcare, insurance, and critical infrastructure. Its architecture supports global deployments, effectively navigating complex regulatory and infrastructure challenges, including in regions with limitations on services like Google.
| Strengths |
|
| Challenges |
|
IBM – IBM Verify
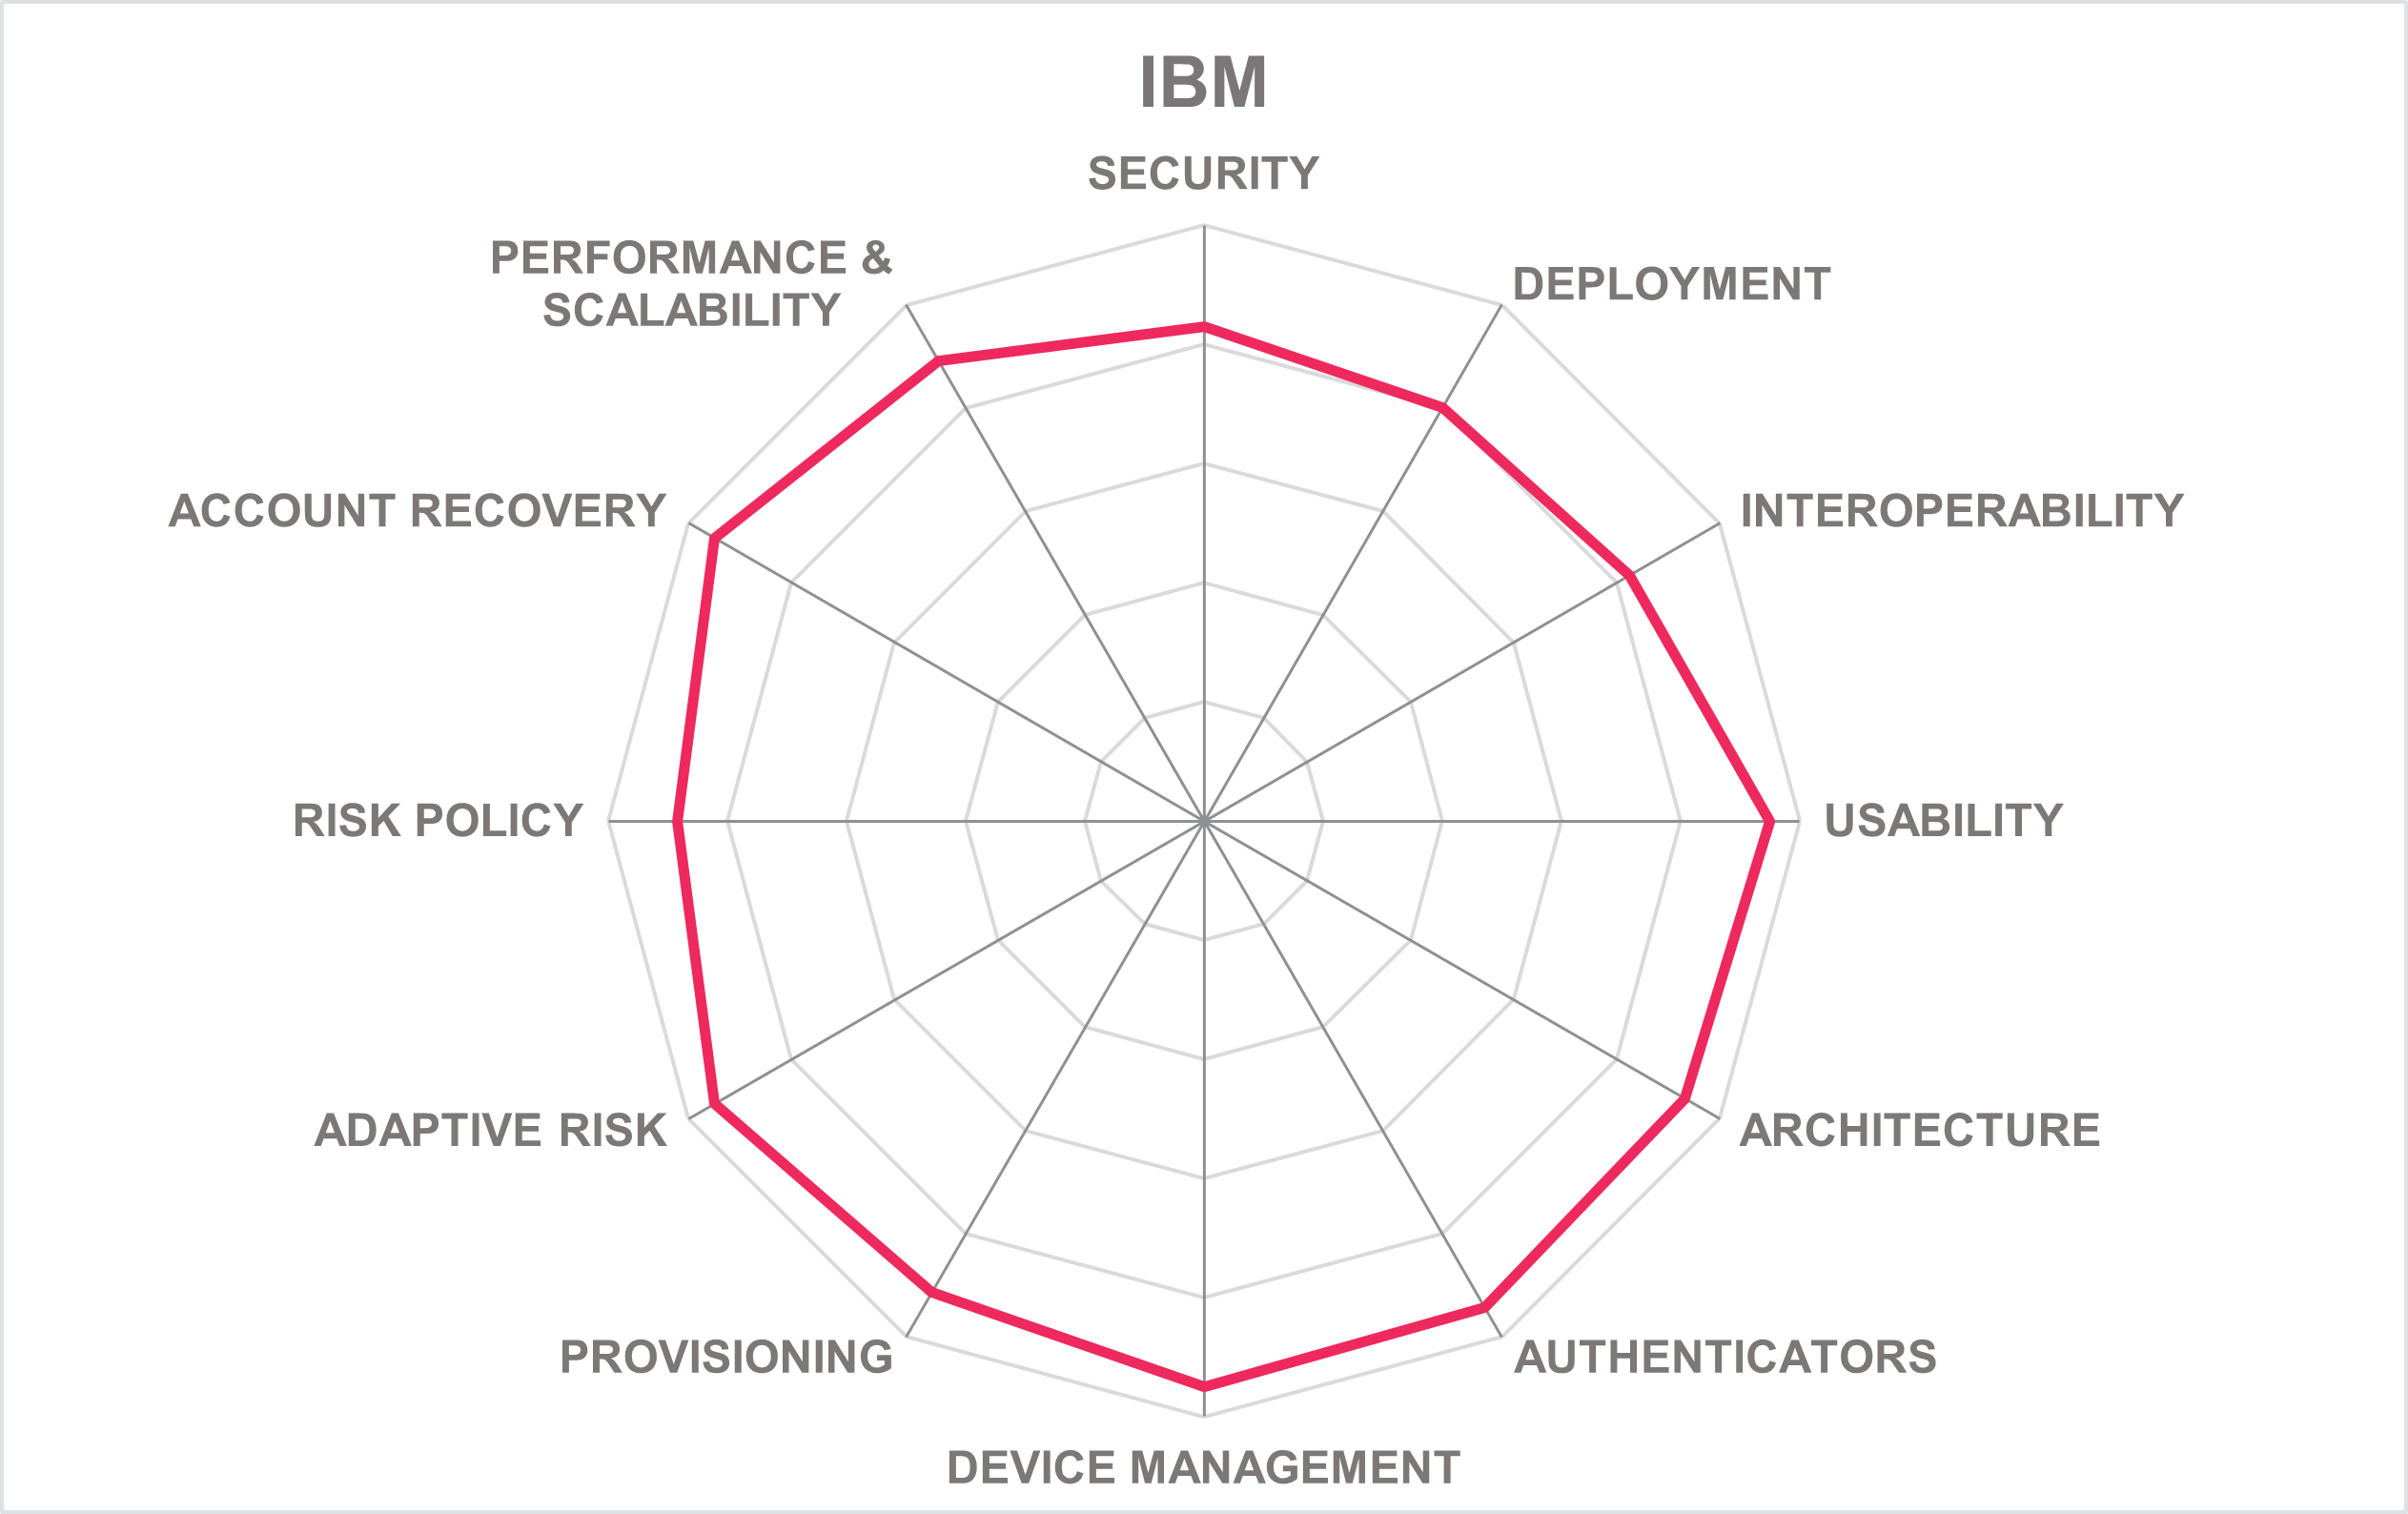
| Leader in | | | | |
International Business Machines Corporation (IBM) was founded in 1911, and has its headquarters in Armonk, New York, in the US. IBM Verify is IBM’s cloud-based identity platform (Identity-as-a-Service) that delivers SSO, MFA, passwordless authentication, lifecycle management, and CIAM. It integrates with IBM Verify Adaptive Access/IBM Verify Trust, which add AI-driven risk-based and adaptive access controls, powered by IBM Trusteer analytics.
IBM Verify implements passwordless authentication using FIDO2/WebAuthn. It acts as a FIDO2 server and supports both platforms (such as Windows Hello and Touch ID) and roaming authenticators (such as YubiKeys and NFC/BLE keys). However, IBM Verify is not listed as a FIDO Certified Server. IBM Verify supports reauthenticating known users with either MFA or passwordless experiences such as social login and contextual access. IBM Verify Mobile App extends passwordless login to mobile devices, using QR code pairing and push notifications to confirm user intent.
Users can register devices via a self-service portal, and developers can embed WebAuthn flows using IBM’s APIs. Users can register, manage, and revoke their devices in self-service mode, while administrators can view and manage registered authenticators for compliance purposes. Policies define which authentication methods (including Passkeys, Tokens, and Verify App) are available. IBM Verify supports device posture assessments, including checks for OS patch levels and the presence and version of anti-malware software.
IBM Verify also supports SCIM-based provisioning and deprovisioning for automated lifecycle management. Organizations can use out-of-the-box connectors for SaaS applications such as Microsoft 365, Salesforce, and Box, or develop custom integrations via the SCIM base URL. This API-driven model supports large-scale CIAM implementations, enabling user onboarding and attribute synchronization.
IBM Verify Adaptive Access continuously evaluates risk using contextual signals from the user, device, and network. Powered by IBM Security Trusteer, it analyzes behavioral biometrics, geo-location, IP reputation, and device fingerprinting to produce dynamic risk scores. These risk insights trigger adaptive authentication, enforcing step-up verification or policy-based restrictions as needed.
Administrators can create and manage adaptive risk policies through a visual policy editor in IBM Verify. Policies define risk thresholds, authentication strength, and conditions for step-up verification. The risk analysis engine is API-addressable, facilitating integration with external systems. The platform also interoperates with third-party services to widen the scope. Policies can be applied across consumer applications via SSO integrations (OIDC/SAML), ensuring consistent risk enforcement across digital channels.
IBM Verify provides passwordless account recovery options including username/password fallback, security questions, email OTP or link, phone OTP, SMS OTP, and mobile push notifications. It provides CIAM, FIDO2, and adaptive building blocks that customers orchestrate to create a complete B2C recovery experience. These flows can be customized through IBM Verify's configuration settings, allowing organizations to configure recovery methods based on their requirements. Users can re-enroll authenticators or use push-based re-verification if access to their primary device is lost.
As a SaaS-based solution, IBM Verify delivers high availability and scalability through distributed infrastructure. Its use of FIDO2/WebAuthn ensures cryptographic operations are performed on-device, minimizing server-side latency.
IBM is positioned as both a product and innovation leader in this report. This is based on the breadth of functionality provided by the solution and the investment that IBM has made in technical innovations over an extended period. The solution also forms part of a wider integrated CIAM solution.
IBM Verify is likely to be attractive to large enterprises, especially in regulated sectors like finance, healthcare, and government. The platform's compliance alignment, scalability, and integration capabilities are important for organizations needing to adhere to regulatory requirements. With a strong presence across North America, EMEA, APAC, and LATAM, IBM solutions meet the needs of global markets.
| Strengths |
|
| Challenges |
|
ITSME – Passwordless Authentication
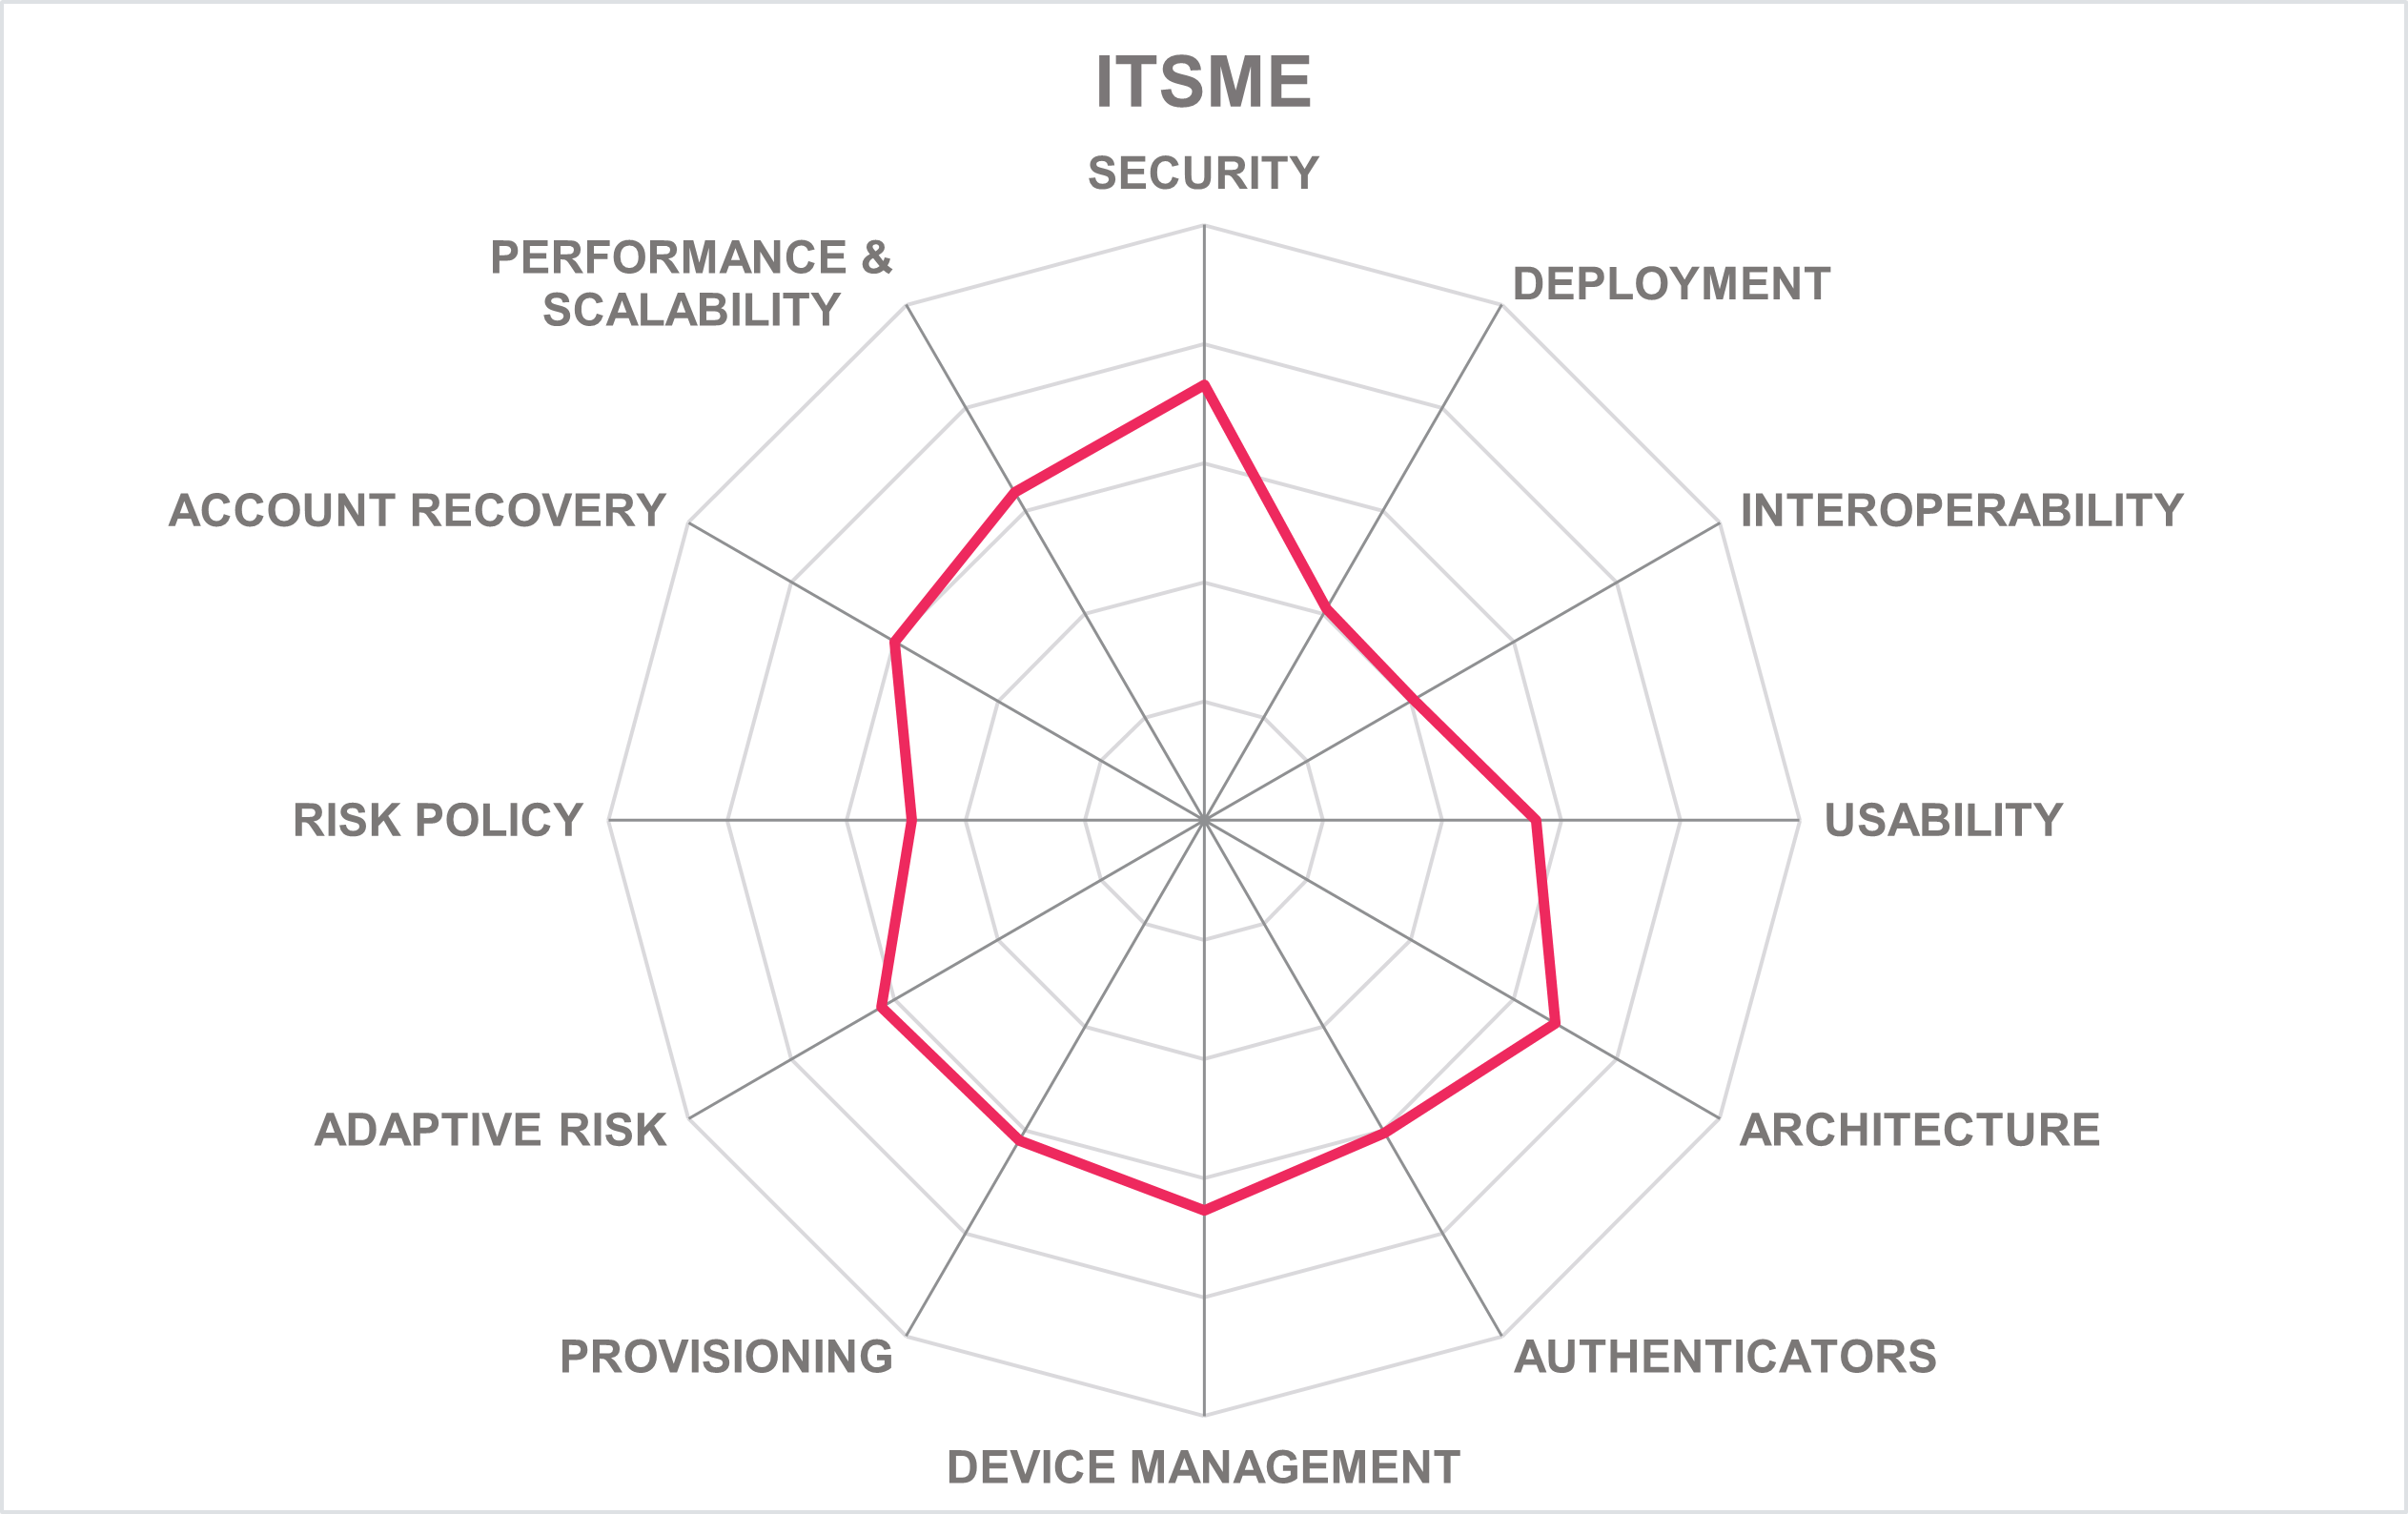
Itsme is operated by Belgian Mobile ID, a consortium of Belgium’s major banks and mobile operators. Founded in 2017 and headquartered in Brussels, Belgium, the itsme app provides secure, passwordless digital identity and authentication services used across banking, insurance, and other private sector applications (telco, utilities, gaming & gambling, postal services and government services). It enables login, confirmation, and Qualified Electronic Signature (QES) under eIDAS regulations, ensuring compliance with EU standards for high-assurance digital identity.
Itsme primarily employs biometric authentication methods through native platform features such as Android fingerprint and facial recognition, and iOS Face ID and Touch ID. During enrollment itsme uses strong biometric authentication through iProov and Keyless. Authentication combines possession (smartphone), a verified identity document, knowledge (itsme code), and biometrics (Face ID/Fingerprint) for secure, phishing-resistant login. Itsme does not support FIDO standards (U2F, UAF, and FIDO2) directly. The service integrates via OAuth 2.0, and OIDC or SAML 2.0, supporting standard authorization code flows for both web and mobile applications. It also supports transaction signing/confirmation, identity verification and data and document exchange. Itsme can be used cross-organizationally - meaning across merchants.
Each itsme account is bound to a single mobile device, combining SIM-based verification, proximity verification through QR code, and hardware security to protect the user’s identity. Users manage their devices directly via the itsme app, which offers functionality to block access if a device is lost or stolen and reactivate the account securely on a new device. The app automatically detects rooted or jailbroken devices and prevents activation to maintain device integrity and trust.
Itsme enables organizations to onboard users through federation with the itsme Identity Provider using OIDC. It provides fast, compliant onboarding through banking or eID verification, allowing users to activate their account via their financial institution or government-issued eID. Integration partners extend onboarding options through REST APIs and redirect-based flows for seamless CIAM deployment.
Itsme evaluates several adaptive risk factors, including IP address, device ID, and time/date anomalies. Additionally, device fingerprinting and software signature are supported that check device integrity and user trustworthiness. User transaction history is maintained for ten years, aiding in anomaly detection tied to user behavior over time. The solution does not support integration with fraud intelligence platforms.
Itsme does not currently support complex risk policy authoring methods or utilize a scoring system for weighted risk analysis in decision-making. Risk and access policies are primarily defined by the relying parties through OIDC scopes, claims, and the trust framework mandated by Belgian Mobile ID. Organizations can apply step-up authentication for high-risk transactions, such as financial approvals or document signing, using itsme’s transaction confirmation feature.
Users can block their itsme account directly from the app or website if the device is lost or compromised. Recovery requires reactivation on a new device through strong identity verification using a biometric and either an eID card with NFC, eID card reader or a bank-based re-identification flow.
itsme operates as a national-scale identity platform, serving over 7 million users in Belgium. It complies with eIDAS Level of Assurance (LoA) High and QES requirements, providing a cloud-based infrastructure with high availability. Itsme takes a unique approach in identification by combining eIDAS high LoA, identity doc binding & strong security with UX, re-usability, and geographical market penetration.
Itsme is a challenger in both product and innovation leadership. This is based on its limited functionality, which is targeted at a niche geographical market. Through the company's strategic involvement in the EUDIW pilot Itsme positions itself as an intermediary for Merchants to accept and connect to country wallets mandated under the EUDIW scheme. . However, the platform could enhance its competitiveness by integrating more diverse use cases and expanding its applicability across broader enterprise solutions and additional European markets.
Itsme is best suited regulated (finance, telco, insurance, utilities, gaming & gambling, postal services and government) operating within the Benelux region, where high-assurance identity verification and regulatory compliance are important. Its strong alignment with GDPR and eIDAS standards makes it an attractive choice for entities with rigorous data protection and digital sovereignty requirements.
| Strengths |
|
| Challenges |
|
Keyless – Keyless Zero-Knowledge Biometrics™
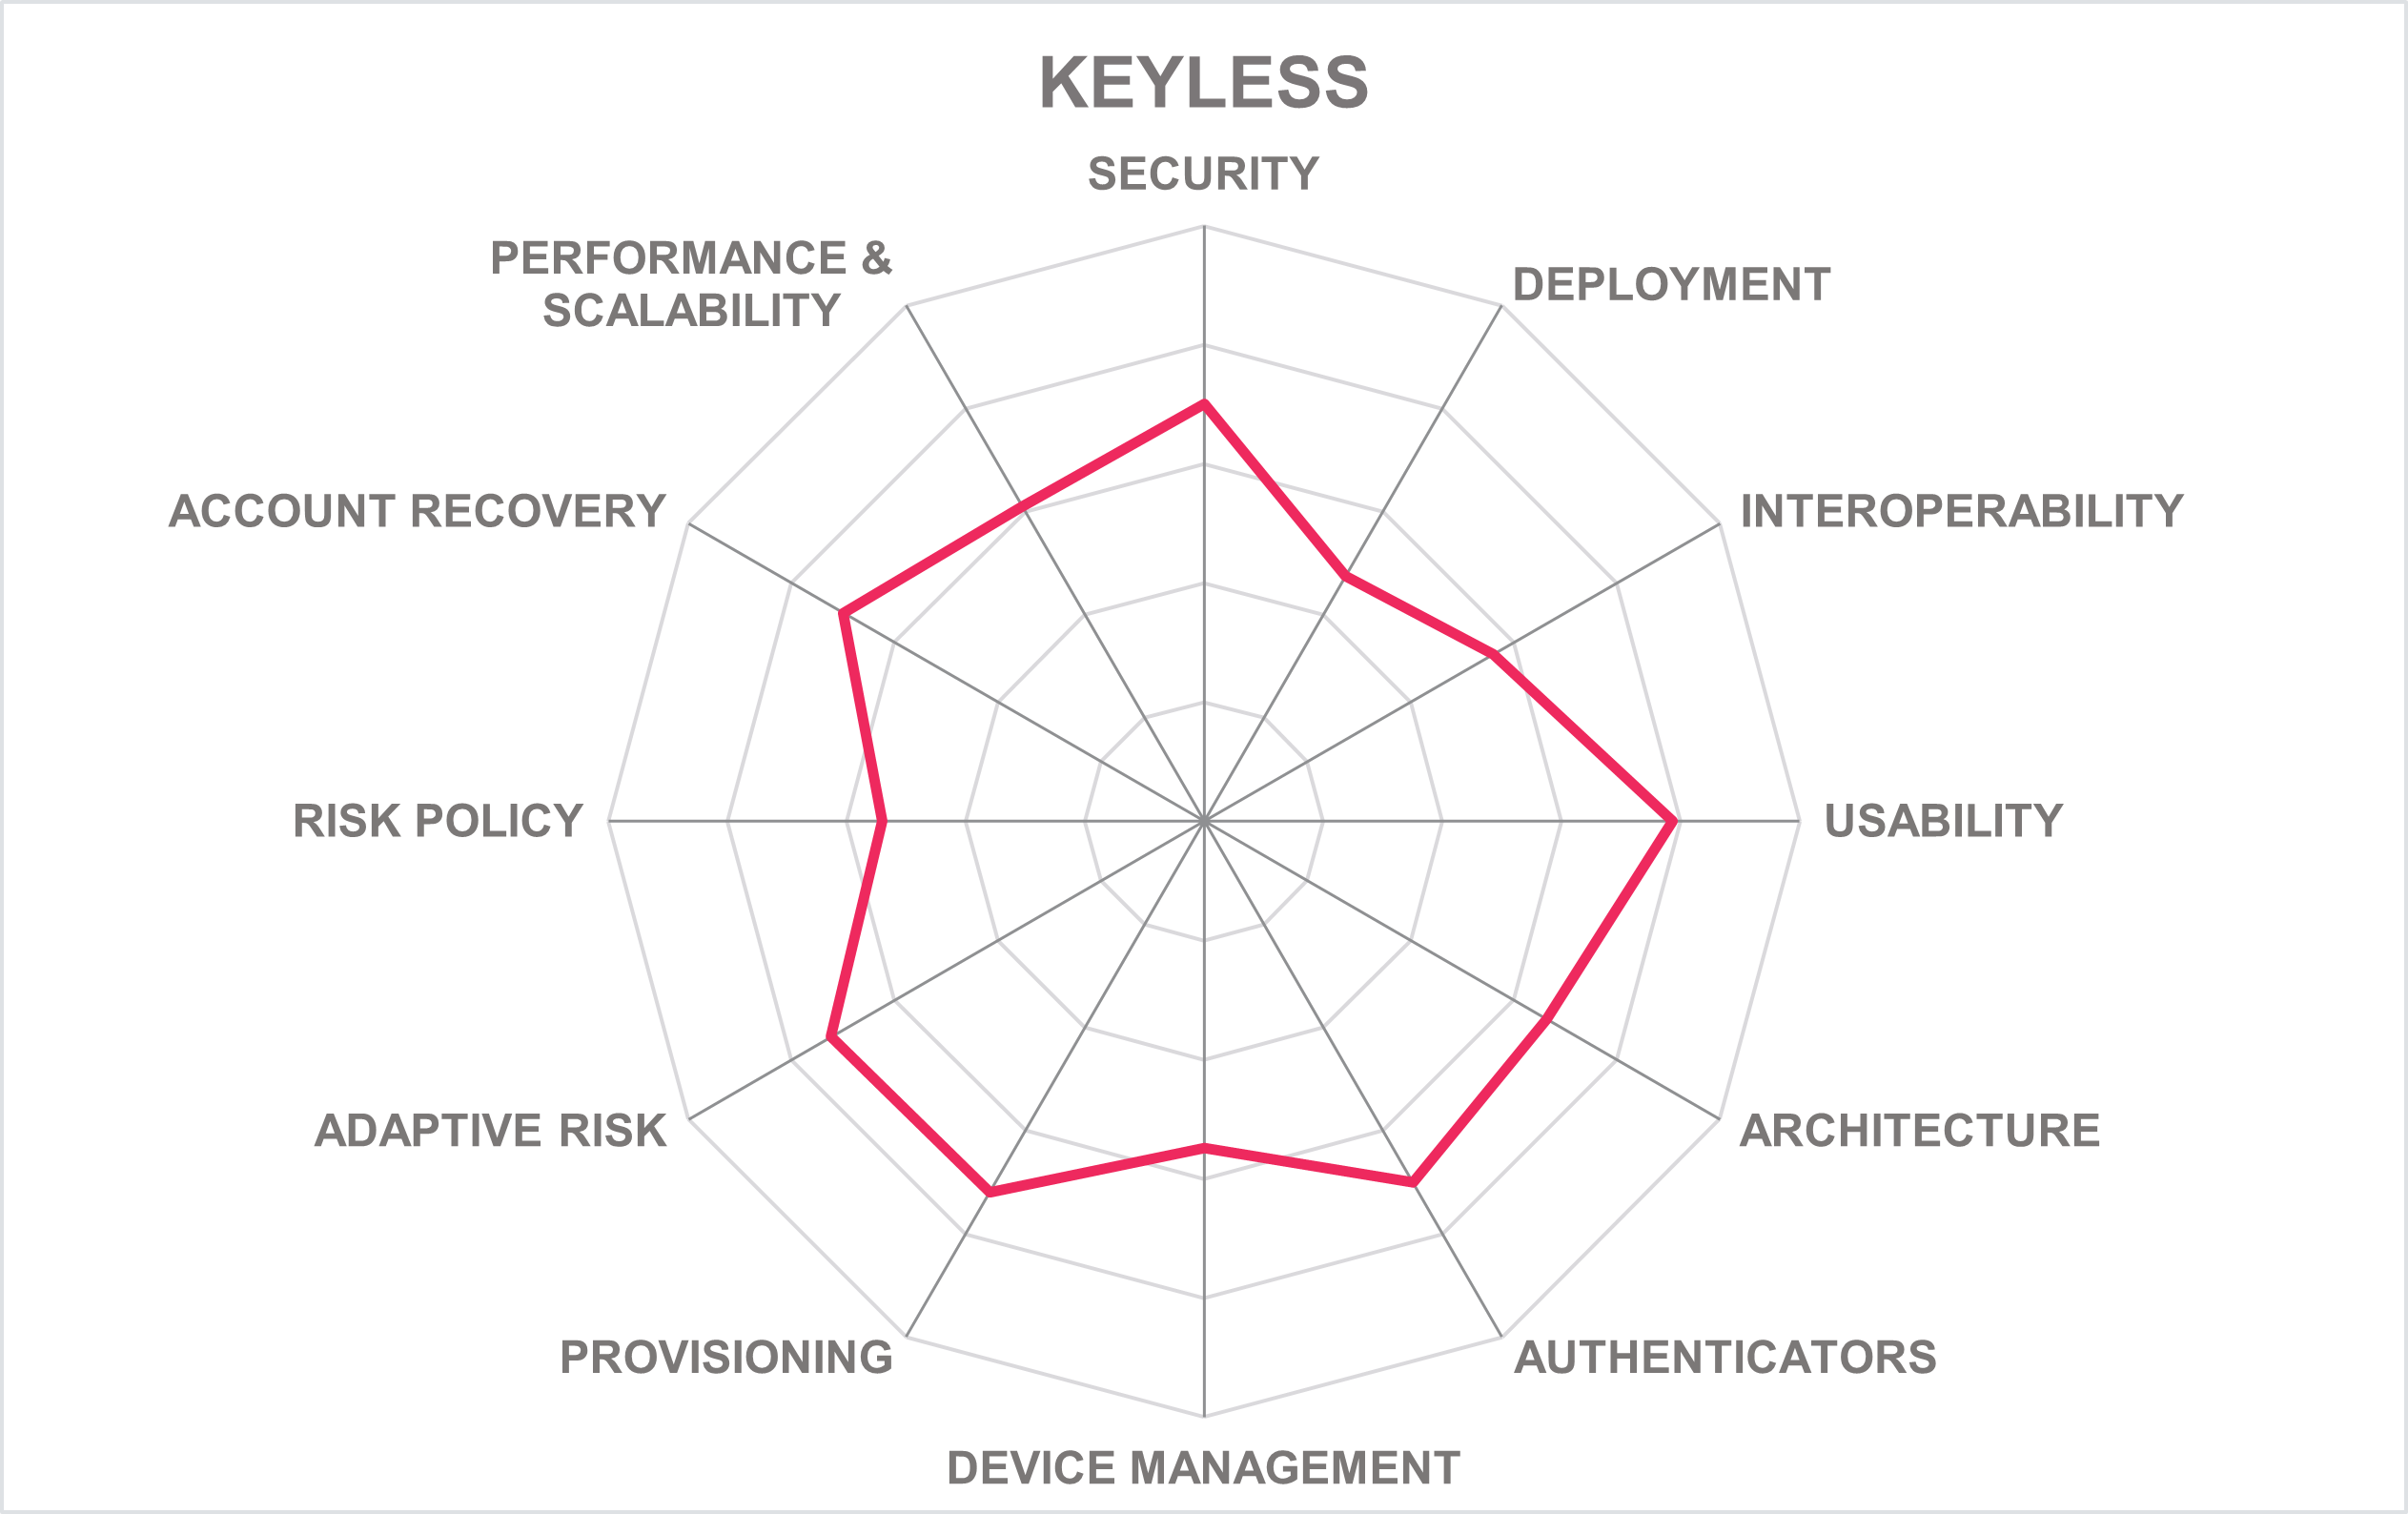
Keyless was founded in 2019 with headquarters in London, UK. In October 2025 Keyless signed a definitive agreement to be acquired by Ping Identity, subject to customary closing conditions and regulatory approvals.
Keyless provides a biometric passwordless authentication platform based on its patented Zero‑Knowledge Biometrics (ZKB) technology. ZKB is a privacy-preserving technology that enables single-glance multi-factor authentication without storing biometric data either on a device or a centralized server. Keyless is available via mobile and Web SDK and also offers on-premises and private cloud deployment options.
Keyless supports passwordless authentication through ZKB, where facial biometrics are captured and transformed on‑device into a cryptographic representation via secure multi‑party computation (sMPC), then matched on the cloud to the template taken during enrollment. Neither Keyless nor the cloud service provider ever sees or stores the user’s original biometric data, differentiating it from centralized biometric systems.
Keyless also differs from device-bound passkey solutions such as passkeys or FaceID. Authentication is not tied to the device; instead, users can authenticate on any device with a front-facing camera – be it a mobile phone, wall-mounted tablet, or desktop. Device-bound solutions can be bypassed with knowledge of the PIN, which is a security concern and makes them single-factor. The Keyless core solution is multi-factor by design, as both face and device are matched against those used to enroll.
Before authenticating with Keyless, users first enroll their face and device, which are then used as the root of trust for future authentications. This is supported through the mobile or web SDK. Keyless does not offer device posture checks, such as assessments of OS patch levels, or device compliance.
While Keyless itself is not an identity verification provider, the Keyless core solution integrates with all major IDV providers to provide continuous trust from onboarding through to authentication. Keyless has a unique technology, the IDV Bridge, which silently enrolls any new users into Keyless during the IDV/KYC check – with existing users bulk-enrolled in the backend
The platform integrates with CIAM platforms including Ping Identity, Azure AD B2C, and Okta/Auth0 to support onboarding and federated user management. While Keyless offers user self-registration, they do not support bulk provisioning from LDAP or SCIM or specific cloud services through APIs.
The Keyless core solution includes spoof‑detection and deep‑fake resistance. While device fingerprinting and detailed posture checks are not included, it leverages certain behavioral signals to detect the presence of synthetic identities including masks and deepfakes.
Risk and authentication policies are typically orchestrated through external CIAM platforms or application‑level logic using Keyless APIs. The platform does not provide a graphical policy authoring tool or generate risk scores, limiting real-time risk analysis capabilities within their platform. However, they allow policy import via API for external orchestration, offering biometric and PIN alternatives for step-up authentication based on external risk evaluations.
Account recovery processes utilize biometric re-enrollment with one glance, typically replacing SMS OTP, call center, and re-KYC flows to recover accounts; it does not support methods like email or SMS OTP. Whenever the user needs to recover their account, their face is matched against the one taken during the identity verification step. It also allows for an additional PIN/Password to be used alongside their biometric solutions to aid in account recovery.
Keyless is a challenger in both product and innovation leadership in this report. While the product capabilities across the range evaluated are adequate, they are not leading. Its major strengths include advanced privacy technology and strong biometric liveness performance.
Keyless is likely to be attractive to industries demanding high-security authentication and rigorous privacy compliance, such as financial services, government, and healthcare sectors. Its privacy-related features make it an attractive choice for multinational corporations engaged in data-sensitive operations.
| Strengths |
|
| Challenges |
|
LoginRadius – CIAM Platform
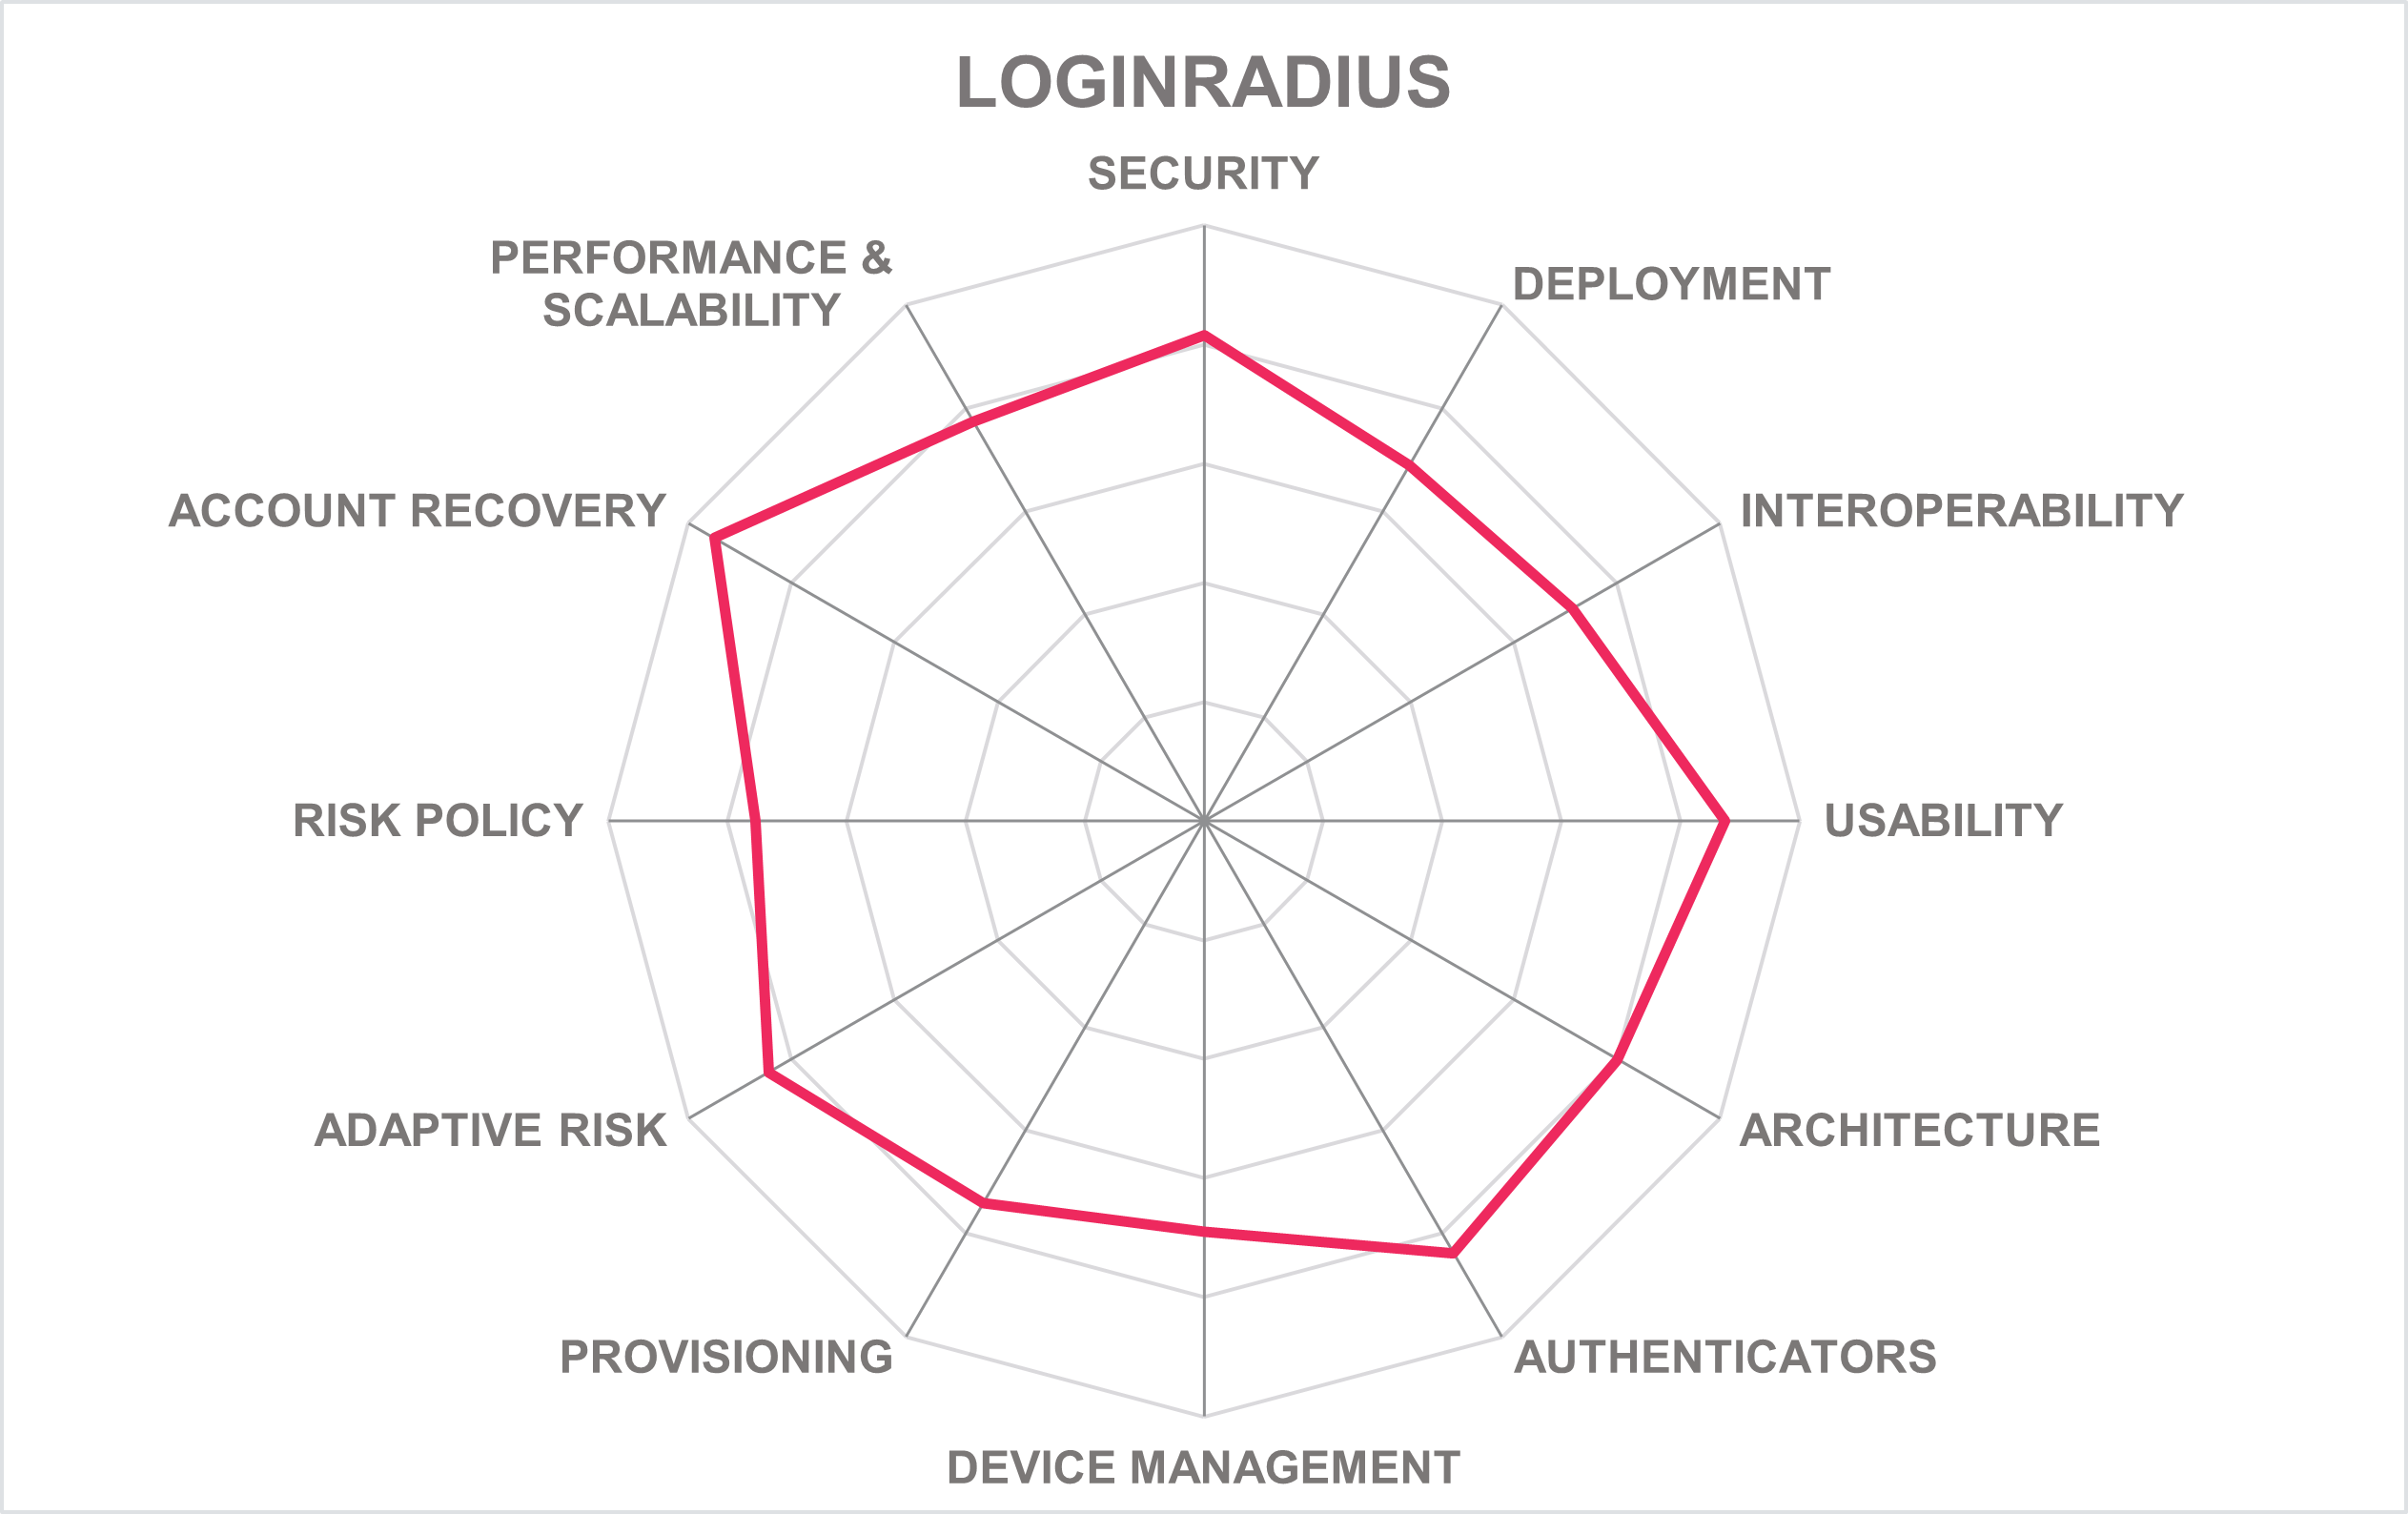
Founded in 2011 in Vancouver, British Columbia, Canada, and now headquartered in San Francisco, California, in the US, LoginRadius is a privately held CIAM provider serving global customers across a wide range of industry sectors. The platform is delivered primarily as SaaS through a multi-cloud architecture distributed across globally located datacenters.
The platform supports customer registration, authentication, profile and consent management, and full identity lifecycle operations. Its passwordless capabilities include passkeys, magic links, and email/SMS OTP, enabling organizations to deploy modern, frictionless consumer authentication flows.
LoginRadius supports multiple passwordless authentication methods including passkeys, mobile-based verification through SMS, push notifications, and vendor-specific apps. Biometric authentication is available using native capabilities on Android and iOS platforms. The platform is compatible with major FIDO standards (FIDO2 and WebAuthn) and supports a range of hardware security keys (including Yubico YubiKey, Feitian Security Key, and Google Titan). However, LoginRadius is not listed as a FIDO Certified Server in the public FIDO Alliance directory. These options can be enabled via the CIAM console or APIs. It also provides secure mobile SDKs, enabling transaction signing.
The platform supports a wide range of devices, including mobile (iOS/Android), desktops, laptops, tablets, IoT devices, and Smart TVs or embedded systems. However, it does not provide capabilities for device posture checks like OS version compliance or malware detection.
LoginRadius CIAM platform enables users to create their own accounts through customizable registration flows, supporting both traditional methods (email/password) as well as others, including social login and phone number-based registration. Organizations can develop and implement device registration flows tailored to their specific needs using REST APIs.
It supports risk-based authentication using contextual signals such as device attributes and user behavior patterns. It assesses a broad range of risk factors including IP reputation, geo-location, geo-velocity (impossible travel detection), and device identifiers. It supports device fingerprinting to evaluate trustworthiness and track historical user behavior. The platform integrates fraud intelligence by evaluating device reputation and adaptations to real-time contextual risk using risk-based access control methods.
LoginRadius supports device fingerprinting as part of its risk-based authentication capabilities. The platform automatically manages trusted devices and flags unrecognized or suspicious device usage by analyzing attributes such as browser, OS, and device metadata. Additionally, Custom Objects provide granular control by allowing organizations to store and manage device fingerprints and statuses directly within the platform for advanced device tracking and policy enforcement.
LoginRadius CIAM Platform provides a browser-based GUI for authoring risk policies. This supports methods like flowchart-based models to define flows. Risk evaluation produces risk but does not support weighting of risk factors. The platform's risk analysis engine is API-addressable, enabling integration with third-party authorization services to include further risk factors. Policies can enforce step-up authentication based on risk thresholds.
The LoginRadius platform supports multiple account recovery methods. These cover a range of secure recovery channels such as username/password fallback, OTPs via email or phone, SMS verification, mobile push notifications, and social login-based recovery. Account linking and help desk-assisted recovery are also supported.
To ensure scalability and performance, the platform is built using an architecture based on microservices, Kubernetes, and multi-layered auto-scaling to accommodate spikes in user demand or growth.
LoginRadius is positioned as a challenger in both product and innovation leadership in this report. While it offers a market leading CIAM, its passwordless capabilities are good but not exceptional.
LoginRadius is well suited to industries that require data protection and privacy compliance, such as financial services, healthcare, and retail. Its global reach, supported by multiple data centers in regions like North America, Europe, and APAC
| Strengths |
|
| Challenges |
|
Microsoft – Microsoft Entra
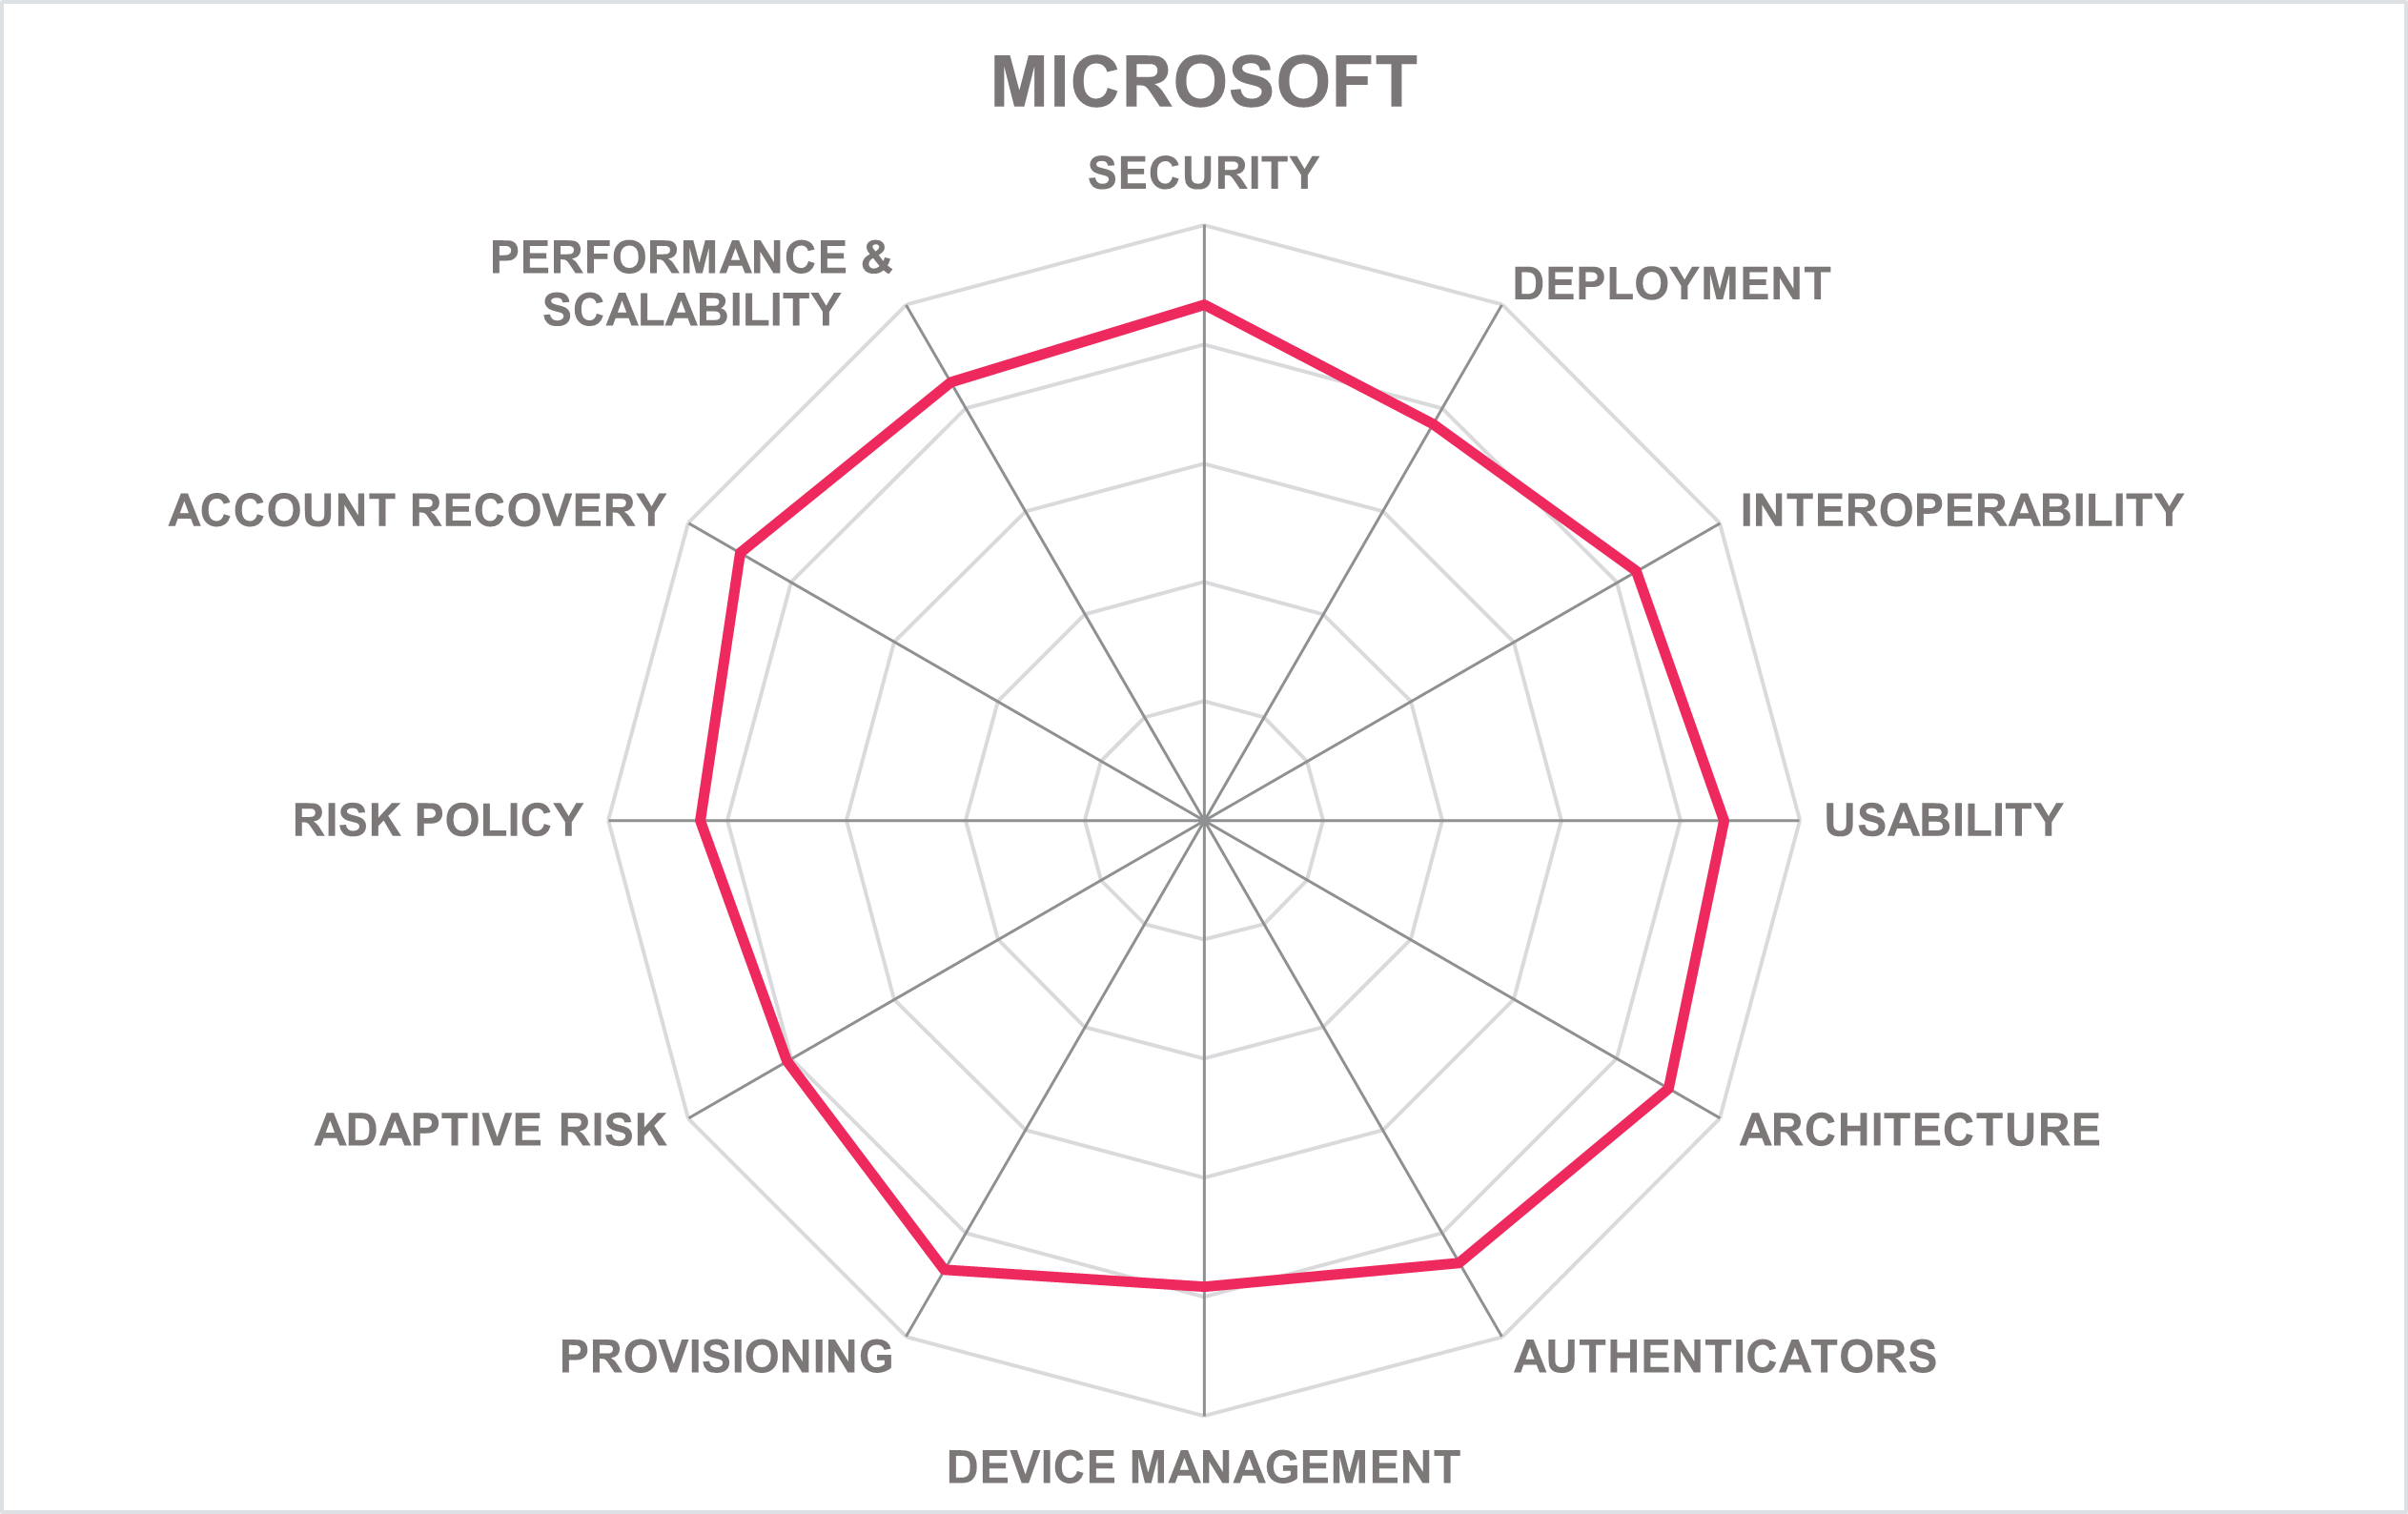
| Leader in | | | | |
Microsoft Corporation, founded in 1975 and with headquarters in Redmond, Washington, in the US, is a global provider of software, cloud infrastructure, and identity services. Microsoft Entra provides a CIAM platform for consumer-facing authentication, supporting large-scale registration, branded sign-in experiences, passwordless authentication, and identity lifecycle management. The platform integrates tightly with Microsoft’s broader identity ecosystem, including Conditional Access, Identity Protection, and Graph APIs.
Microsoft Entra supports a variety of passwordless authentication methods. The solution is FIDO-certified, supporting the FIDO2 standards for secure passwordless authentication, supporting hardware security keys like YubiKey, Google Titan, and others, through browser or platform authenticators. Microsoft operates a FIDO2 Certified Server for the underlying identity infrastructure. The authentication framework also supports enterprise protocols such as SAML, OAuth 2.0, and OIDC, providing interoperability with existing identity infrastructures. Entra offers secure mobile SDKs for administrative functions and supports transaction signing for high-trust operations.
The platform device management capabilities support a wide range of devices, including desktops, mobile phones, and FIDO2 external keys. The solution includes device health checks leveraging Conditional Access. However, OS integrity, jailbreak or root detection are not built-in capabilities for Entra External ID passwordless flows.
Entra supports self-service registration, custom attributes, consent capture, social providers, and customizable user flows. It provides APIs and Microsoft Graph integrations to manage large-scale user provisioning and lifecycle operations. It also supports bulk provisioning through LDAP and SCIM.
The platform supports risk-based authentication through Entra Identity Protection and Conditional Access. It evaluates risk factors such as IP reputation, geo-location, geo-velocity, and device identification. The solution employs proprietary device fingerprinting and software signatures to assess device trustworthiness and detect anomalies. External ID does not include native behavioral biometrics or fraud analytics, but risk signals from Entra ID Protection deliver baseline adaptive authentication. It can also integrate external fraud intelligence sources. It enables dynamic adjustment of authentication requirements based on real-time contextual risk evaluations.
Administrators can configure Conditional Access policies to enforce passwordless MFA, or additional verification based on user, device, risk level, or location. Policies can be created through the Entra Admin Center or Microsoft Graph and imported as JSON. It includes a weighted risk factor evaluation mechanism producing granular risk scores, and it can be integrated with external services via APIs for broader security evaluation. The policy framework supports the orchestration of actions like conditional access or step-up verification based on different risk thresholds, as well as through integration capabilities with third-party services.
Microsoft Entra supports account recovery through alternative sign-in methods, email-based verification, and multifactor recovery paths. User flows can be customized for recovery operations. Recovery codes facilitate secure fallback options in scenarios of device loss or second factor failure. It also supports help desk assisted recovery.
The platform runs on Microsoft Azure’s global cloud infrastructure, offering high availability, global distribution, and elasticity for consumer-scale authentication workloads. The platform demonstrates resilience with latency times ranging from 1-2 seconds and guarantees high availability with a 99.99% monthly uptime in its SLA.
Microsoft is positioned as both a product leader and an innovation leader in this report. This is based on the breadth of functionality provided by the solution and the investment that Microsoft has made in technical innovations in the identity space over an extended period.
Microsoft Entra passwordless is best suited to organizations that run high-volume, consumer-facing apps where phishing resistance, scale, and multi-channel UX matters.
| Strengths |
|
| Challenges |
|
Nevis – Nevis Identity Suite, Nevis ID & Authentication Cloud
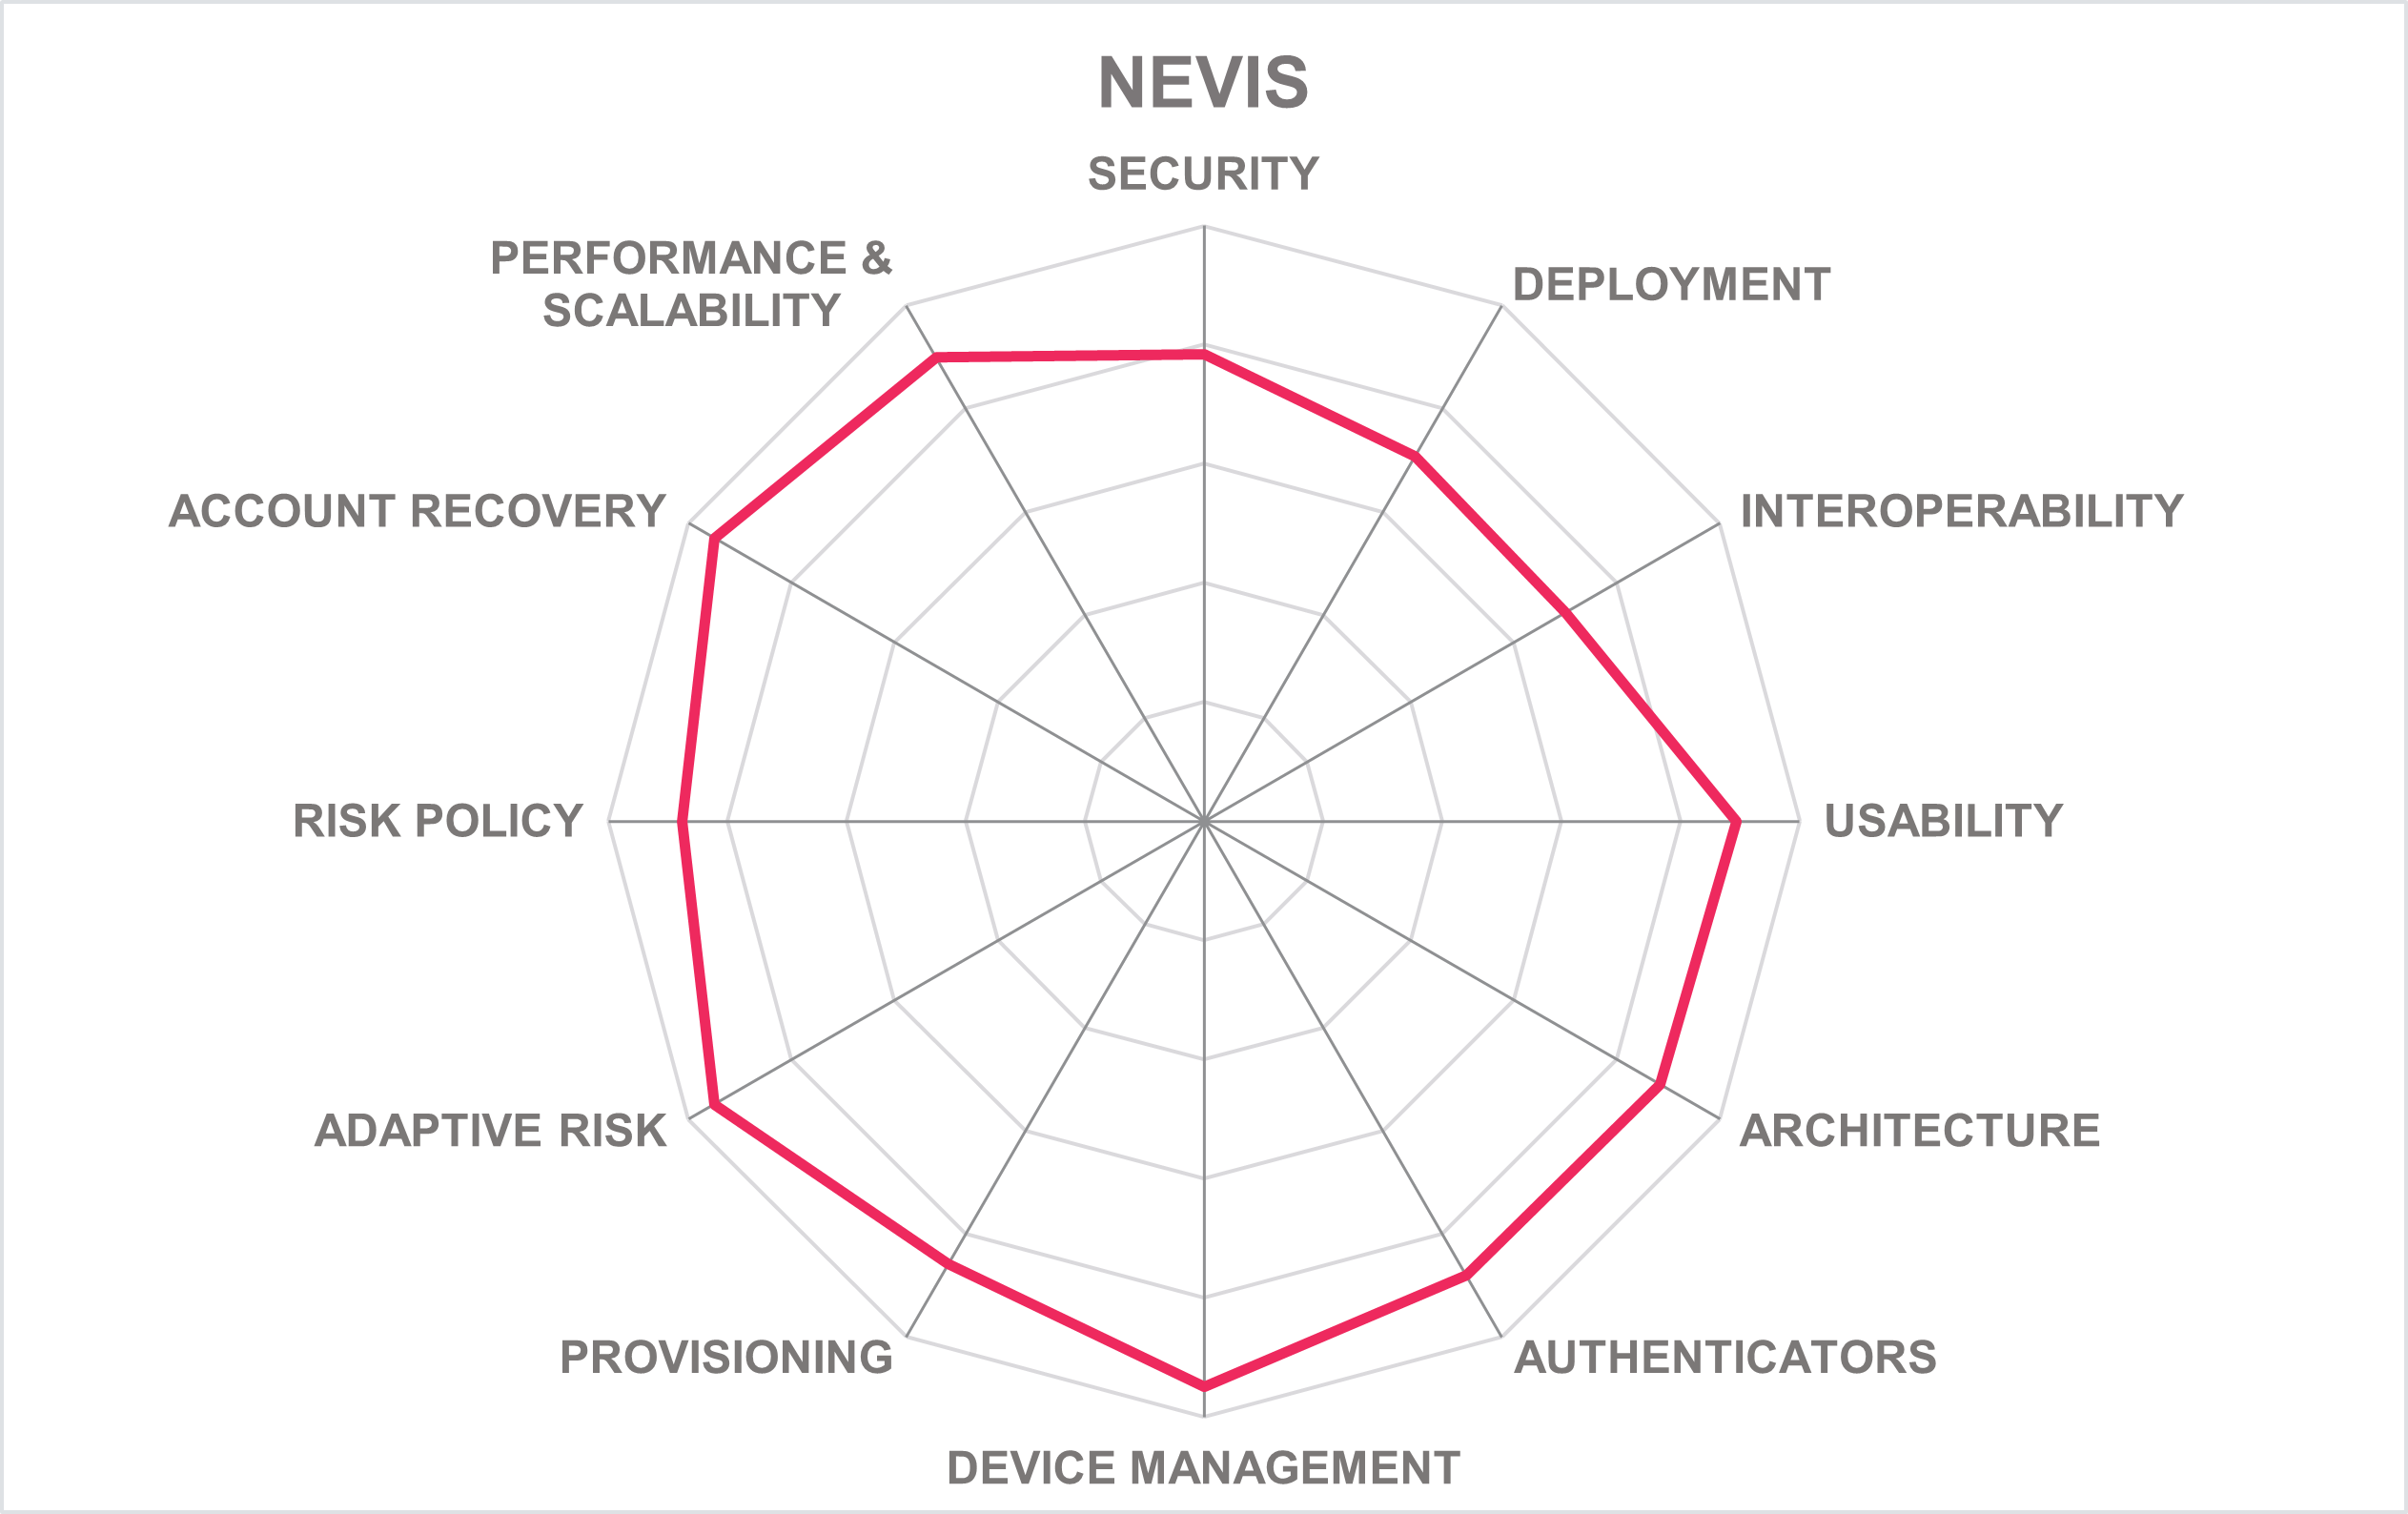
| Leader in | | | | |
Nevis, a privately held company owned by IHAG Holdings and headquartered in Zurich, Switzerland, specializes in CIAM solutions. It was founded in 2020 as a spin off from Adnovum Informatik AG. Its customer base is primarily located in the EU, with a strong presence in the DACH region, and additional deployments in the US and Singapore. Their target customers are in the finance, health care, energy, manufacturing, gaming, and government sectors.
Nevis offers three products related to CIAM: Nevis ID Platform is a SaaS CIAM platform for customer identities, registration, authentication, profile & consent management. Nevis Identity Suite deployed on premises is a CIAM/IDM/AM with support for FIDO, OAuth 2.0, OIDC, SAML 2.0 and mobile. Nevis Authentication Cloud is a fully managed passwordless authentication and transaction signing as a service, marketed explicitly for customer authentication with biometric MFA and FIDO-based.
Nevis delivers passwordless customer authentication primarily via Nevis Authentication Cloud and Nevis ID / Identity Suite. This supports a range of authentication options, which include support for traditional credentials as well as passwordless methods such as passkeys, mobile-based verifications with SMS and push notifications, and a vendor-specific mobile app. For biometric authentication, it supports native capabilities on both Android and iOS through Face ID, Touch ID, and various platform-native biometric features. The solution is FIDO-certified with support for FIDO UAF and FIDO2 standards and is compatible with a variety of hardware security keys such as YubiKey and Google Titan. The solution also integrates with existing enterprise authentication protocols (SAML, OAuth 2.0, OIDC, and RADIUS).
With the FIDO UAF-based Access App or SDK it is possible to create cryptographically signed transaction confirmations, which follow FIDO's " What You See Is What You Sign (WYSIWYS) " and are compliant with PSD2 requirements such as SCA or dynamic linking.
The platform offers device management that covers smartphones, desktops, and IoT devices. This flexibility extends to multiple devices per user, with support for device trust that is managed across devices. Posture-check capability ensures that devices evaluate correctly for compliance with operational security posture, covering aspects such as OS versions and other security features like anti-malware protection. For instance, Apple App Attestation and Android Key Attestation are employed to validate the device's security.
The platform supports user self-registration, and the registration flow can be customized using the configuration tool. The solution supports the integration of identity proofing services, such as document-based identity verification with providers like PXL Vision or Jumio. It also supports bulk provisioning from LDAP and SCIM, as well as provisioning to or from other cloud services using APIs.
The platform supports adaptive authentication through its nevisAdapt and nevisDetect modules, which use device fingerprinting, behavioral signals, and contextual data to adjust authentication requirements based on risk. These include IP Address and Network, Geo-location and geo-velocity, and date and time anomalies. The system verifies the device software integrity using methods such as Apple App Attestation, Google Play Store Attestation, and Android Key. It also tracks user interactions and behaviors historically to detect deviations from normal patterns that could indicate potential security threats. Nevis integrates external fraud intelligence services to enhance its assessment capabilities. This includes feeds from IP 2 Location, MaxMind, and FireHOL, among others. It can also track compromised credentials through integrations with services like Have I Been Pwned.
It provides identity orchestration tools enabling no-code/low-code configuration of authentication workflows and conditional logic. Administrators can configure different authentication journeys based on user attributes, device context, or risk events. It supports risk policy authoring through GUI and file upload (XML and JSON) with weighted assignment of risk factors. Risk assessments yield the scores used to guide policy-driven actions like step-up authentication or conditional access.
The platform supports self-service account recovery and device switching, its mobile authentication SDK enables secure re-binding of new devices. Users can recover accounts using predefined security questions, OTPs-time passwords sent via email or SMS, Mobile Push Notifications, and through pre-associated trusted accounts, such as social or enterprise identities.
Nevis is positioned as a product leader in this report. This leadership is based on the strong capabilities that the solution offers across all the requirements for consumer passwordless authentication described above.
Nevis is best suited for financial services, insurance, government, and healthcare organizations that require both high security and compliance with data protection regulations such as GDPR. It is equally applicable for enterprises looking for a combined workforce and consumer IAM solution.
| Strengths |
|
| Challenges |
|
OKTA Inc. – OKTA and Auth0 Platforms
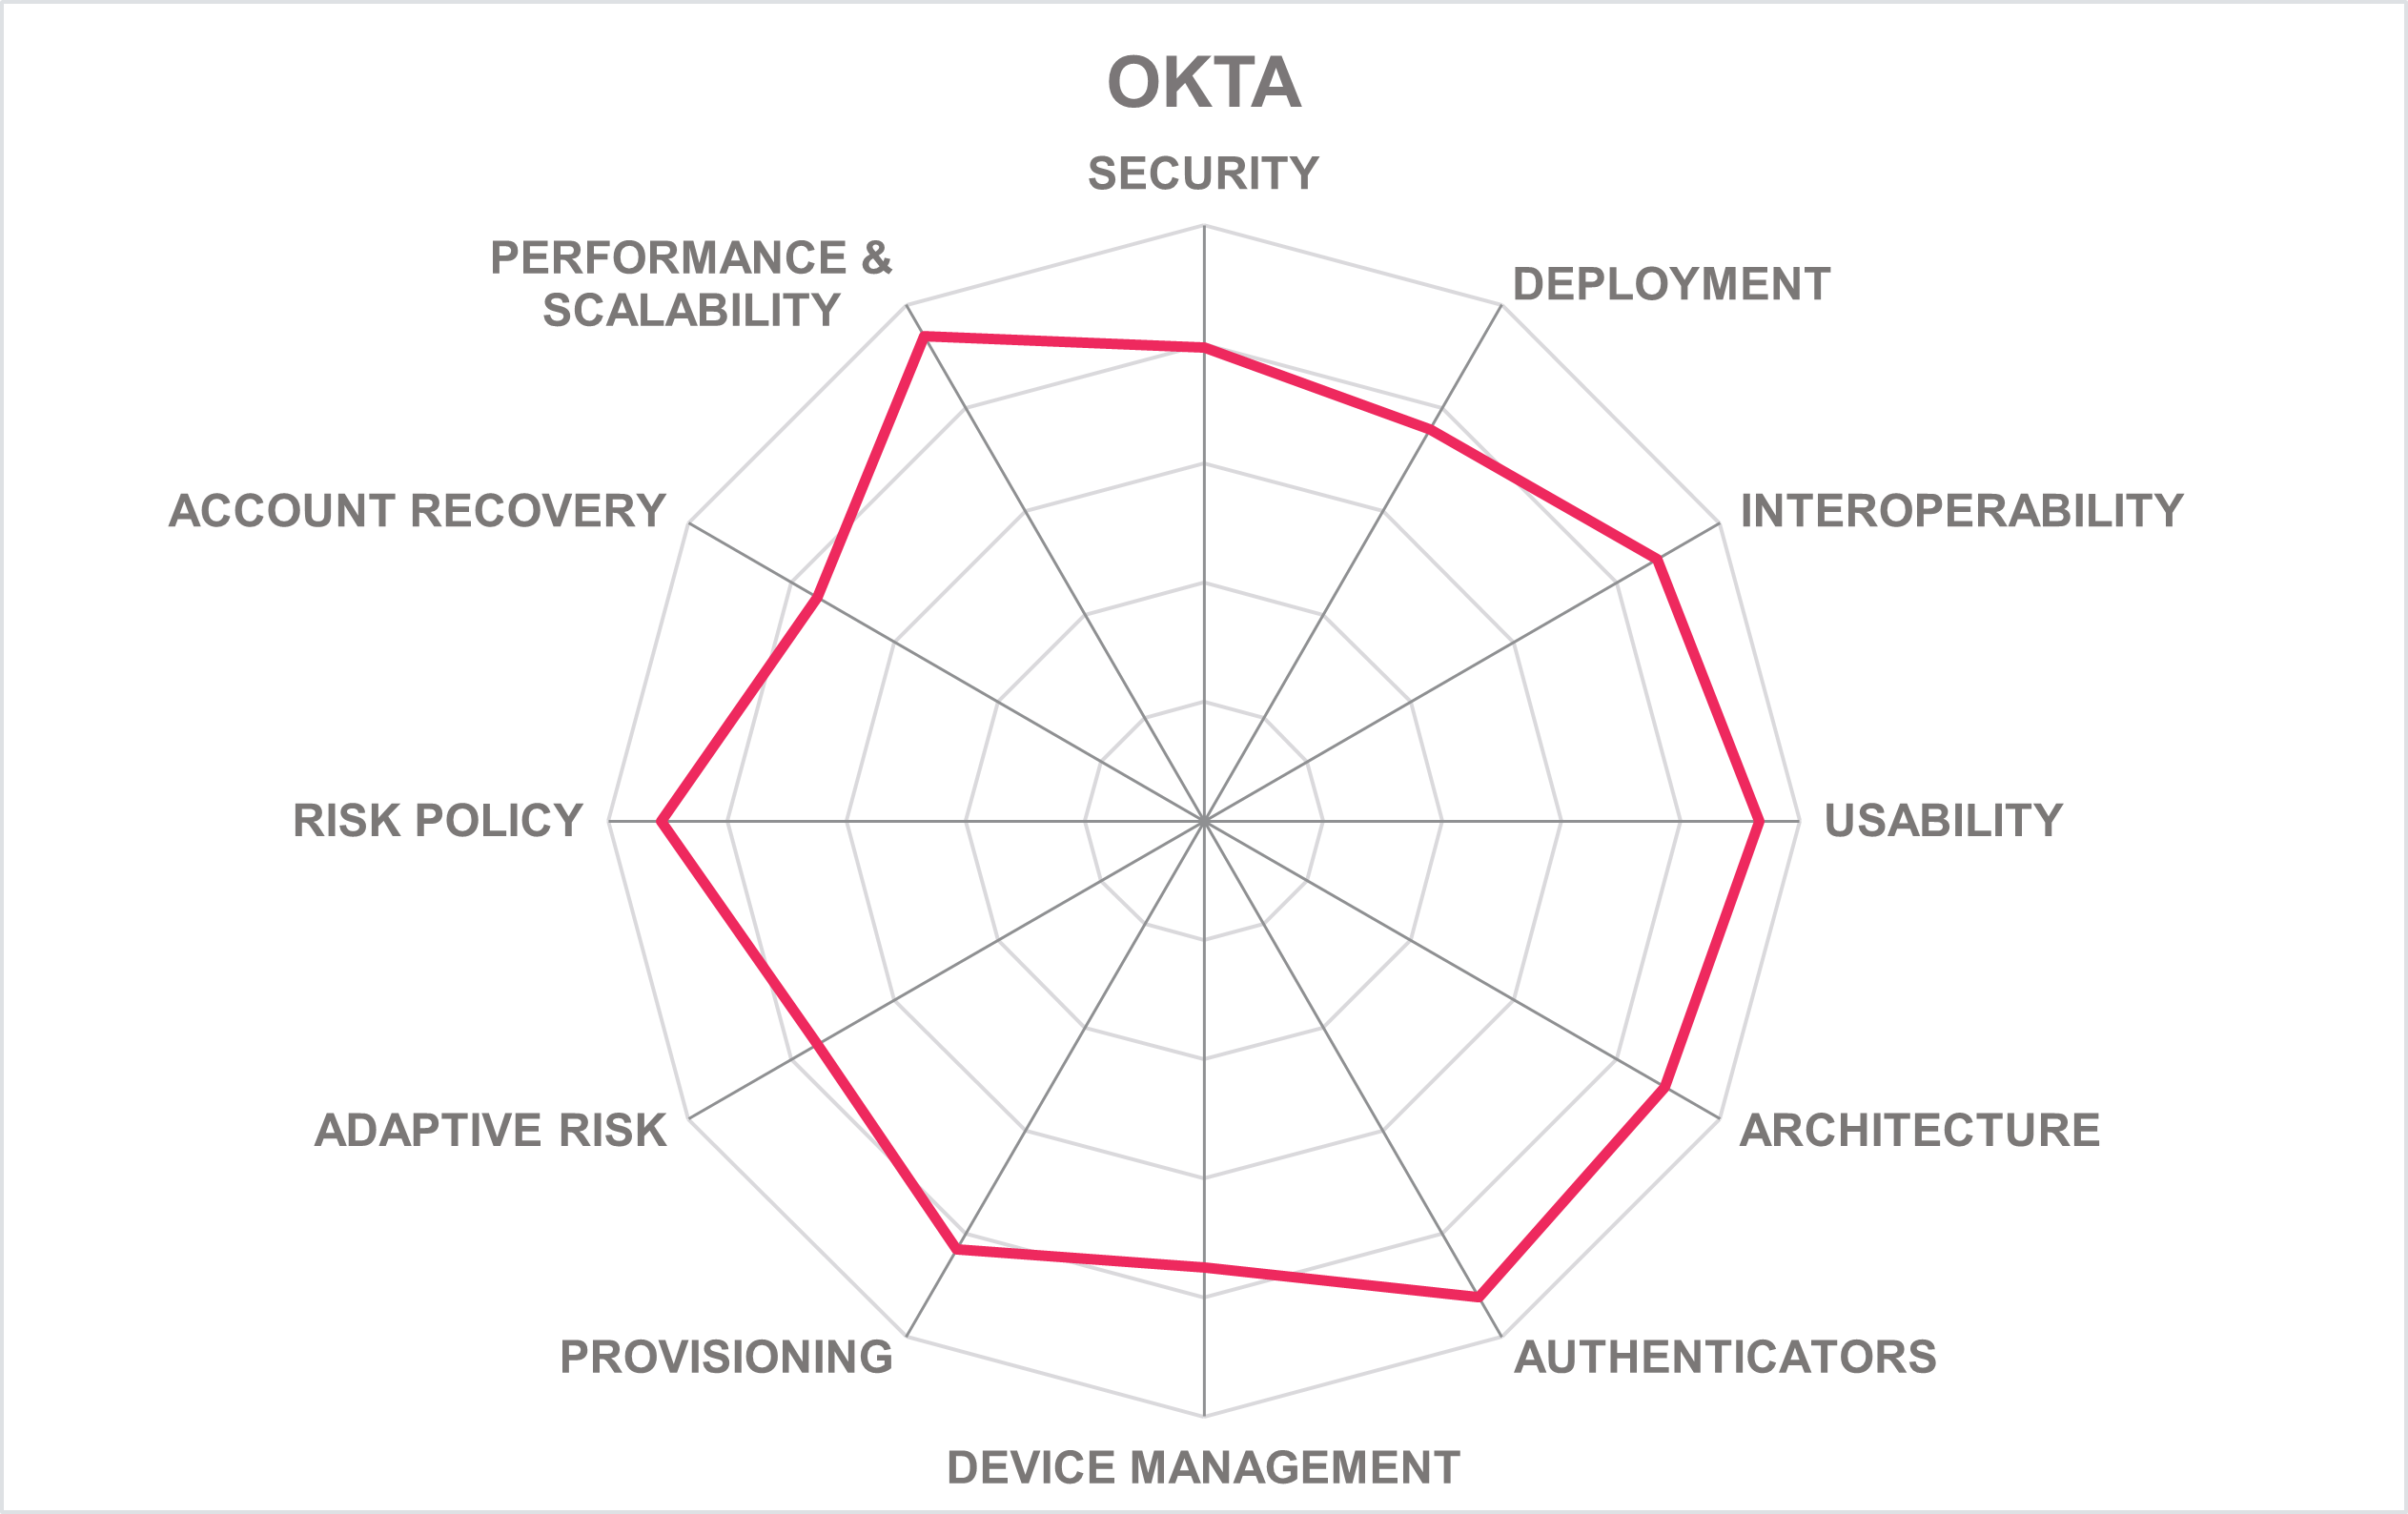
| Leader in | | | | |
Okta, founded in 2009 and headquartered in San Francisco, is a leading independent identity provider. In 2021, Okta acquired Auth0, a developer-focused CIAM platform, resulting in two complementary CIAM offerings: Okta Customer Identity (OCI) and Auth0. Both platforms support B2C identity use cases with passwordless authentication, identity orchestration, adaptive risk evaluation, and global-scale reliability. Both solutions are SaaS, hosted in public IaaS, and private cloud options as well.
For B2C passwordless authentication, Okta and Auth0 provide support for WebAuthn/FIDO2 passkeys, including platform authenticators such as Touch ID, Face ID, and Windows Hello. However, neither OCI nor Auth0 are certified as FIDO2 servers. Additional passwordless authentication options include social and custom social login, SMS OTP, Voice OTP, email OTP, and magic links. Okta Verify is available but is rarely adopted in B2C scenarios, and WebAuthn remains the primary method for consumer passwordless authentication for Okta Customer Identity.
Both OCI and Auth0 enable customers to secure applications on mobile and desktop devices, including iOS, iPadOS, Android, Windows, and macOS. In B2C, Okta Customer Identity and Auth0 support device management through authenticator registration rather than workforce-style device posture. Consumers register passkeys or WebAuthn authenticators, and Okta Customer Identity stores metadata such as the public key, device type, and credential ID. Auth0 similarly supports multi-device registration through WebAuthn. Okta Verify may be used as an optional mobile authenticator with QR-based binding but does not include enterprise device assurance. It does not support device posture such as root/jailbreak detection, OS integrity, hardware attestation.
Okta Customer Identity and Auth0 provide B2C onboarding features, including self-service registration, social login, progressive profiling, consent management, and customizable data schemas. Both platforms support API-driven identity lifecycle management and user profile enrichment with corresponding SDKs. Enterprise provisioning technologies such as SCIM are supported but play a secondary role in B2C consumer onboarding.
Okta Adaptive MFA provides consumer-relevant risk signals including IP reputation, anonymizer/VPN detection, geo-location anomalies, bot protection, and breached password checks. Auth0 adds anomaly detection capabilities such as brute-force protection and bot identification. Device assurance and endpoint checks are not available for B2C, but the available contextual signals support adaptive authentication decisions. Auth0 provides anomaly detection capabilities such as brute-force protection, bot detection, suspicious IP throttling, and breached password protection, and IP-based access control. Auth0 further secures user-accounts Adaptive MFA that only challenges the end-user when the authentication is deemed risky by analyzing trusted devices, impossible travel, and originating IP. Auth0 MFA options include Email/SMS/Voice OTP, platform and roaming WebAuthn, customizable Push notifications with rich authorization requests (RAR), TOTP, and Recovery Codes.
Both platforms provide flexible policy frameworks suitable for B2C identity flows. Administrators can define policies based on user attributes, geo-location, network conditions, and risk scores. Auth0’s Actions and Rules enable extensible, programmable policy logic. Additionally, Okta’s Workflows allow for extensible actions for a more flexible registration, onboarding, and authentication experience. Workforce-specific policy conditions such as device compliance are not applicable to B2C and are not exposed in consumer policies.
Okta Customer Identity and Auth0 support consumer-friendly account recovery mechanisms, including email verification, SMS recovery, reset links, WebAuthn credential re-registration, and recovery codes. Okta also provides temporary access codes for account recovery. Recovery flows can be customized using Okta Workflows or Auth0 Actions to optimize usability.
Both Okta Customer Identity and Auth0 are engineered for global-scale B2C workloads with multi-region presence, edge network acceleration, and 99.99% SLAs. Auth0 provides highly scalable login flows optimized for developer-centric CIAM use cases requiring high concurrency. Okta Customer Identity provides APIs and SDKs to help with login flows.
Okta is positioned as both a product leader and an innovation leader in this report. This is because of the breadth and depth of its capabilities which are described above. Okta’s leadership in identity innovation stems from its ability to combine advanced adaptive intelligence, cross-ecosystem interoperability, and developer-centric extensibility within a single cloud-native platform.
Okta Customer Identity and Auth0 are best suited for consumer-facing organizations that require secure, scalable, and consumer-friendly digital identity experiences. It is widely adopted across sectors such as financial services, retail, and e-commerce, media, and entertainment, travel, hospitality, and technology.
| Strengths |
|
| Challenges |
|
One Identity – OneLogin Advanced Authentication
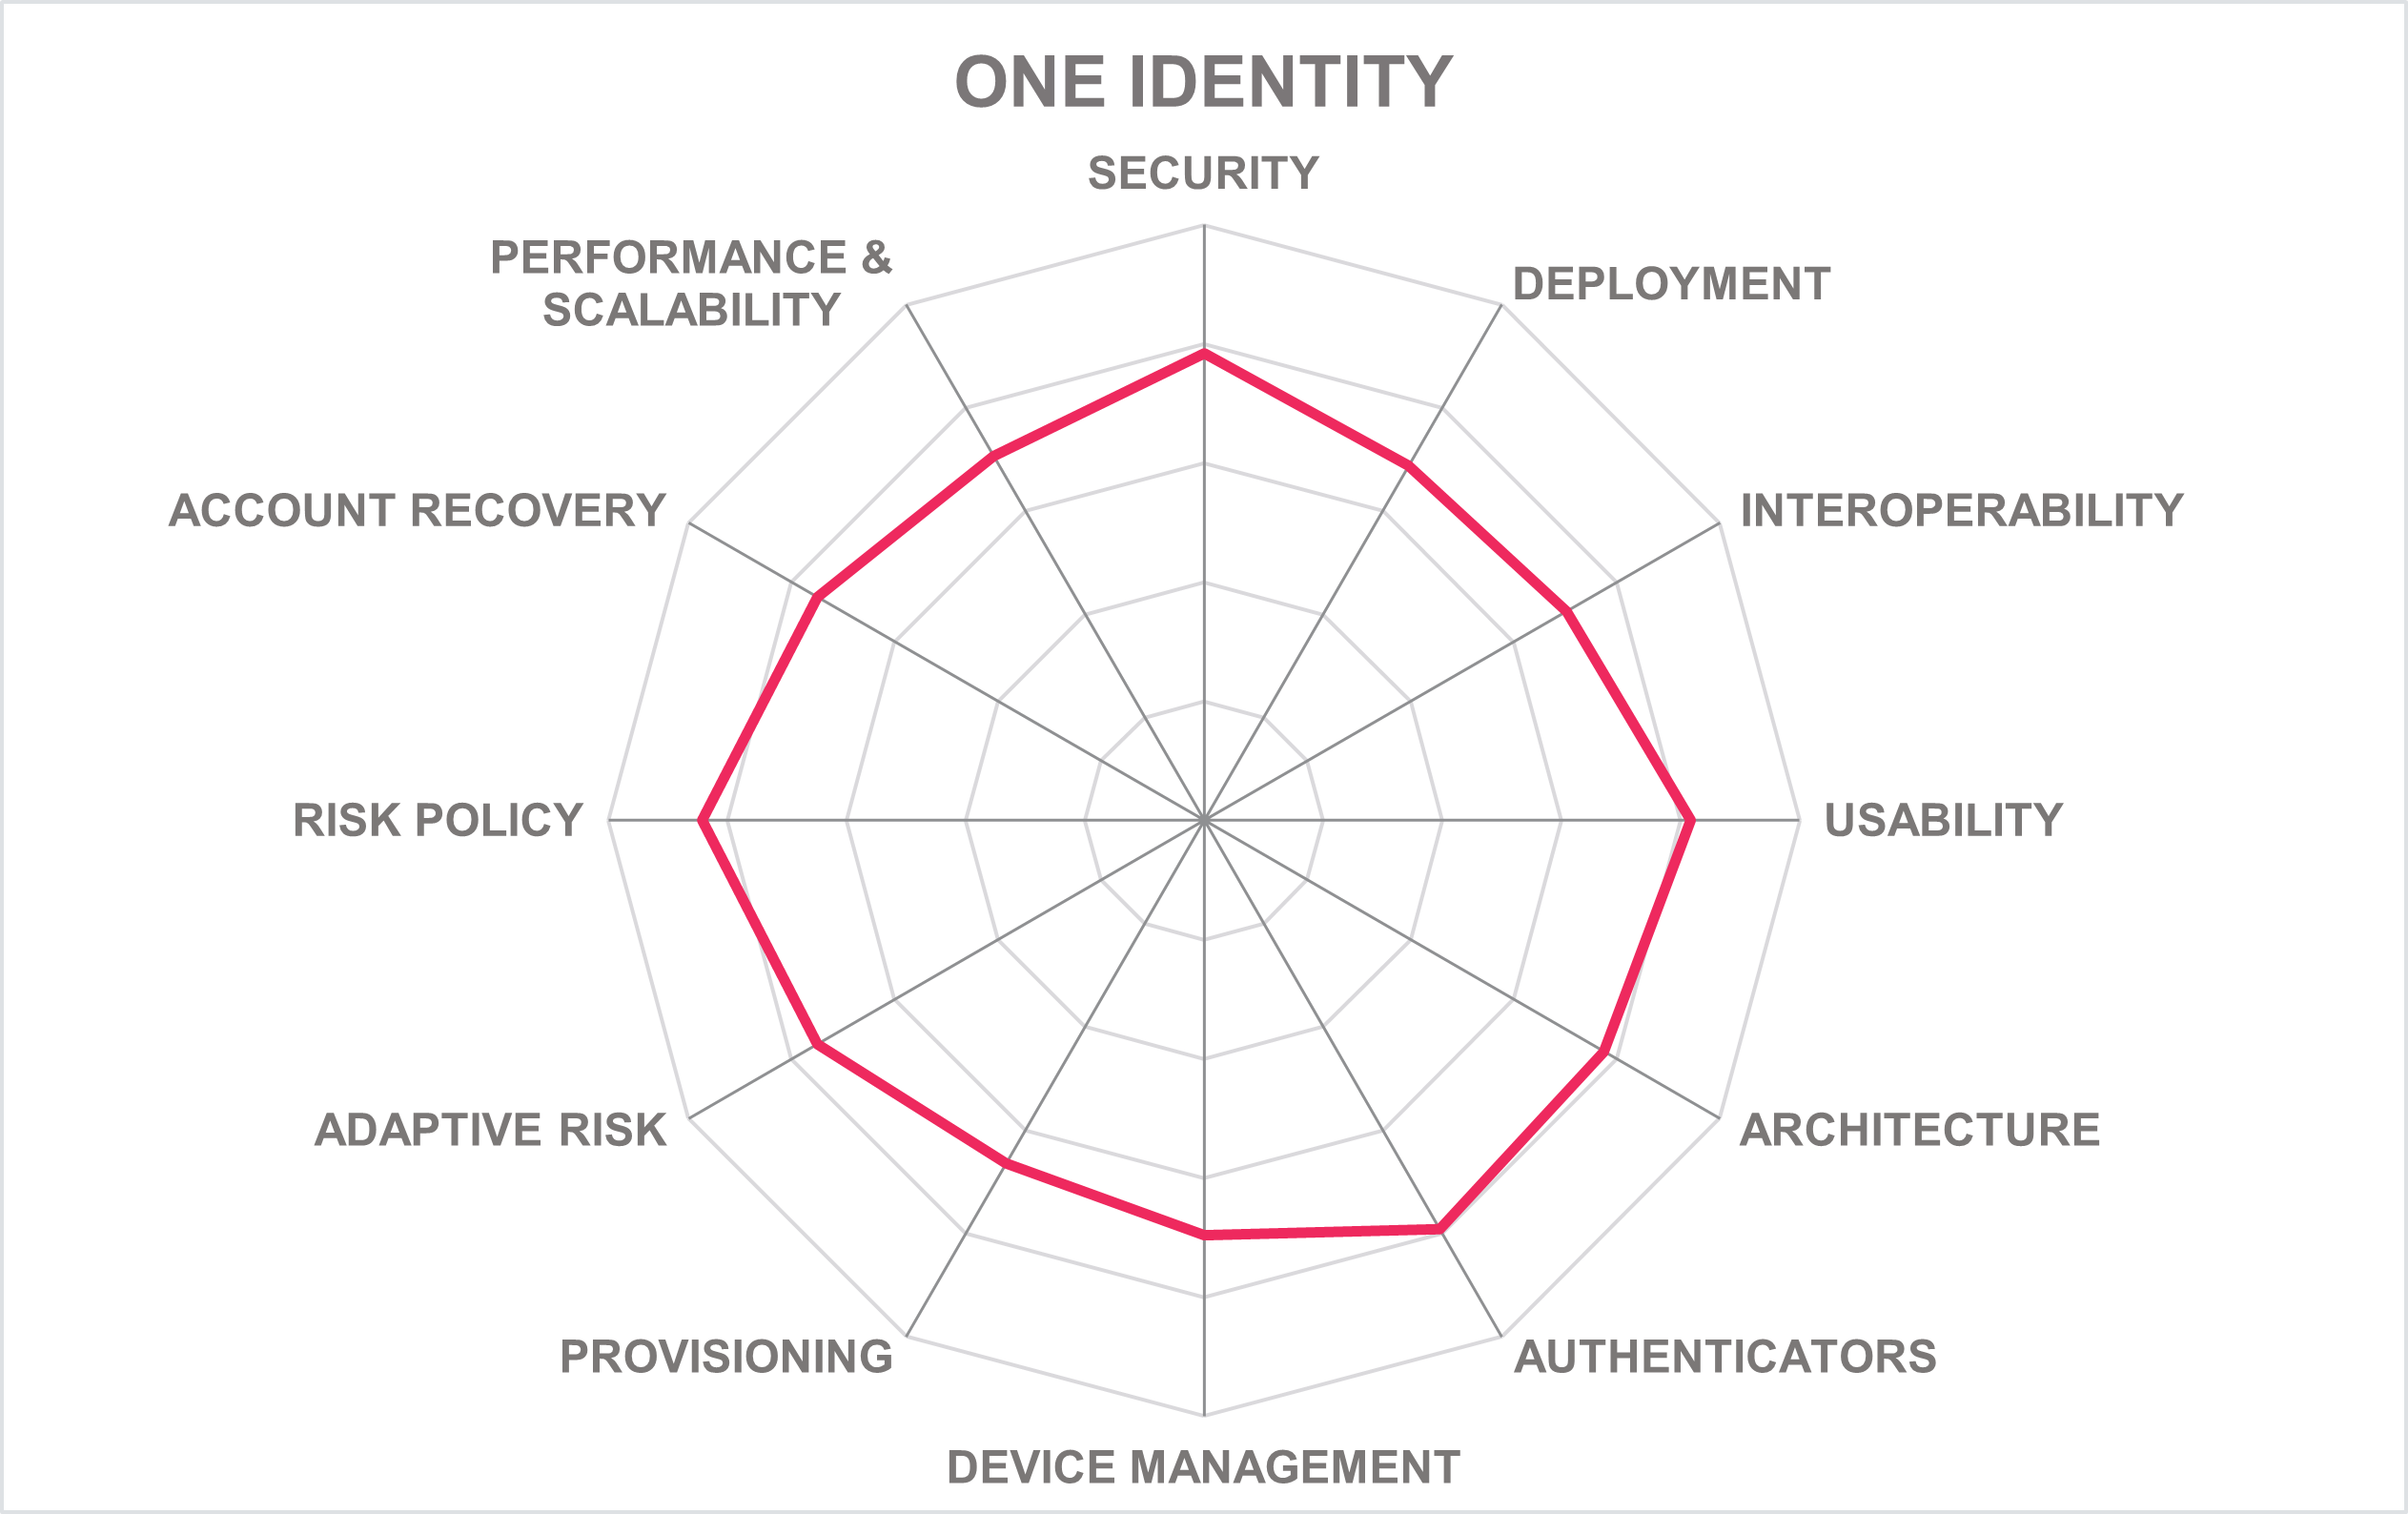
One Identity is a global identity-security provider headquartered in Aliso Viejo, California, in the US, operating as an independent brand within the Quest Software family of businesses. The company originated from the identity and access management portfolio formerly part of Dell, which was later acquired and reorganized under Quest. Today, One Identity delivers identity governance, access management and authentication solutions including OneLogin Advanced Authentication which is a cloud-first authentication platform providing MFA, WebAuthn / FIDO2-based passwordless login, risk-based authentication, and identity federation.
One Identity Advanced Authentication supports B2C passwordless authentication through passkeys (WebAuthn/FIDO2), mobile biometrics, and security keys. It integrates vendor-specific apps, to support biometric authentication native to both Android and iOS platforms. It also supports social login through Google, Apple, Facebook, and others. The OneLogin Protect app supports biometrics and push notifications. Although the solution is not FIDO-certified, it supports hardware security keys like Google Titan and YubiKey, through WebAuthn. It is also compatible with enterprise authentication protocols including SAML, OAuth 2.0, OIDC.
For B2C scenarios, the platform enables device binding through passkey registration and optionally through a mobile app for push-based authentication. OneLogin Protect is a mobile authenticator app that allows a user’s mobile device to be registered and used as a security factor (OTP generation or push notifications). In the B2C case the solution does not provide endpoint posture checks such as jailbreak/root detection, OS version, and app integrity checks, apart from the OneLogin Protect MFA app which does offer these features.
The platform supports consumer onboarding via custom self-registration links which allow users to register themselves. Self-service flows also allow consumers to manage their authenticators. While the product includes identity authentication and management capabilities, it is less focused on full CIAM provisioning than specialized B2C identity platforms. It may be integrated with a full CIAM platform or customer development using OneLogin APIs.
For adaptive risk, the platform offers SmartFactor Authentication as an add-on risk-based/adaptive authentication module that can be included for CIAM use cases. This uses ML via the SmartFactor Risk Engine risk engine to assess login attempts and dynamically adapt flows (such as step-up MFA and deny access) based on signals such as device, location, user behavior which provide contextual risk. However, it does not include factors like transaction risk, behavioral biometrics, and device malware detection.
The platform offers a graphical interface with drop-down menu options for risk policy definition. However, it lacks the capacity for importing configurations via JSON or XACML and does not allow risk factor weighting. Policies can drive actions such as step-up authentication triggered by risk scores, providing a tailored response to detected threats. The API-addressable risk analysis engine and interoperability with external services via Smart Hooks maximize this adaptability, ensuring comprehensive coverage in security response and management. Policies can incorporate factors such as risk score, device context, and user behavior, enabling flexible and dynamic consumer authentication flows.
The platform provides multiple channels for account recovery. Options include username/password fallback, security questions, OTPs via email, phone, SMS, and mobile push notifications. A help desk support option is also available.
The solution is delivered hosted on AWS and supports scaling through Horizontal Pods Autoscaling in Amazon Elastic Kubernetes Service (EKS) with an SLA uptime of 99.9%.
One Identity is a challenger in both product and innovation leadership for B2C in the passwordless authentication market. This is because its capabilities are better aligned with the enterprise use case.
One Identity should be considered by organizations that require B2C passwordless authentication as an extension of their existing One Identity enterprise solution.
| Strengths |
|
| Challenges |
|
OneSpan – Digipass S3 Authentication Software
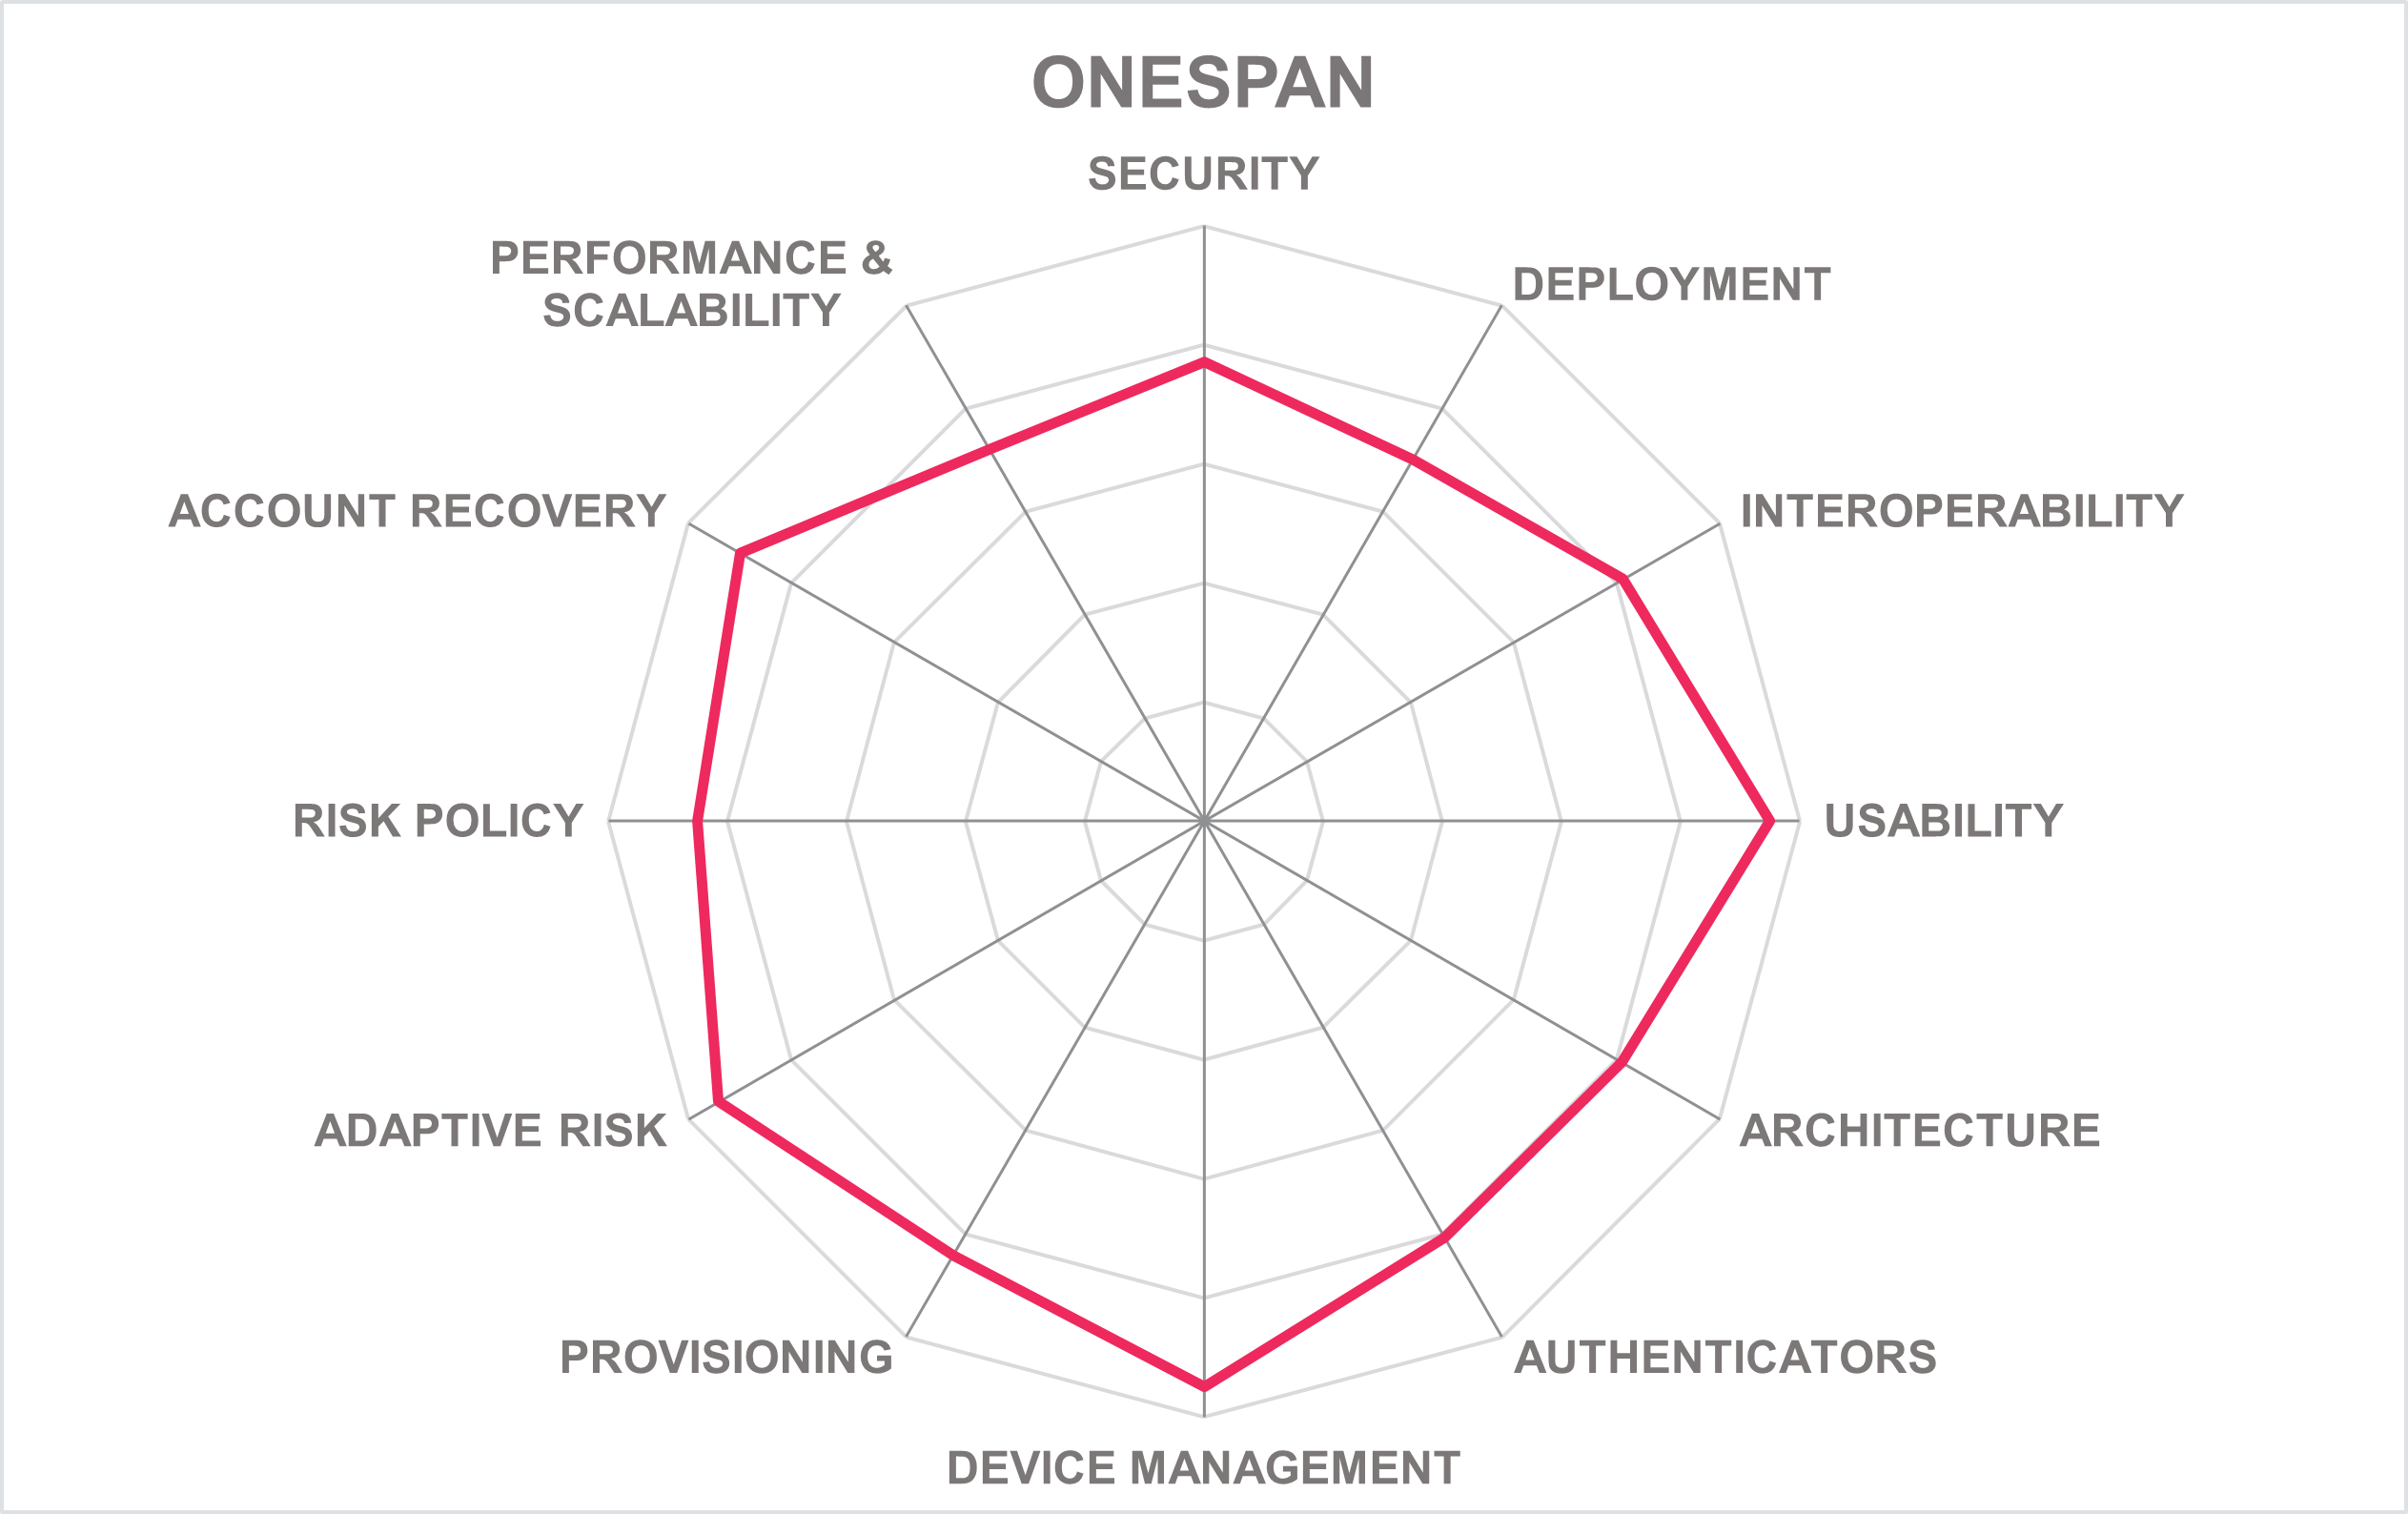
| Leader in | | | | |
OneSpan, with its headquarters in Boston, Massachusetts, in the US, was originally founded as Vasco Data Security. It provides authentication and digital identity security solutions for high-assurance consumer online channels. OneSpan offers a range of authentication solutions that cover passwordless authentication cases. These solutions are comprised of the following set of products: OneSpan Cloud Authentication, OneSpan Authentication Suite, OneSpan Authentication Server, Digipass FIDO2 security keys, OneSpan Mobile Security Suite SDK, OneSpan Mobile FIDO SDK, including latest editions from the Nok Nok acquisition: Nok Nok S3 Suite (now Digipass S3 Authentication Software), Nok Nok Authentication Cloud (now Digipass S3 Cloud), Smart Analytics, Smart Sense (now Digipass Smart Analytics and Digipass Smart Sense).
OneSpan Digipass S3 Authentication Software supports a variety of authentication methods, including username/password, passkeys, SMS OTP, mobile push notifications, and vendor-specific mobile applications. The service also supports biometrics through Android fingerprint and facial recognition, iOS Face ID, and Touch ID. It is built around FIDO2 passkeys and supports FIDO UAF, FIDO U2F and FIDO2/WebAuthn protocols, including synced and device-bound passkeys. FIDO2 server functionality is provided via OneSpan Cloud Authentication which is FIDO-certified. In addition, OneSpan Authentication Suite can be used to validate e-signatures, and it supports transaction signing.
It offers several flavors of authenticator app that can be used by companies that do not use their own mobile app for authentication. For example, Nok Nok Passport app also contains its own Bluetooth Low Energy (BLE) authenticator, which can be used as a security key when authenticating to Windows platforms.
The platform supports Mobile Phones, Wearables (watchOS and Wear OS) plus any other FIDO certified/compliant roaming authenticators, Digipass hardware authenticators, and EMV Chip Authentication Program (EMV-CAP)-enabled cards. OneSpan offers a “Root Detection SDK” (part of its Mobile Security Suite) that can detect whether an app is running on a rooted Android device or a jailbroken iOS device. It gathers contextual and device attributes including OS version, device manufacturer, IP address, geo-location, network type, and SDK version.
Digipass S3 Authentication Software supports the onboarding of consumer users through mobile/web SDKs that allow enrollment of passkeys or other authenticators. It provides lifecycle operations including onboarding, recovery, suspension, and deprovisioning. While not a full CIAM platform, Digipass S3 Authentication Software integrates with CIAM systems to deliver consumer identity registration flows.
For risk based adaptive authentication, OneSpan’s Digipass S3 Authentication Software platform collects and analyses attributes such as device health, OS version, device model, application integrity, IP reputation, network type, geo-location, geo-velocity, Wi-Fi network identity, and indicators of fraud. The policy-driven risk engine can also incorporate external fraud intelligence or behavioral biometrics through third-party integrations. The platform supports intelligent decisioning to trigger step-up verification (such as biometrics, PIN, or additional challenges) for high-risk scenarios (such as new devices, suspicious locations, or anomalous behavioral patterns.)
The platform supports risk policy management, offering both JSON-based policy import and a GUI with dropdown attributes. Risk factors can be given weights, producing a risk score (ranging 0-100) to inform authentication decisions. While direct API addressing of the risk analysis engine is not available, policies are configurable to implement step-up authentication based on risk scores.
OneSpan Digipass S3 Authentication Software supports a range of options for B2C users to recover their accounts. These include username/password, security questions/knowledge-based authentication, email OTP or link, phone and SMS OTP, mobile push notifications as well as help desk support. This can all be managed through the OneSpan policies and rule engine.
OneSpan is positioned as a product leader in the market for B2C passwordless authentication. This is based on the breadth and depth of the capabilities that the platform offers.
Organizations in regulated sectors such as finance, healthcare, and government agencies, as well as those offering high value digital platforms should consider OneSpan Digipass.
| Strengths |
|
| Challenges |
|
Ping Identity – Ping Identity Platform
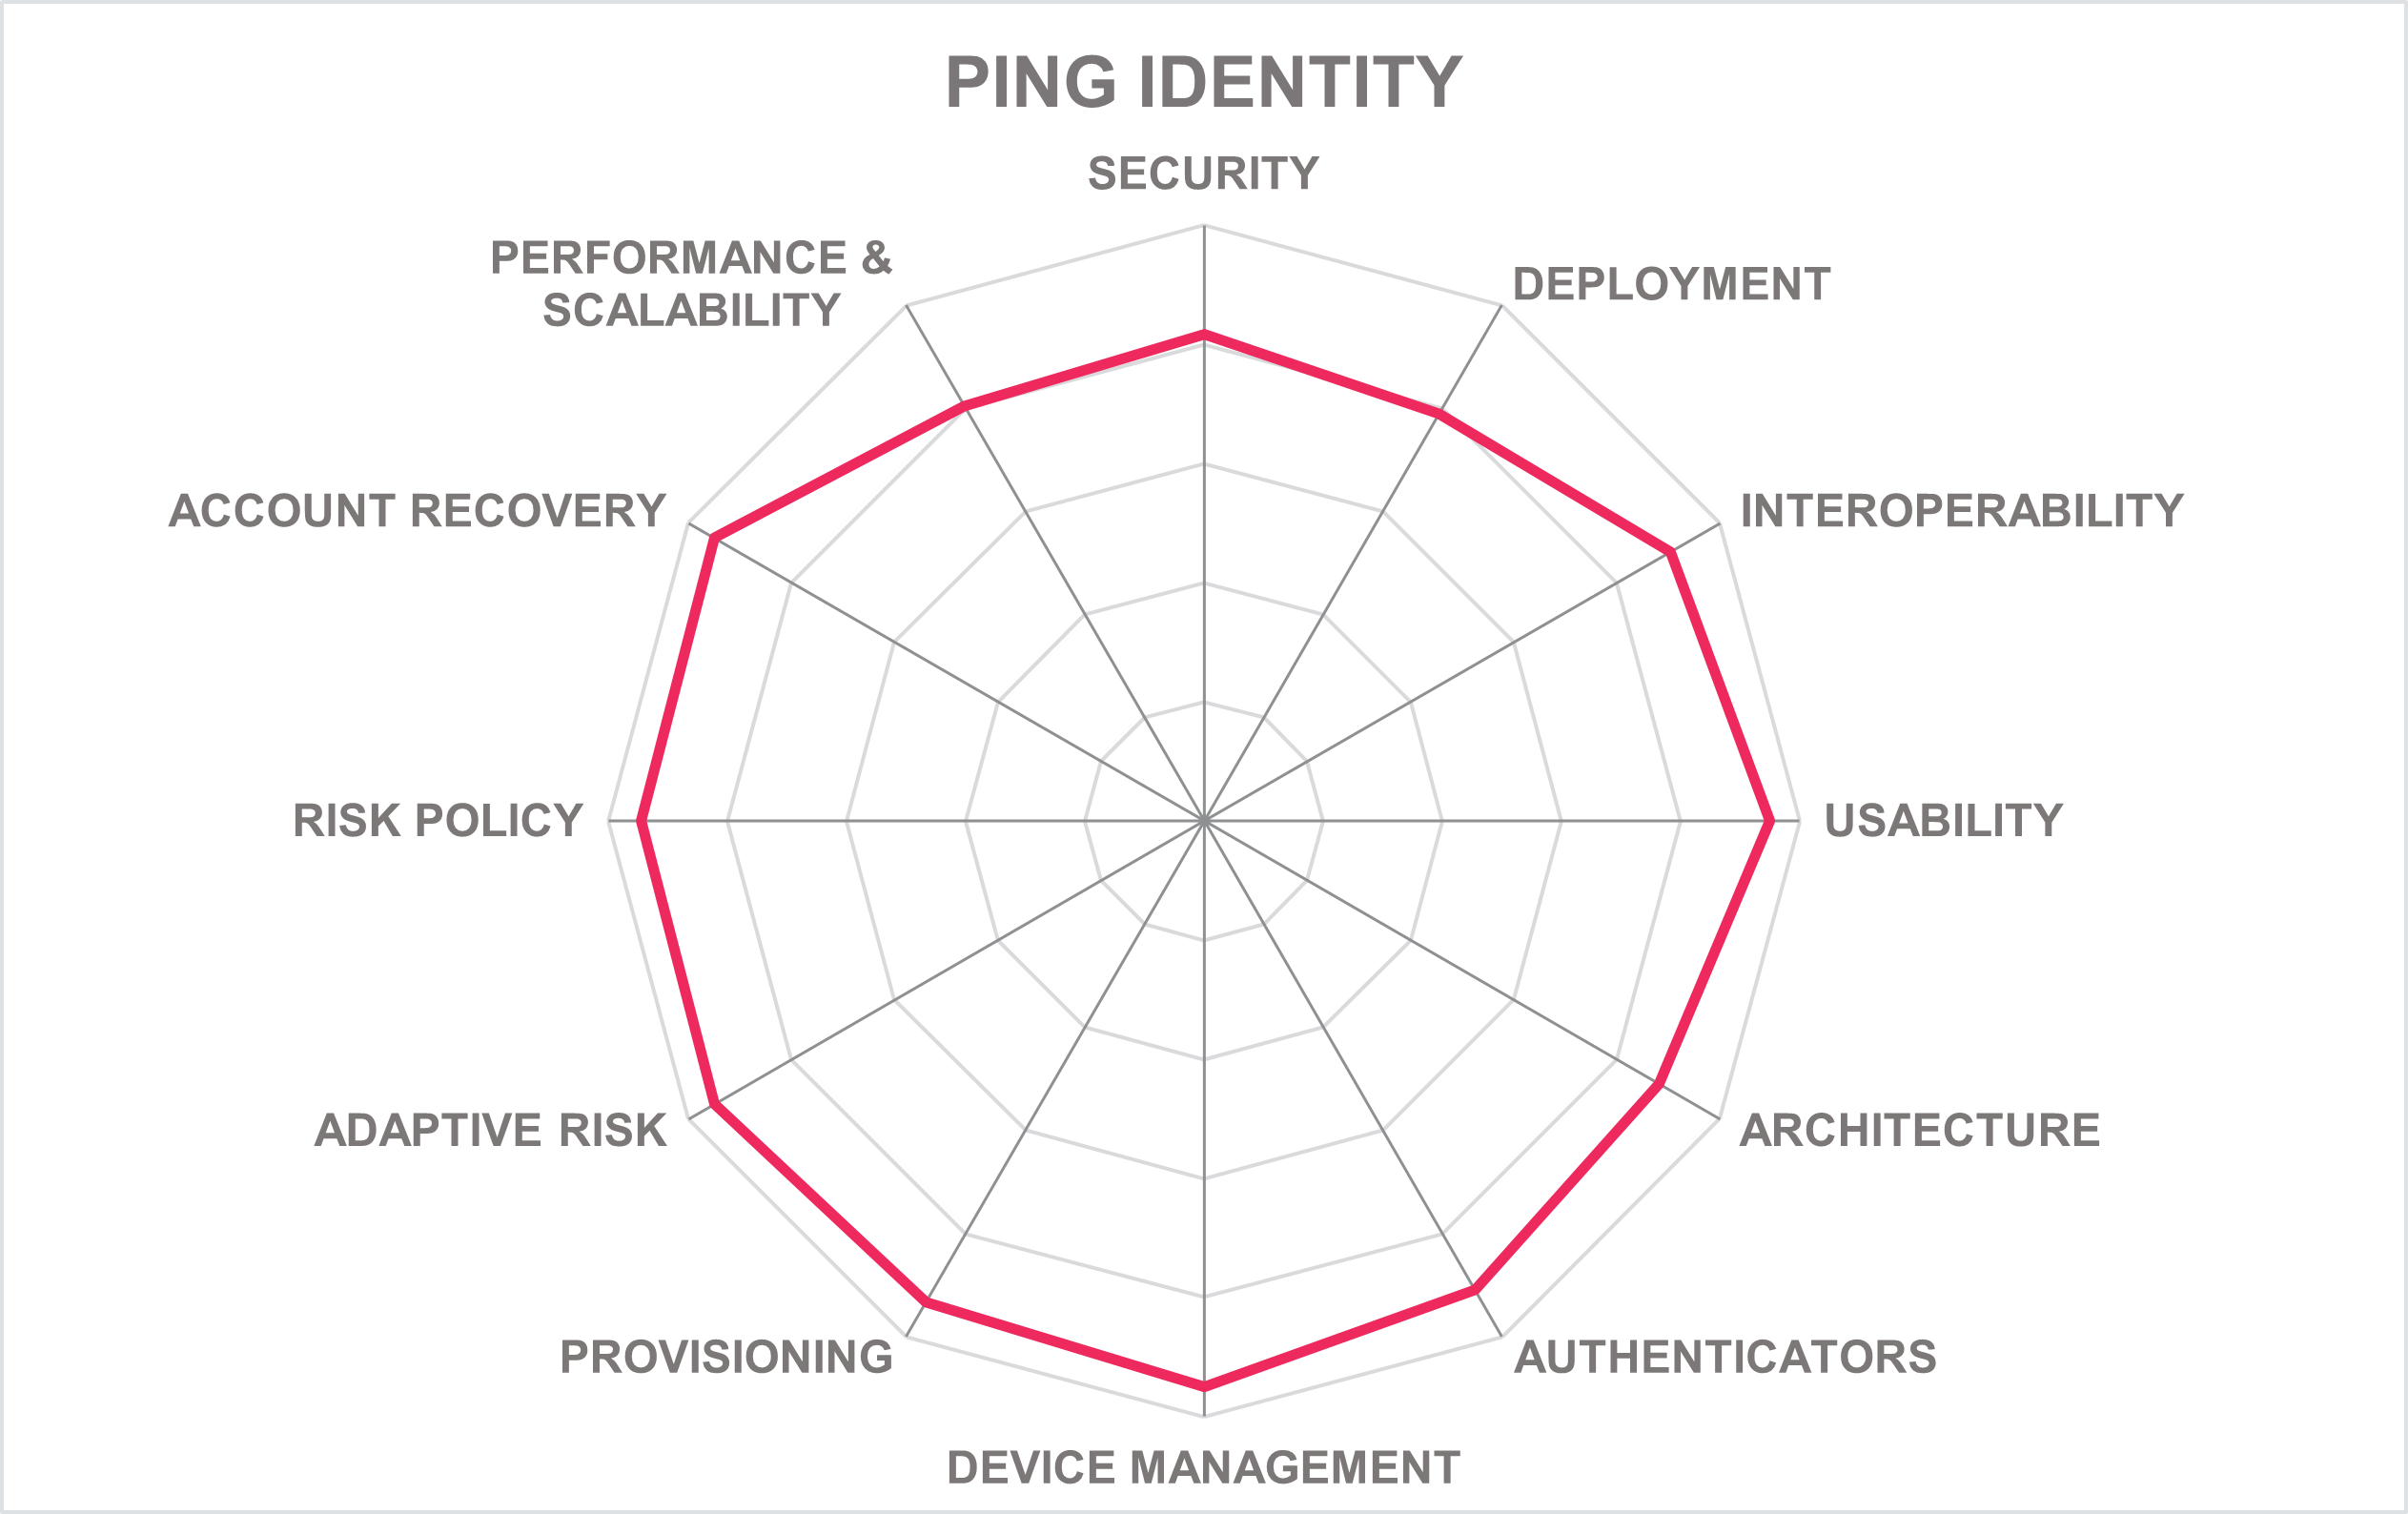
| Leader in | | | | |
Ping Identity, founded in 2002 and headquartered in Denver, Colorado, in the US, is a provider of enterprise and customer identity solutions. The Ping Identity Platform is SaaS-hosted across multiple Tier 1 IaaS providers in datacenters on five continents. Simple and predictable pricing is typically based on the number of active users per month, , or year, however, for customers that desire maximum flexibility, a transaction-based price is still available. PingOne for Customers supports passwordless authentication, including FIDO2 passkeys, adaptive risk analysis, and no-code orchestration through PingOne DaVinci. For B2C passwordless use cases, the key product components are PingOne for Customers Passwordless, PingOne Protect for adaptive risk and fraud detection, and PingOne MFA for device-based authentication and passkey support.
PingOne for Customers Passwordless provides out-of-the-box DaVinci flows that support passwordless authentication using FIDO2/WebAuthn passkeys, device biometrics, push notifications, QR codes, and magic links. Consumers can authenticate using platform biometrics such as Face ID and Touch ID. Ping’s FIDO2 server is formally certified in the FIDO Alliance Certified Products Directory. This foundation enables true passwordless sign-in rather than MFA layered on top of passwords, and it supports hybrid deployments for organizations migrating users progressively toward passwordless. Though outside of the evaluation period of this report, Ping also recently announced the intention to acquire Keyless, a privacy-preserving biometrics provider.
Ping Identity Platform enables the registration of a wide range of devices, including mobile, desktops, IoT devices, and wearables. Device recognition and lightweight device posture assessment are supported through PingOne Protect and the PingOne Signals SDK. Ping collects device attributes (OS version, browser, user agent, IP, geo-location, network type, device reputation) and supports “new device” and “suspicious device” detection. DaVinci solution packs provide dedicated sub flows for device registration and trusted device recognition, enabling consumers to reauthenticate using previously registered devices. While Ping provides device profiling, it does not natively support deep mobile device posture checks (such as jailbreak/root detection); these capabilities can be added via third-party integrations.
PingOne for Customers Plus and Passwordless include pre-built customer self-registration flows, covering account creation, email verification, terms of service agreement, device registration, and initial passwordless authenticator enrolment. DaVinci sub flows enable organizations to customize onboarding (for example, including inserting ID verification, consent collection, or fraud checks) without code. The packaged flows include “Registration and Authentication Main Flow” and “CIAM Passwordless Registration/Authentication/Recovery Main Flow,” designed specifically for B2C adoption.
Adaptive authentication and fraud detection capabilities are provided by PingOne Protect, which applies ML and behavioral analysis to each sign-in attempt. PingOne Protect evaluates a broad set of signals including Bot detection, IP/user velocity, geo-location anomalies, device reputation, anonymous or risky networks, behavioral signals (via SDK), and new-device or suspicious-device predictors. Risk scoring is integrated with DaVinci, allowing flows to automatically step up based on risk.
The Ping Identity Platform capabilities for risk policy authoring include JSON imports, XACML, and a graphical interface. Policies can incorporate weighted risk factors to generate scores ranging from 0 to 100, determining actions such as step-up authentication or transaction verification. The risk engine is API-accessible and interoperable with third-party services like authorization and fraud engines, ensuring comprehensive integration for real-time access decisions.
PingOne for Customers Passwordless includes account recovery sub flows within DaVinci solution packs. Recovery uses email possession, device recognition, or high-assurance checks via PingOne Protect. The flows support re-binding of authenticators (such as registering a new passkey) after identity verification. PingOne Verify provides IDV services via mobile/web/desktop SDKs that do selfies (with liveness detection) to document photo matching. It is designed to be resilient against deepfakes and user-friendly. More than 13,000 document types are supported. Moreover, connectors are available for more than 30 third-party IDV services.
Ping Identity is a product leader in B2C passwordless authentication due to its combination of FIDO2-certified passkey authentication, advanced adaptive risk detection, and a highly flexible no-code orchestration platform (DaVinci) that enables organizations to design frictionless consumer identity journeys.
PingOne for Customers is well suited for organizations looking for a B2C passwordless solution as part of a cloud-native CIAM platform designed for large consumer populations with multi regional support.
| Strengths |
|
| Challenges |
|
Relock – Relock invisible MFA.
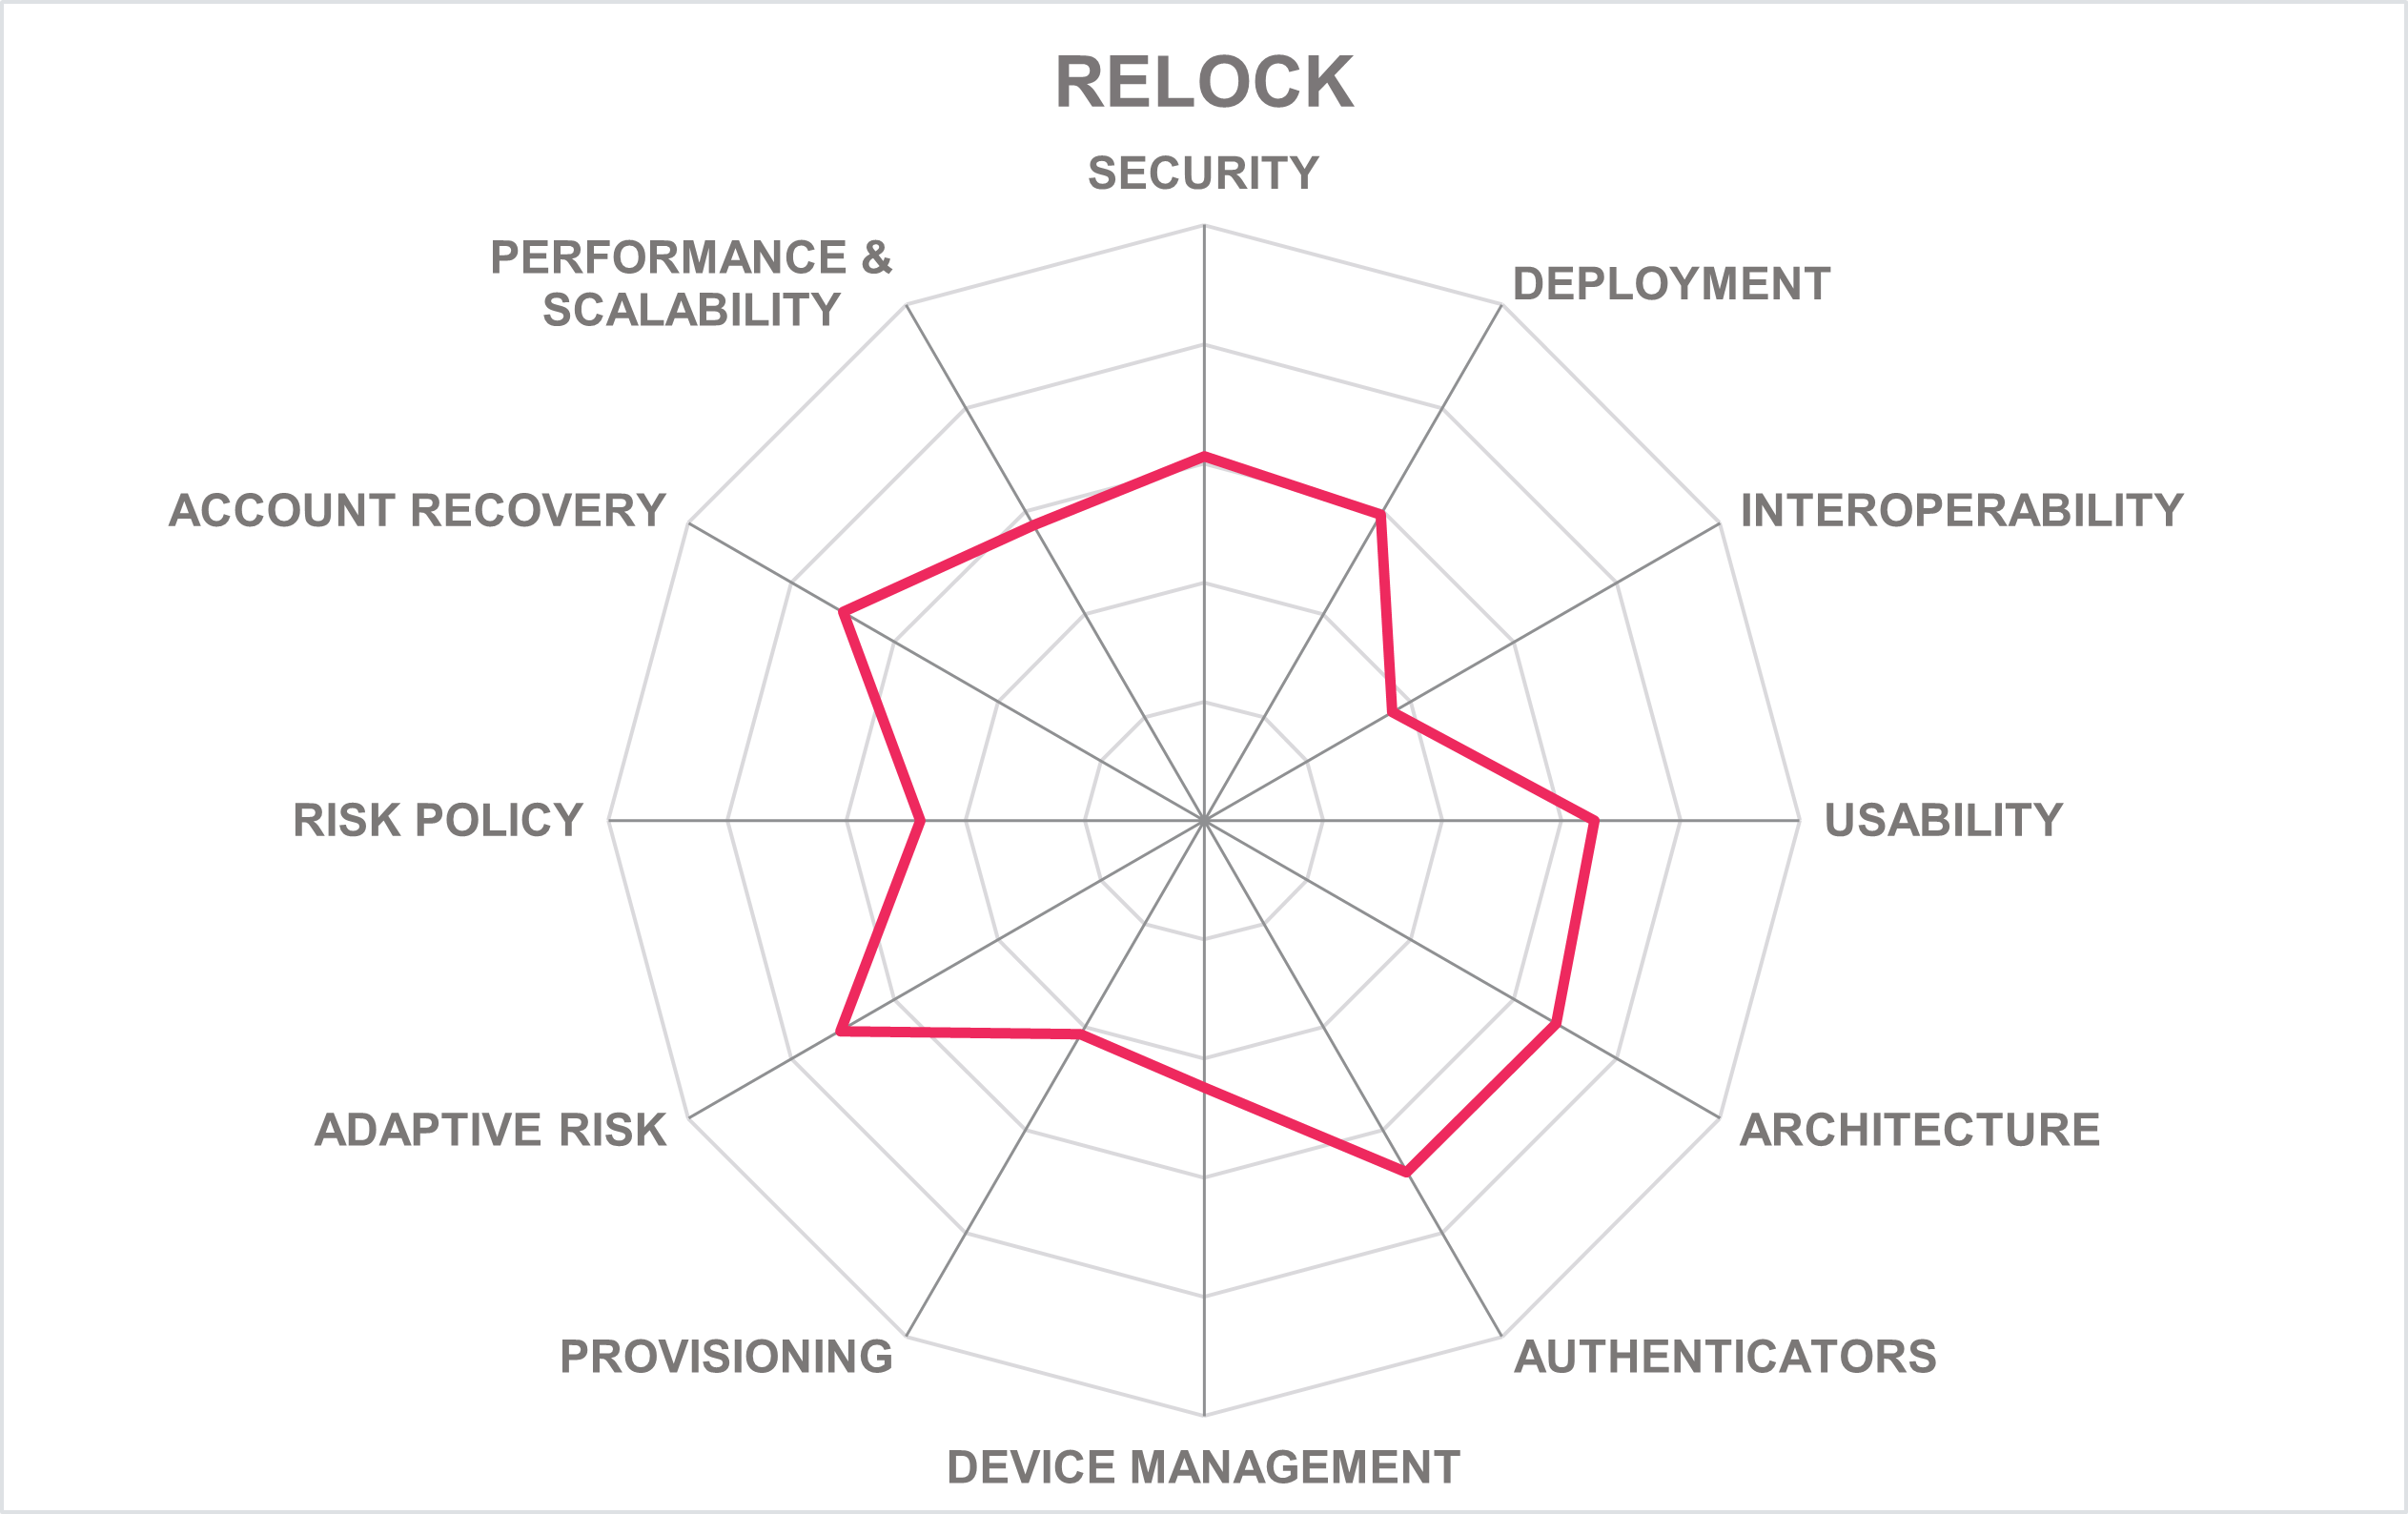
Relock is a US-based cybersecurity startup founded in 2023 and headquartered in Austin, Texas. It positions itself as the first “passive authentication company,” focused on invisible, continuous authentication for both internal and external users. The Relock platform operates with cryptographic session validation and transparent MFA checks that run silently in the background without requiring user interaction. Its value proposition is centered on eliminating phishing, session hijacking, and token theft.
Relock delivers authentication through an invisible, continuous verification model using cryptographic one-time keys that are regenerated and validated continuously. Instead of requiring explicit consumer actions such as passkey prompts or OTPs, the system silently verifies session legitimacy in the background, even if credentials have been compromised. This approach secures B2C authentication flows from phishing, token theft, and session hijacking. While Relock is not a FIDO server, it can operate alongside a FIDO2/passkey system within a broader CIAM architecture.
Relock does not function as a full device-management or mobile-attestation solution, but it uses browser-/session-level telemetry, device binding properties, and continuous signature checks to maintain session and device integrity. The platform verifies each interaction independently, ensuring that even if tokens are stolen or replayed on another device, Relock can terminate or block the session. The platform verifies each interaction independently, ensuring that even if tokens are stolen or replayed on another device, Relock can terminate or block the session.
Relock currently does not allow for bulk provisioning from LDAP or SCIM and does not support provisioning to or from cloud services using specific APIs. However, user self-registration is supported.
The solution evaluates adaptive risk factors including IP address checks, geo-location, geo-velocity, device ID and type, date/time, and device fingerprinting. It supports software signatures but does not perform device posture assessment or evaluate device reputations. User history and detection of known users on new devices are present, but jailbreak/root checks and risk-based access controls are not supported.
Relock's approach to risk policy management is limited, with no support for importing policies, obtaining risk scores, or risk analysis via an API. However, it does allow for configuring deterministic security signals to trigger specific actions in response to different security events, which can be used to construct policy actions like step-up authentication.
Relock is a challenger in both product and innovation leadership. It offers a niche product for browser-based passwordless authentication.
The solution supports account recovery through email and phone OTPs, SMS OTPs, mobile push notifications, and account linking, though it does not support username/password recovery or security questions/KBA.
Organizations that require B2C passwordless capabilities that are limited to browser-based access should consider Relock.
| Strengths |
|
| Challenges |
|
SecureAuth – SecureAuth IAM
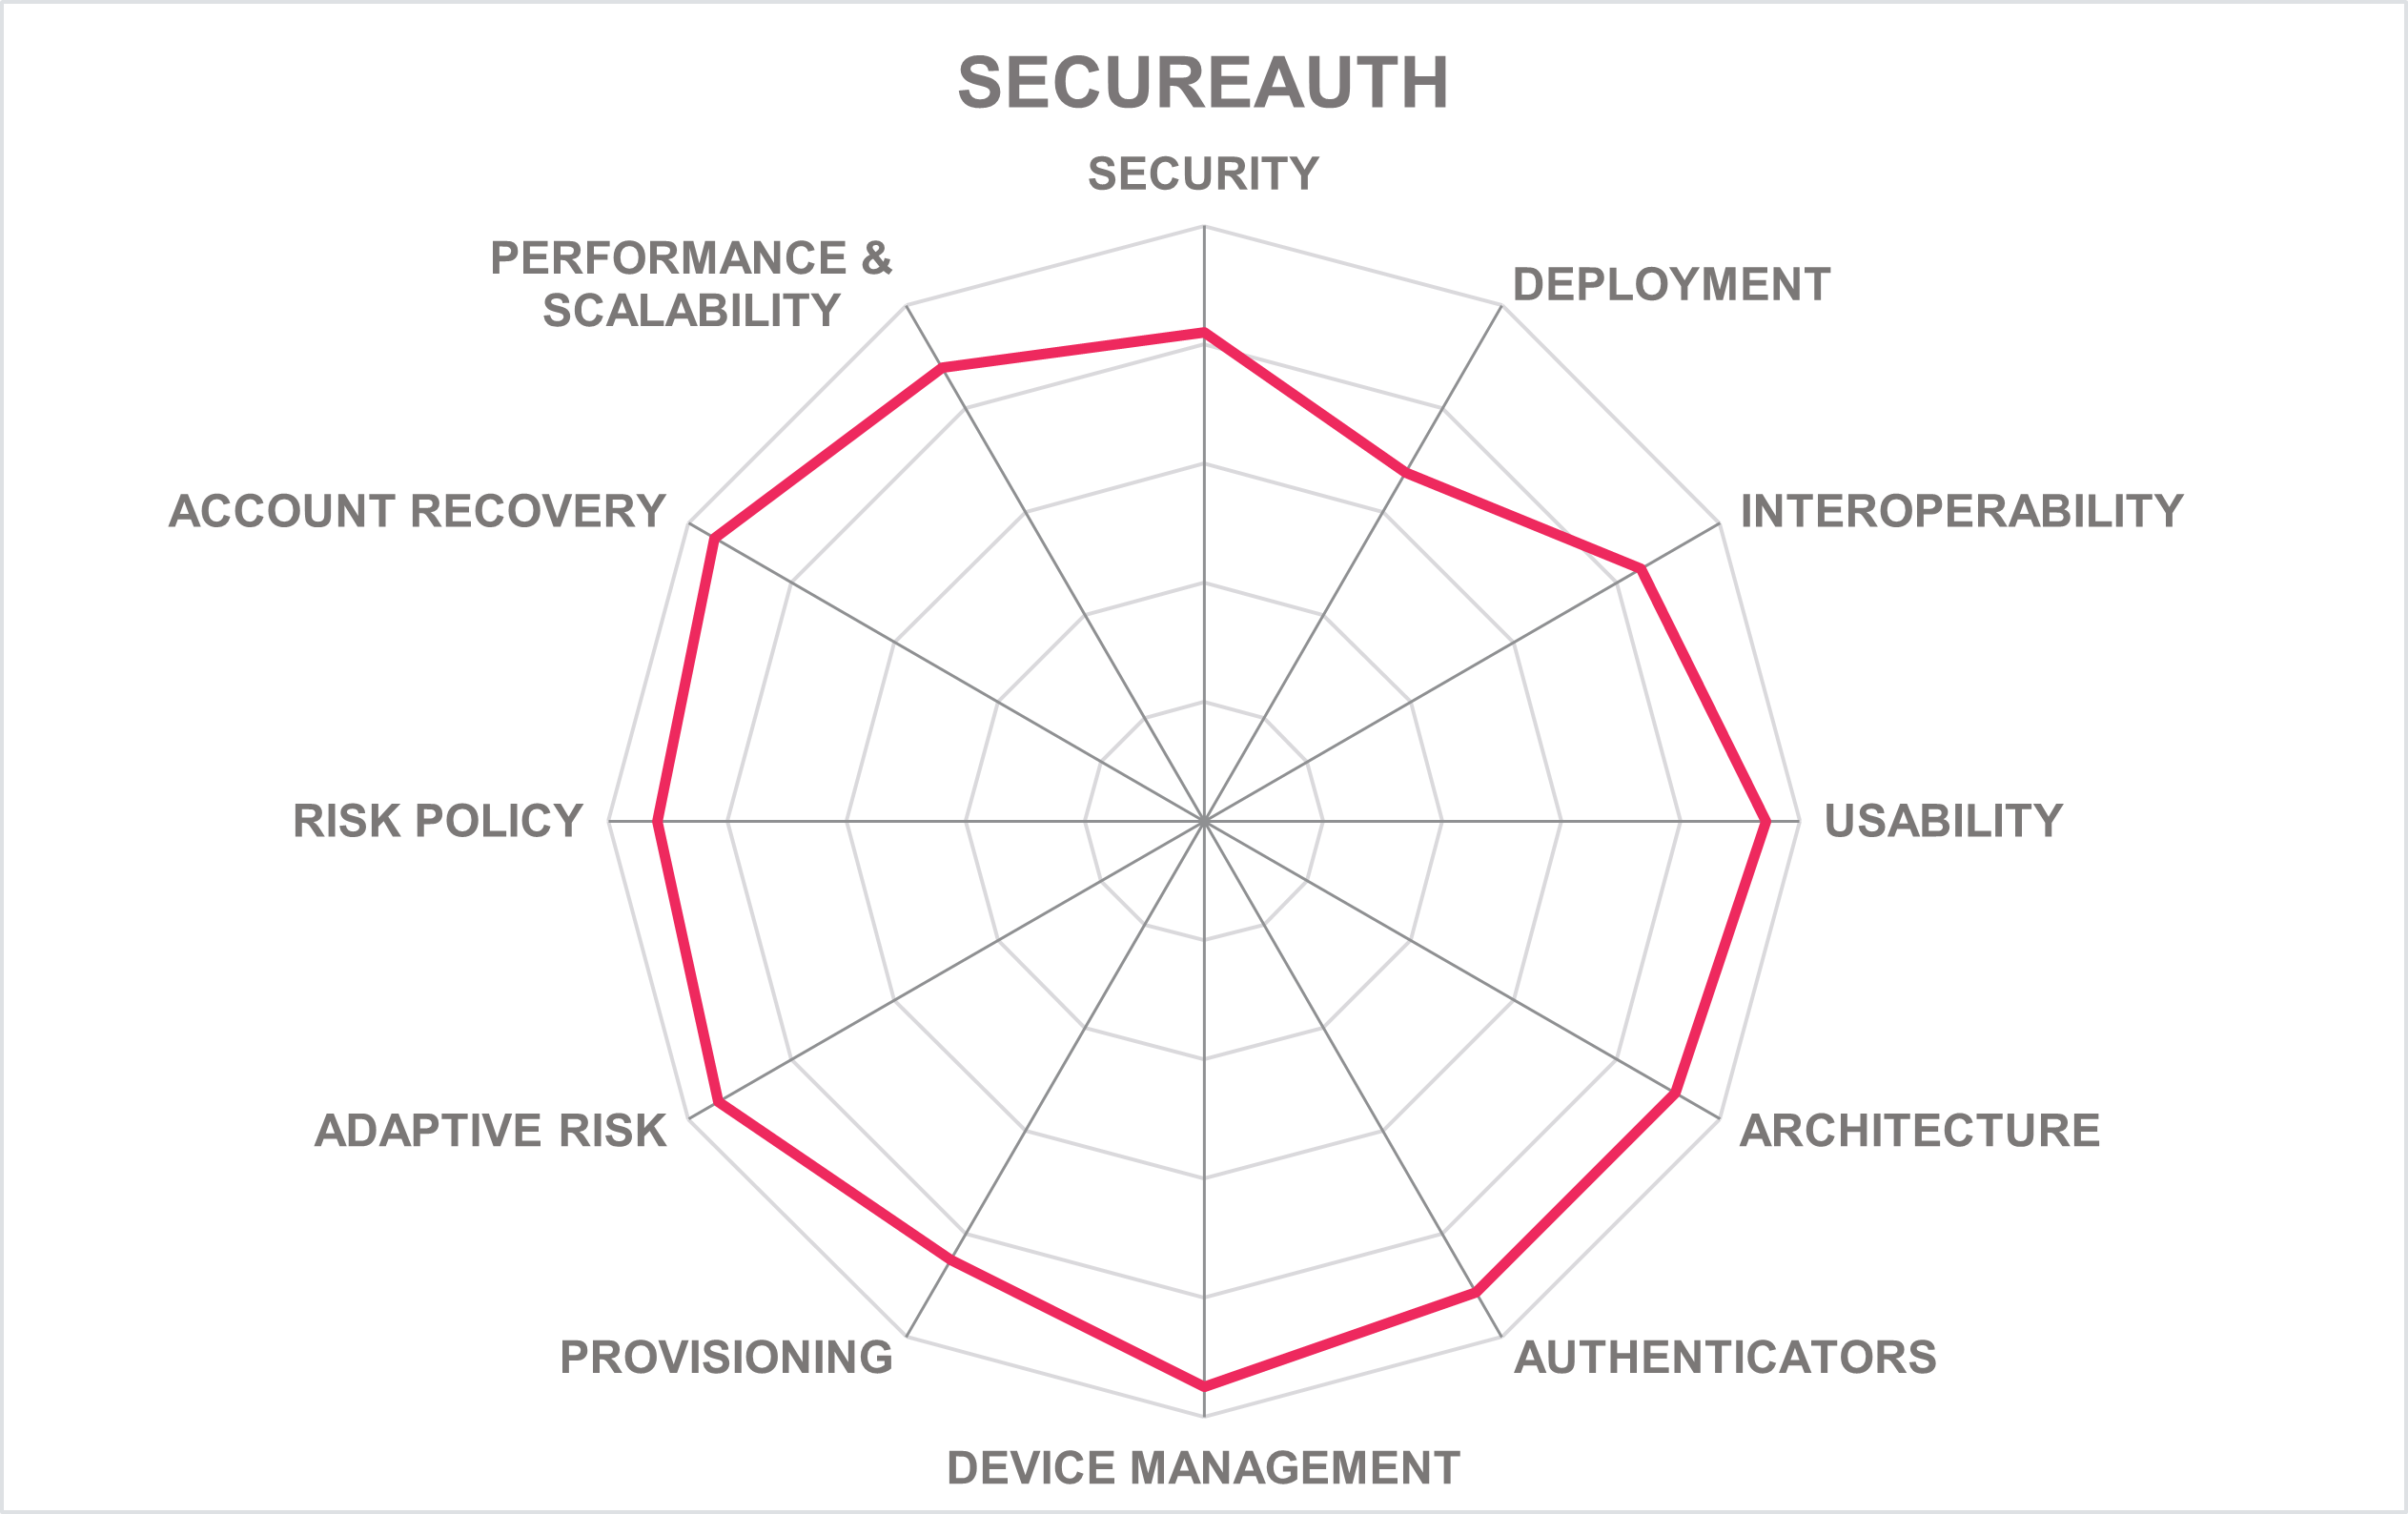
| Leader in | | | | |
SecureAuth, founded in 2005 and headquartered in Irvine, California, in the US, acquired Cloudentity in late 2023. SecureAuth is recognized for its enterprise workforce IAM and passwordless MFA authentication offerings, while Cloudentity was known for its CIAM and advanced authorization capabilities. SecureAuth IAM is the combined solution, which is available via public SaaS hosted on a Tier 1 IaaS provider across three continents and can also be deployed on-premises or in private clouds that support Kubernetes.
SecureAuth IAM accepts the widest range of authenticators, including TOTPs, mobile push notifications, Mobile Connect, all major authenticator apps, Android and iOS biometrics, and all flavors of FIDO. SecureAuth’s platform supports the FIDO Alliance standards via FIDO2/WebAuthn for customer identity management, and SecureAuth is a member of the FIDO Alliance. Additionally, SecureAuth is capable of being its own passkey provider, which eliminates its customers’ dependence on passkeys provided by the larger public IDPs such as Apple, Google and Microsoft.
SecureAuth supports the registration of a wide range of device types such as mobile phones, desktops, tablets, and wearables. It incorporates some device posture checks including antimalware and firewall detection. For B2C use the platform can recognise known devices and apply risk policies. Users can associate multiple devices for authentication purposes, and the solution facilitates device recovery options if devices are changed or replaced.
In the B2C/CIAM context, SecureAuth supports branded registration workflows, self-service account creation, social login, passkey registration, and identity-pool onboarding. It also supports bulk provisioning from both LDAP and SCIM. The solution integrates with other cloud services through APIs, supporting user provisioning and deprovisioning.
SecureAuth’s platform includes an adaptive risk engine that evaluates device context, behavior, location, session dynamics, and threat indicators (for example compromised credentials, and account takeover patterns) to manage authentication decisions. These risk assessments include checks on IP addresses, geolocation, geo-velocity, date/time, and specific device identifiers. The solution also processes and tracks device and browser fingerprints and performs device posture assessments. Known compromised credential intelligence is employed to flag and prevent login attempts from high-risk scenarios, while integrated fraud detection capabilities help to protect against suspicious activities.
Risk policies can be authored using various methods, including GUI-based approaches with flow chart models and policy import via JSON. The SecureAuth solution allows for weighing different risk factors within policies and computes a risk score that informs access decisions. Administrators can construct policies that trigger specific actions, like step-up authentication, based on the evaluated risk score. The policy framework supports integration with third-party services, such as external authorization services and SIEM platforms.
SecureAuth offers account recovery options including password recovery, security questions, email OTP or link, phone and SMS OTP, mobile push notifications, and account linking. Help desk assistance is also available.
SecureAuth’s platform is cloud-native, supports multi‐tenant and multi-brand B2C identity flows, and markets scalability for large consumer populations. SecureAuth has obtained SOC 2 Type 2 attestation and ISO27001 certifications. Set-up and incident handling services are available as part of premium support packages. English is the only language for support and documentation.
SecureAuth is a product leader in this report. It combines standards-based passwordless methods (passkeys/biometrics) with adaptive risk and device intelligence, all within a unified CIAM platform designed for consumer experiences.
Organizations with large numbers of consumers and complex digital channels, such as telecommunications providers, online retailers, media platforms, utilities as well as financial regulated Industries requiring adaptive risk & fraud controls should consider SecureAuth.
| Strengths |
|
| Challenges |
|
Signicat – MobileID
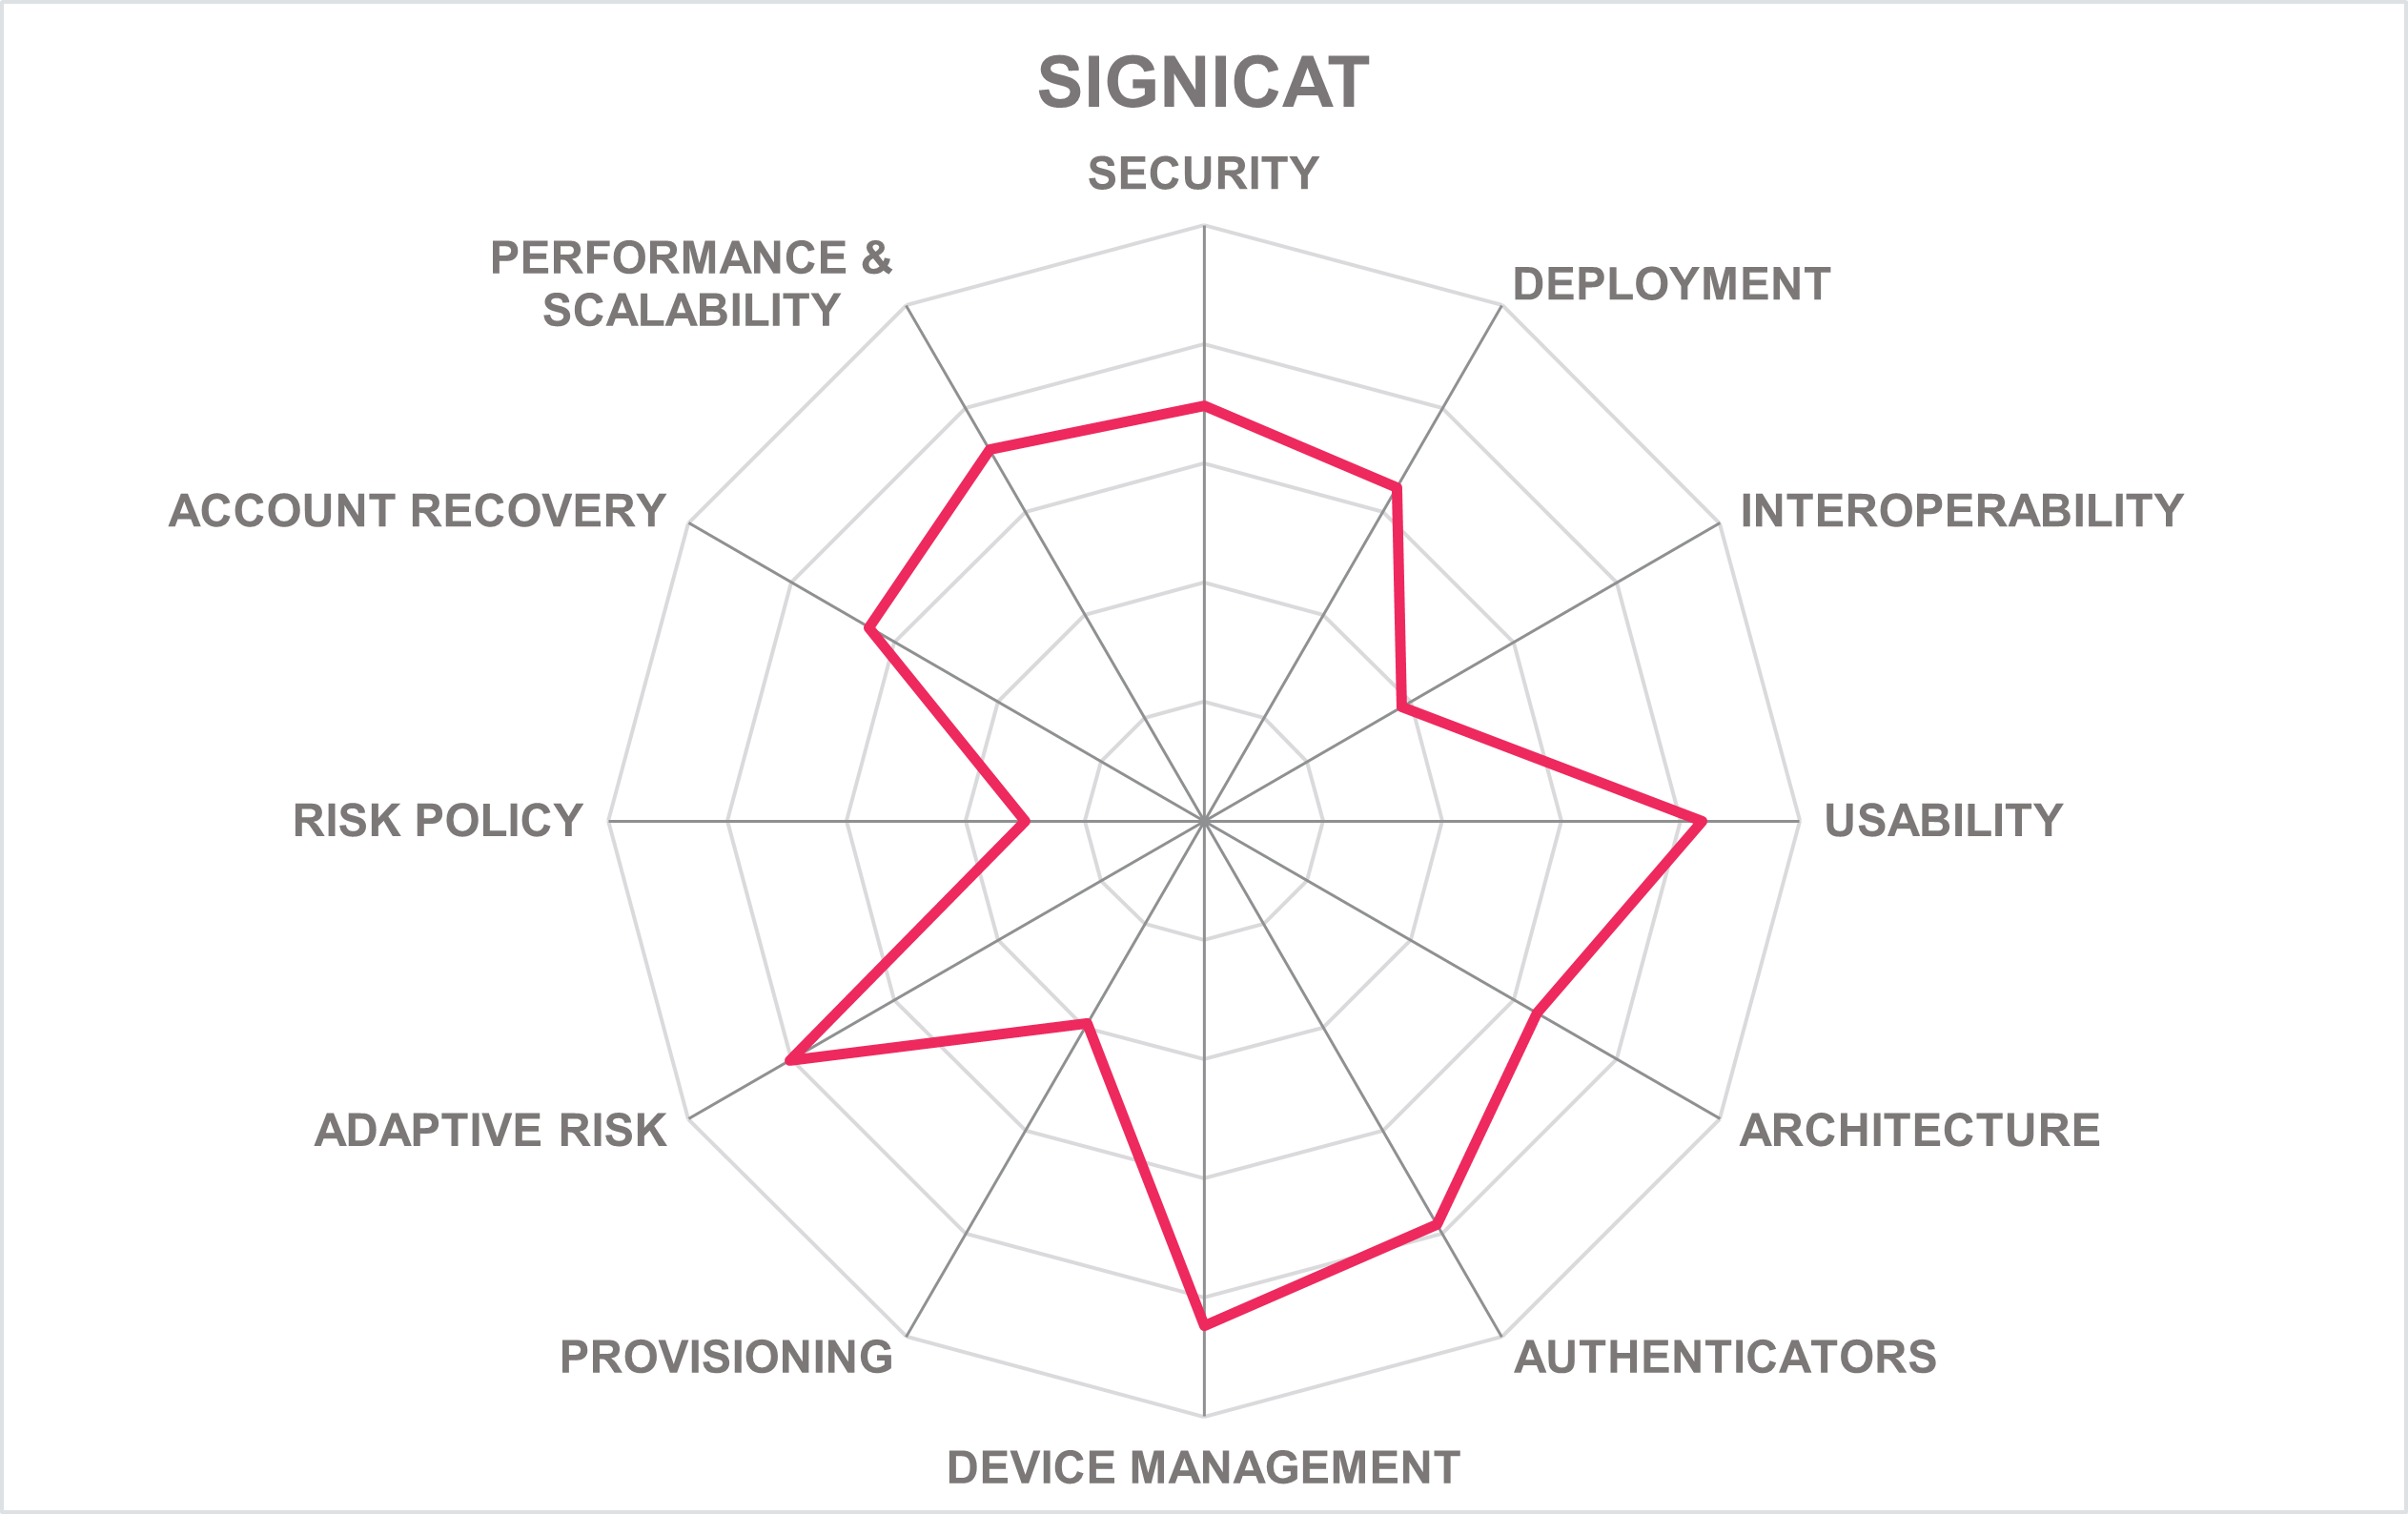
Signicat is a European digital identity and trust-services provider, founded in 2006 and headquartered in Trondheim, Norway. It operates one of Europe’s digital identity platforms, covering identity proofing, authentication, electronic signatures, and orchestration, and is a Qualified Trust Service Provider (QTSP) under eIDAS.
Signicat MobileID is their mobile strong customer authentication product, providing secure mobile identification, authentication, and authorization via an organization’s own mobile app, with on-device biometrics, device binding, app attestation, and PSD2-compliant strong customer authentication.
MobileID is a software-based MFA product that can be deployed on either Android or iOS. In addition to MobileID, Signicat supports passkeys as an authentication method, and if a hardware token is chosen to store the passkey, it can support that token, for example YubiKey. Signicat Passkeys can support any native FIDO authentication methods, such as Apple Face ID or Android Biometrics. It can also support third-party Fido Authenticators such as YubiKey, providing they support Passkeys. However, MobileID itself is not listed in the public FIDO Alliance Certified Products directory as a FIDO2 server or authenticator.
MobileID uses the mobile device as a possession factor combined with either server-side biometrics (with Face Authentication) as an option for MFA, on-device biometrics (Face ID, Touch ID, or Android fingerprint) or a local PIN, providing PSD2-compliant MFA. It supports login, transaction authorization, and confirmation of sensitive operations entirely within the customer’s own mobile app.
MobileID creates a strong and persistent binding between a MobileID user and one or more mobile devices. Those devices then function as the trusted possession factor for authentication and transaction authorization. The MobileID feature set includes app attestation and app security to detect third-party use of the APIs, prevent tampering, and harden the app against common mobile attacks. It creates a device hash for each device that is unique to that specific app and device. It also stores private keys in the trusted execution environment, ensuring that the keys are bound uniquely to that device. The protocol involves rolling encryption of the keys for each transaction to protect against cloning of the device.
MobileID supports user registration and device enrolment flows via its APIs and authenticator app, or SDK for Android. During registration, MobileID generates an activation code which is passed back to the relying service; this code can be passed by the customer to the app, displayed on a web page or other channel, or represented as a QR code for the user to scan with the app. This enables onboarding where end users self-enroll their device and set up biometrics or a PIN for MobileID without manual admin intervention. Mobile ID integrates with Signicat’s broader identity platform (eID Hub, ReuseID, and identity proofing), allowing B2C providers to combine mobile enrolment with KYC or eID-based verification and orchestrated CIAM flows.
MobileID evaluates adaptive risk factors including IP address, geolocation, date/time, device ID, and type, amongst others. It supports device fingerprinting and posture assessment, contributing to the security of the device environment through checks on OS patch levels and RASP solutions. In addition, it includes face authentication with 3D liveness and 3D face matching to counter fraud such as deepfakes, account takeover, and AI-driven identity attacks. While it does not integrate with FRIPs, Signicat is in progress of developing capabilities in this area.
MobileID does not have any out-of-the-box policy configuration capabilities. However, single-factor authentication (1FA), two-factor authentication (2FA), or a combination of 1FA-Device with PIN/Biometrics or Server-Side Biometrics are supported based on policies for that are implemented in the customers domain.
MobileID offers a proprietary account recovery method. This combines possession of a new device with additional verification (for example SMS, email, or eID-backed verification) mediated by the relying service. MobileID manages technical credential recovery and binding, while the customer’s backend and Signicat’s orchestration can enforce appropriate verification steps for B2C recovery flows.
Scalability is supported through automatic scaling on Google Cloud, allowing for dynamic management in response to increased loads to maintain performance metrics. The SLA promises 99.8% availability, with a higher guarantee available at additional cost.
Signicat is a challenger in product and innovation leadership. MobileID offers highly specialized capabilities targeted on specific markets. While these are excellent for that market, their range of capabilities does not match those provided by leading generalist vendors.
Organizations looking for a B2C passwordless authentication solution with a strong European base and ecosystem should consider Signicat.
| Strengths |
|
| Challenges |
|
Thales Group – Thales OneWelcome Identity Platform
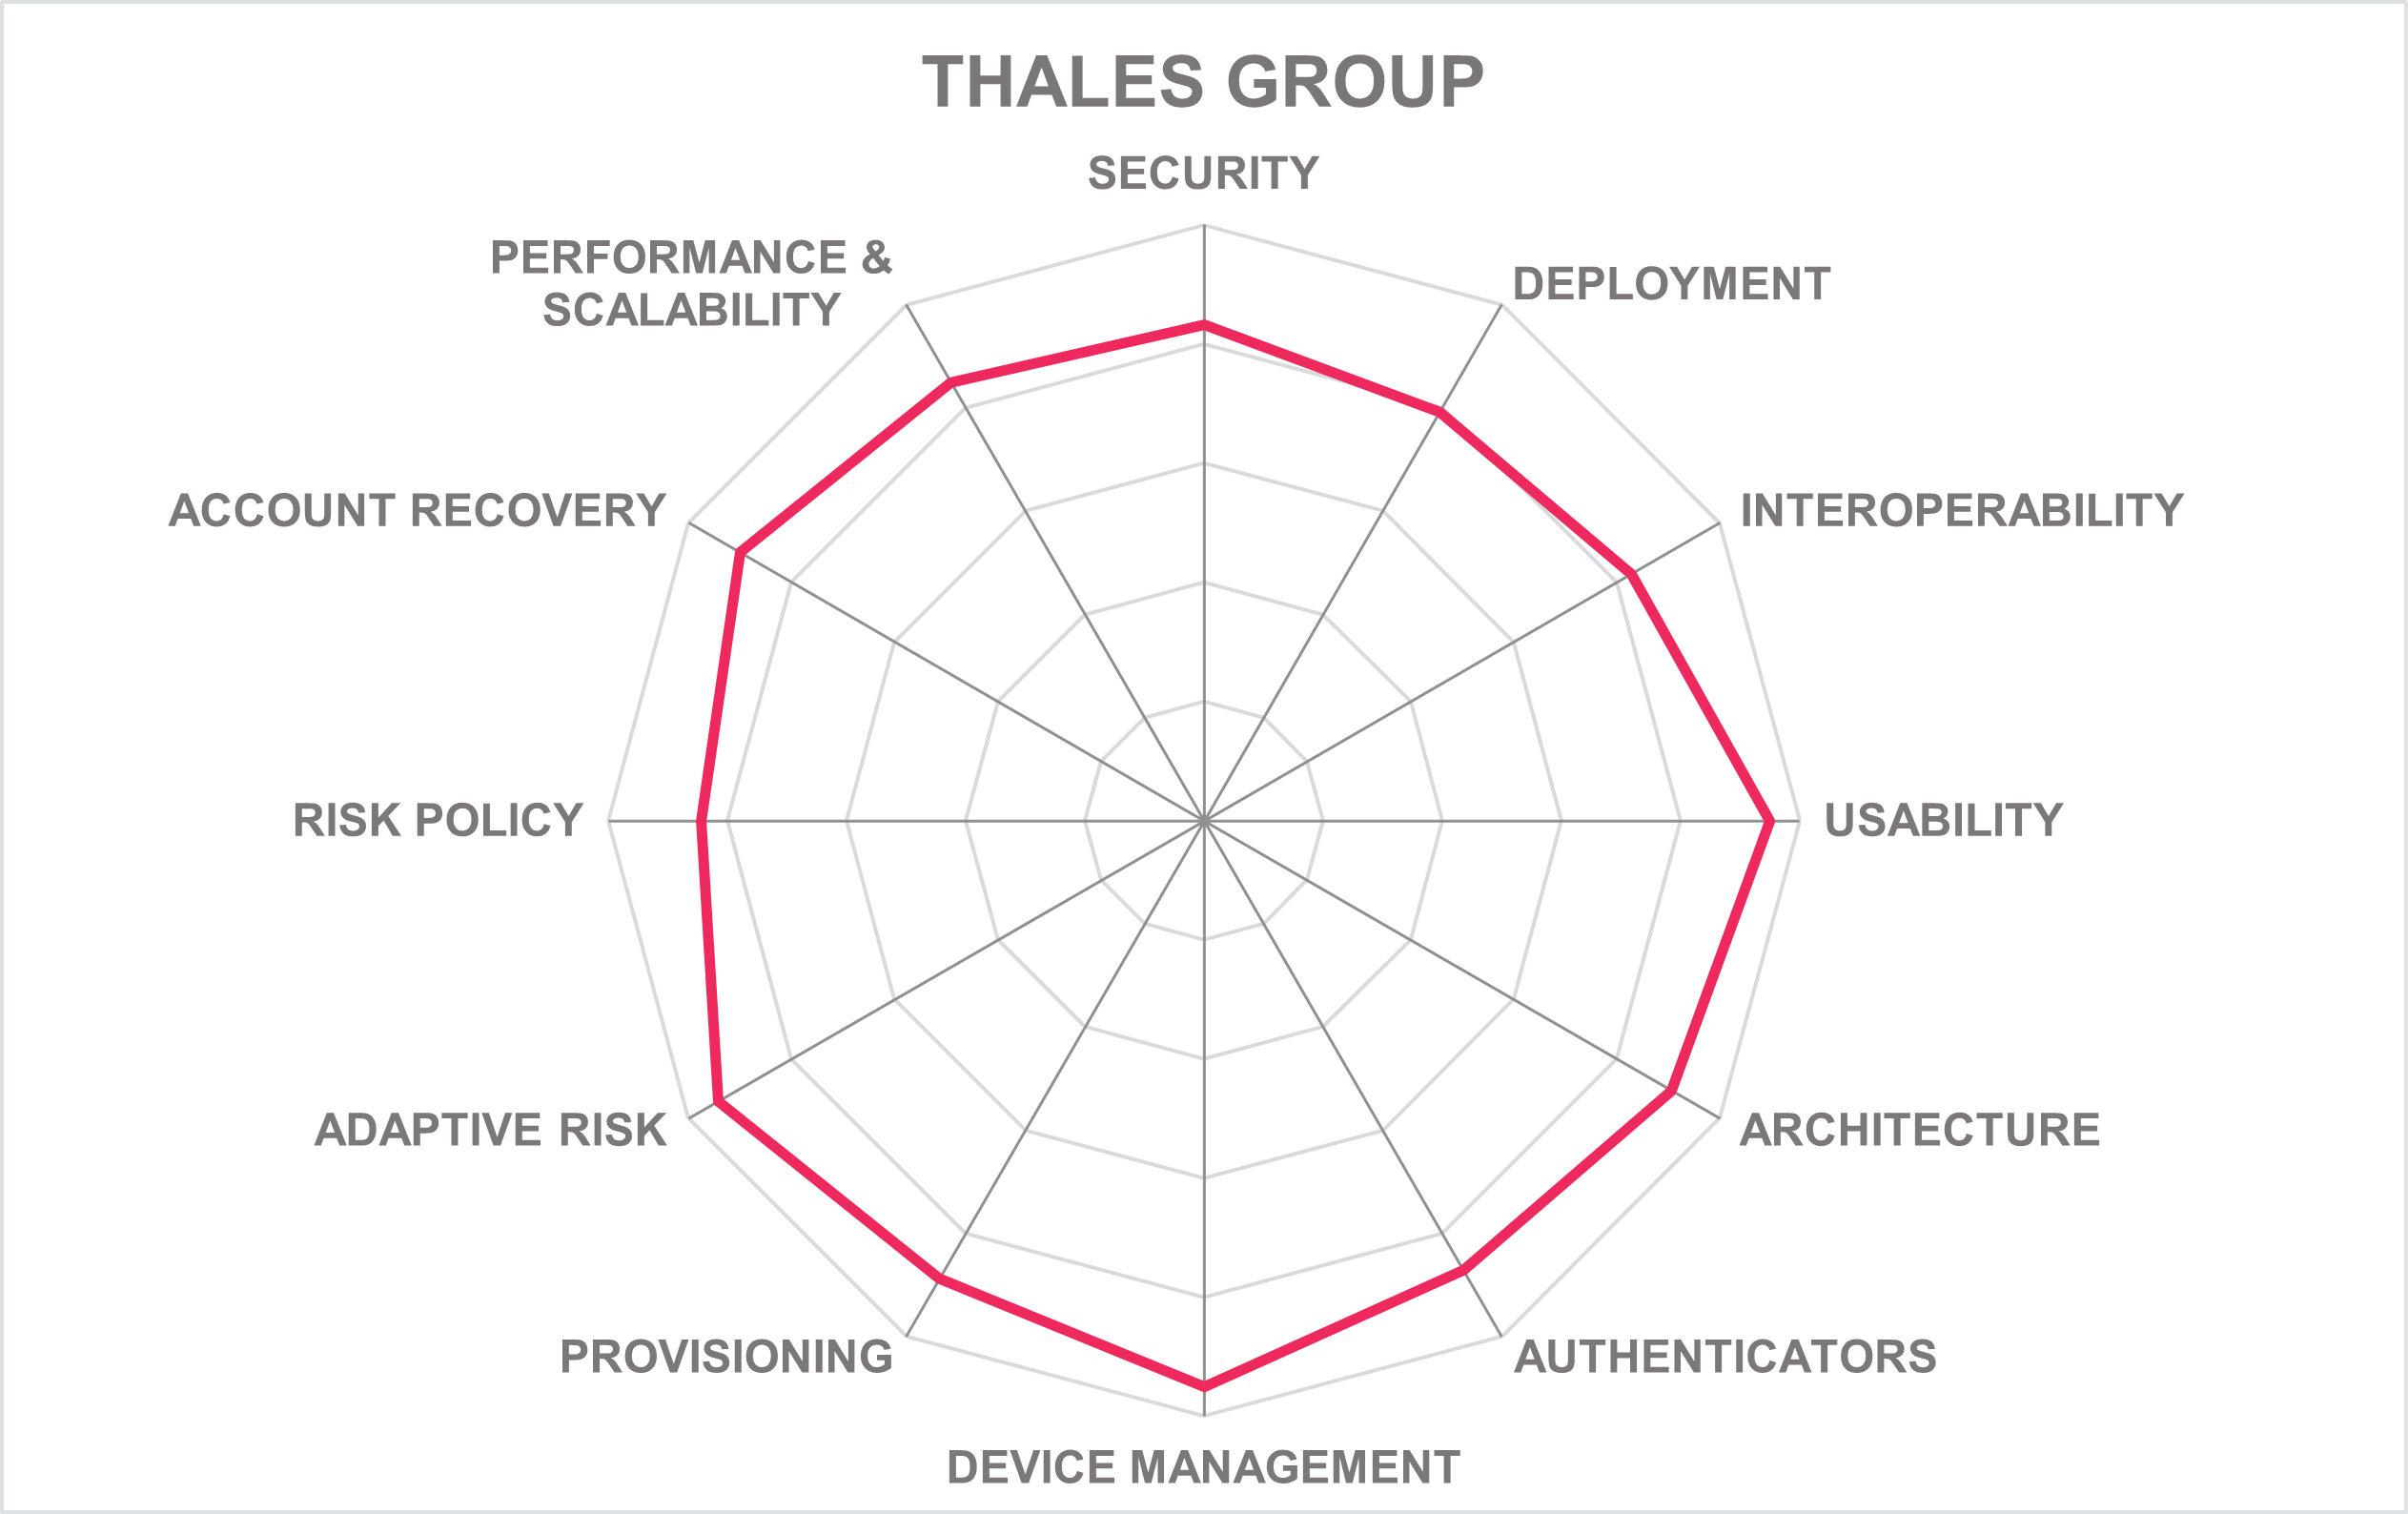
| Leader in | | | | |
Thales Group is a global technology and security provider headquartered in Paris, France, operating across aerospace, defense, cybersecurity, and digital identity. In 2022, Thales acquired OneWelcome, a leading European CIAM provider, expanding Thales’s identity capabilities across consumer, workforce, and partner ecosystems. The OneWelcome Identity Platform supports large-scale B2C identity management, including onboarding, self-registration, consent management, multi-brand identity administration, and strong authentication for high-volume consumer populations.
Thales OneWelcome supports a wide range of authentication methods, including username/password, passkeys, SMS OTP, mobile push notifications, vendor-provided mobile apps, and several third-party authenticator apps like Google Authenticator, Authy, and Microsoft Authenticator. Thales’s “Passwordless 360°” approach places passkeys at the core of authentication for consumers, complementing mobile app–based methods. The OneWelcome Authenticator app and mobile SDKs enable biometric authentication directly within the organization’s mobile app, supporting fully passwordless login and transaction approval.
Thales supports both native and third-party FIDO authenticators and provides its own FIDO2 and 2.1 tokens and smart cards, featuring multiple form factors and usage scenarios, and certified by the FIDO Alliance.
The platform provides device registration and binding, enabling consumers to link mobile devices as trusted authenticators. QR-code flows allow desktop-to-mobile login without passwords.
Thales OneWelcome offers a customizable device registration workflow and supports a variety of devices, including access devices and mobile authenticators. It enables consumers to link mobile devices as trusted authenticators. Additionally, QR-code flows allow desktop-to-mobile login without passwords. The solution provides device posture checks, including jailbreak/root and tampering detection.
It supports self-registration, identity verification, multi-brand identity pools, social login, BYOI, and customizable CIAM workflows. Passwordless enrolment flows are supported through mobile SDKs and the OneWelcome Authenticator, enabling consumers to link passkeys or mobile biometrics during onboarding.
Thales OneWelcome includes adaptive risk analysis capabilities that evaluate user behavior, device context, and transaction parameters during login. It supports device fingerprinting with a Unique Device Identifier (UDID) and tracks user history. The solution can detect jailbreak/root checks for authenticator devices and offers in-platform identity verification services. It also integrates with Badge’s cryptographic authentication for additional risk-aware features such as shared device protection, frictionless recovery, and “authentication without secrets.” Passwordless 360° includes risk-based orchestration that adjusts authentication strength dynamically for consumer use cases. It can integrate with FRIPs like LexisNexis Risk Solutions.
It supports risk policy authoring using Rego, the policy language of OPA and offers a GUI with drop-down attribute and action lists. It allows weighting of risk factors within policies and yields a granular risk score ranging from 0-200 in its risk evaluation. Policies can trigger step-up authentication with mobile biometrics or passkeys when risk thresholds are exceeded.
The solution supports a variety of account recovery options, including username/password, security questions, email OTPs, phone/SMS OTPs, mobile push notifications, and help desk support. Integration with Badge enables users to re-establish trust in new devices without relying on shared secrets or high-risk recovery methods. Custom recovery flows based on APIs can be created to provide a tailored approach to account recovery.
The solution’s cloud architecture enables rapid scaling to manage high-traffic events. The SLA commitment is for 99.99% uptime.
Thales OneWelcome is a product and market leader in the B2C passwordless market due to its depth of CIAM functionality, multi-channel passwordless capabilities, and integration with Thales’s world-class digital identity and security ecosystem.
Organizations looking for a B2C passwordless solution that is part of a feature-rich CIAM, with special emphasis on eIDAS and EU privacy compliance, should have Thales OneWelcome Identity Platform on their shortlist.
| Strengths |
|
| Challenges |
|
Transmit Security – Mosaic Platform
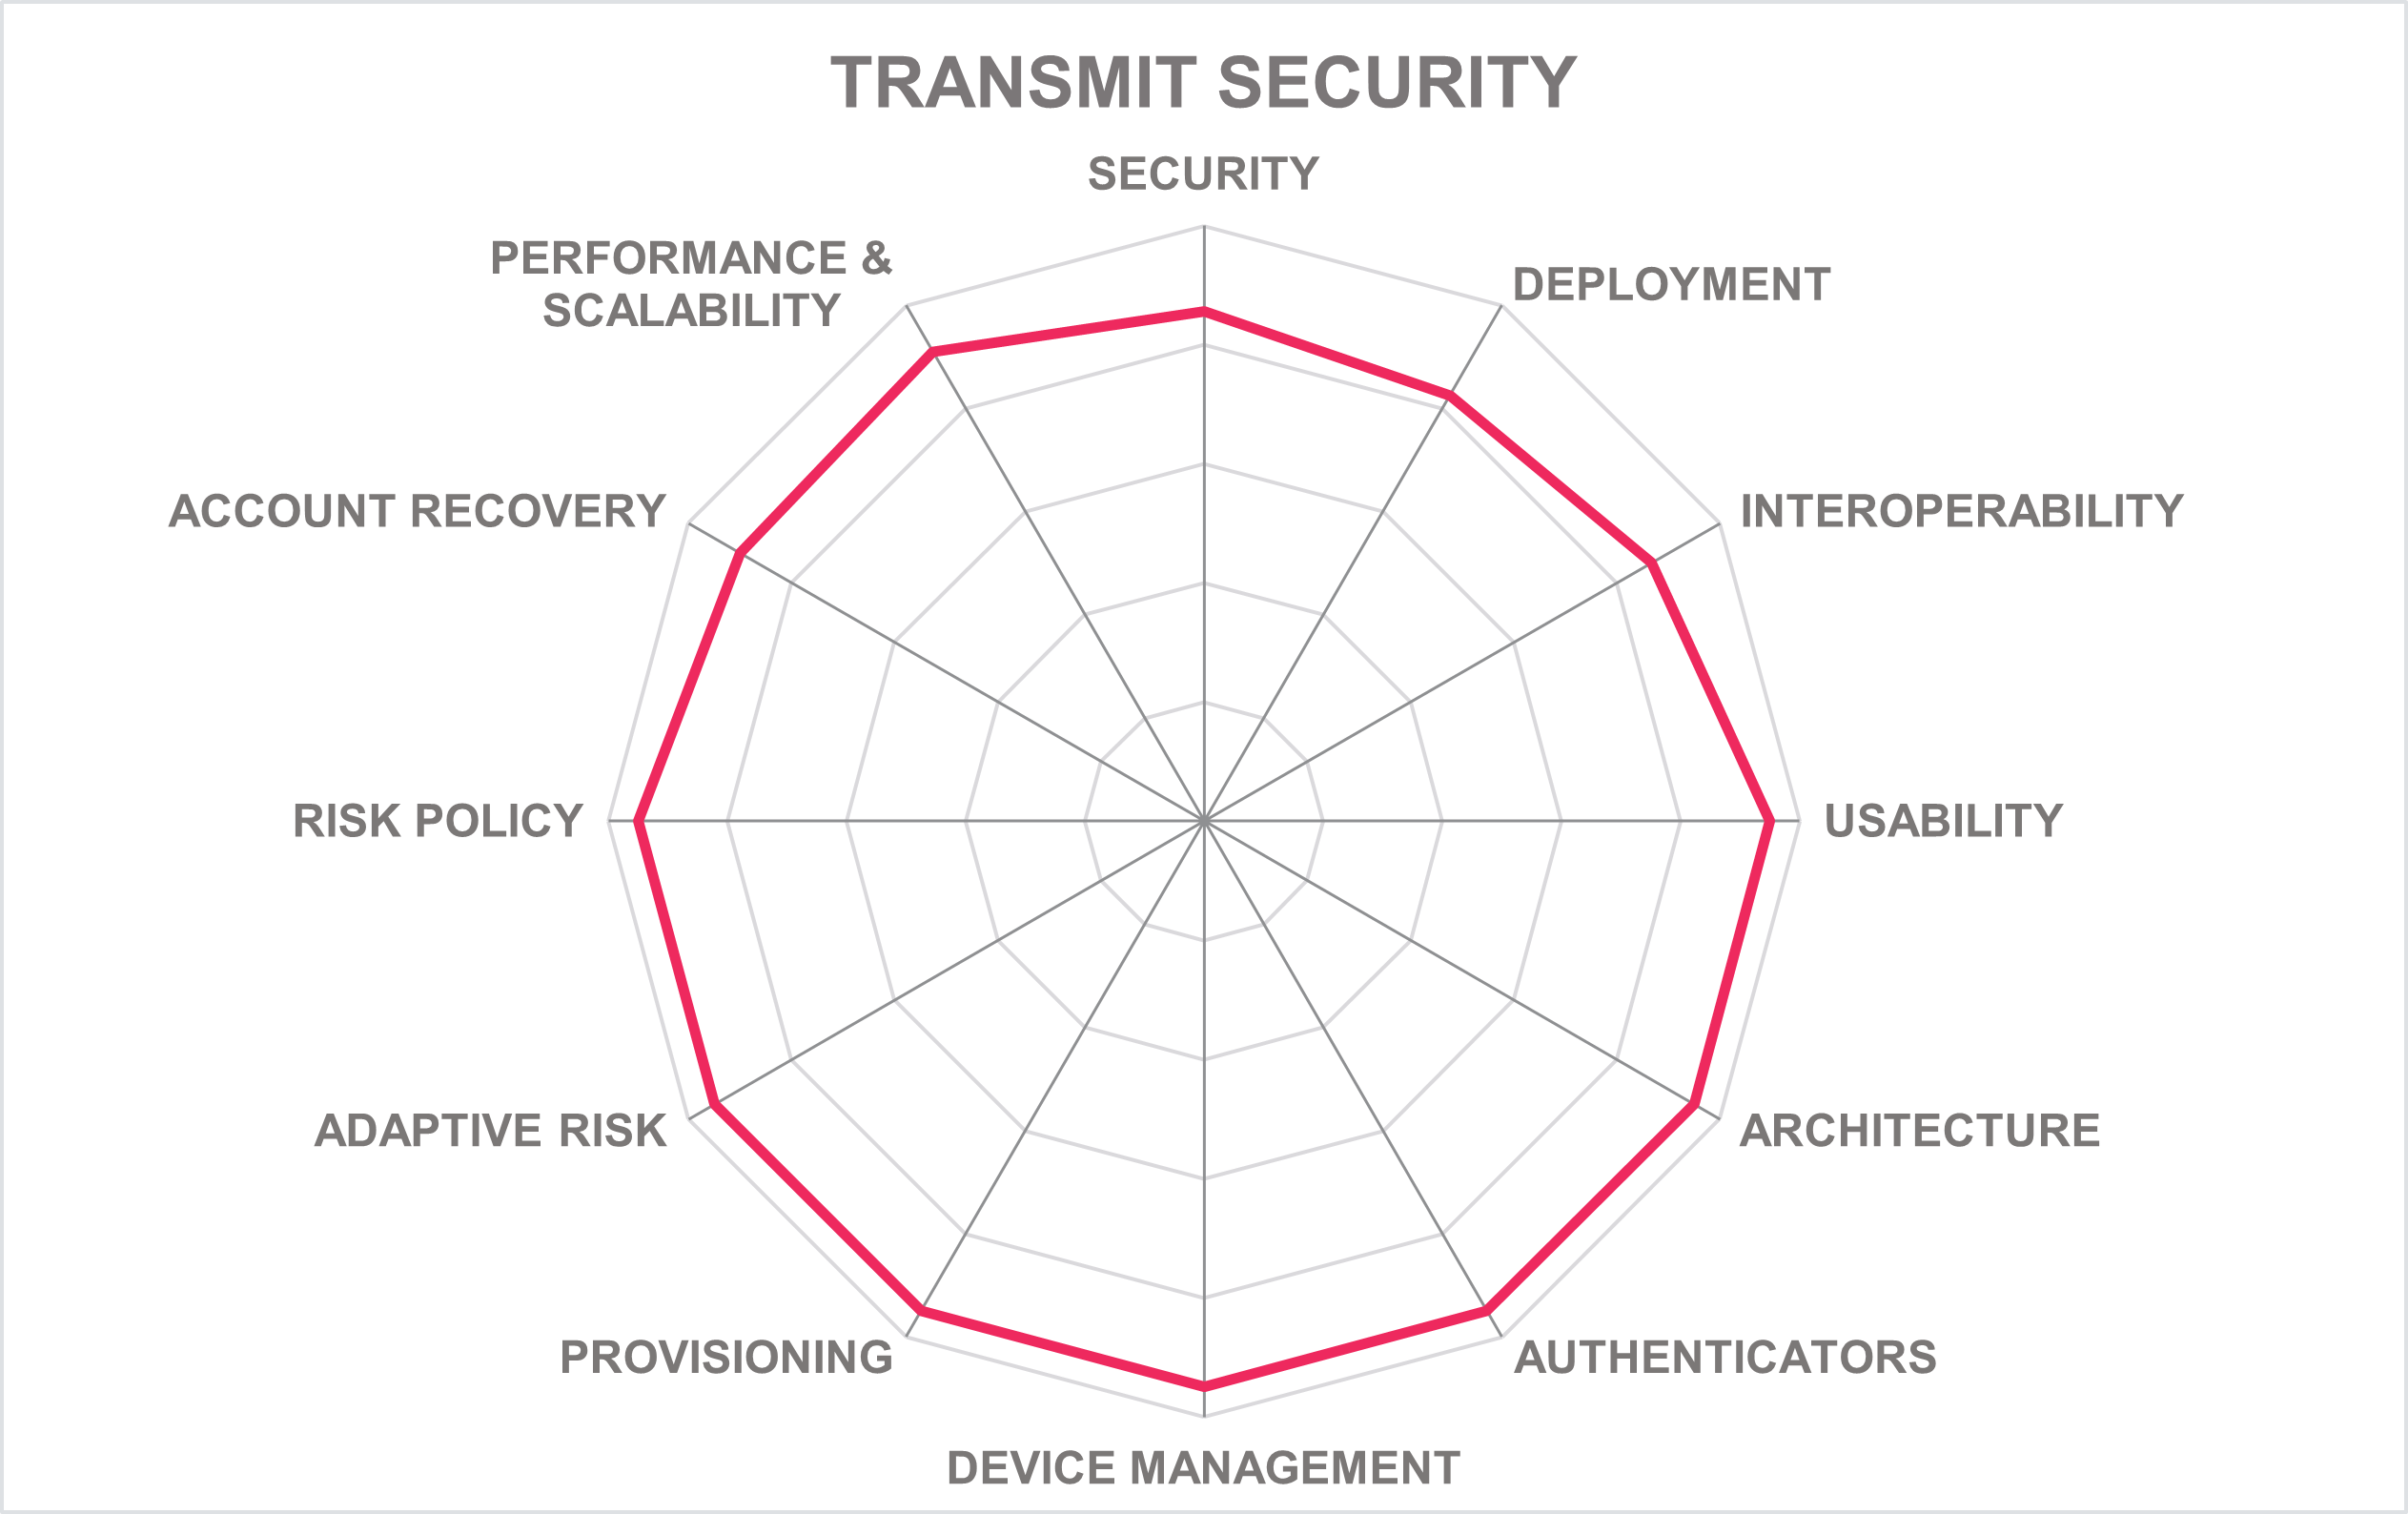
| Leader in | | | | |
Transmit Security, established in 2014, maintains headquarters in both Tel Aviv, Israel, and Boston, Massachusetts in the US. It is a privately held and well-funded company.
The Mosaic Platform is a modular, cloud-native CIAM and fraud suite, combining passwordless authentication, identity verification, and AI-driven identity threat and fraud detection into a unified solution for large-scale B2C applications. The platform is delivered as a SaaS solution, with operations spanning the APAC, EU, and North America regions. SaaS deployments are hosted across multiple public IaaS providers to support high availability and authentication throughput. The company is a FIDO Alliance Board Member, and several Transmit products use FIDO-certified authenticators.
The Mosaic Platform supports passkeys, and various MFA options such as SMS OTP, mobile push notifications, and third-party apps including Google Authenticator and Microsoft Authenticator. It supports both native and third-party FIDO authenticators. Native FIDO authenticators include platform authenticators such as Windows Hello, Apple Face ID/Touch ID, and Android biometrics via WebAuthn. It also supports transaction signing.
The platform supports customizable device registration workflows for devices including mobiles, desktops, laptops, IoT devices, and wearables. It uses cryptographic device binding, generating a device-specific key pair where the private key is stored securely on-device. This allows Mosaic to recognize trusted devices, manage device lifecycle (register, remove, and block), and verify device-held private keys. Mosaic augments this with a secure device identity, which is a stable fingerprinting system with high fraud-rejection accuracy. It also supports device posture checks, including OS integrity and jailbreak/root detection.
Mosaic for B2C Identity supports user self-registration, including identity verification, registration, consent capture, and device/passkey enrolment. Organizations can orchestrate the process using low-code capabilities. Registration is fully API-driven, enabling brand-consistent flows without UI constraints. Passkeys and device keys can be bound during onboarding, establishing strong cryptographic trust from the first interaction.
The Mosaic Platform evaluates a wide range of adaptive risk factors including IP address checks, known bad IP ranges, geo-location, geo-velocity, device ID, and device type, among others. It evaluates these in real time, leveraging built-in risk engines, and third-party integrations (such as threat intel feeds and EDR). Mosaic’s AI-based Detection and Response service, analyses device, network, behavioral, identity, and transaction signals to detect bots, scams, synthetic identities, and ATO attempts in real time. Risk scoring is tied directly to authentication strength: passkeys, biometrics and device-bound credentials can adjust based on risk.
The platform provides capabilities to create and manage risk policies. These include importing policies via JSON, using graphical interfaces, and natural language inputs. Mosaic’s identity orchestration engine supports complex policy logic with weighting for risk factors to create a risk score. It supports conditional logic based on risk score, device reputation, behavior, user segment, geo-location, and transaction attributes. The risk engine is fully addressable via API for both evaluation and policy management, with support for real-time invocation. It also integrates with policy decision engines (such as OPA), policy frameworks, and external fraud/risk tools such as BioCatch, LexisNexis, Ping Authorize, and internal ABAC systems.
Mosaic provides risk-aware account recovery, using the same fraud and risk detection signals used at login. Consumers can recover accounts through self-service flows, with additional friction applied only when the risk engine detects suspicious behavior. Temporary Access Codes allow secure device/passkey re-binding after offline or OOB verification. It also supports account recovery via device-based biometric re-authentication, passkeys, centralized face authentication, behavior-based recovery, trusted device fallback, and in-platform IDV, including government ID and liveness checks.
Transmit Security is an overall leader, product, market, and innovation leader in the B2C passwordless authentication market. It integrates CIAM, fraud detection and identity verification in a unified platform. Mosaic enriches every authentication and recovery journey with device intelligence, behavioral analytics, and real-time fraud risk scoring.
Organizations looking for a no-code/low-code identity orchestration platform that unifies passkeys, device intelligence, and fraud signals into adaptive B2C journeys without heavy coding should consider Transmit Security.
| Strengths |
|
| Challenges |
|
TrustBuilder – TrustBuilder.io
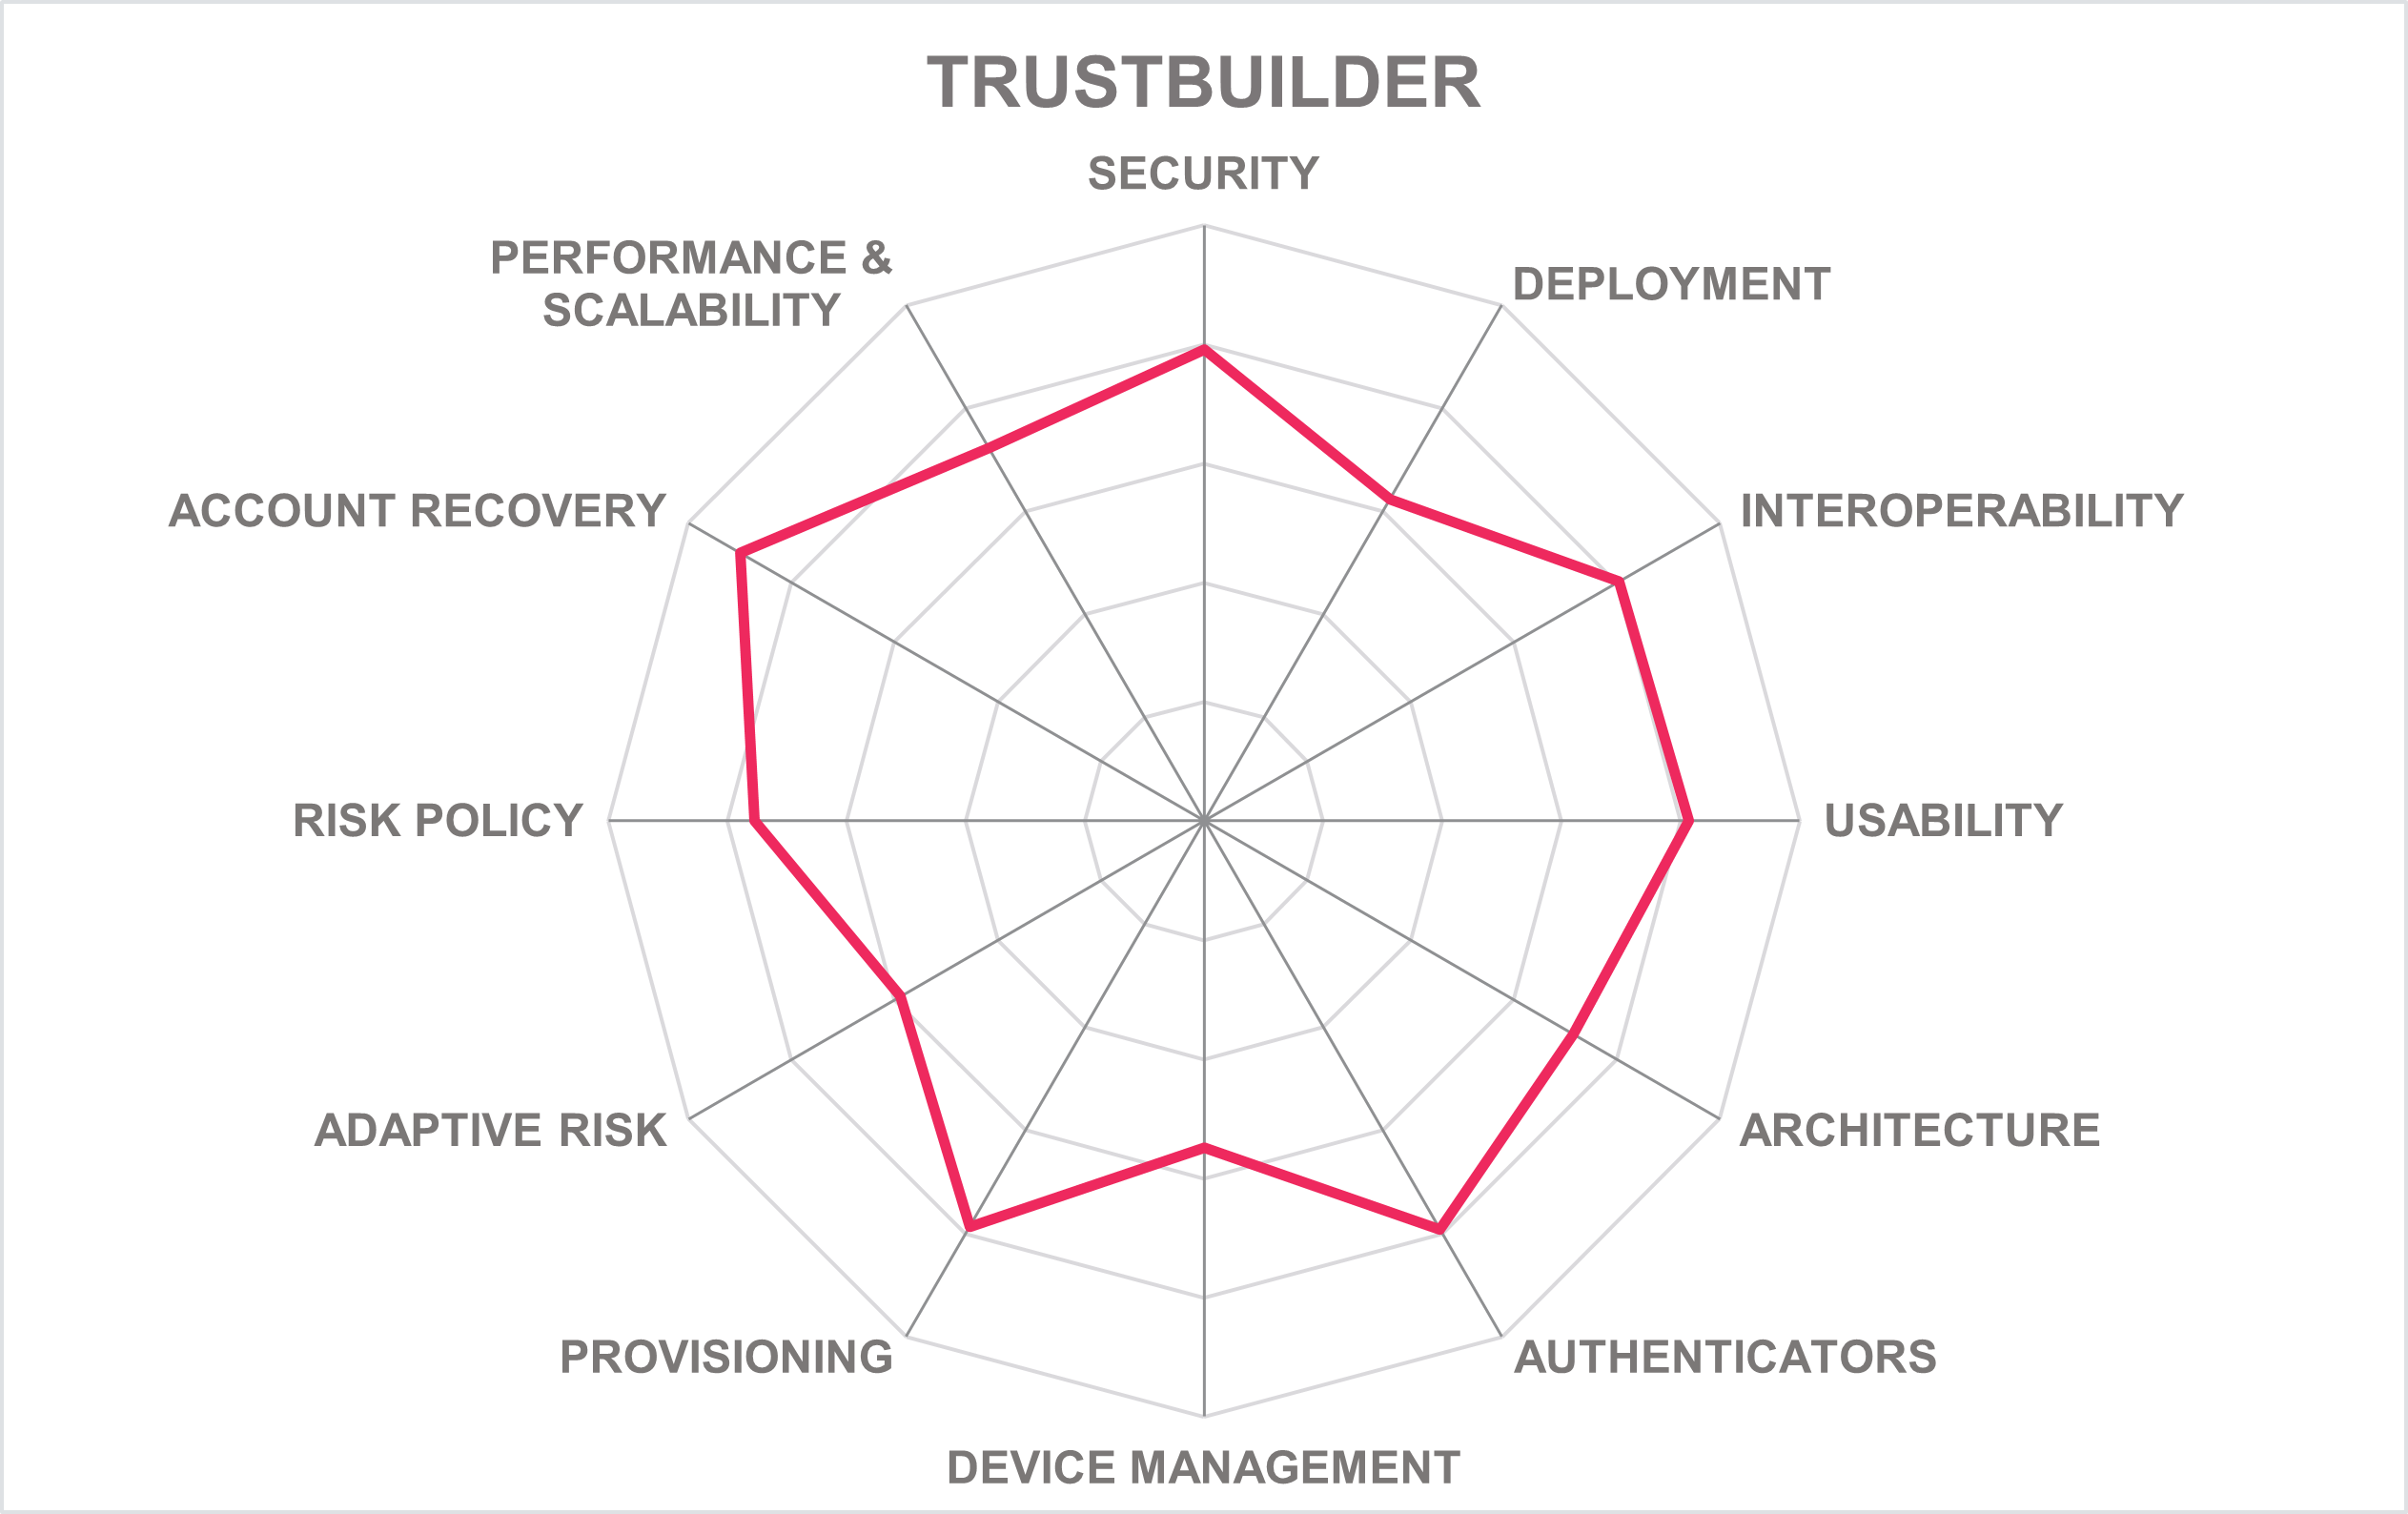
TrustBuilder is a European cybersecurity vendor providing SaaS-based CIAM, MFA and passwordless authentication. It is part of the inWebo group and offers a unified digital identity platform serving customers, partners, and employees. TrustBuilder was founded in 2008 and is headquartered in Ghent (Gent), Belgium. The company is backed by private equity and focuses on Access Management and CIAM. TrustBuilder maintains offices in Belgium, France, the Netherlands, Germany, the UK, and the US, with most of its customer base concentrated in France and the Benelux region. The SaaS-delivered platform operates on a single public IaaS environment hosted in datacenters in Belgium and France.
TrustBuilder.io is a modular Access Management platform that allows organizations to define and enforce authentication security policies. It is composed of several components: TrustBuilder.io is the central SaaS orchestrator handling policies, session lifecycles, personas, analytics, and adaptive authentication. TB Connect is a private connector integrating with backend systems, identity verification, federation using SAML/OIDC, and external services. TrustBuilder MFA is a patented dynamic-key, passwordless authentication engine using browser/desktop tokens.
The platform supports a variety of authentication methods including passkeys, SMS OTP, mobile push notifications, vendor-provided mobile apps, and biometric options such as Android fingerprint, Android facial recognition, iOS Face ID, and iOS Touch ID. TrustBuilder does not appear in the public FIDO Alliance Certified Products directory as a certified FIDO2 Server.
TrustBuilder supports mobile and desktop devices. It provides a device registration workflow for these devices, although this is not customizable. The platform does not include device security posture checks. The platform supports user self-registration as well as bulk provisioning from sources like LDAP and SCIM. However, it does not support provisioning to or from other cloud services using specific Cloud service APIs.
TrustBuilder MFA supports adaptive authentication, using its dynamic random key technology (ANSSI-certified) to strengthen authentication based on context. The platform evaluates several adaptive risk factors, including IP Address, known bad IP/network range checks, geo-location, geo-velocity, date/time, and device ID/type. It supports device fingerprinting linked to authentication. Additionally, it incorporates risk-based access controls.
Administrators can create risk policies through JSON import, XACML, a GUI with dropdowns, and a flow chart model. It supports weighting of risk factors within policies and provides a risk score. Policies can include combinations of actions based on risk scores and equivalent. The risk engine is accessible via an API; however, it does not currently interoperate with third-party services.
The platform provides multiple account recovery options such as username/password, email OTP or link, phone and SMS OTP, mobile push notifications, account linking, and help desk support. It also includes options like document verification or using government IdP's.
The solution's architecture is designed for cloud hosting and scalability. The service offers an SLA of 99.95% availability running on Google Cloud and using cloud-native services like Cloud Run and Google Kubernetes Engine (GKE) for scaling during high-traffic events.
TrustBuilder offers other passwordless solutions including TrustBuilder MFA, and combining multiple approaches can cover all environments and differ in how they balance security, usability and scalability.
Organizations looking for policy-driven orchestration with rich EU identity connectors, enabling fine-grained, context-aware passwordless journeys across multiple identity sources, should consider TrustBuilder.
| Strengths |
|
| Challenges |
|
Wultra – PowerAuth
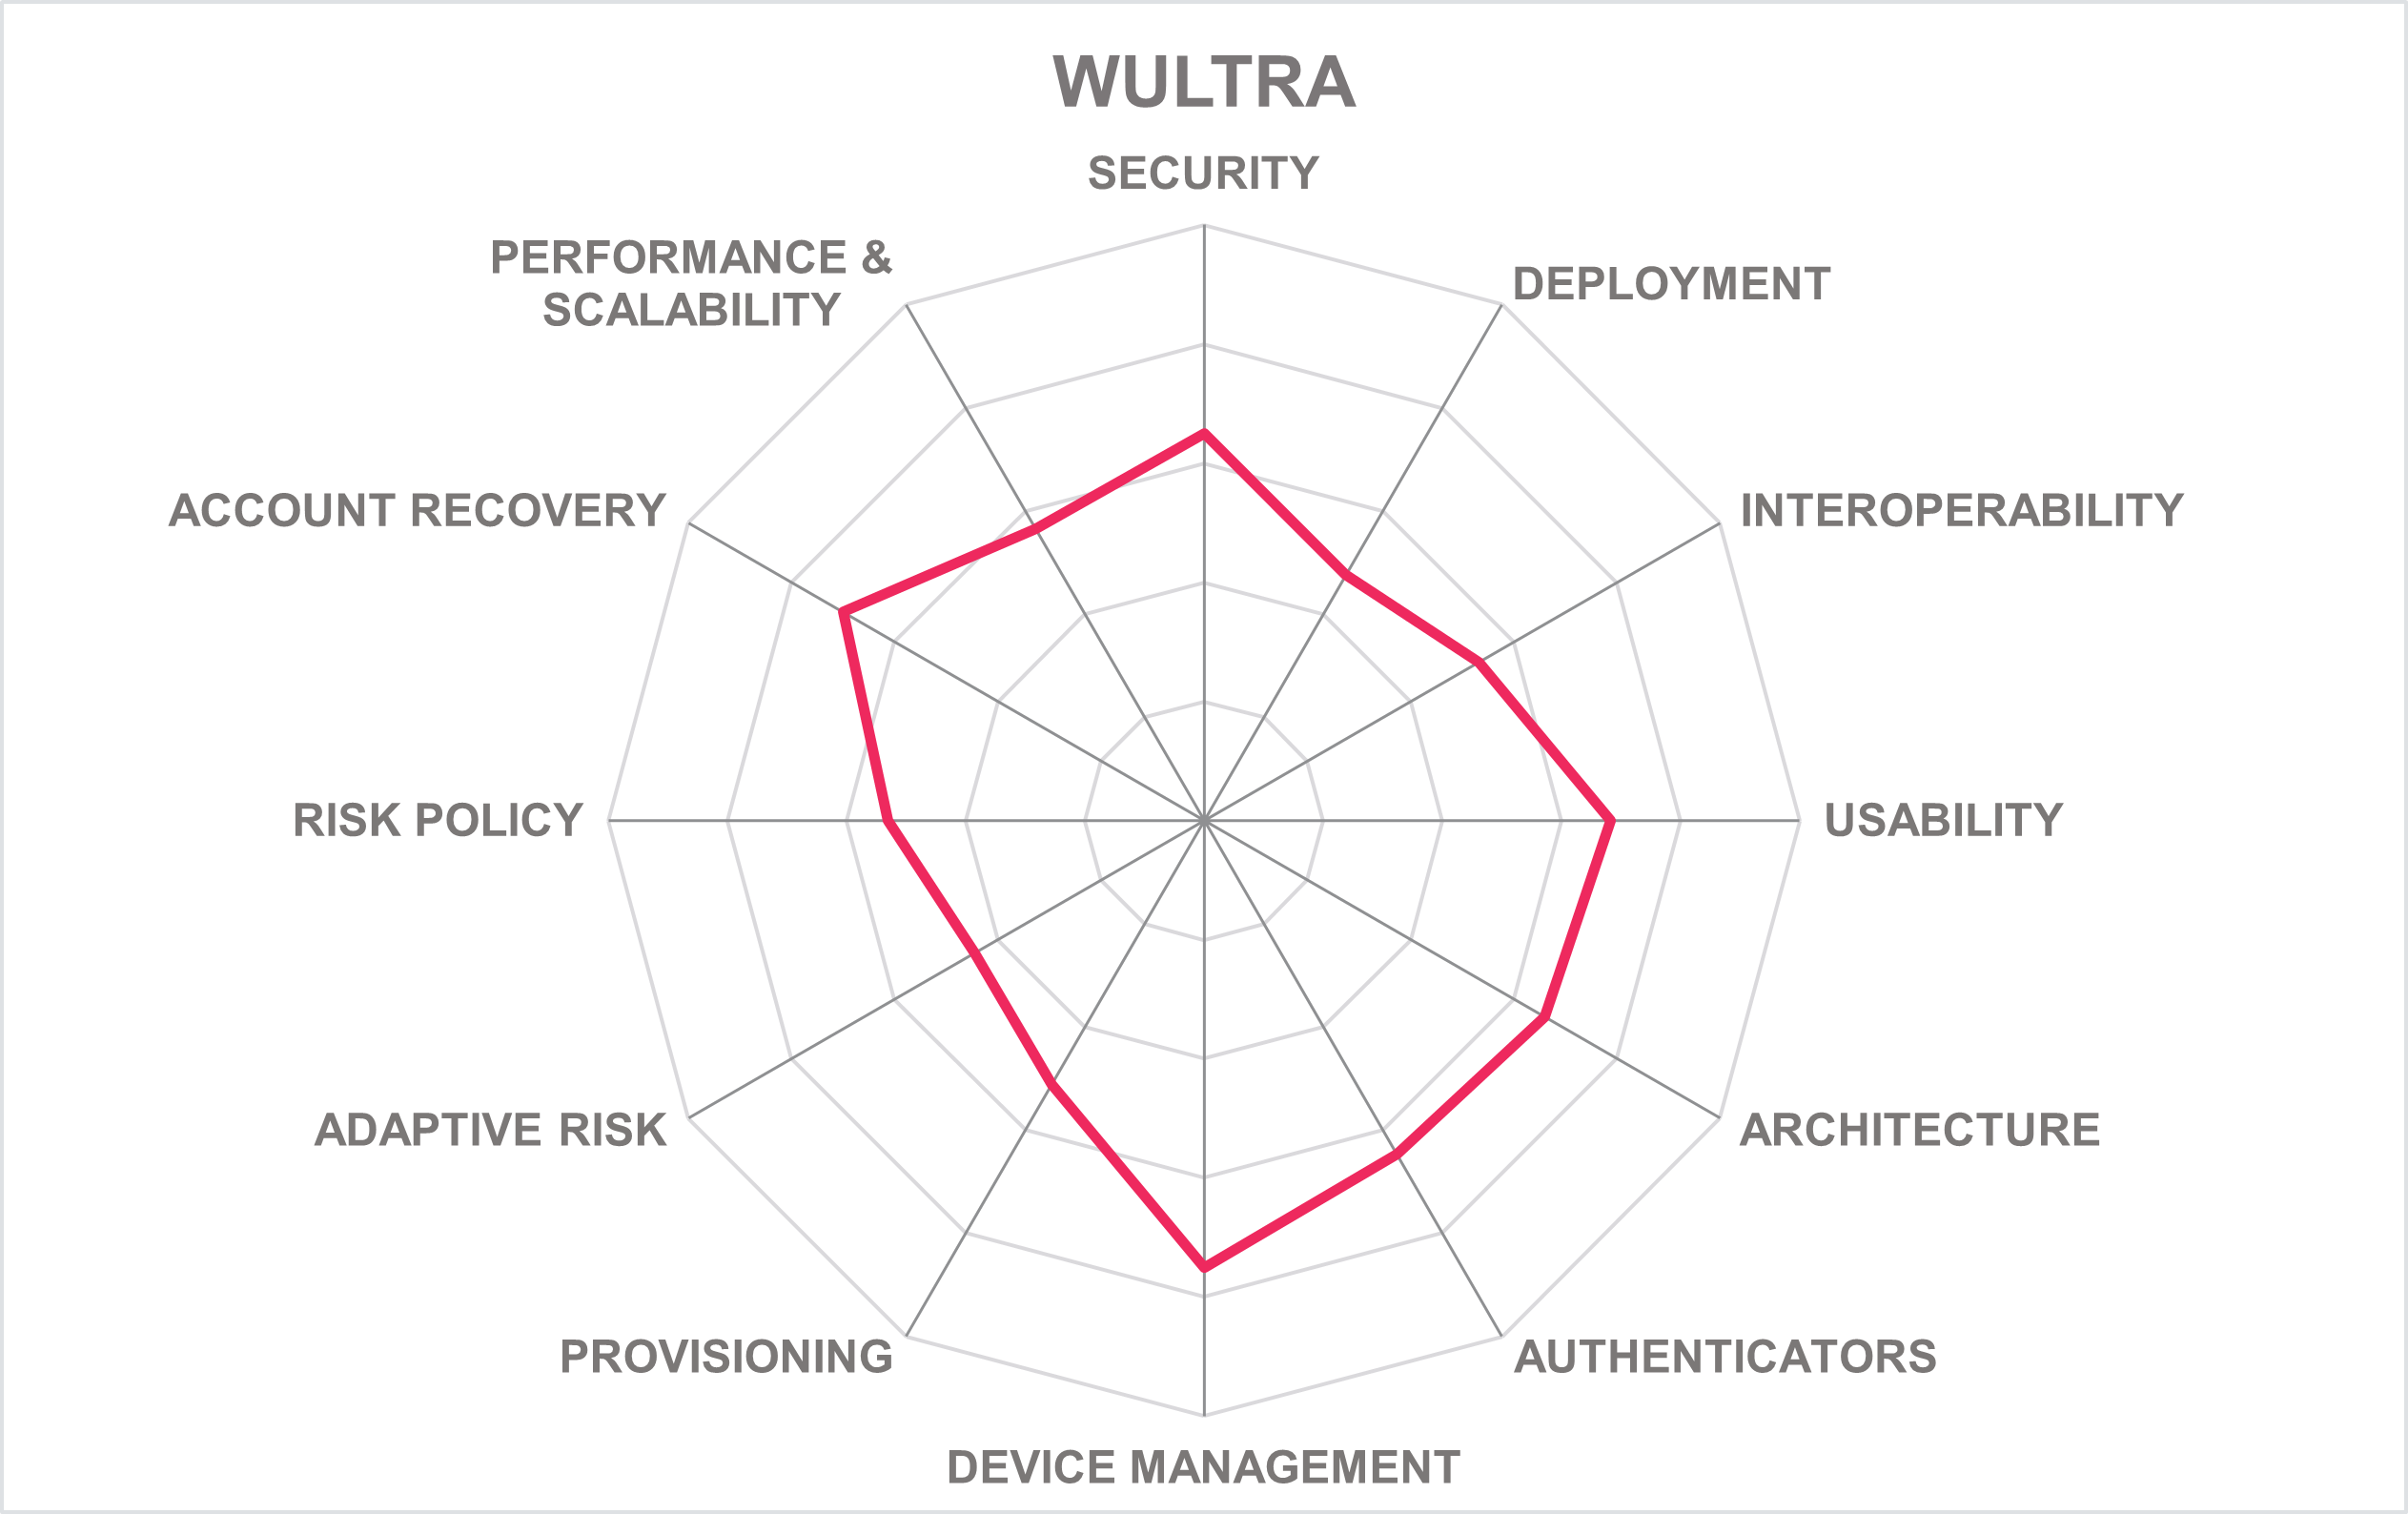
Wultra is a security-software vendor headquartered in Prague the Czech Republic, focused on mobile-first authentication, post-quantum cryptography, and secure SDKs for banking and fintech applications. Wultra PowerAuth is an open-source protocol and commercial platform for strong customer authentication, device binding, mobile app activation, and transaction signing. It is primarily used in financial services but applicable to B2C passwordless authentication scenarios. The company operates predominantly across Europe, Asia, and LATAM, supporting banks and fintech firms with deployment models that include on-premises installations and managed services.
Wultra claims that PowerAuth is the first post-quantum authentication platform on the market that supports software tokens, such as a mobile app, and FIDO2-based hardware tokens with visual transaction confirmations. It uses a single back-end infrastructure for all authentication means and typically is integrated into applications by the customer. It does not provide its own GUI or administrator management capabilities.
PowerAuth supports a variety of authentication methods including username/password, passkeys, SMS OTPs, mobile push notifications, vendor-provided mobile apps, Android and iOS biometrics, and FIDO2-based cross-platform authenticators. It also allows for digital signing of transactions, primarily intended for the financial use case. Customer authentication is the primary focus for this solution. However, Wultra is not listed as a FIDO Certified Server for B2C consumer identity.
PowerAuth supports a wide range of devices including mobile/tablet, smartwatch, and hardware tokens (FIDO2 keys). It supports both fully custom registration or de-coupling via activation code or OIDC/OAuth 2.x. It includes device posture checks including in-app protections, with optional device hardening provided by Promon. It only provides partial support for non-FIDO devices.
It supports user self-registration but not bulk provisioning from LDAP and SCIM, nor provisioning to/from other cloud services using specific APIs. A B2C service can allow a user to download the mobile app, scan a QR code or link the device, and enroll their authenticator without relying on passwords. The open-source nature of the platform and its SDKs support custom branding and integration into consumer registration journeys.
PowerAuth depends upon decisions from external systems such as anti-fraud products that the customers have. It integrates with fraud reduction platforms such as Feedzai, Hot Scan 360, and ThreatMark but does not track user history or evaluate user attributes directly.
PowerAuth does not provide risk policy management capabilities. It does not compete with anti-fraud systems but rather provides ways to change authentication behavior based on externally measured risk.
PowerAuth supports multiple account recovery options including username/password, email and phone OTPs, mobile push notifications, account linking, and help desk support. Alternatives include identity verification and OAuth 2.x based flows for recovery.
PowerAuth is designed to support large-scale enterprise and financial services’ needs. It claims to have been tested to 10 million users, and its cloud-based deployment offers an SLA of 99.95% availability with an optional 99.99%.
Wultra is a challenger in the passwordless authentication market. It is a niche product with capabilities narrowly focused on the financial services market.
Organizations looking for a mobile-first passwordless solution that features cryptographically strong device binding and transaction signing, with a roadmap for post-quantum encryption, should consider Wultra.
| Strengths |
|
| Challenges |
|
Vendors to Watch
Besides the vendors covered in detail in this document, we observe some other companies in the market that readers should be aware of. These vendors did not participate in the rating for several reasons but nevertheless offer a significant contribution to the market space.
1Password
Founded in 2005 and headquartered in Toronto, Canada, 1Password is a provider of digital identity solutions, specializing in password management and authentication. It offers a suite of products designed to protect sensitive information and streamline authentication processes for businesses and individuals alike. The company's focus is small and medium-sized organizations in North America, EMEA, APAC and LATAM.
Why worth watching: Passage is a passwordless authentication and user management solution for consumer apps and websites that enable developers to quickly implement login flows based on passkeys, magic links, login codes, and social logins. Passage can also add passkey authorization to an existing WebAuthn solution. Its adaptable nature allows customization to suit the unique requirements of each application. Customers have the flexibility to integrate authentication flows directly into their apps or utilize a hosted login page provided by Passage. Furthermore, it can function as a standalone user identity management system or integrate with external IdPs.
Digidentity
Digidentity BV was founded in 2008 and is headquartered in The Hague, Netherlands. The company serves multiple customer verticals including financial services (for KYC, AML, onboarding, and authentication), government (digital identity, citizen access), recruitment (right-to-work checks, employee onboarding) and developers/enterprises requiring authentication and digital identity solutions. Its region of operation is primarily Europe, with global reach into regulated markets and partnerships in the UK and beyond.
Why worth watching: It offers a secure, password-free authentication solution built on verified digital identities and trusted regulatory status. As a QTSP recognized by the European Union, it combines identity verification, electronic signatures, and authentication within a single mobile app. Users can authenticate simply by scanning a QR code, providing a fast and reusable digital identity experience that strengthens security while reducing friction. This approach helps organizations prevent fraud, streamline onboarding, and integrate flexible, standards-based identity proofing into their processes.
Entersekt
Entersekt was founded in 2010. In addition to its headquarters in Atlanta, Georgia, in the US, Entersekt operates offices in South Africa, Mauritius, UK, and Europe. The company provides transaction authentication to financial institutions, ensuring that it is both secure and free of unnecessary friction. In 2023, to expand its customer base, Entersekt announced the acquisition of Modirum, a digital payment security provider. The solution is designed to address the challenges of fraud in a holistic way. Coverage includes North America, EMEA, APAC, and LATAM.
Why worth watching: Entersekt excels in delivering authentication in a cross-channel and context-aware manner, ensuring the optimal authenticator is selected for each channel, use case, and risk level. Additionally, the solution provides the ability to escalate to more stringent identity verification measures as the situation requires. By supporting various biometric and passwordless methods, Entersekt aims to eliminate reliance on traditional password-based systems.
Entrust
Entrust, formerly known as Entrust Datacard, is a well-established vendor and trusted by leading customers in finance, government, healthcare, insurance, and enterprise use cases. The company provides identity-based security software and services in the areas of PKI, MFA, and fraud detection for those looking to access secure networks, connected devices, or conduct financial transactions. In 2024, Entrust announces the completion of its acquisition of Onfido, a global leader in identity verification and non-code orchestration capabilities. Headquartered in Minneapolis, Minnesota, in the US, Entrust also has offices in London, UK, Tokyo, Japan, Washington, District of Columbia, in the US, and other cities internationally.
Why worth watching: Entrust Identity as a Service (IDaaS) is a cloud-based IAM platform that facilitates a broad range of MFA authenticators, certificate-based passwordless access, SSO, and more. The platform has three product lines for workforce, consumer, and citizen use cases. It is an all-in-one user authentication and authorization solution in the cloud that helps organizations realize a Zero Trust framework with an identity first approach. The solution provides passwordless authentication with x.509 certificate-based authentication for both users and devices as well as support for FIDO2 keys and passkeys.
IDlayr
IDlayr is headquartered in London, UK, and was founded in 2020 by serial entrepreneurs who previously built cloud communications and payments platforms Mblox, Nexmo, and Boku. IDlayr uses the cryptographic security of the SIM card that resides in every phone to deliver a binary response that confirms a verified identity (with the mobile number), a verified credential (with the SIM card), and a verified digital presence (with the active session). The product is targeted at workforce, consumer, and partner use cases.
Why worth watching: IDlayr is a digital identity provider focused on transforming mobile phone numbers into trusted online identities. Its platform enables banks and large enterprises to strengthen authentication, reduce fraud, and enhance user experience through network-based, possession-factor security. By verifying users via their active mobile connection and SIM card, without relying on passwords, PINs, or SMS one-time codes, IDlayr delivers instant, invisible identity verification designed for the mobile era. The company’s technology aims to mitigate threats such as phishing, SIM swapping, and account takeover while supporting secure, frictionless onboarding, login, and step-up authentication processes for mobile users.
Mitek
Founded in 1985 and headquartered in San Diego, California, in the US, Mitek provides digital identity verification and access solutions. The company’s technology bridges the physical and digital worlds by enabling secure, compliant, and user-friendly identity verification across industries. The company helps businesses reduce fraud, meet regulatory requirements, and streamline digital onboarding and authentication processes.
Why worth watching: Mitek’s passwordless authentication solution replaces passwords and one-time passcodes with enterprise-grade biometrics through its MiPass platform. Using a combination of face, voice, and liveness detection, it delivers secure, frictionless access while preventing impersonation and identity theft. Designed for scalability and bias-free accuracy, MiPass integrates easily into existing customer experiences, storing encrypted biometric data in the cloud to simplify management and enhance both trust and user convenience.
Veridium
Founded in 2016 and headquartered in New York, Veridium is a cybersecurity company specializing in phishing- and hacking-resistant authentication for zero-trust environments. Its technologies verify user identity in real time across desktops, applications, and databases, ensuring that the right person is using the right device and network. Veridium’s mission is to eliminate the traditional trade-offs between security, privacy, and user experience by providing seamless, passwordless authentication solutions for enterprises worldwide.
Why worth watching: Veridium’s Identity Assurance Platform delivers AI-driven identity threat protection, behavioral biometrics, and continuous authentication. The platform combines active and passive biometric factors to ensure accurate, frictionless user verification from start to finish. Designed for hybrid and multi-cloud environments, it integrates with existing platforms, supports VPNs, virtual desktops, and legacy applications, and offers consistent passwordless experiences across all devices and connections. With its AI-based behavioral biometrics and anomaly detection, Veridium’s solution strengthens enterprise security, while maintaining ease of use and operational flexibility.
Related Research
Leadership Compass: Passwordless Authentication for Consumers: Securing Fast Business Online
Buyer's Compass: Passwordless Authentication for Consumers
Leadership Compass: Customer Identity and Access Management
Buyer's Compass: Customer Identity and Access Management
Leadership Compass: Fraud Reduction Intelligence Platforms - Finance
Leadership Compass: Fraud Reduction Intelligence Platforms - eCommerce
Leadership Compass: Passwordless Authentication for Enterprises
Copyright
© 2026 KuppingerCole Analysts AG. All rights reserved. Reproducing or distributing this publication in any form is prohibited without prior written permission. The conclusions, recommendations, and predictions in this document reflect KuppingerCole Analysts' initial views. As we gather more information and conduct deeper analysis, the positions presented here may undergo refinements or significant changes. KuppingerCole Analysts disclaims all warranties regarding the completeness, accuracy, and adequacy of this information. Although KuppingerCole Analysts' research documents may discuss legal issues related to information security and technology, we do not provide legal services or advice, and our publications should not be used as such. KuppingerCole Analysts assumes no liability for errors or inadequacies in the information contained in this document. Any expressed opinion may change without notice. All product and company names are trademarks™ or registered® trademarks of their respective holders. Their use does not imply any affiliation with or endorsement by them.
KuppingerCole Analysts supports IT professionals with exceptional expertise to define IT strategies and make relevant decisions. As a leading analyst firm, KuppingerCole Analysts offers firsthand, vendor-neutral information. Our services enable you to make decisions crucial to your business with confidence and security.
Founded in 2004, KuppingerCole Analysts is a global, independent analyst organization headquartered in Europe. We specialize in providing vendor-neutral advice, expertise, thought leadership, and practical relevance in Cybersecurity, Digital Identity & IAM (Identity and Access Management), Cloud Risk and Security, and Artificial Intelligence, as well as technologies enabling Digital Transformation. We assist companies, corporate users, integrators, and software manufacturers to address both tactical and strategic challenges by making better decisions for their business success. Balancing immediate implementation with long-term viability is central to our philosophy.
For further information, please contact clients@kuppingercole.com.
Executive Summary


Key Findings
Market Analysis
Key Market Trends and Innovations
Delivery Models
Required Capabilities
Leadership
Product/Vendor evaluation
Spider graphs
1Kosmos – 1Kosmos Customer
Badge – Badge
Beyond Identity – Secure Customers (CIAM)
cidaas – cidaas
CyberArk – CyberArk Identity Security Platform
Descope – Descope
Ergon – Airlock IAM
Exostar – Access One Platform
Futurae Technologies – Futurae Authentication Platform
HID – Authentication Platform, Risk Management Solution, Enterprise Passkey Management
HYPR – Identity Assurance Platform
IBM – IBM Verify
ITSME – Passwordless Authentication
Keyless – Keyless Zero-Knowledge Biometrics™
LoginRadius – CIAM Platform
Microsoft – Microsoft Entra
Nevis – Nevis Identity Suite, Nevis ID & Authentication Cloud
OKTA Inc. – OKTA and Auth0 Platforms
One Identity – OneLogin Advanced Authentication
OneSpan – Digipass S3 Authentication Software
Ping Identity – Ping Identity Platform
Relock – Relock invisible MFA.
SecureAuth – SecureAuth IAM
Signicat – MobileID
Thales Group – Thales OneWelcome Identity Platform
Transmit Security – Mosaic Platform
TrustBuilder – TrustBuilder.io
Wultra – PowerAuth
Vendors to Watch
Related Research
Copyright



Table of Contents


Table of contents
Close
Executive Summary
Key Findings
Market Analysis
Key Market Trends and Innovations
Delivery Models
Required Capabilities
Leadership
Product/Vendor evaluation
Spider graphs
1Kosmos – 1Kosmos Customer
Badge – Badge
Beyond Identity – Secure Customers (CIAM)
cidaas – cidaas
CyberArk – CyberArk Identity Security Platform
Descope – Descope
Ergon – Airlock IAM
Exostar – Access One Platform
Futurae Technologies – Futurae Authentication Platform
HID – Authentication Platform, Risk Management Solution, Enterprise Passkey Management
HYPR – Identity Assurance Platform
IBM – IBM Verify
ITSME – Passwordless Authentication
Keyless – Keyless Zero-Knowledge Biometrics™
LoginRadius – CIAM Platform
Microsoft – Microsoft Entra
Nevis – Nevis Identity Suite, Nevis ID & Authentication Cloud
OKTA Inc. – OKTA and Auth0 Platforms
One Identity – OneLogin Advanced Authentication
OneSpan – Digipass S3 Authentication Software
Ping Identity – Ping Identity Platform
Relock – Relock invisible MFA.
SecureAuth – SecureAuth IAM
Signicat – MobileID
Thales Group – Thales OneWelcome Identity Platform
Transmit Security – Mosaic Platform
TrustBuilder – TrustBuilder.io
Wultra – PowerAuth
Vendors to Watch
Related Research
Copyright